
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-29015 — Proof-of-concept for a stored XSS vulnerability in Code Astro Internet Banking System 2.0.0, demonstrating session hijacking and client-side attacks via the name parameter in pages_account.php. | Kitploit
Tools/GitHubGitHub/b1tm4r/cve-2025-29015
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubb1tm4r/cve-2025-29015

CVE-2025-29015

Proof-of-concept for a stored XSS vulnerability in Code Astro Internet Banking System 2.0.0, demonstrating session hijacking and client-side attacks via the name parameter in pages_account.php.

View Repository
11 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2025-29015 - Internet Banking System 2.0.0 Stored XSS in pages_account.php

Description

A Stored Cross-Site Scripting (XSS) vulnerability exists in Code Astro Internet Banking System 2.0.0 via the name parameter in /admin/pages_account.php. Malicious JavaScript code can be injected and stored in the system, executing whenever an admin views the affected page. This can lead to session hijacking and other client-side attacks.

Affected Component

  • name parameter in /admin/pages_account.php
  • Data is stored and executed when accessed by an admin

Exploitation Steps

  1. Log in to the admin panel and navigate to the "Account" section.


  1. Insert the following payload in the name field and submit the form:
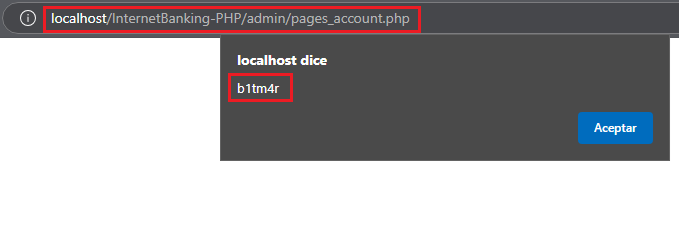
   //--></SCRIPT>">'><SCRIPT>alert(String.fromCharCode(98, 49, 116, 109, 52, 114));</SCRIPT>
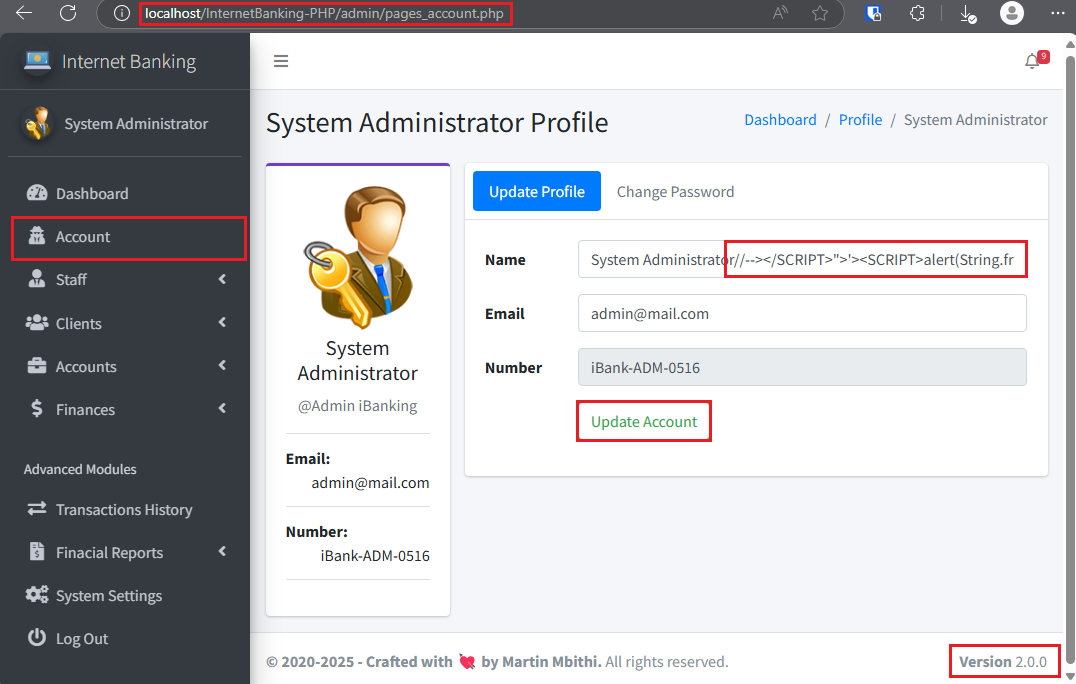
  1. When the user visits any page or menu, the payload will trigger.


Impact

  • Session Hijacking
  • Phishing Attacks
  • Arbitrary Actions on Behalf of an Admin

Mitigation

  • Implement proper input sanitization (e.g., escaping special characters).
  • Use Content Security Policy (CSP) to limit script execution.
  • Validate and encode user input before storing it.

References

  • OWASP XSS Guide
Download Tool