 ashutosh1206/crypton
Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange, Authentication methods along with example challenges from CTFs

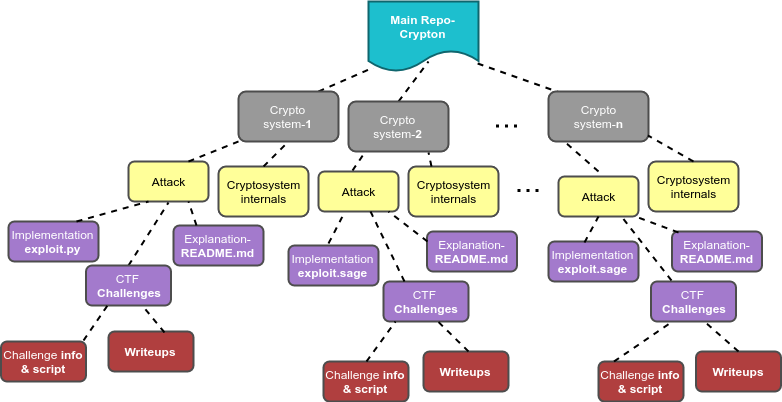
Crypton is an educational library to learn and practice Offensive and Defensive Cryptography. It is basically a collection of explanation and implementation of all the existing vulnerabilities and attacks on various Encryption Systems (Symmetric and Asymmetric), Digital Signatures, Message Authentication Codes and Authenticated Encryption Systems. Each attack is also supplemented with example challenges from "Capture The Flag" contests and their respective write-ups. Individuals who are already acquainted (or are into CTFs) with this field can use Crypton as a tool to solve challenges based on a particular existing vulnerability.
The library will be continuously updated with attack explanations and CTF challenges! Feel free to email me regarding any suggestions!
I have written a blog post on the timeline of development of this library: https://masterpessimistaa.wordpress.com/2018/08/12/announcing-crypton-an-educational-library-to-learn-offensive-and-defensive-cryptography/
WARNING: The author in no way guarantees that the code is secure. The library is only meant for educational purposes and the code should not be used for implementing in real world. All the example scripts in the library are trivial implementations.
There are different sections in this README:
Help CTF players and individuals interested in the field of Cryptography provide a platform for learning attacks in crypto and for experienced CTF players to practice challenges systematically divided into attacks associated with different sub-domains in crypto. Also, illustrate through various attack explanations how proper implementation of protocols is crucial.

| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|---|---|---|---|---|
| 1 | Block Cipher Basics- working of block ciphers, padding etc. |
|
|
|
| 2 | Modes of Encryption- different modes of operation on block ciphers: ECB, CBC, CTR |
|
|
|
| 3 | Block Size Detection- detect blocksize of a block cipher encrypting data on a remote service |
|
|
|
| 4 | Mode Detection- detect type of mode of encryption: independent or dependent encryption of blocks |
|
|
|
| 5 | ECB Byte at a Time- byte at a time decryption of a secret string running on a remote service encrypting input+secret in ECB mode |
|
|
|
| 6 | CBC IV Detection- detect the value of Initialisation Vector on a remote service that is encrypting our input using a block cipher in CBC mode |
|
|
|
| 7 | CBC Bit Flipping Attack- exploiting cookie generation mechanism to login as admin when cookie is generated using a block cipher in CBC mode |
|
|
|
| 8 | CBC Byte at a Time- byte at a time decryption of a secret string running on a remote service encrypting input+secret in ECB mode |
|
|
|
| 9 | CBC Padding Oracle Attack- decryption of data encrypted by a vulnerable service providing encryption/decryption |
|
|
|
| 10 | CTR Bit Flipping- exploiting cookie generation mechanism to login as admin when cookie is generated using a block cipher in CBC mode |
|
|
|
