

 arpsyndicate/kenzer
automated web assets enumeration & scanning [DEPRECATED]


A Conceptual Introduction to Automating Bug Bounties


git clone https://github.com/ARPSyndicate/kenzer /home/ubuntu/kenzer && cd /home/ubuntu/kenzer (preferred)Settings > Your Bots > Add a new botkenzerconfigs/kenzer.conf./install.sh -b [if you need kenzer-compatible binaries to be installed] (preferred)./install.sh [if you do not need kenzer-compatible binaries to be installed]./run.sh [if you do not need installation at all]./service.sh [initialize it as a service post-installation] (preferred)bash swap.sh [in case you are facing memory issues]kenzer using Zulip client, by adding bot to a stream or via DM.@**kenzer** man as Zulip input to display available commands.@**kenzer** (name of your chatbot).
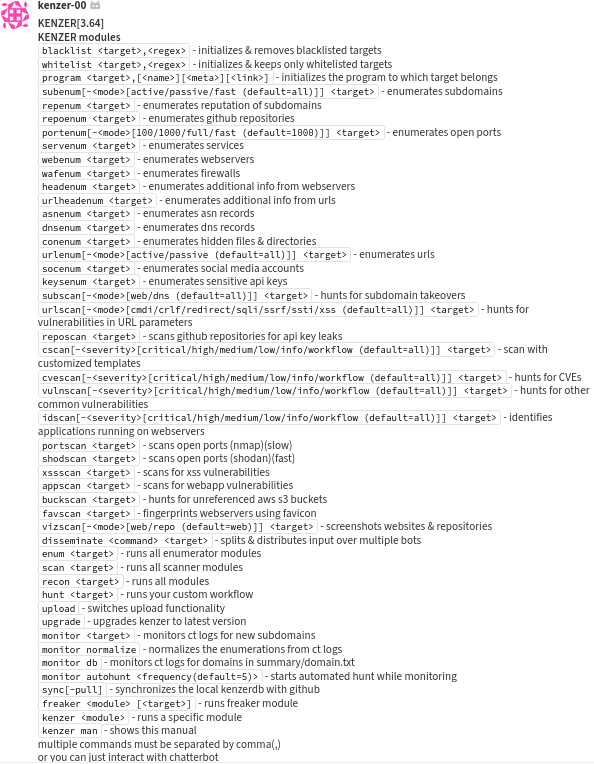
blacklist <target>,<regex>- initializes & removes blacklisted targetswhitelist <target>,<regex>- initializes & keeps only whitelisted targetsprogram <target>,[<name>][<meta>][<link>]- initializes the program to which target belongssubenum[-<mode>[active/passive (default=all)]] <target>- enumerates subdomainsrepenum <target>- enumerates reputation of subdomainsrepoenum <target>- enumerates github repositoriesportenum[-<mode>[100/1000/full/fast (default=1000)]] <target>- enumerates open portsservenum <target>- enumerates serviceswebenum <target>- enumerates webserversheadenum <target>- enumerates additional info from webserversurlheadenum <target>- enumerates additional info from urlsasnenum <target>- enumerates asn recordsdnsenum <target>- enumerates dns recordsconenum <target>- enumerates hidden files & directoriesurlenum[-<mode>[active/passive (default=all)]] <target>- enumerates urlssocenum <target>- enumerates social media accountskeysenum <target>- enumerates sensitive api keyswafscan <target>- scans for firewallssubscan[-<mode>[web/dns (default=all)]] <target>- hunts for subdomain takeoversurlscan[-<mode>[cmdi/crlf/redirect/sqli/ssrf/ssti/xss (default=all)]] <target>- hunts for vulnerabilities in URL parametersreposcan <target>- scans github repositories for api key leaksbakscan <target>- scans for backup filescscan[-<severity>[critical/high/medium/low/info/workflow (default=all)]] <target>- scan with customized templatescvescan[-<severity>[critical/high/medium/low/info/workflow (default=all)]] <target>- hunts for CVEsvulnscan[-<severity>[critical/high/medium/low/info/workflow (default=all)]] <target>- hunts for other common vulnerabilitiesidscan[-<severity>[critical/high/medium/low/info/workflow (default=all)]] <target>- identifies applications running on webserversportscan <target>- scans open ports (nmap)(slow)shodscan <target>- scans open ports (shodan)(fast)xssscan <target>- scans for xss vulnerabilitiesappscan <target>- scans for webapp vulnerabilitiesbuckscan <target>- hunts for unreferenced aws s3 bucketsfavscan <target>- fingerprints webservers using faviconvizscan[-<mode>[web/repo (default=web)]] <target>- screenshots websites & repositoriesenum <target>- runs all enumerator modulesscan <target>- runs all scanner modulesrecon <target>- runs all moduleshunt <target>- runs your custom workflowdisseminate <command> <target>- splits & distributes input over multiple botsupload- switches upload functionalitywaf- switches waf avoid functionality"proxy- switches proxy functionality"upgrade- upgrades kenzer to latest versionmonitor <target>- monitors ct logs for new subdomainsmonitor normalize- normalizes the enumerations from ct logsmonitor db- monitors ct logs for domains in summary/domain.txtmonitor autohunt <frequency(default=5)>- starts automated hunt while monitoringsync- synchronizes the local kenzerdb with githubfreaker <module> [<target>]- runs freaker modulekenzer <module>- runs a specific modulekenzer man- shows this manual
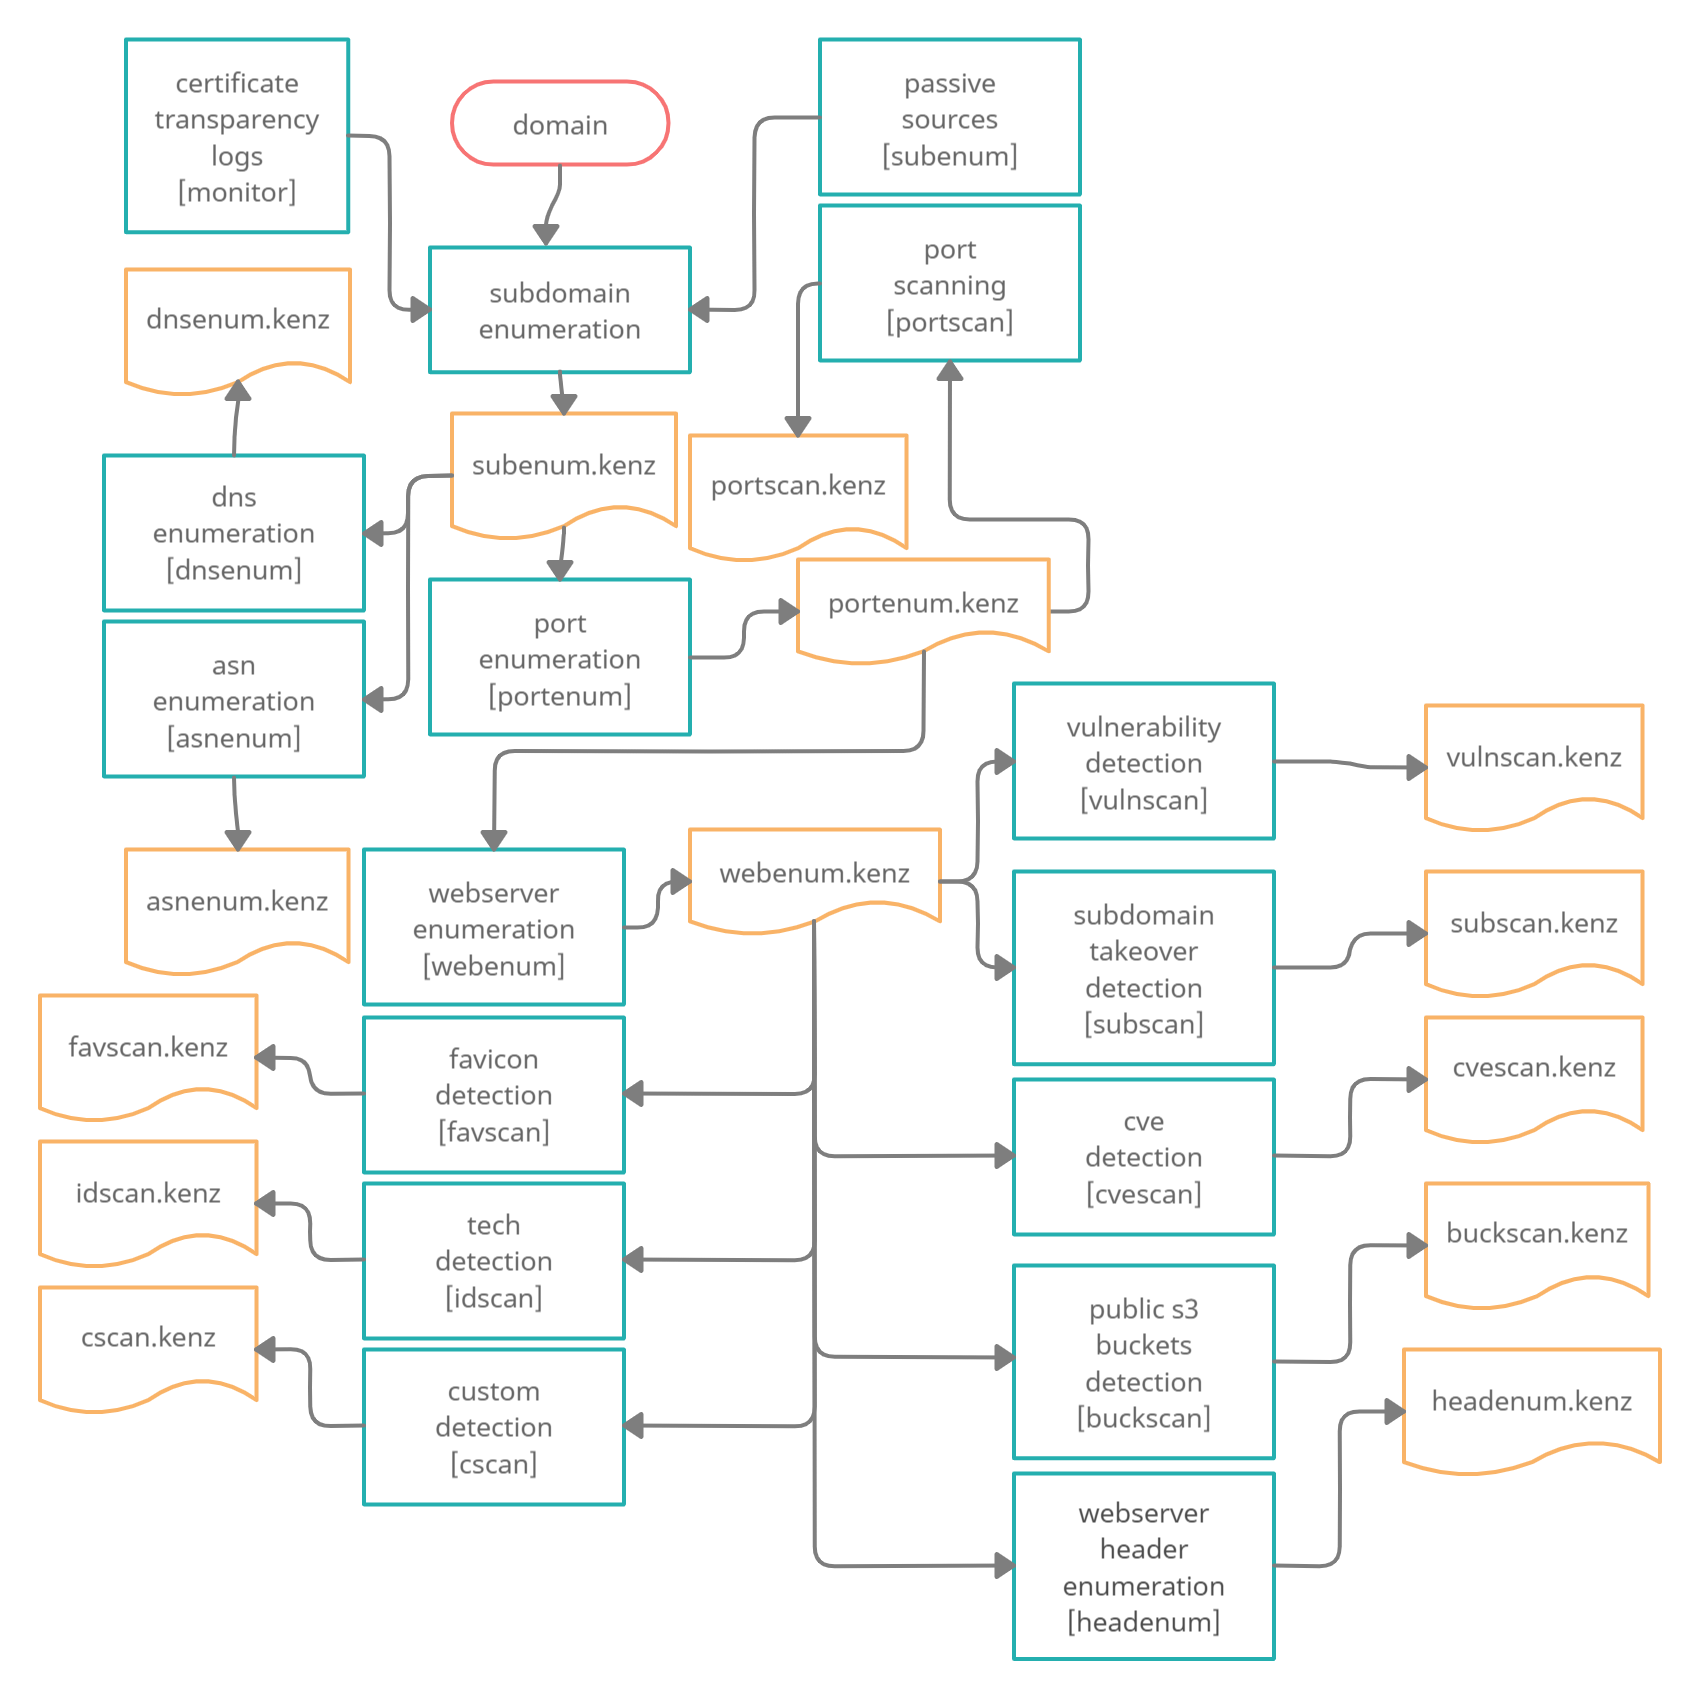
Although few more modules are available & much more is going to be released in the course of time which can advance this workflow, yet this one is enough to get started with & listed below are few of its successful hunts.

COMPATIBILITY TESTED ON UBUNTU 20.04.5 (x86_64) ONLY
RIGGED WITH LOGIC ISSUES
FEEL FREE TO SUBMIT PULL REQUESTS
