 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.

CVE-2026-89026 is the security issue targeted by this project.
This repository contains a PoC exploit and scanner for researching and validating the affected Issabel PBXAPI authentication behavior.
The project is designed for authorized security research, vulnerability validation, penetration-testing labs, and defensive assessment.
Important: Only test systems that you own or have explicit authorization to assess.
The PoC implements the authentication-forging research flow against the Issabel PBXAPI endpoint.
It includes:
The scanner supports two input modes:
[1] Single URL
[2] IP:PORT List
[0] Back
A single authorized target can be supplied, for example:
https://target.example.com:8443
A text file can contain targets in this format:
http://192.168.1.10:8443
http://192.168.1.20:443
http://10.0.0.15:8080
Targets are processed sequentially.
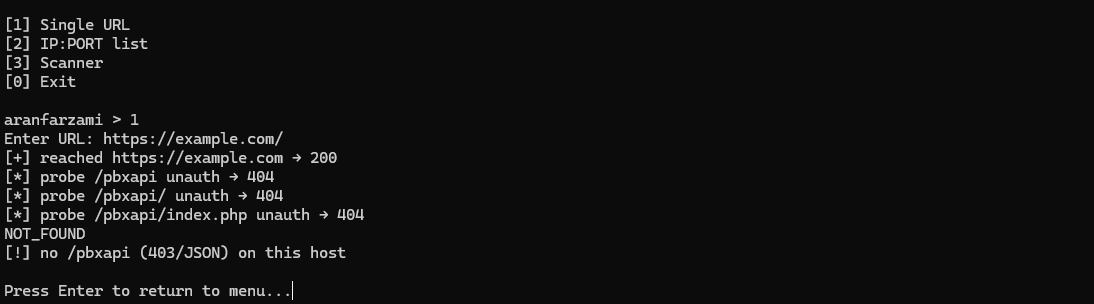
The scanner checks the Issabel /pbxapi endpoint and determines whether
the researched authentication condition is present.
Typical results:
VULNERABLE
or:
NOT_VULNERABLE
The scanner's detection path is intended to validate the authentication issue without using the optional command-execution path.
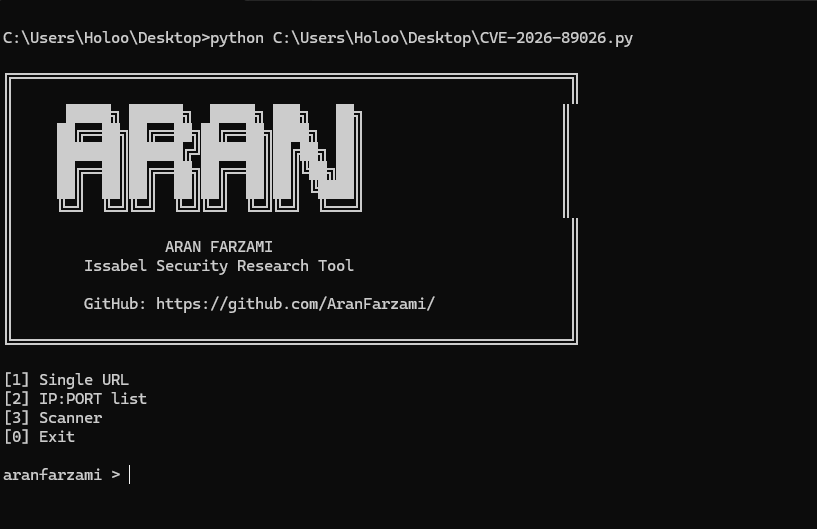
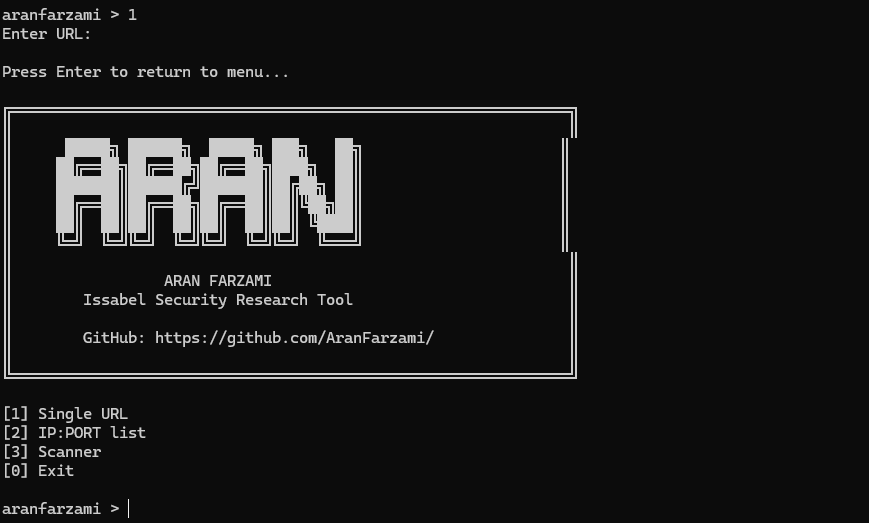
Place your screenshots in the repository's screenshots/ directory.
.
├── aranfarzami_issabel_cve_2026_89026_final.py
├── README.md
├── screenshots/
│   ├── main.png
│   ├── scanner.png
│   └── result.png
└── targets.txt
Aran Farzami
Security Researcher & Programmer
GitHub:
https://github.com/AranFarzami/
This project is provided for authorized security research and educational purposes.
Do not use this PoC or scanner against systems without explicit permission.
The author does not authorize or take responsibility for unauthorized access, disruption, data access, or other unlawful use of this project.
Choose and add an appropriate open-source license before publishing this repository.
