 aquasecurity/cloudsploit
Multi-cloud security posture scanner that audits AWS, Azure, GCP, and OCI for misconfigurations, compliance violations (HIPAA, PCI, CIS), and security risks via automated plugin-based checks.


$ git clone https://github.com/aquasecurity/cloudsploit.git
$ cd cloudsploit
$ npm install
$ ./index.js -h
$ git clone https://github.com/aquasecurity/cloudsploit.git
$ cd cloudsploit
$ docker build . -t cloudsploit:0.0.1
$ docker run cloudsploit:0.0.1 -h
$ docker run -e AWS_ACCESS_KEY_ID=XX -e AWS_SECRET_ACCESS_KEY=YY cloudsploit:0.0.1 --compliance=pci
CloudSploit by Aqua is an open-source project designed to allow detection of security risks in cloud infrastructure accounts, including: Amazon Web Services (AWS), Microsoft Azure, Google Cloud Platform (GCP), Oracle Cloud Infrastructure (OCI), and GitHub. These scripts are designed to return a series of potential misconfigurations and security risks.
CloudSploit is available in two deployment options:
Follow the instructions below to deploy the open-source version of CloudSploit on your machine in just a few simple steps.
A commercial version of CloudSploit hosted at Aqua Wave. Try Aqua Wave today!
Ensure that NodeJS is installed. If not, install it from here.
$ git clone [email protected]:cloudsploit/scans.git
$ npm install
CloudSploit requires read-only permission to your cloud account. Follow the guides below to provision this access:
For AWS, you can run CloudSploit directly and it will detect credentials using the default AWS credential chain.
The CloudSploit config file allows you to pass cloud provider credentials by:
Start by copying the example config file:
$ cp config_example.js config.js
Edit the config file by uncommenting the relevant sections for the cloud provider you are testing. Each cloud has both a credential_file option, as well as inline options. For example:
azure: {
    // OPTION 1: If using a credential JSON file, enter the path below
    // credential_file: '/path/to/file.json',
    // OPTION 2: If using hard-coded credentials, enter them below
    // application_id: process.env.AZURE_APPLICATION_ID || '',
    // key_value: process.env.AZURE_KEY_VALUE || '',
    // directory_id: process.env.AZURE_DIRECTORY_ID || '',
    // subscription_id: process.env.AZURE_SUBSCRIPTION_ID || ''
}
If you use the credential_file option, point to a file in your file system that follows the correct format for the cloud you are using.
{
  "accessKeyId": "YOURACCESSKEY",
  "secretAccessKey": "YOURSECRETKEY"
}
{
  "ApplicationID": "YOURAZUREAPPLICATIONID",
  "KeyValue": "YOURAZUREKEYVALUE",
  "DirectoryID": "YOURAZUREDIRECTORYID",
  "SubscriptionID": "YOURAZURESUBSCRIPTIONID"
}
Note: For GCP, you generate a JSON file directly from the GCP console, which you should not edit.
{
    "type": "service_account",
    "project": "GCPPROJECTNAME",
    "client_email": "GCPCLIENTEMAIL",
    "private_key": "GCPPRIVATEKEY"
}
{
  "tenancyId": "YOURORACLETENANCYID",
  "compartmentId": "YOURORACLECOMPARTMENTID",
  "userId": "YOURORACLEUSERID",
  "keyFingerprint": "YOURORACLEKEYFINGERPRINT",
  "keyValue": "YOURORACLEKEYVALUE",
}
CloudSploit supports passing environment variables, but you must first uncomment the section of your config.js file relevant to the cloud provider being scanned.
You can then pass the variables listed in each section. For example, for AWS:
{
  access_key: process.env.AWS_ACCESS_KEY_ID || '',
  secret_access_key: process.env.AWS_SECRET_ACCESS_KEY || '',
  session_token: process.env.AWS_SESSION_TOKEN || '',
}
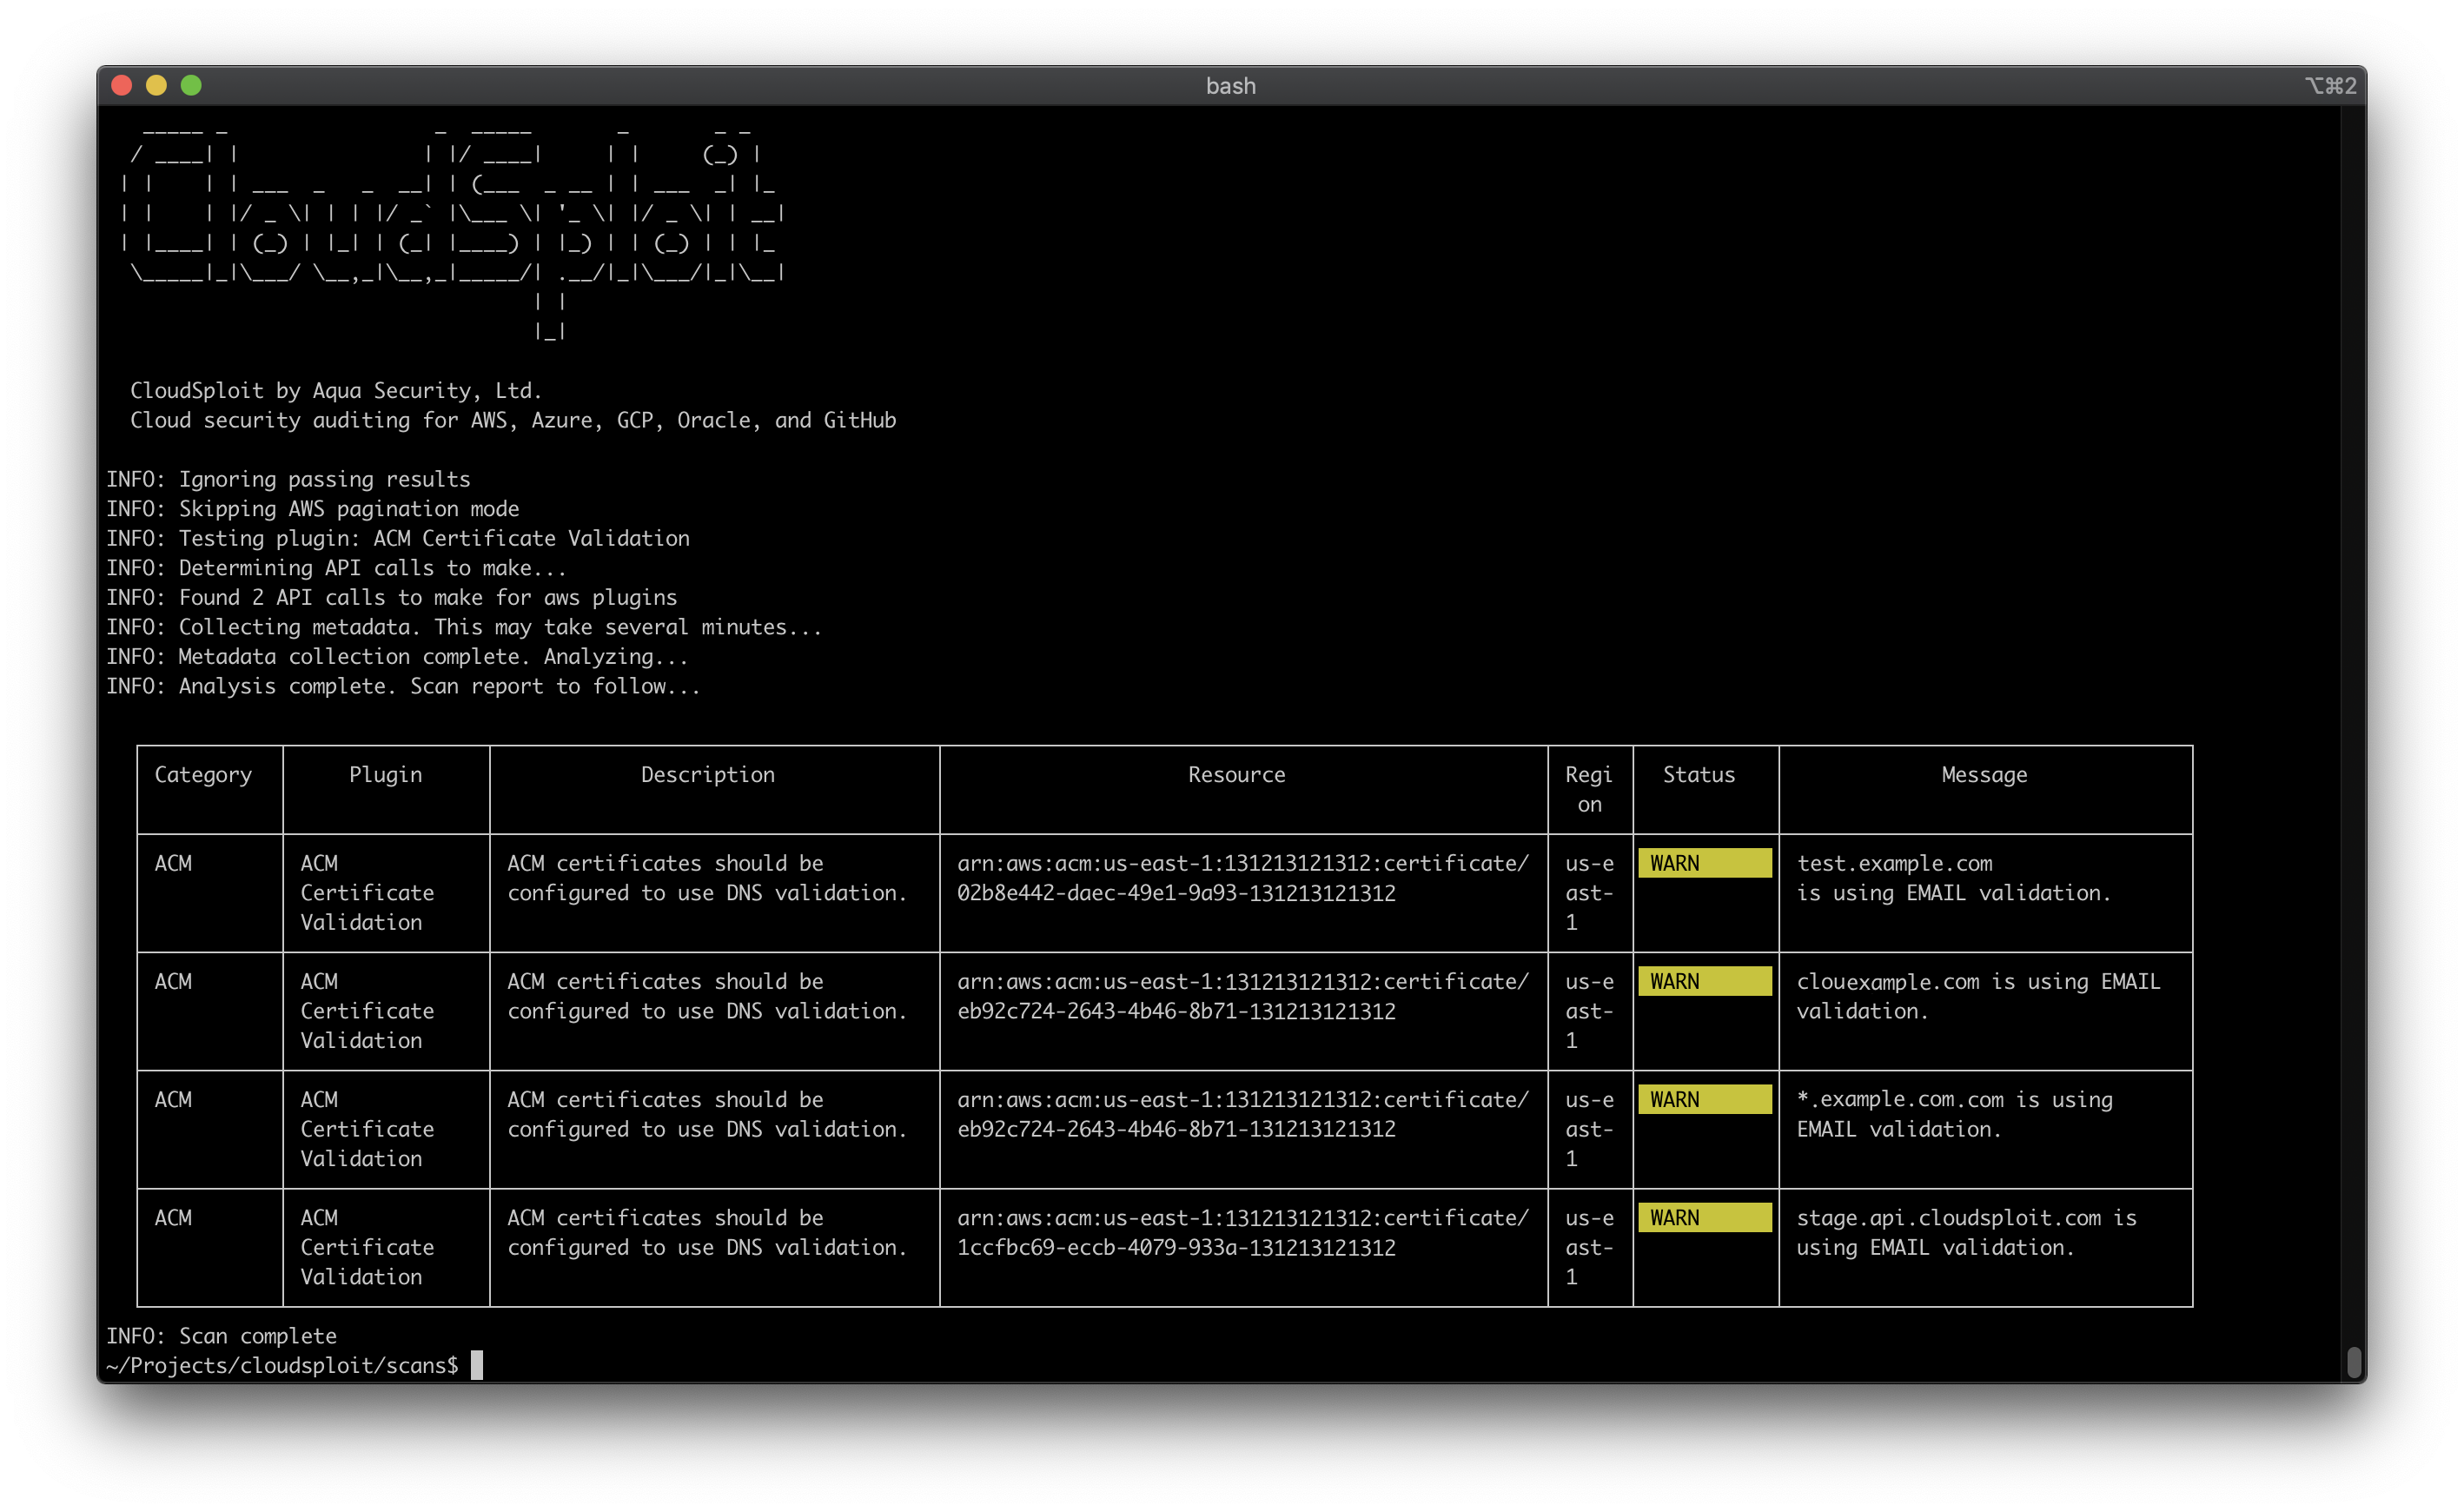
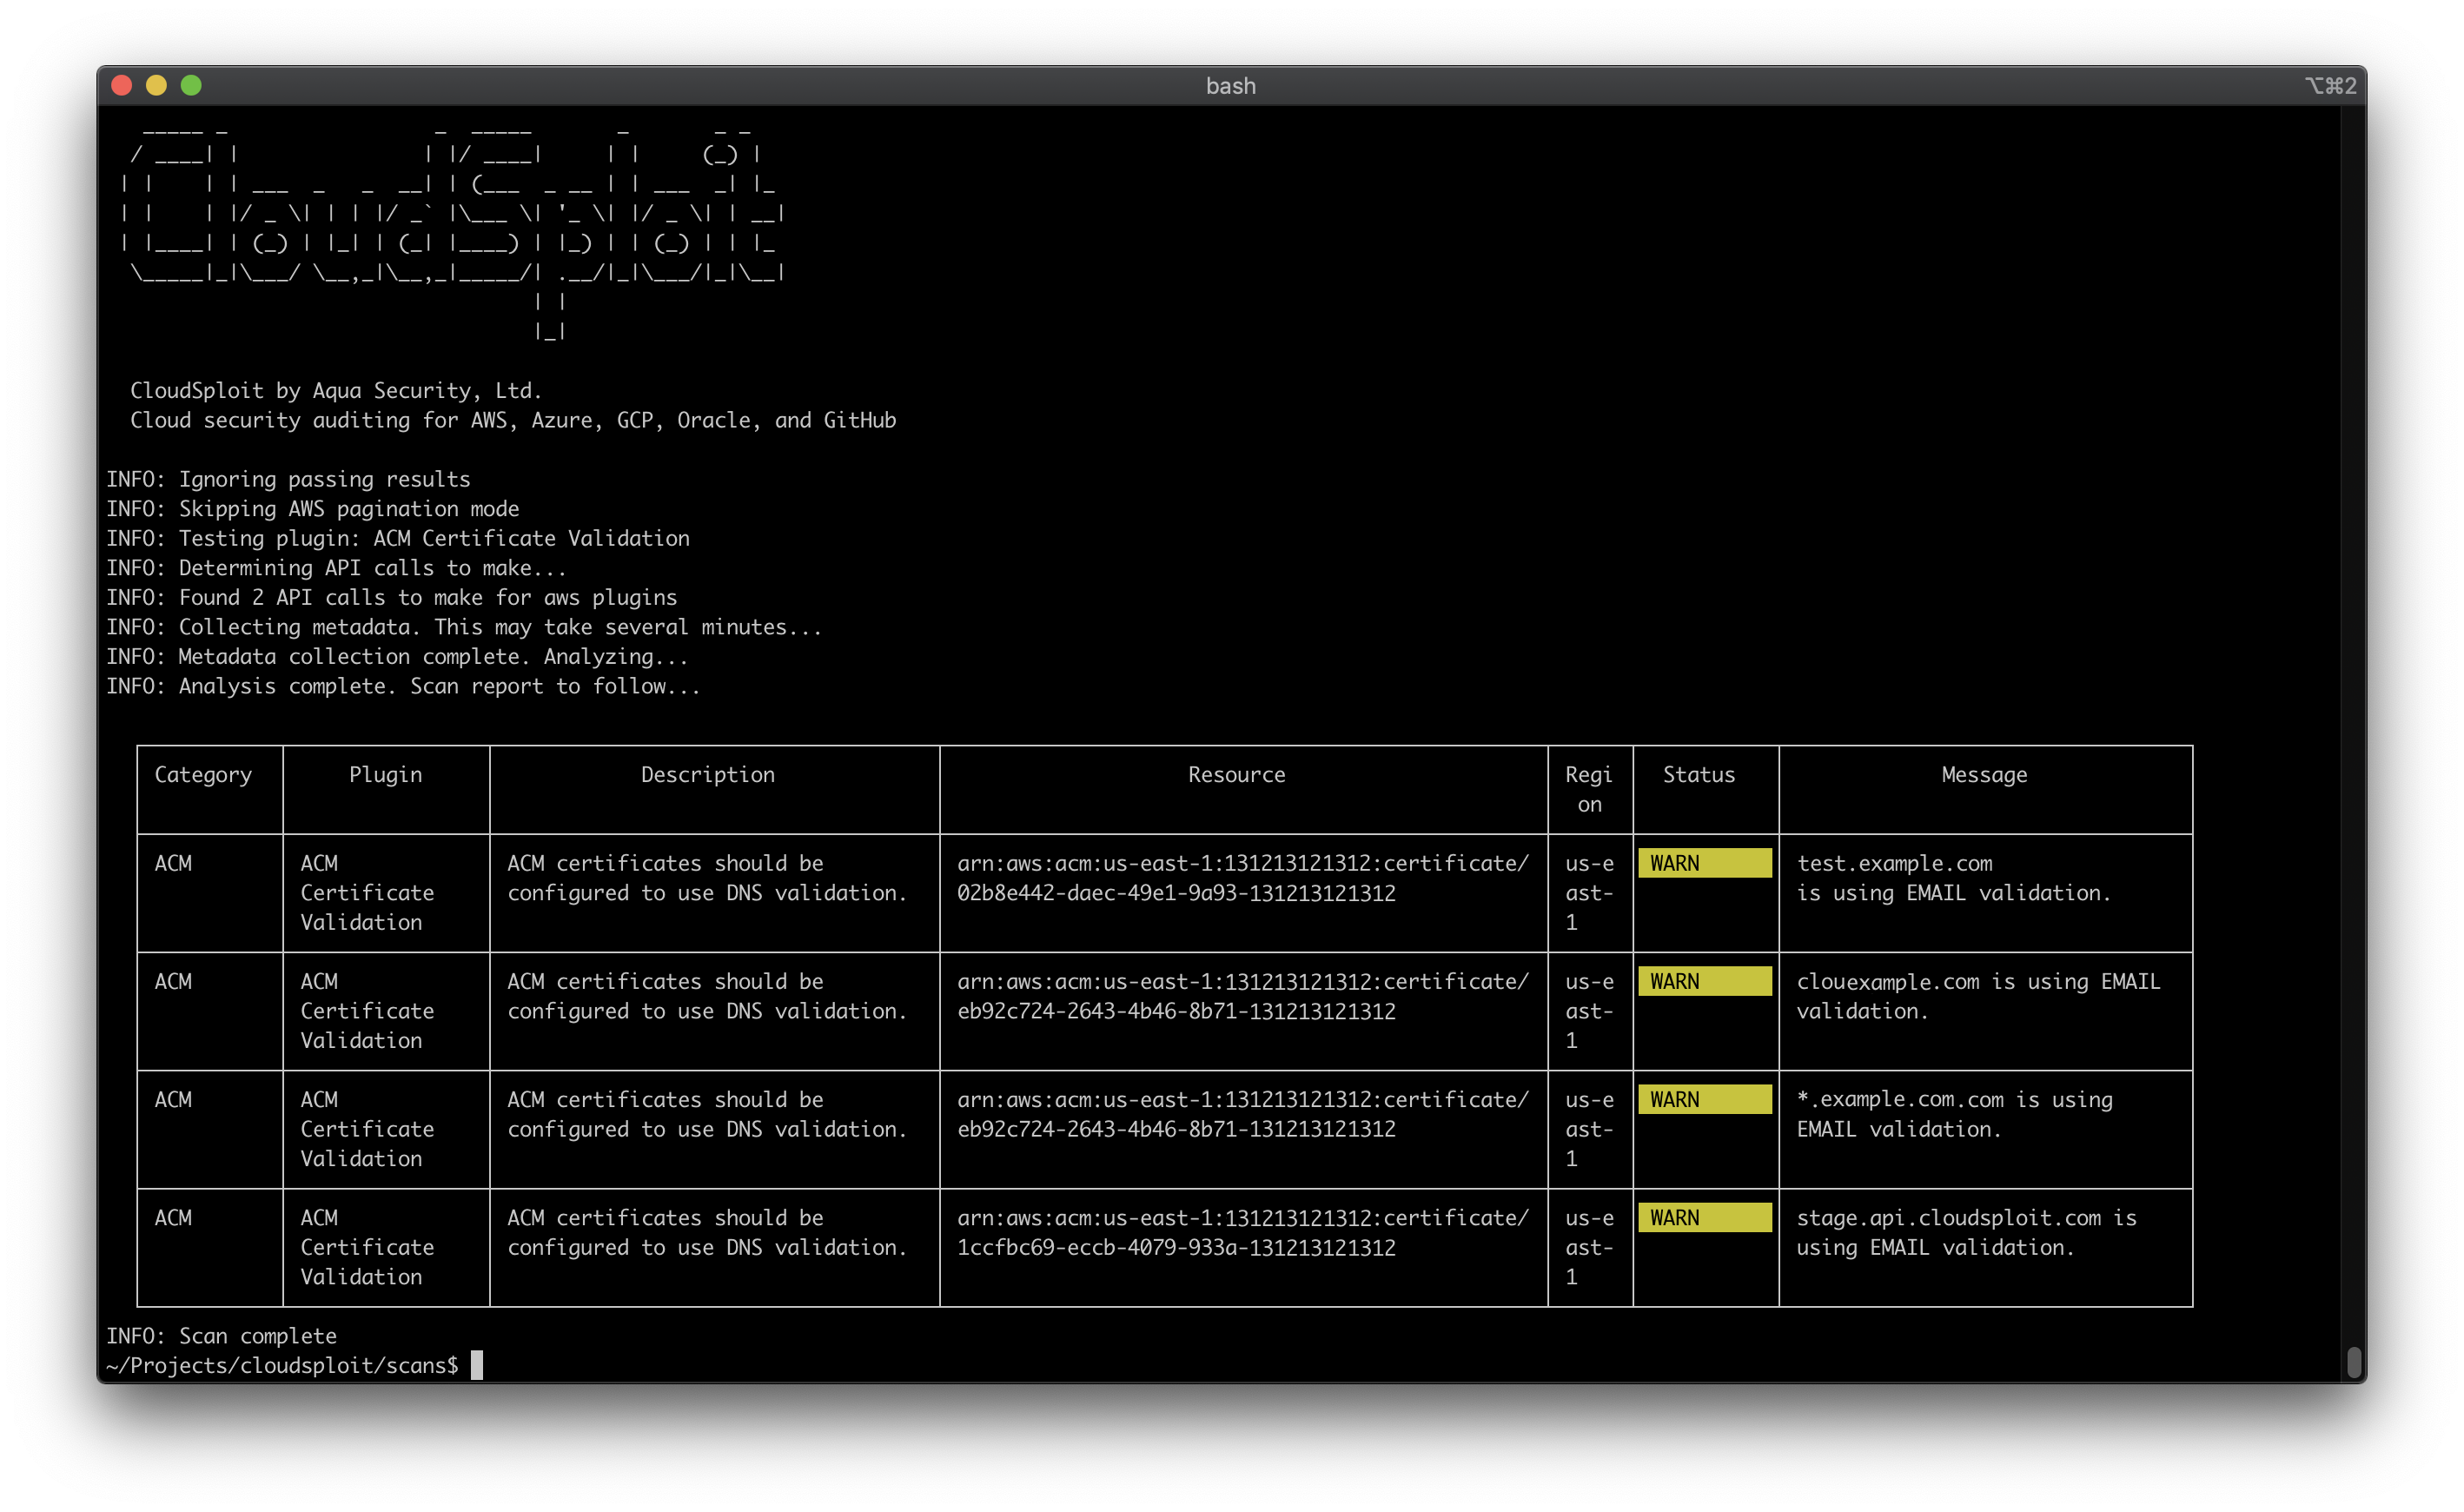
To run a standard scan, showing all outputs and results, simply run:
$ ./index.js
CloudSploit supports many options to customize the run time. Some popular options include:
--govcloud--china--collection=file.json--ignore-ok--exit-code
--console=textSee Output Formats below for more output options.
$ ./index.js -h

  _____ _                 _  _____       _       _ _
  / ____| |               | |/ ____|     | |     (_) |
| |    | | ___  _   _  __| | (___  _ __ | | ___  _| |_
| |    | |/ _ \| | | |/ _` |\___ \| '_ \| |/ _ \| | __|
| |____| | (_) | |_| | (_| |____) | |_) | | (_) | | |_
  \_____|_|\___/ \__,_|\__,_|_____/| .__/|_|\___/|_|\__|
                                  | |
                                  |_|

  CloudSploit by Aqua Security, Ltd.
  Cloud security auditing for AWS, Azure, GCP, Oracle, and GitHub
