 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD pipelines for risks.

[📖 Documentation][docs]
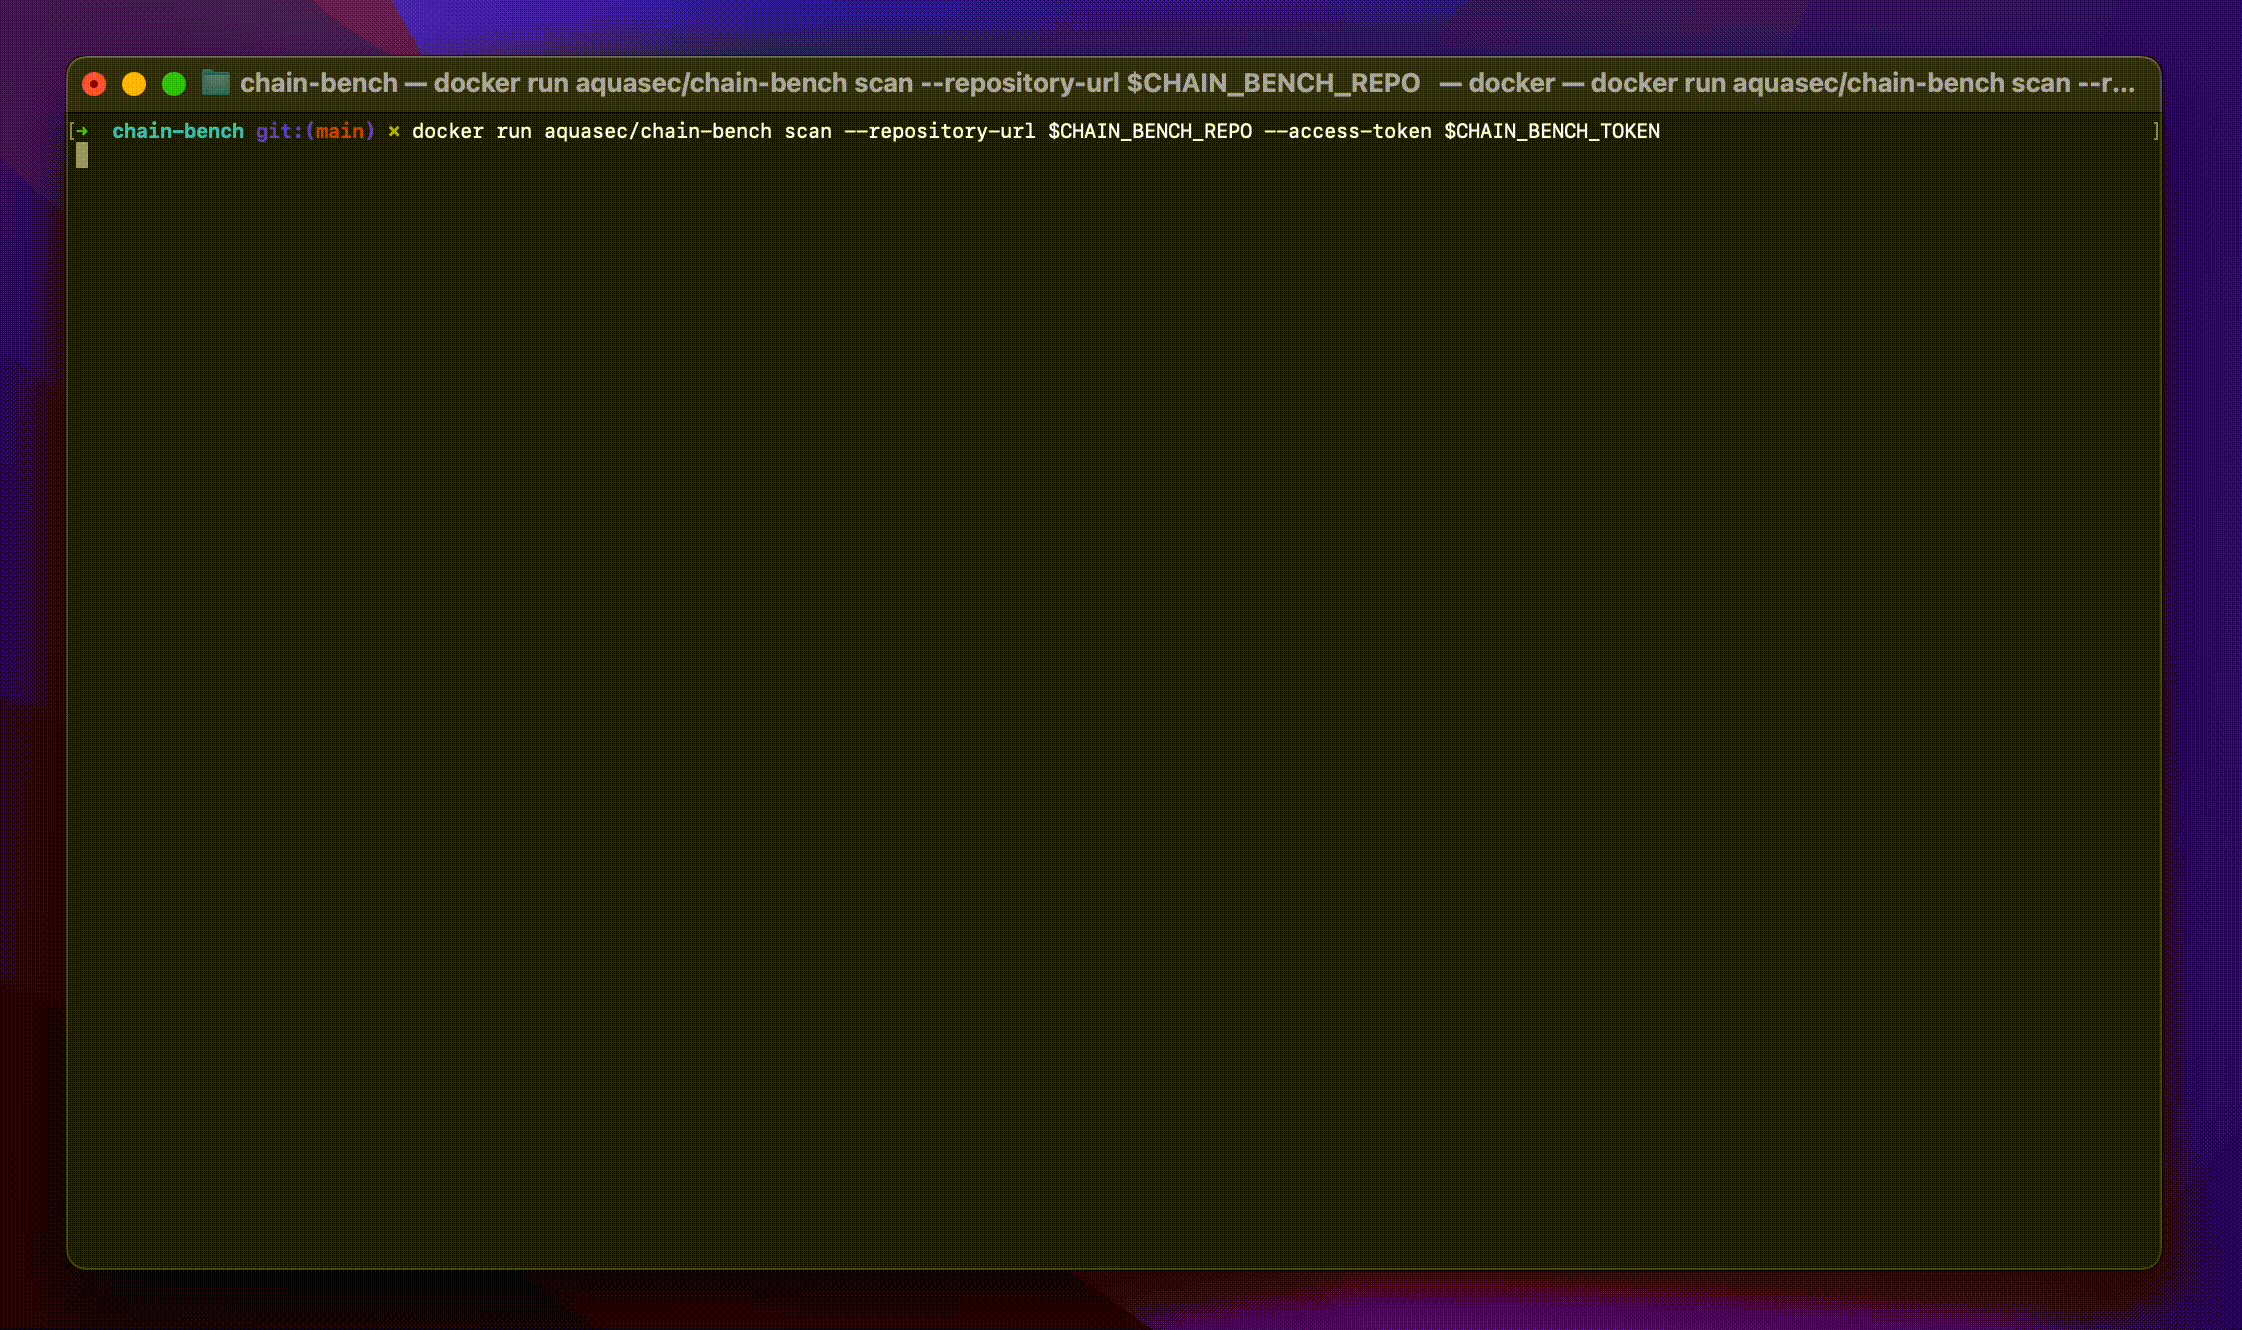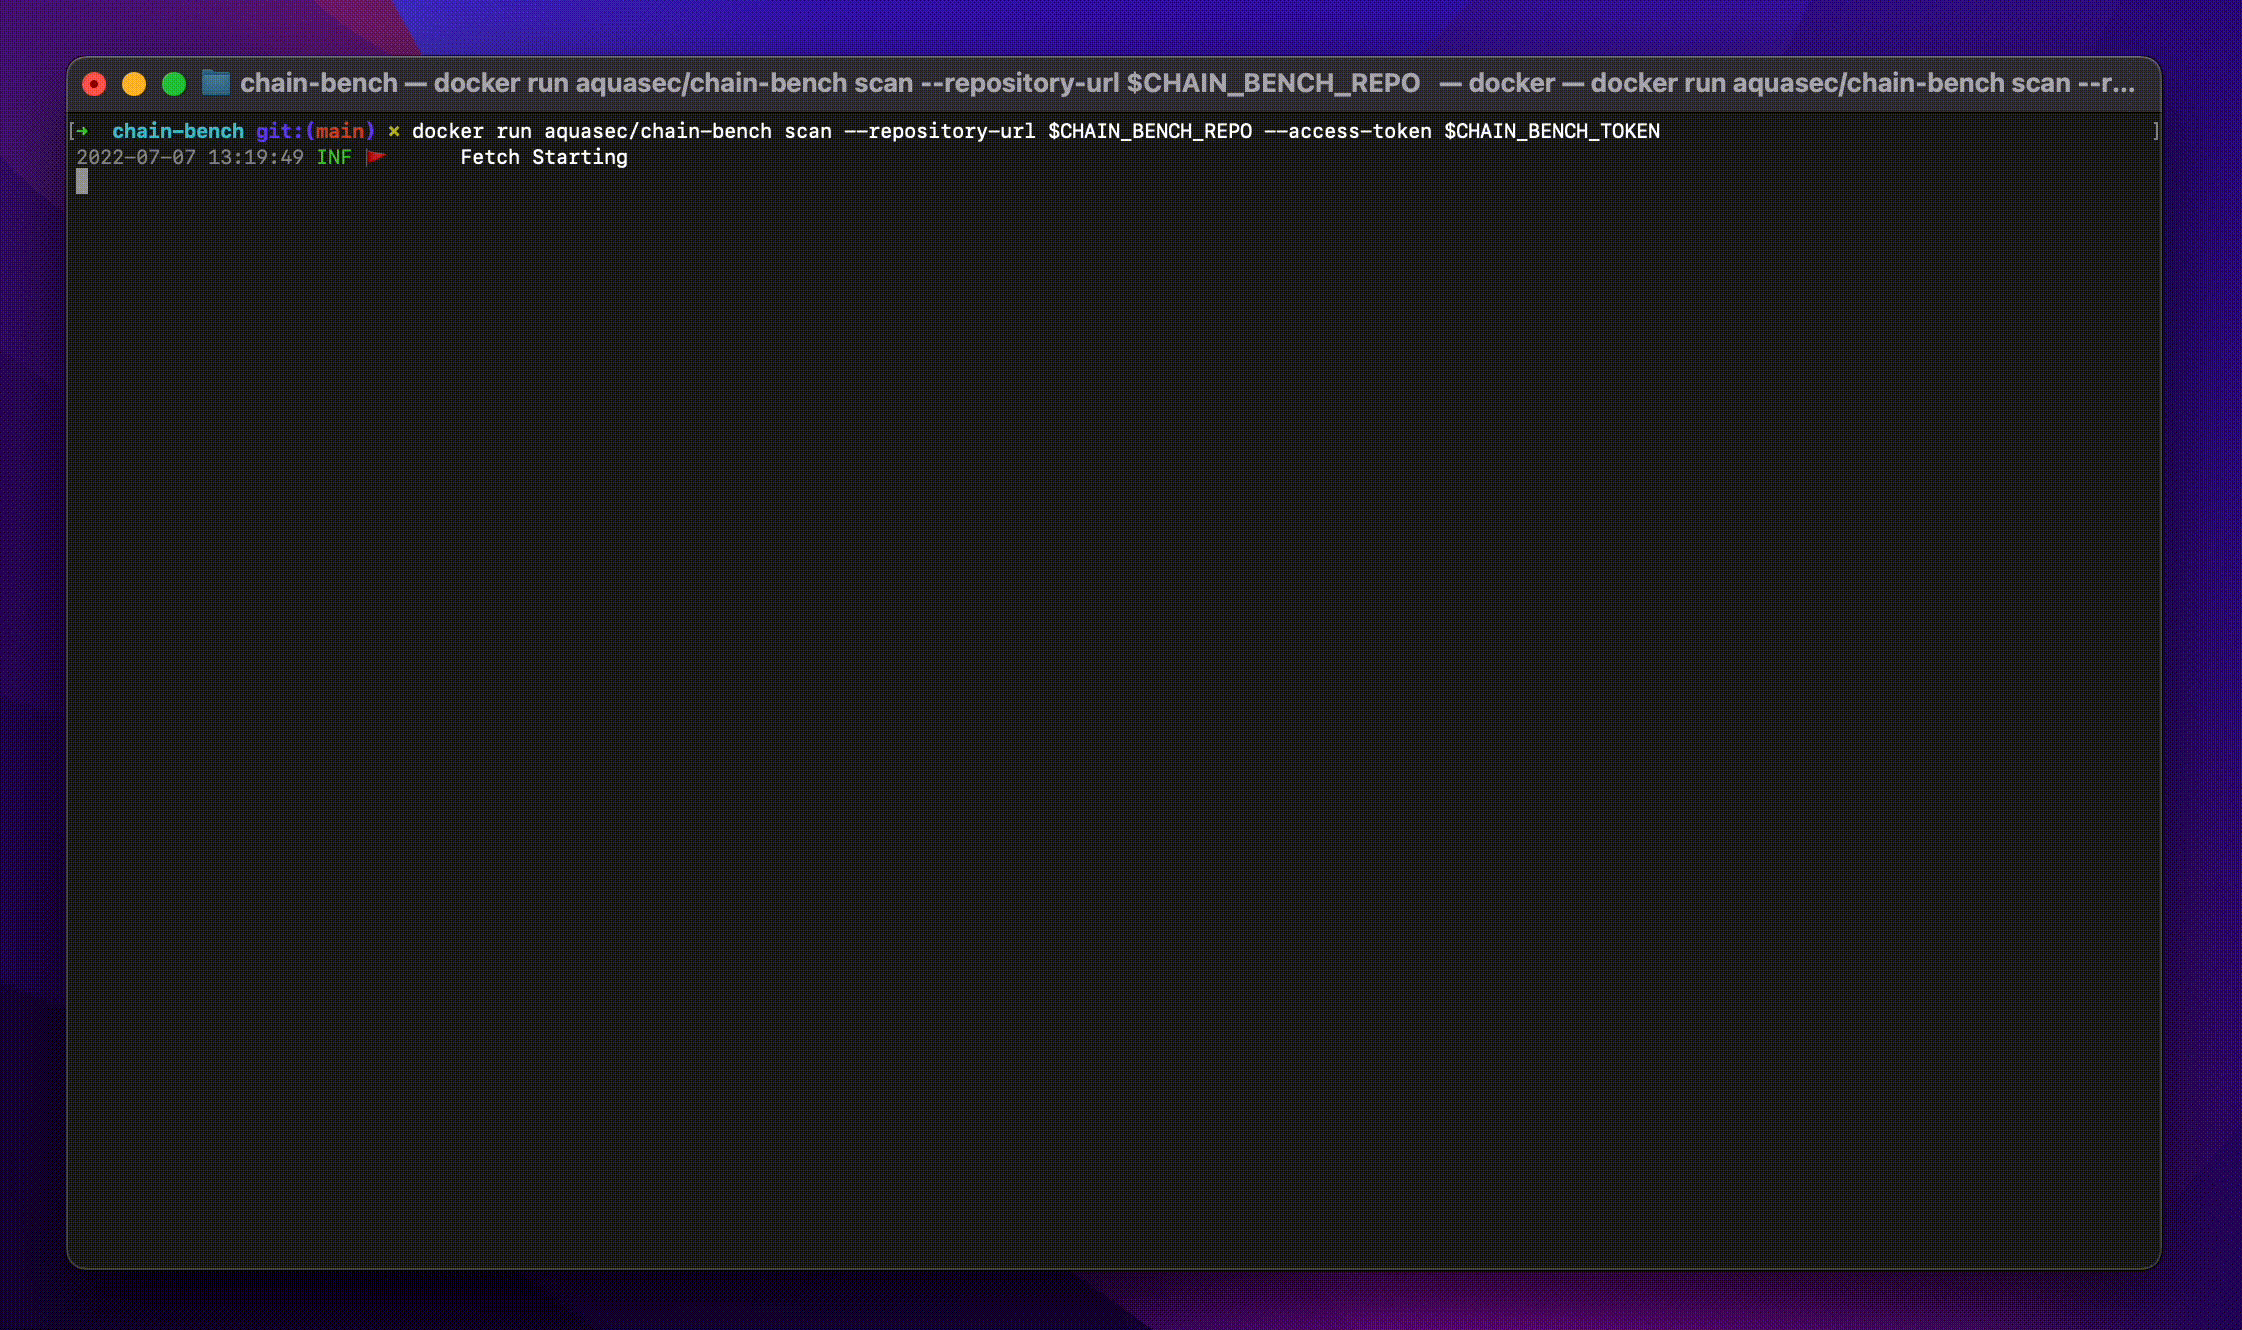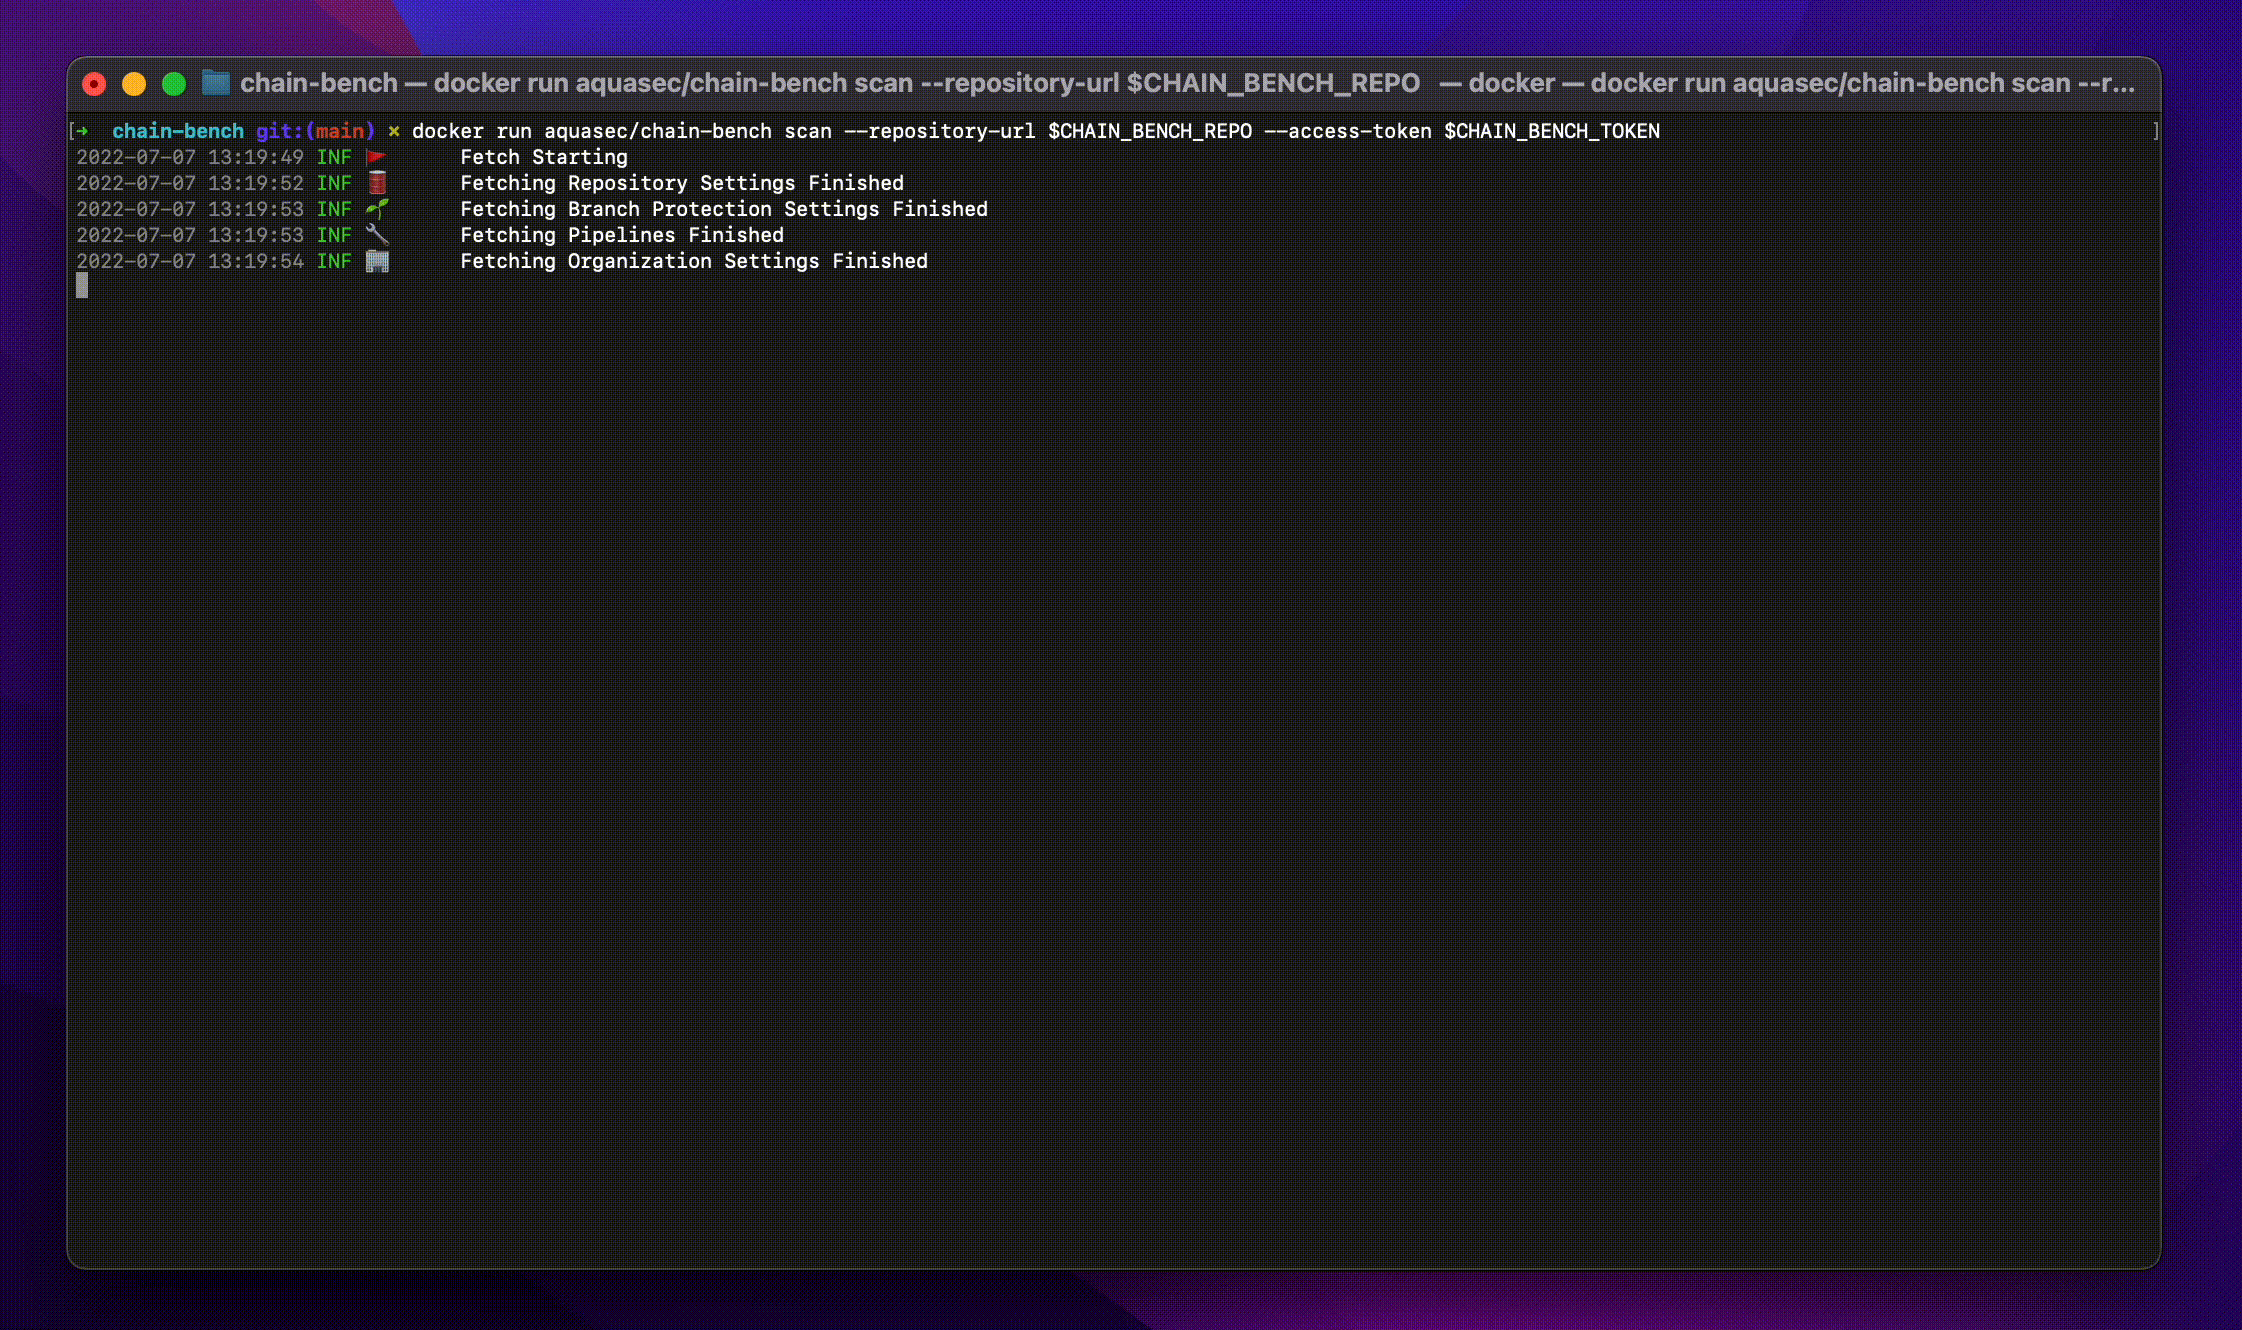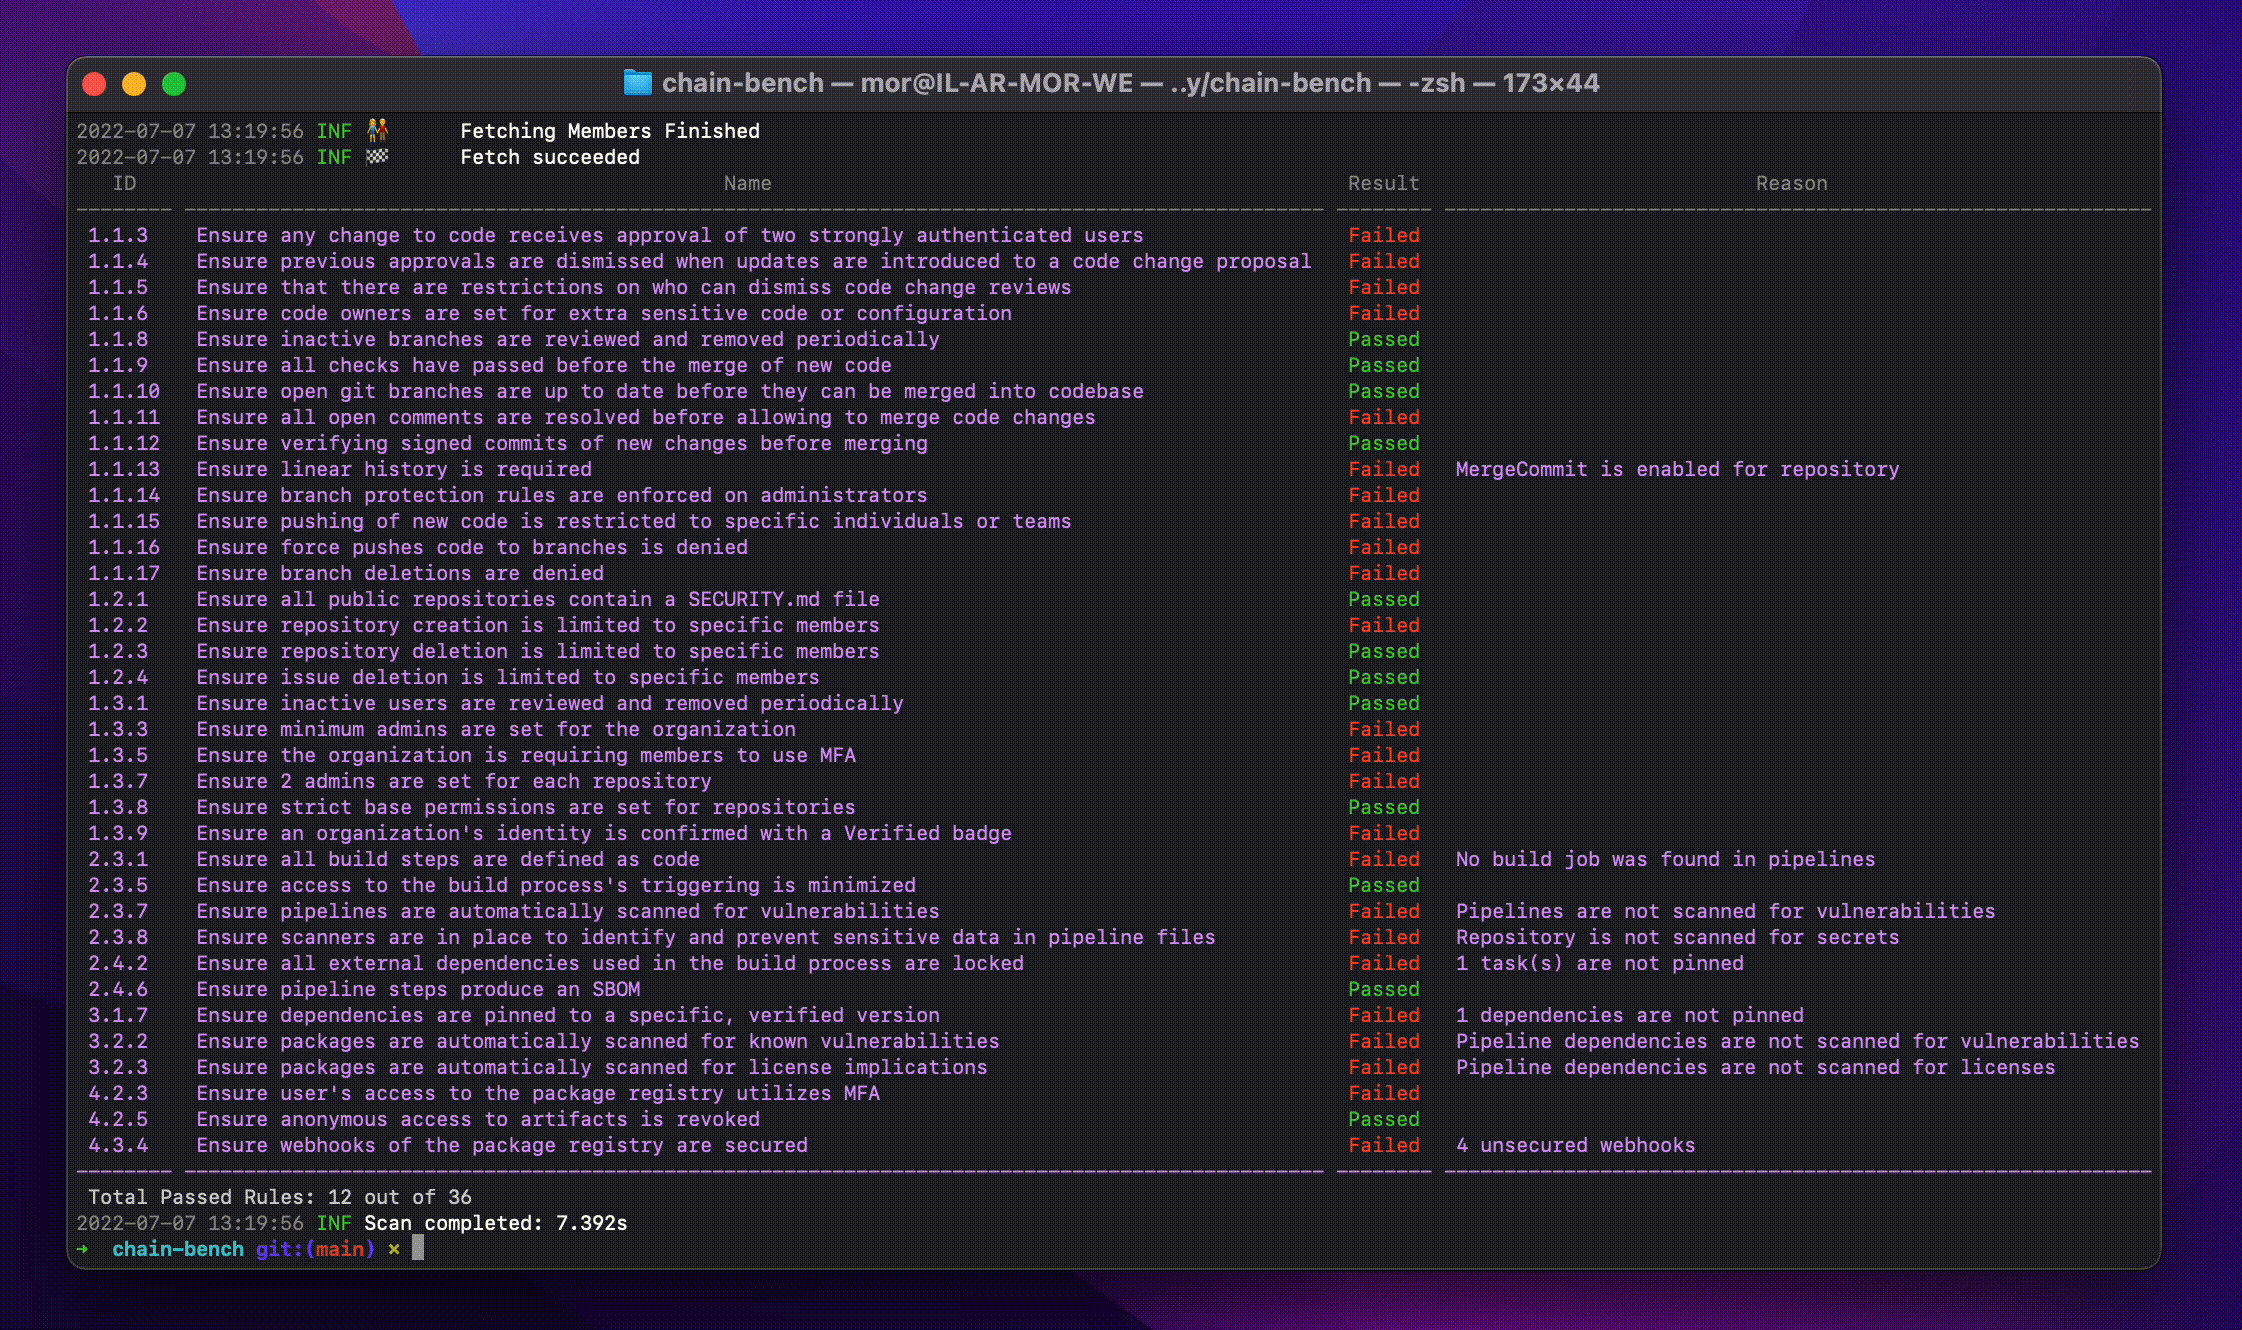
Chain-bench is an open-source tool for auditing your software supply chain stack for security compliance based on a new CIS Software Supply Chain benchmark. The auditing focuses on the entire SDLC process, where it can reveal risks from code time into deploy time. To win the race against hackers and protect your sensitive data and customer trust, you need to ensure your code is compliant with your organization’s policies.
Read more in the [Chain-bench Documentation][docs]


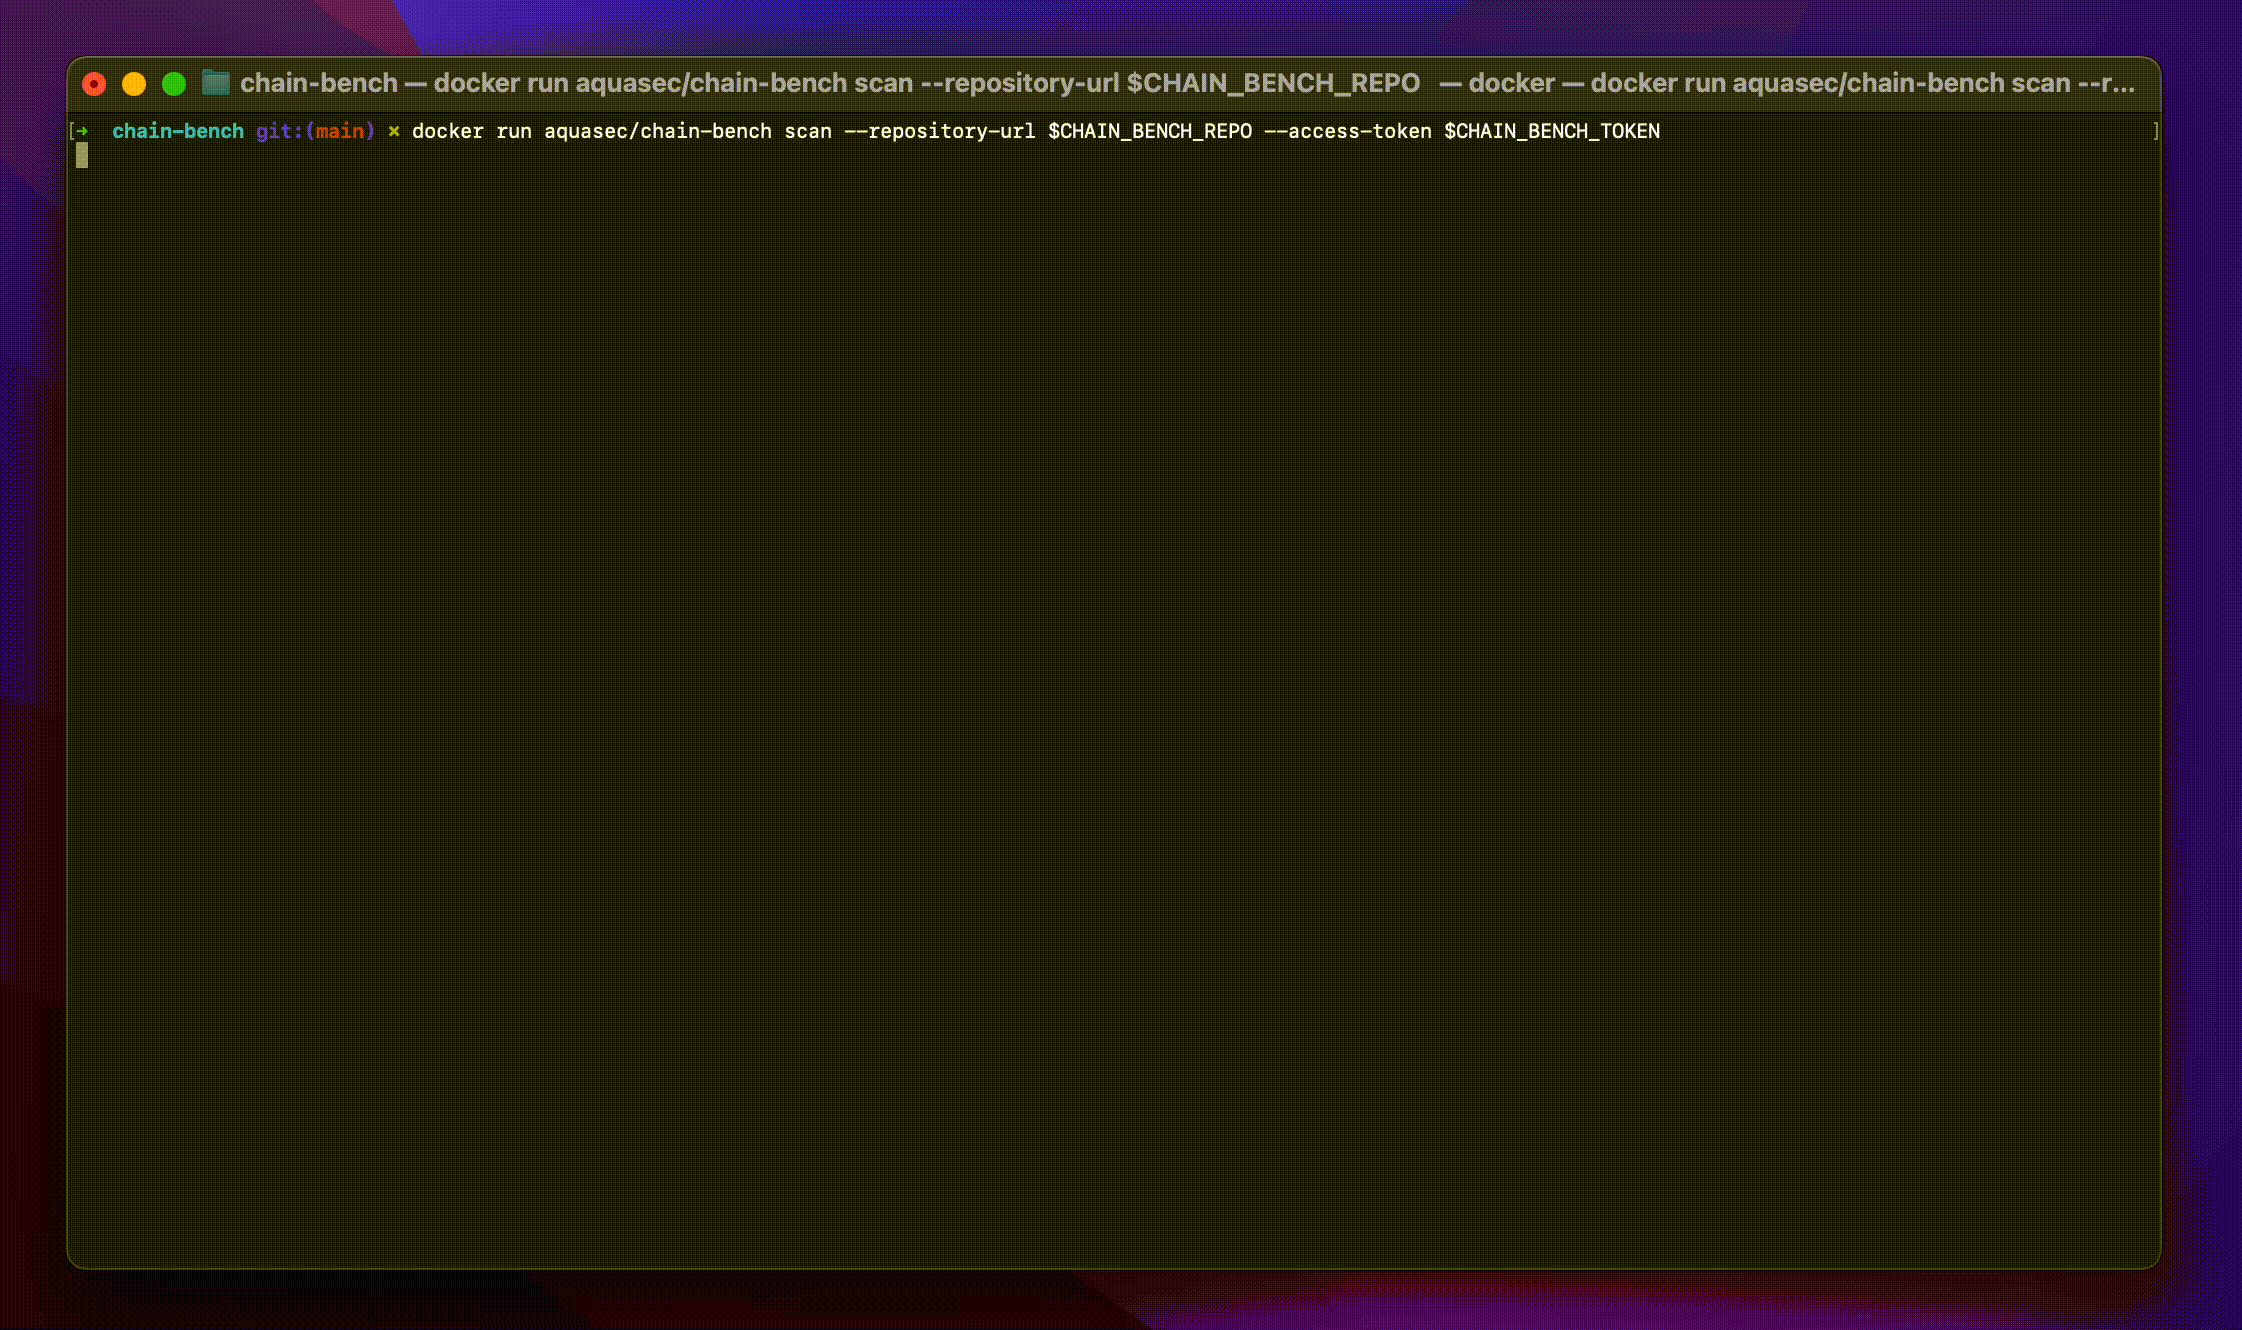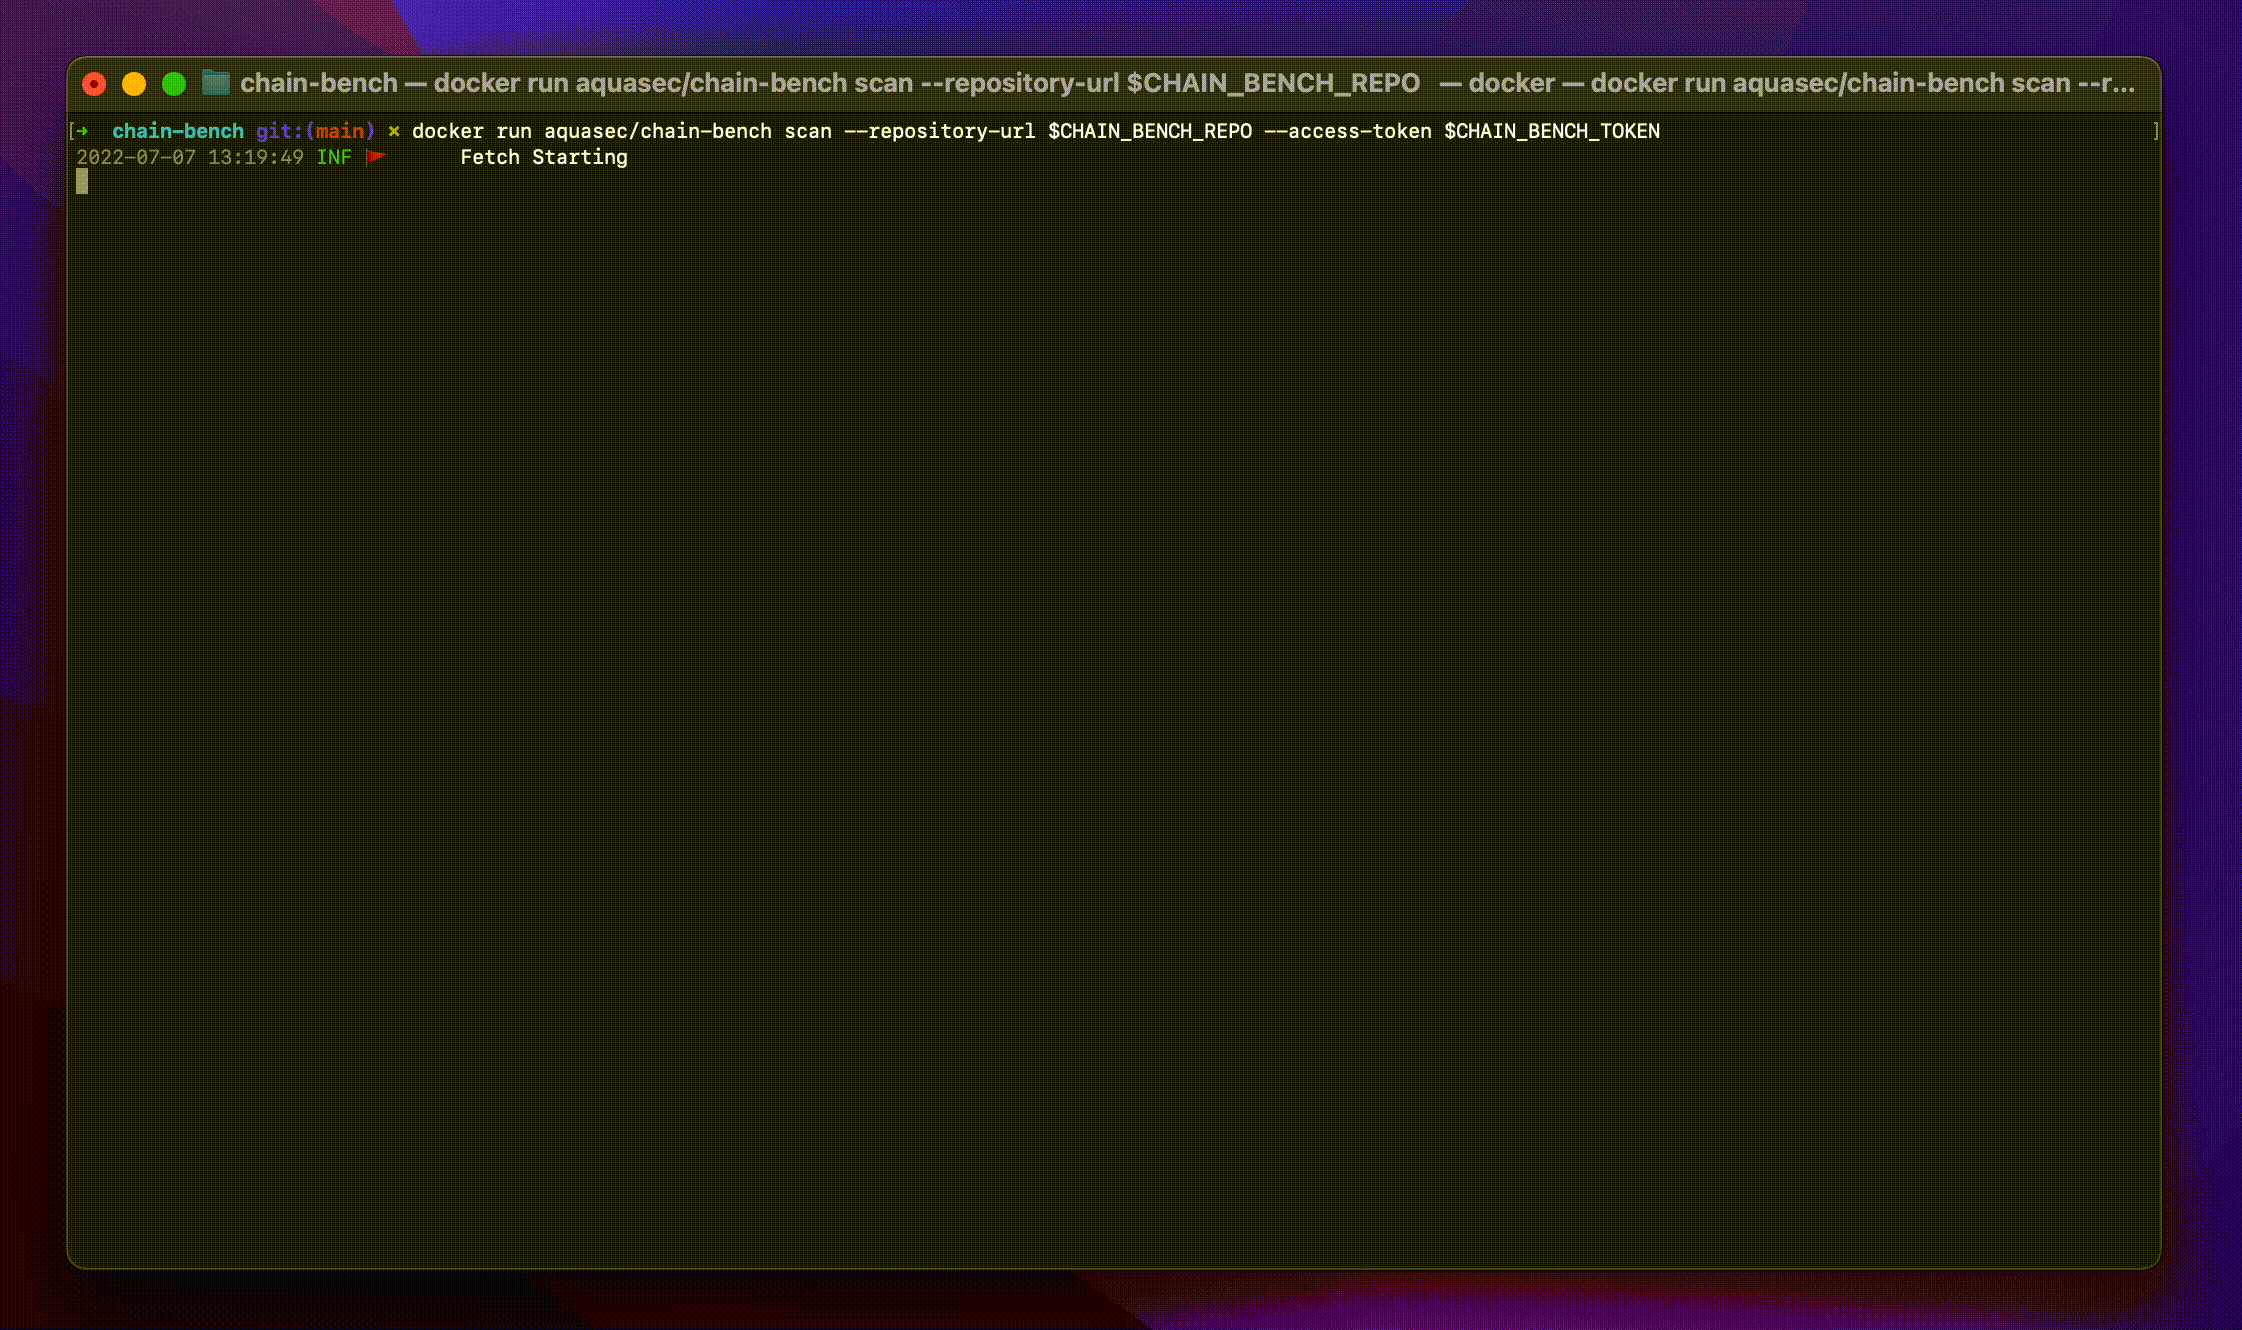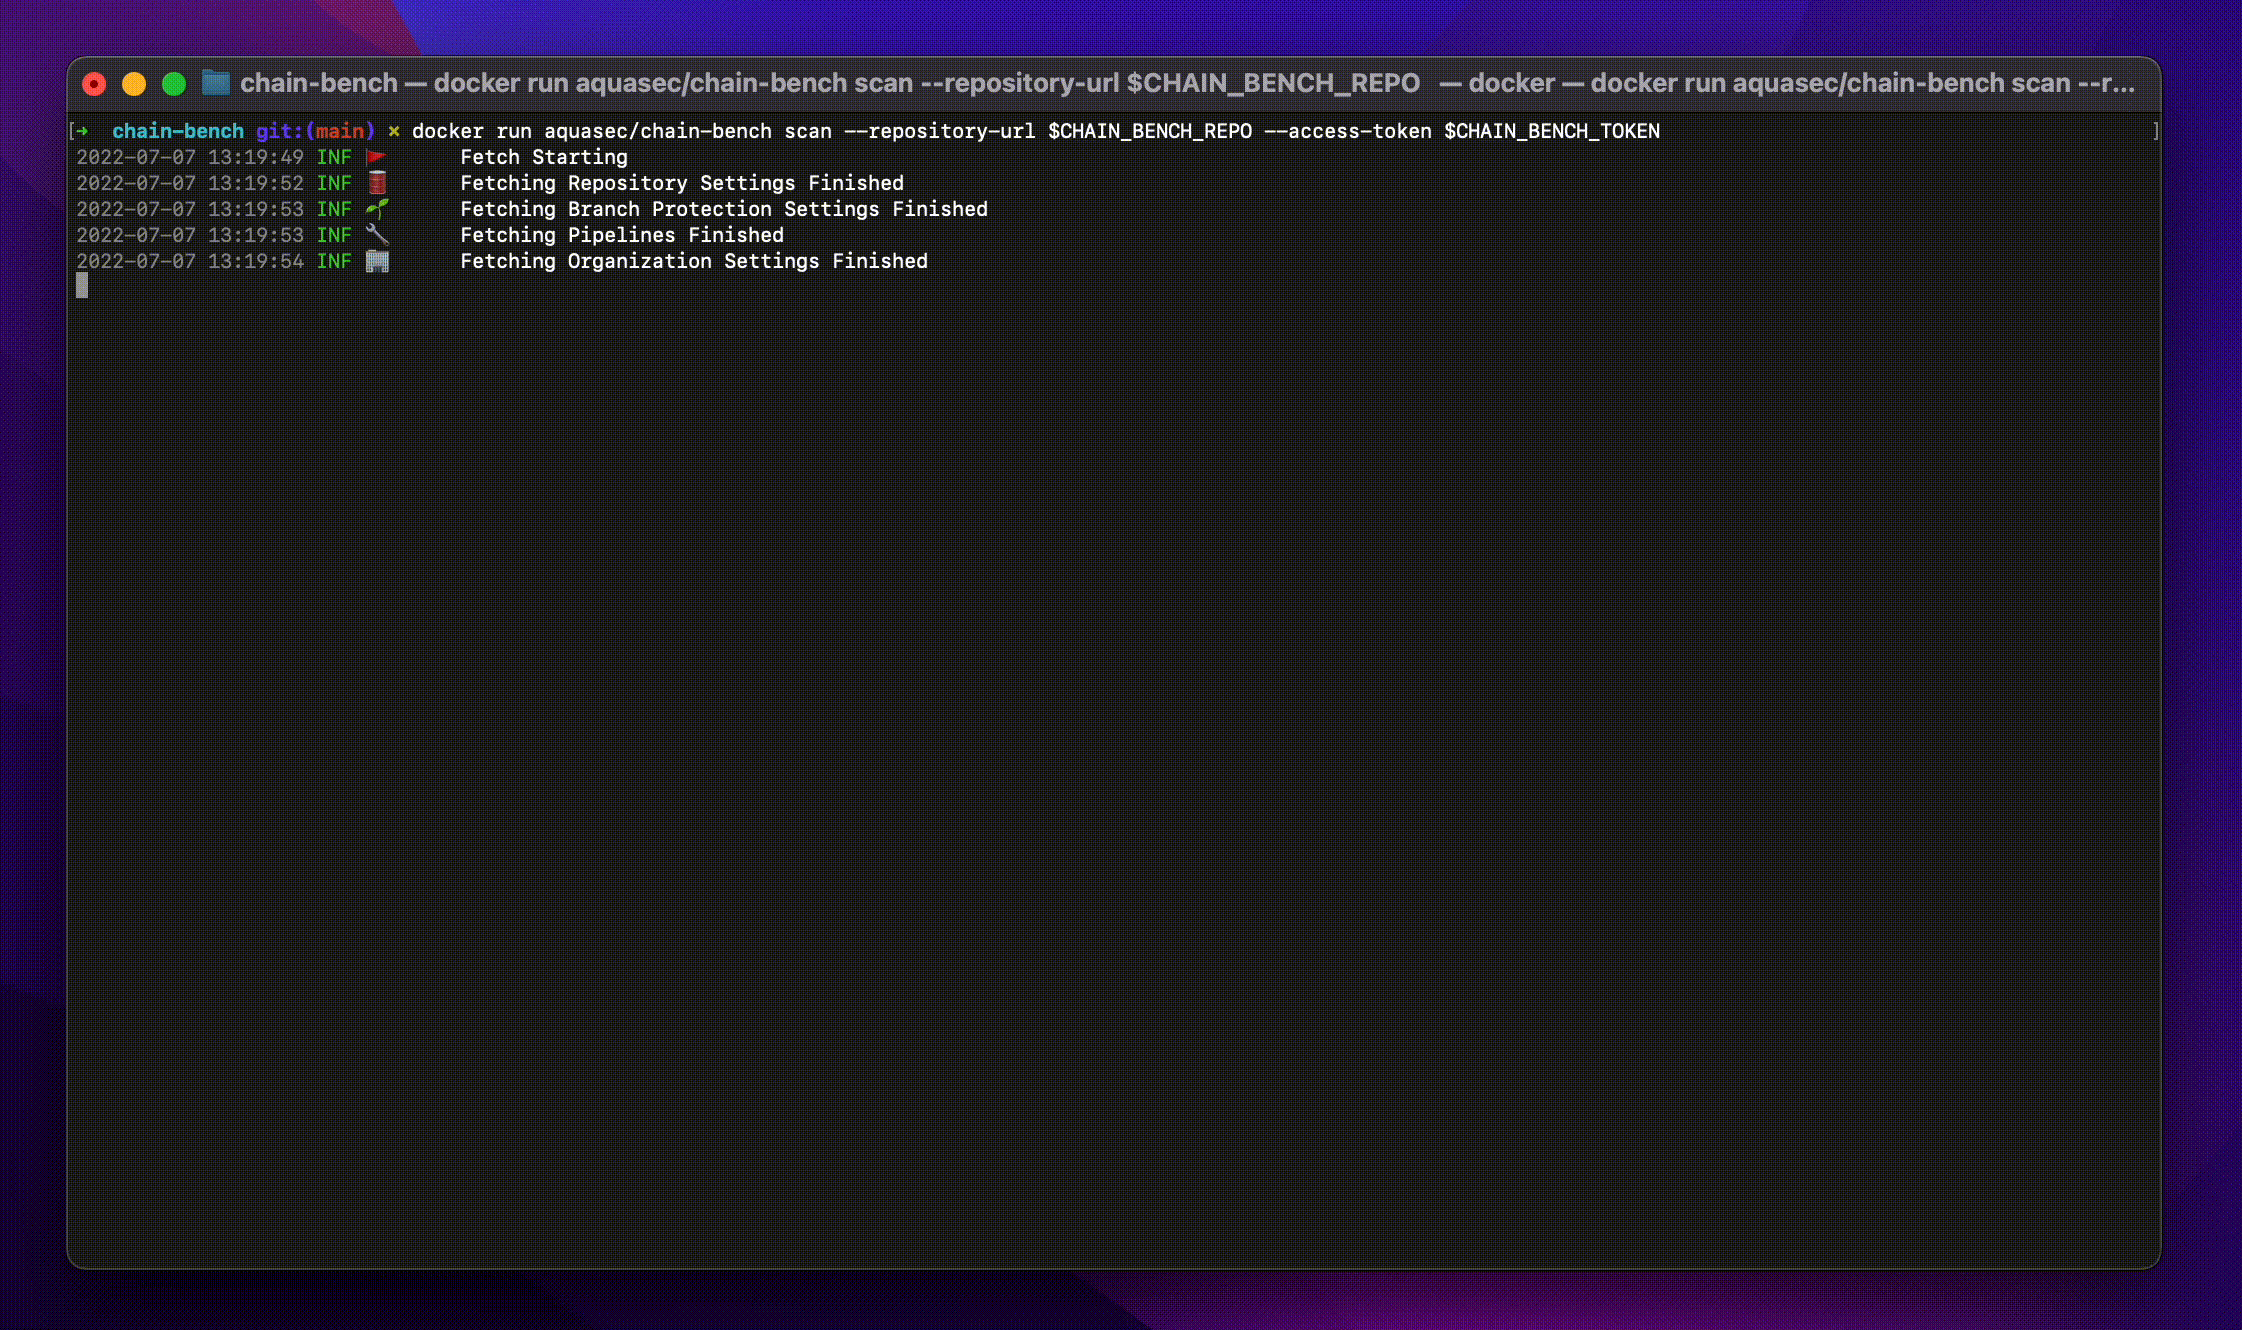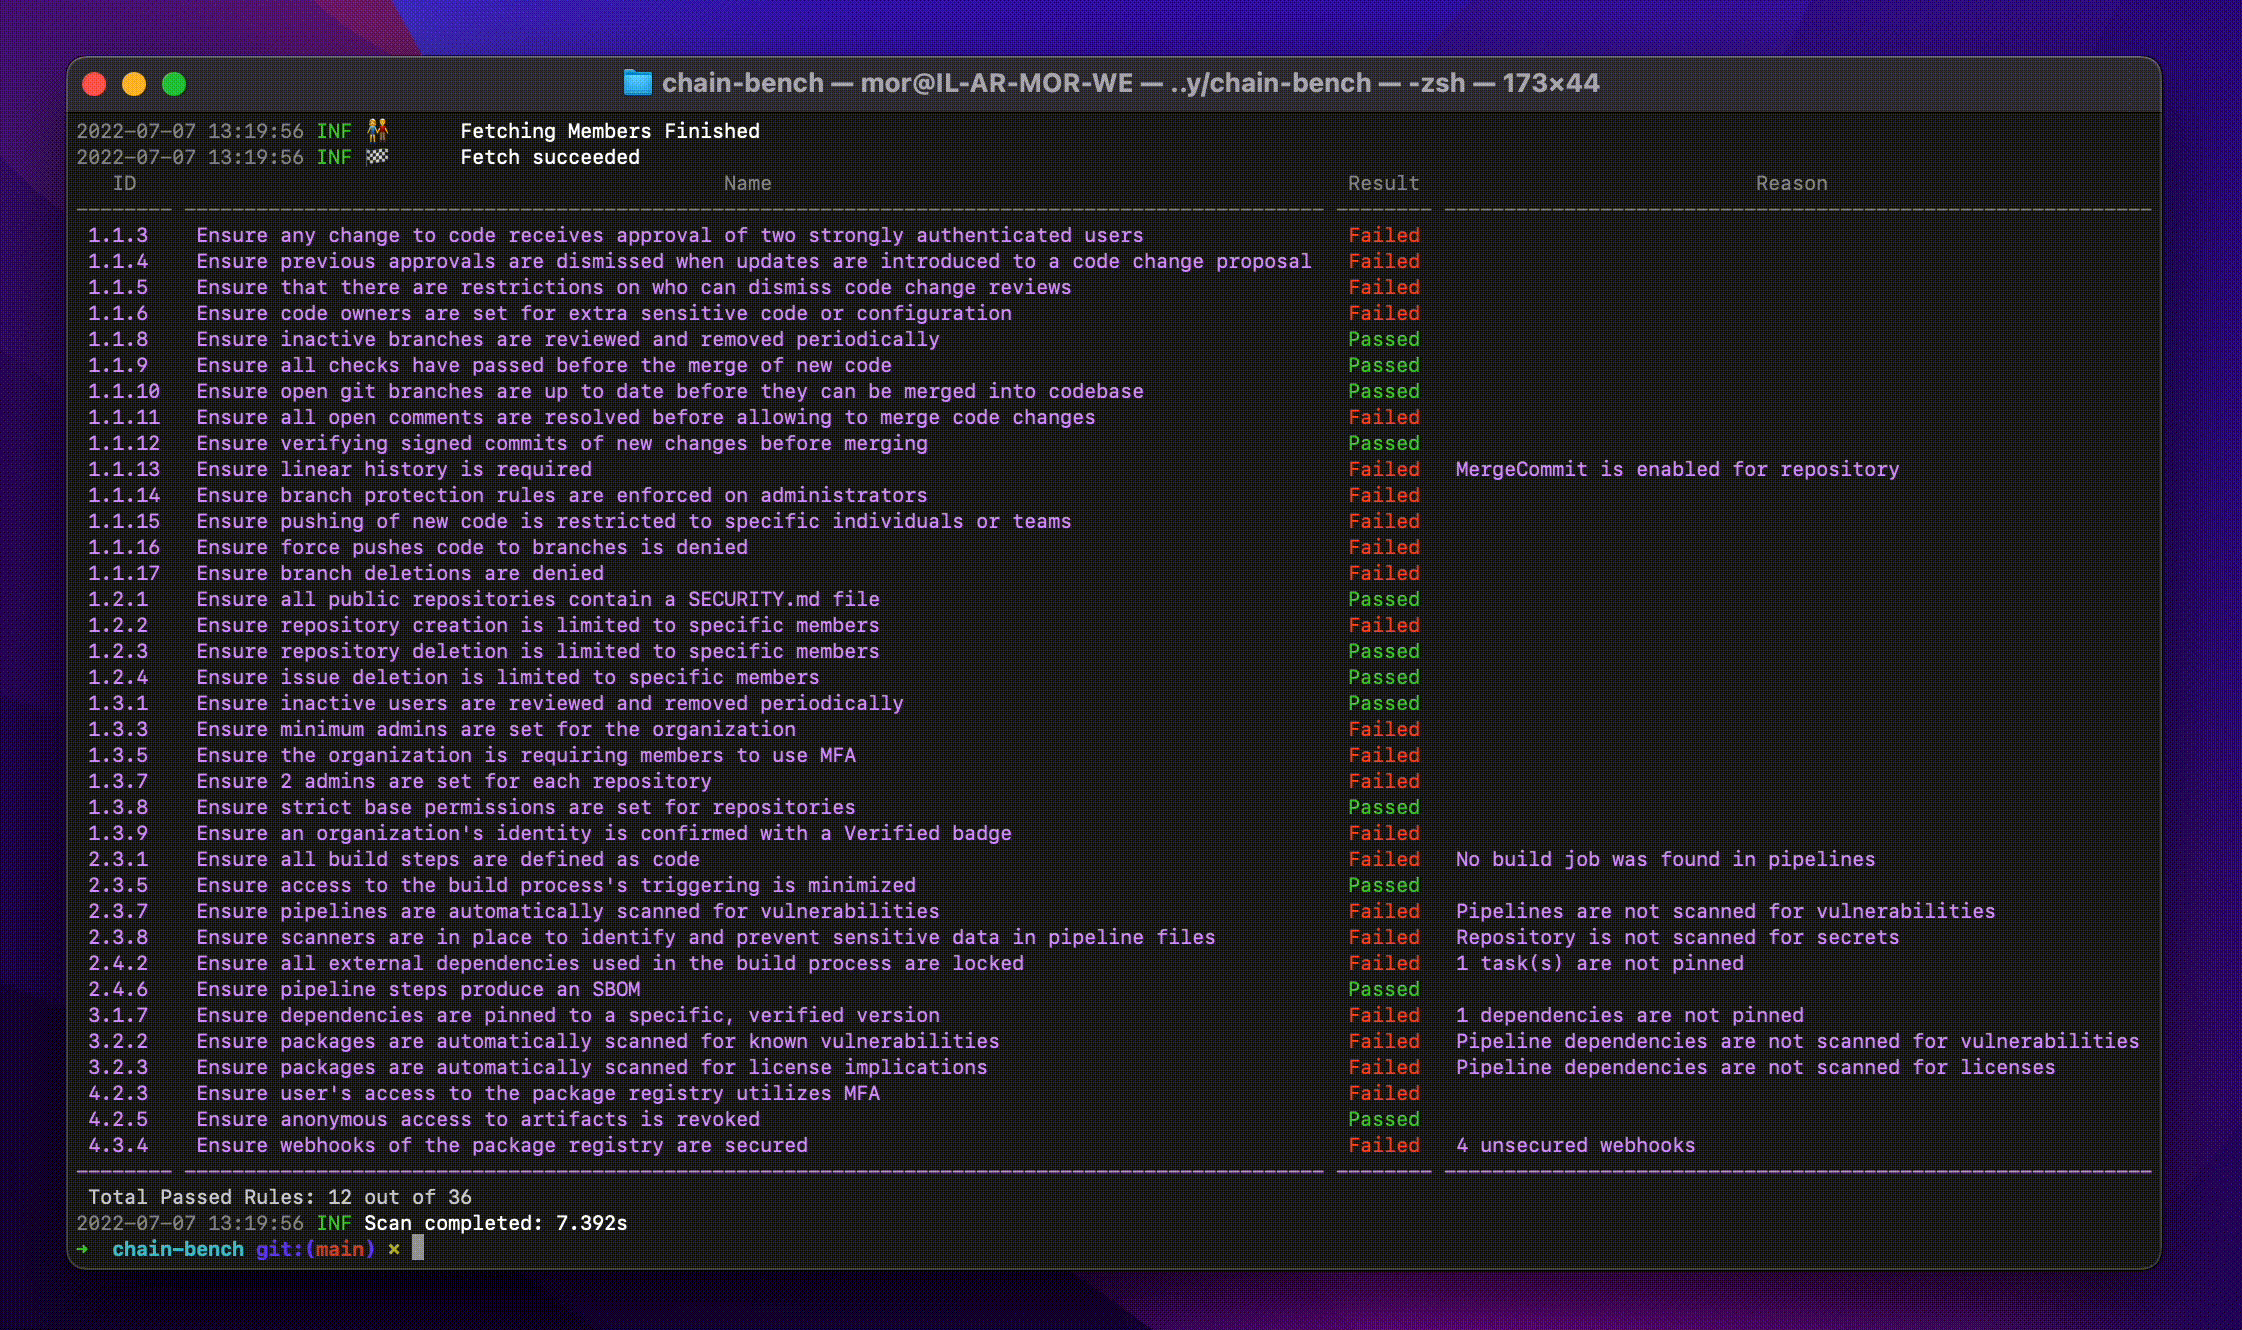
Chain-bench is an open-source tool for auditing your software supply chain stack for security compliance based on a new CIS Software Supply Chain benchmark. The auditing focuses on the entire SDLC process, where it can reveal risks from code time into deploy time.
The primary way to run chain-bench is as a standalone cli. It requires an access token for your account and the repository url in order to access your SCM.
Get Chain-bench via your favorite installation method. See [installation] section in the documentation for details. For example:
brew install chain-benchnix-env --install -A nixpkgs.chain-benchdocker run aquasec/chain-benchchain-bench scan --repository-url <REPOSITORY_URL> --access-token <TOKEN> -o <OUTPUT_PATH>
chain-bench scan --repository-url <REPOSITORY_URL> --scm-platform <SCM_PLATFORM> --access-token <TOKEN> -o <OUTPUT_PATH>
Supported options for scm-platform are "github" and "gitlab" (beta)
docker run aquasec/chain-bench scan --repository-url <REPOSITORY_URL> --access-token <TOKEN>
See the repository at https://github.com/aquasecurity/chain-bench-action
