
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot observability, and audit-ready exports. Runs inside your VPC.

The on-prem control plane for AI coding agents. Per-engineer cost attribution · hard budgets · egress governance · context-rot observability · audit-ready exports — all inside your VPC.


Conduit sits between your AI coding agents (Claude Code, Cursor, Codex, Aider) and whatever provider you already use (Anthropic, OpenAI, Bedrock, Azure — or your existing LiteLLM / Portkey deployment). One env var to adopt, zero client changes, prompts and completions never stored.
[Claude Code / Cursor / Codex]
         │  ANTHROPIC_BASE_URL=https://conduit.yourco.dev
         ▼
[Conduit]  vk_live_… (per-engineer)
         │  metering · budgets · governance · audit · context-rot
         ▼
[LiteLLM / Portkey / direct providers]
         │
         ▼
[Anthropic / OpenAI / Bedrock / Azure]
Overview — spend, cache savings, tokens, blocked requests, and governance flags at a glance.

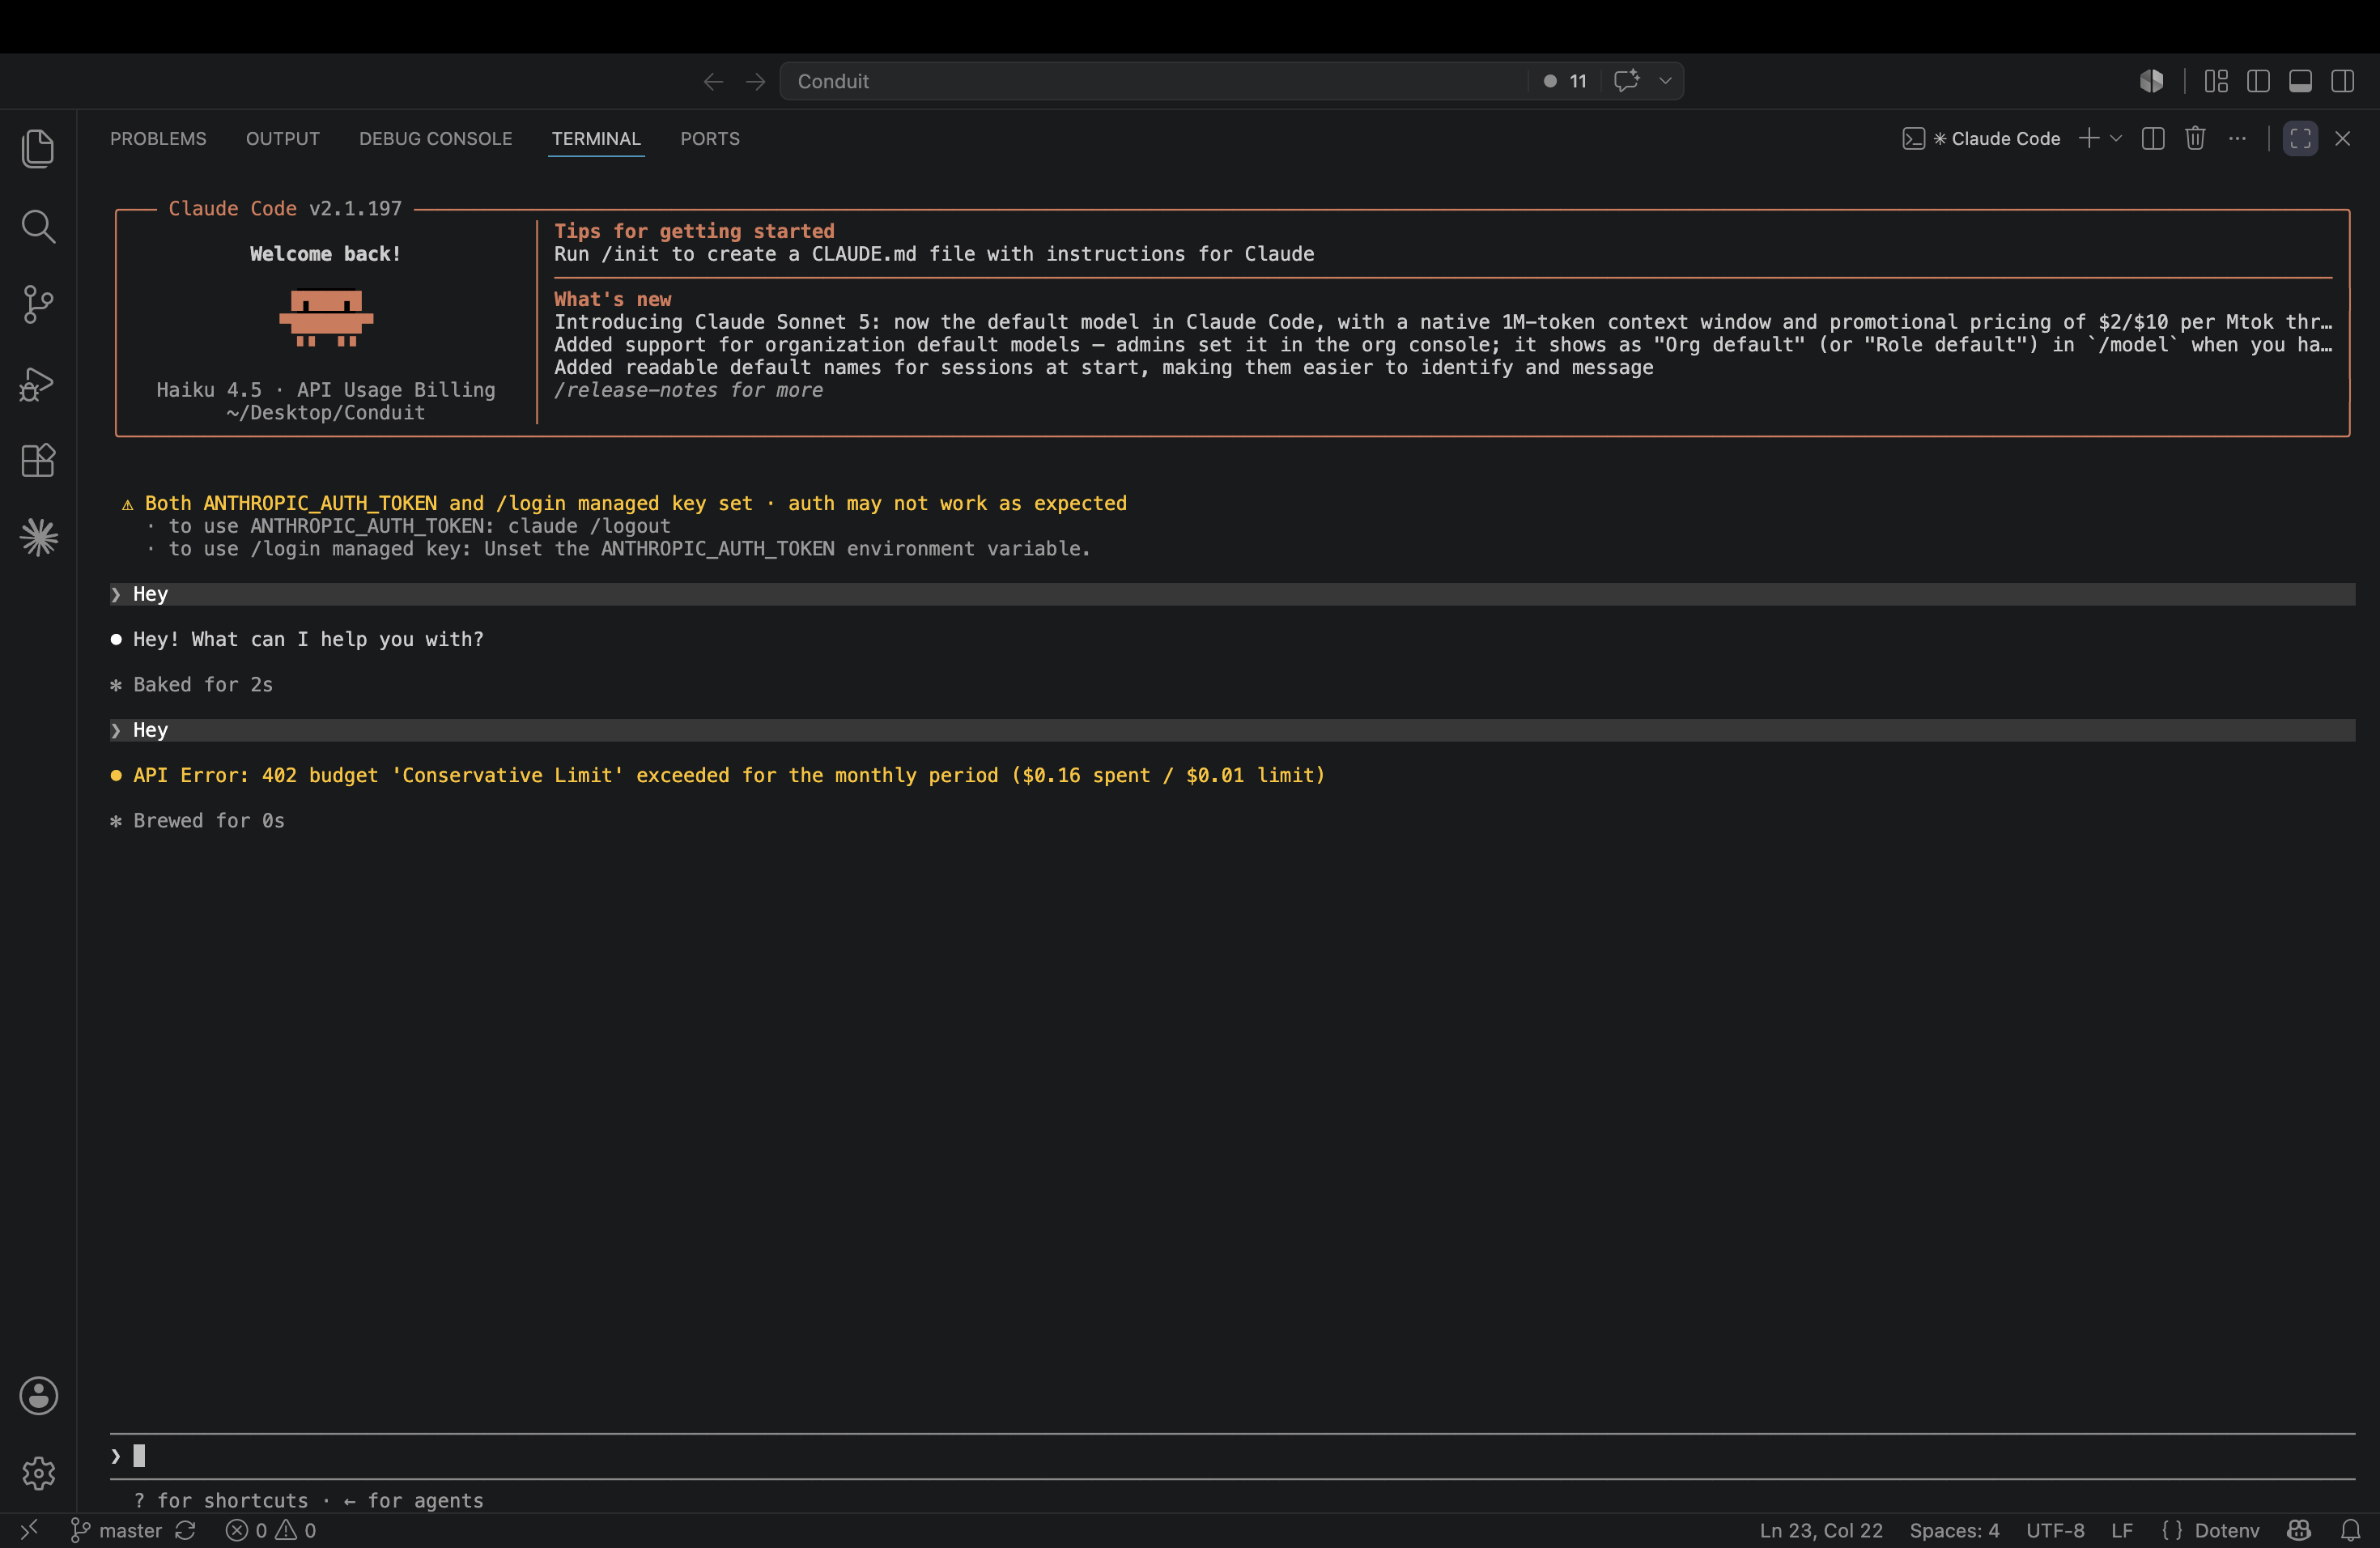
Hard budget enforcement — over the limit returns a 402 at the gateway, before the request reaches the provider.
Egress governance — a request carrying an AWS key is blocked with a 451; only the category is recorded, never the value.

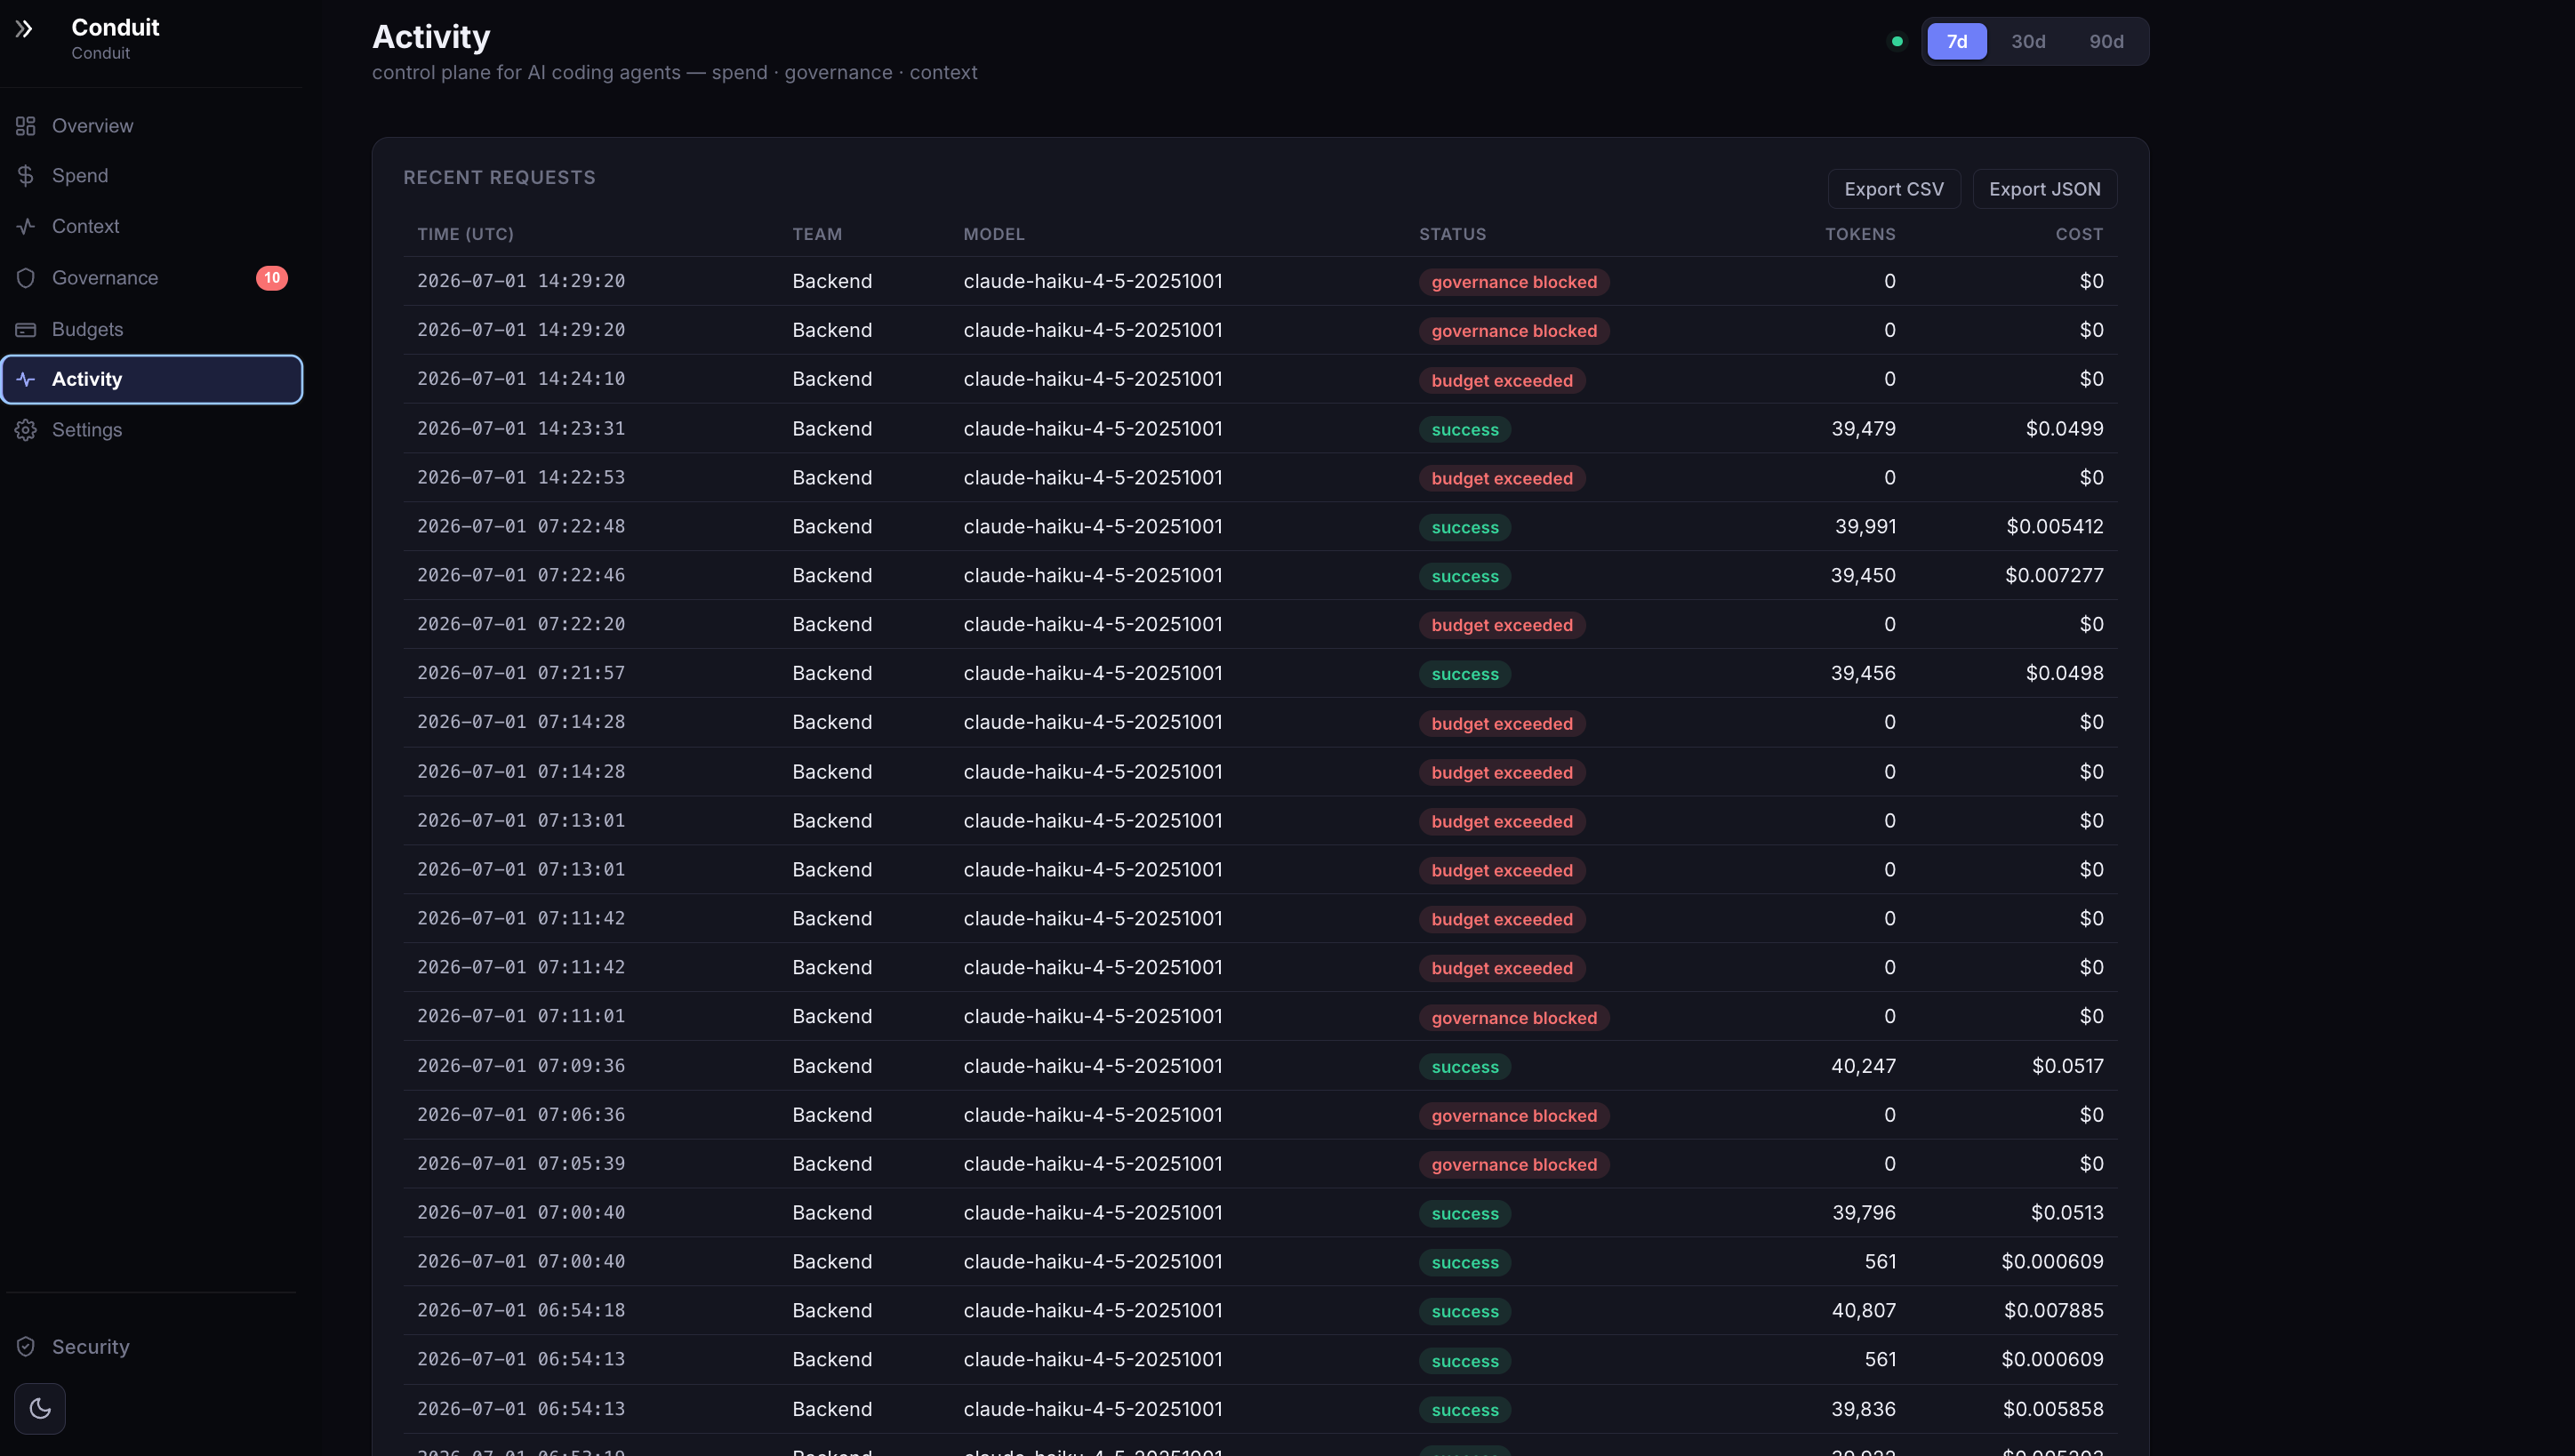
Activity — every request with a distinct status: success · cache hit · rate limited · model blocked · budget exceeded · governance blocked.
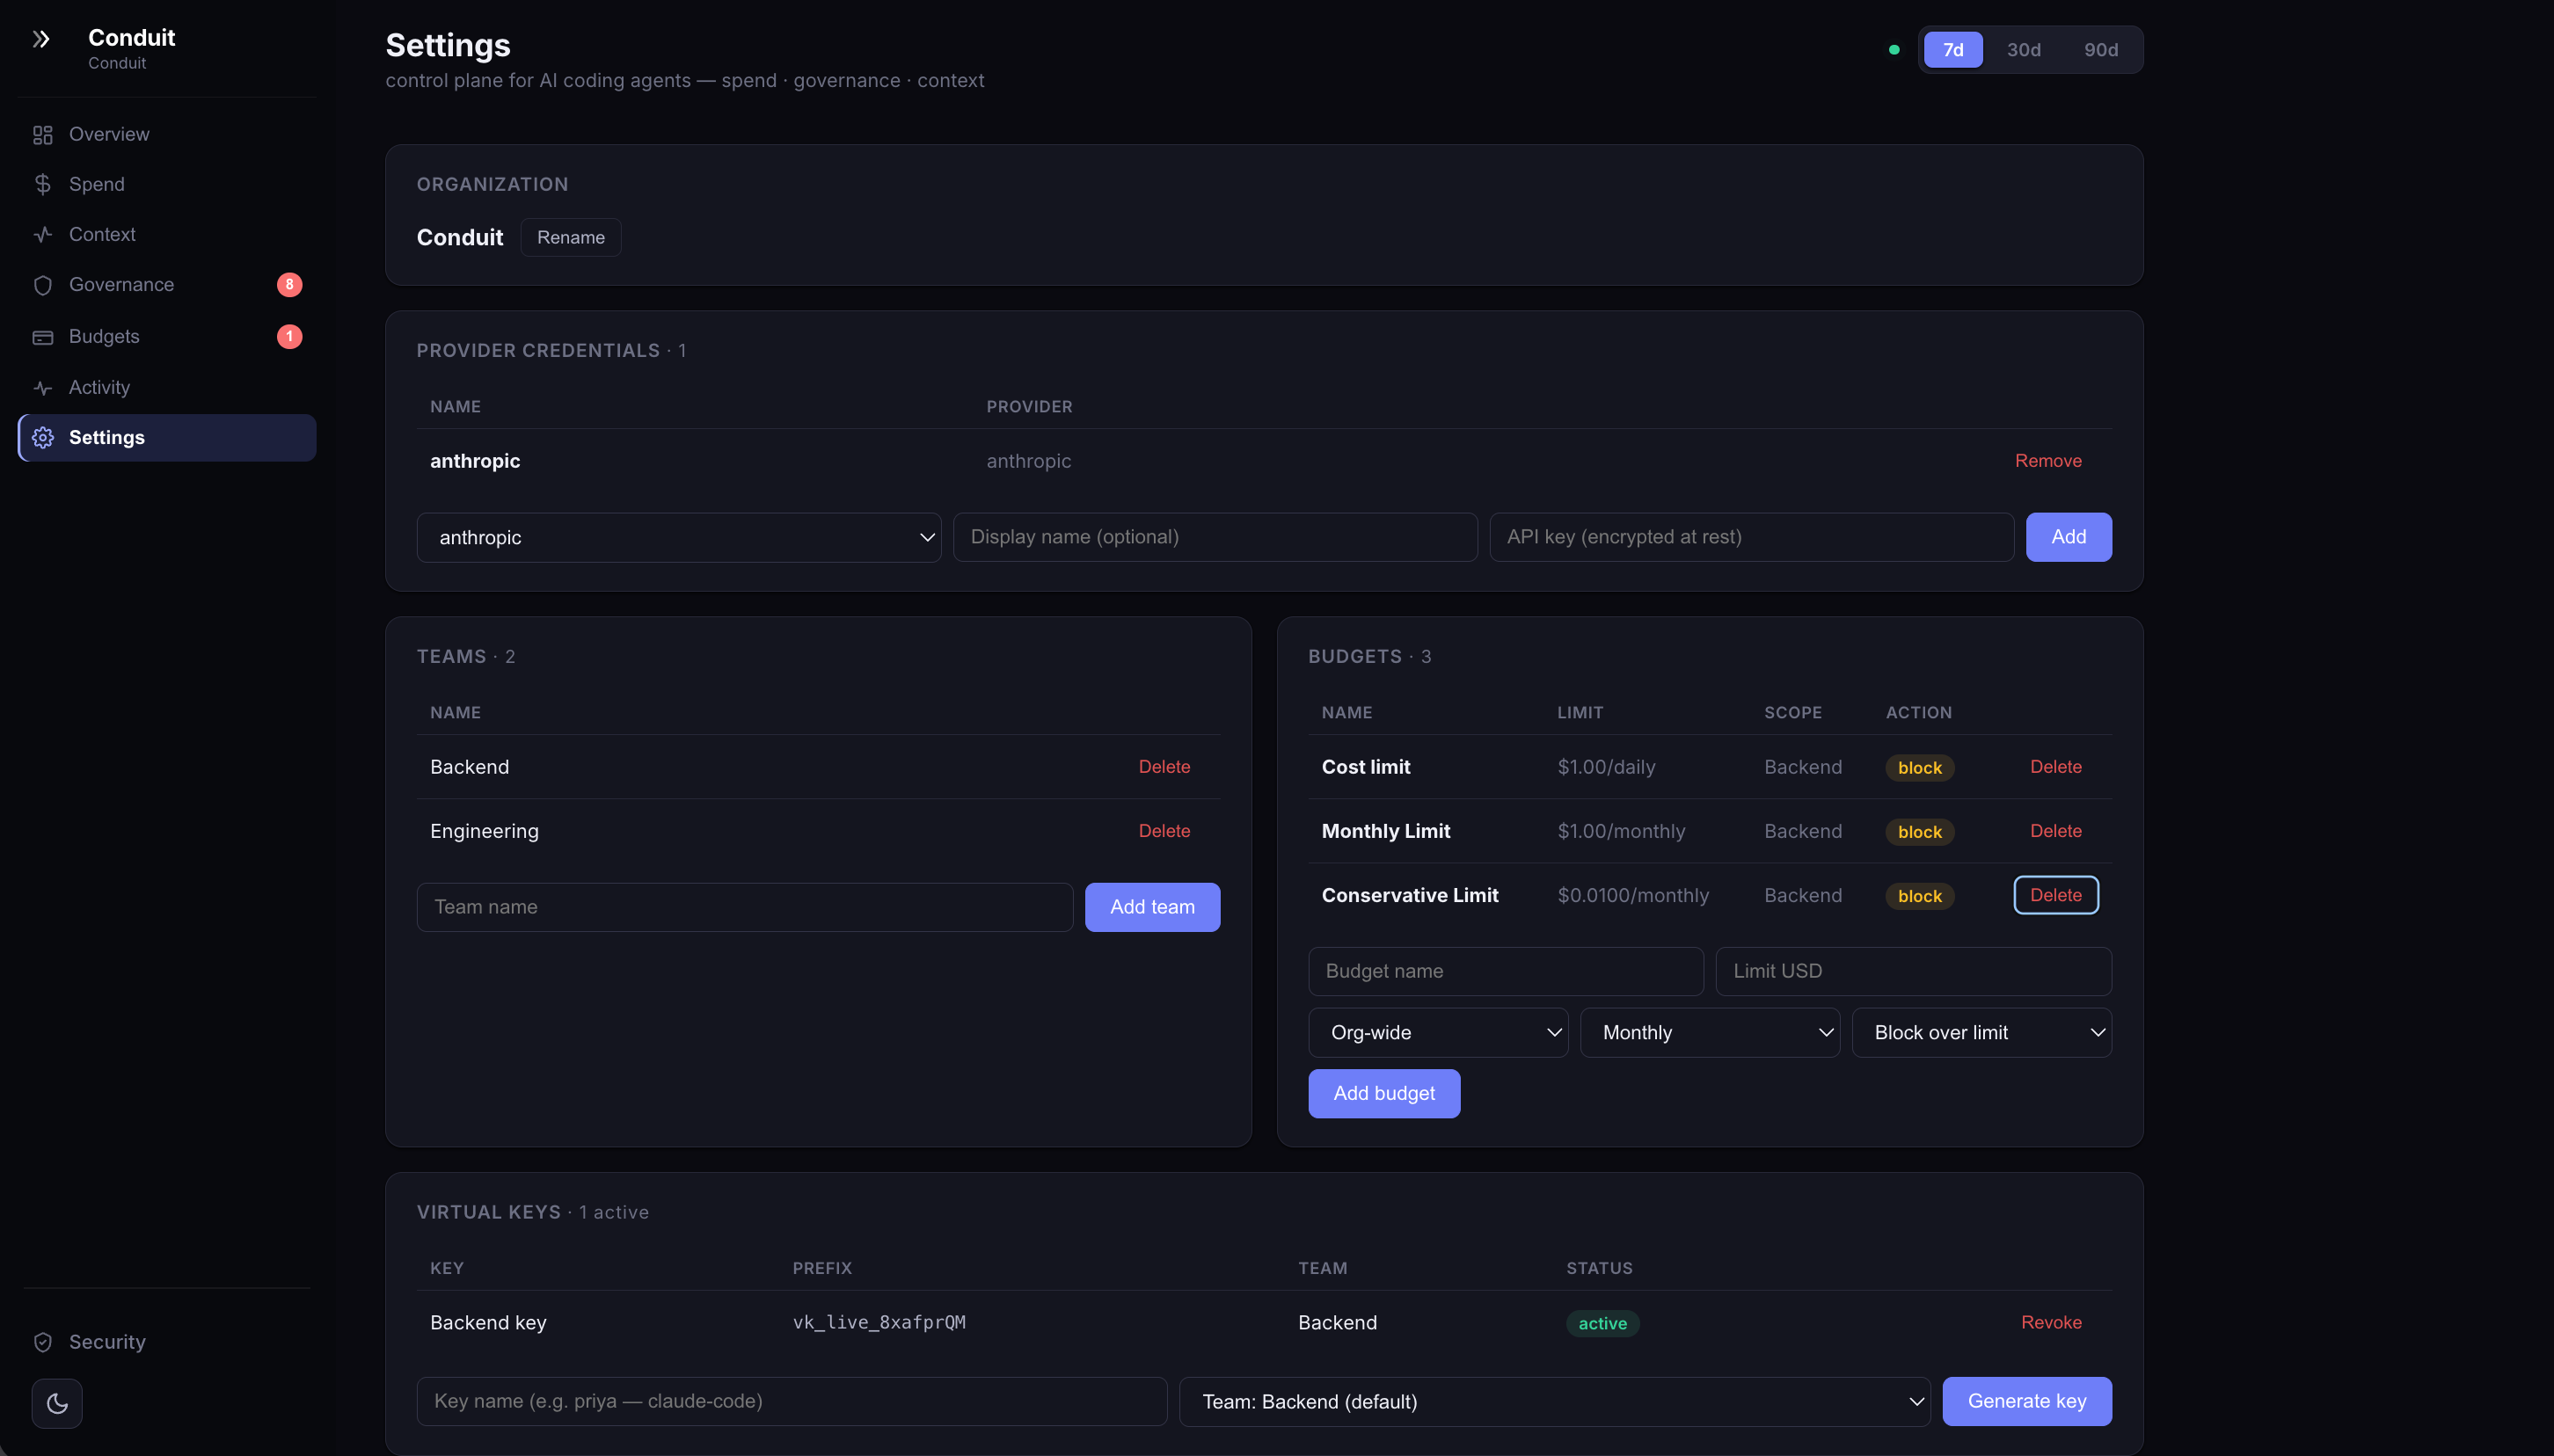
Settings — full CRUD for org, provider credentials, teams, budgets, and virtual keys.
Bedrock / Vertex / Azure private endpoints + no-train BAAs solve the channel to the vendor. They don't tell finance who spent the $40k, don't catch secrets at egress, don't give auditors a record, and don't show where context rot is burning your token budget. That's the gap Conduit fills — without ever seeing your prompts.
Pulls the latest signed images from GHCR (verifiable via cosign verify, see Security posture).
# 1. Get the compose file + env template (no full clone needed)
curl -fsSL https://raw.githubusercontent.com/anee769/conduit/master/docker-compose.yml -o docker-compose.yml
curl -fsSL https://raw.githubusercontent.com/anee769/conduit/master/.env.example -o .env

# 2. Generate a real master encryption key
sed -i.bak "s|^MASTER_ENCRYPTION_KEY=.*|MASTER_ENCRYPTION_KEY=$(openssl rand -base64 32)|" .env && rm .env.bak

# 3. Pull the signed images + start
docker compose --profile app pull
docker compose --profile app up -d

# 4. Run migrations + seed the pricing book (one-time)
docker exec conduit-gateway-1 pnpm --filter @finops/db db:migrate
docker exec conduit-gateway-1 pnpm --filter @finops/db seed-pricing

# → open http://localhost:3000/setup → create org / credential / team / virtual key
Pin to a specific release by exporting GATEWAY_IMAGE and CONTROL_PLANE_IMAGE before up:
export GATEWAY_IMAGE=ghcr.io/anee769/conduit-gateway:v0.1.0
export CONTROL_PLANE_IMAGE=ghcr.io/anee769/conduit-control-plane:v0.1.0
git clone https://github.com/anee769/conduit && cd conduit
cp .env.example .env
sed -i.bak "s|^MASTER_ENCRYPTION_KEY=.*|MASTER_ENCRYPTION_KEY=$(openssl rand -base64 32)|" .env && rm .env.bak

docker compose --profile app up -d --build
docker exec conduit-gateway-1 pnpm --filter @finops/db db:migrate
docker exec conduit-gateway-1 pnpm --filter @finops/db seed-pricing
export ANTHROPIC_BASE_URL=http://localhost:4000
export ANTHROPIC_AUTH_TOKEN=vk_live_…       # virtual key from /setup
claude                                       # or cursor / codex / aider
Full from-zero walkthrough in INSTALL.md.
| You run today | Configure Conduit's upstream as |
|---|---|
| LiteLLM (any model, any provider) | UPSTREAM_ANTHROPIC_URL=http://litellm:4000 → full walkthrough: docs/run-with-litellm.md |
| Portkey | Point UPSTREAM_OPENAI_URL / UPSTREAM_ANTHROPIC_URL at your Portkey base URL |
| Direct Anthropic / OpenAI | Default — nothing to configure |
| AWS Bedrock | Configure a Bedrock credential in /setup; Conduit signs requests with SigV4 |
| Azure OpenAI | Configure an Azure credential (deployment name + api-version) in /setup |
| Conduit | LiteLLM | Portkey | Helicone | |
|---|---|---|---|---|
| Open-source license | Apache 2.0 | MIT | Apache 2.0 (gateway) | MIT |
| Runs entirely on-prem / in your VPC | ✅ | ✅ | ✅ (enterprise) | ✅ (self-host) |
| Provider routing + aliasing + fallback | ✅ (any upstream) | ✅ | ✅ | ❌ |
| Per-engineer cost attribution (virtual keys with names) | ✅ | partial (master-key shared bills) | ✅ | ✅ (observe-only) |
| Hard budgets (fail-closed 402) | ✅ | partial | ✅ | ❌ |
| Egress governance (secrets + per-org entity allowlist, alert→block) | ✅ | ❌ | ✅ (guardrails) | ❌ |
| Audit-ready CSV/JSON export (metadata-only) | ✅ | ❌ | partial | ✅ |
| Context-rot observability (cost-and-error curve by input-token size) | ✅ | ❌ | ❌ | ❌ |
| Prompts / completions never stored | ✅ | logs by default | configurable | logs by default |
| Signed releases + CycloneDX SBOM | ✅ | ❌ | ❌ | ❌ |
| Designed to sit on top of others | ✅ | n/a | n/a | n/a |
LiteLLM is excellent at model aliasing and routing — Conduit adds the layer your security and finance teams asked for. Portkey is the closest feature overlap but is closed-source enterprise once you need governance + on-prem. Helicone is observability-only (it tells you where tokens went; it doesn't control where they go).

