 alt3kx/wafparan01d3
Quick WAF "paranoid" Doctor Evaluation | WAFPARAN01D3 Tool

The Web Application Firewall Paranoia Level Test Tool.
— From alt3kx.github.io


In essence, the Paranoia Level (PL) allows you to define how aggressive the Core Rule Set is.
Reference: https://coreruleset.org/20211028/working-with-paranoia-levels/
wafparan01d3.py python3 script takes malicious requests using encoded payloads placed in different parts of HTTP requests based on GET parameters, The results of the evaluation are recorded in the report debug file wafparan01d3.log created on your machine.mysql_gosecure.txt based on the research "A Scientific Notation Bug in MySQL left AWS WAF Clients Vulnerable to SQL Injection" from gosecure available here https://www.gosecure.net/blog/2021/10/19/a-scientific-notation-bug-in-mysql-left-aws-waf-clients-vulnerable-to-sql-injection/ evaluating our WAFs using modsecurity in their different levels of paranoia either in a default configuration or by disabling different rules / IDs in a staggered and quick way.
Pentesters: GreyBox scope with limited access to WAF Linux box using a "shell" with privileges to start/reload and edit WAF Apache config files on DEV/STG/TEST enviroments sending diferent payloads.Secutity Officers: Take the best decision to apply the level of WAF paranoia for each solution in your organization. Blueteamers: Rule enforcement, best alerting , less false positive results in your organization. Integrators: Perform a depper troubheshooting and define the adequate level of WAF paranoia quickly customizing rules or creating virtual patches. Reference: https://www.inmotionhosting.com/support/server/apache/install-modsecurity-apache-module/
$ sudo apt update -y && sudo apt dist-upgrade -y
$ sudo apt-get install build-essential -y
$ sudo apt-get install apache2 -y
$ sudo apt install libapache2-mod-security2 -y
$ sudo apt-get install curl vim gridsite-clients net-tools -y
$ sudo systemctl restart apache2
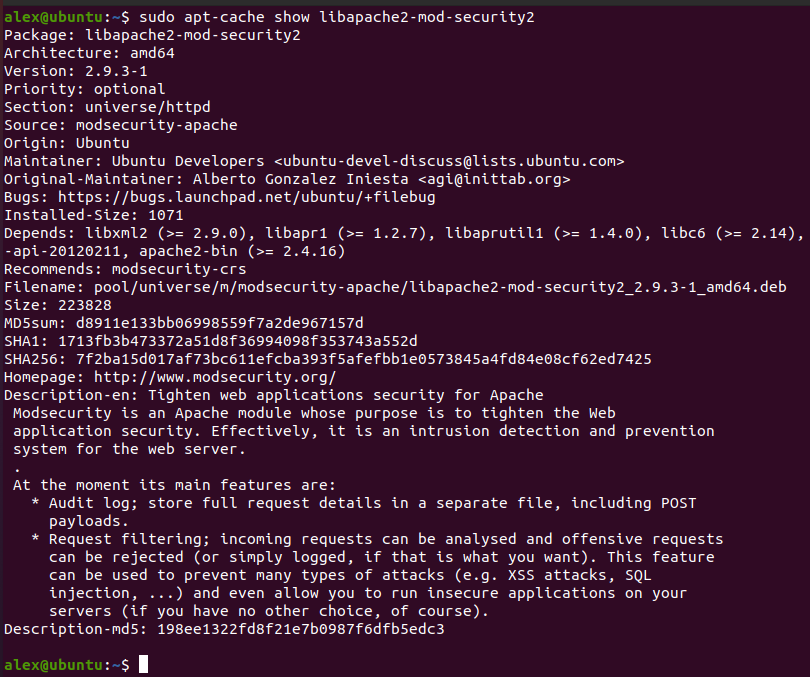
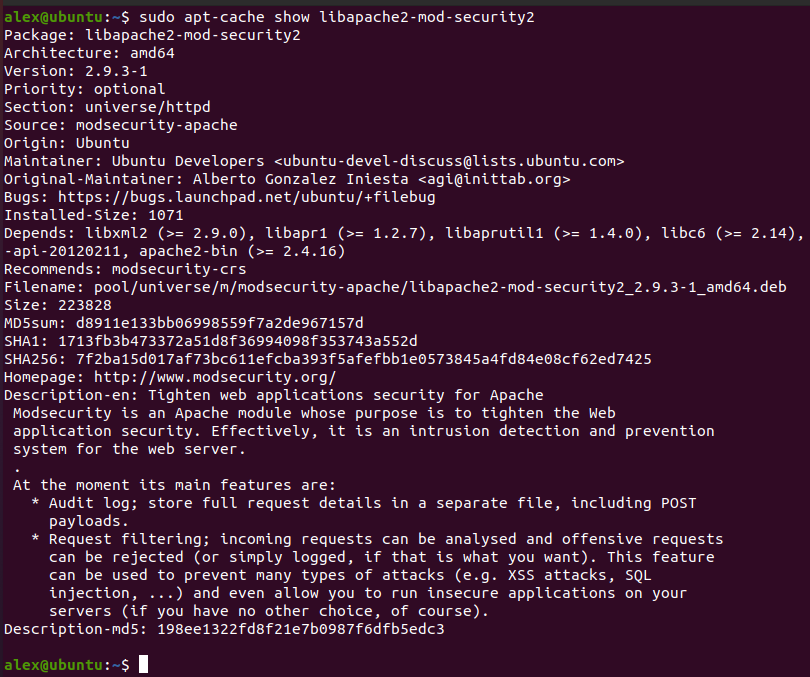
$ sudo apt-cache show libapache2-mod-security2
$ sudo cp /etc/modsecurity/modsecurity.conf-recommended /etc/modsecurity/modsecurity.conf
Next, change the ModSecurity detection mode. First, move into the cd /etc/modsecurity folder
2. Edit the ModSecurity configuration file with vi, vim, emacs, or nano.
$ sudo vim /etc/modsecurity/modsecurity.conf
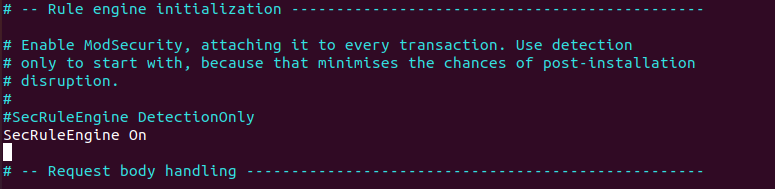
SecRuleEngine DetectionOnly. Change DetectionOnly to On. Original value: SecRuleEngine DetectionOnly
New value: SecRuleEngine On
$ sudo systemctl restart apache2
$ cd ~
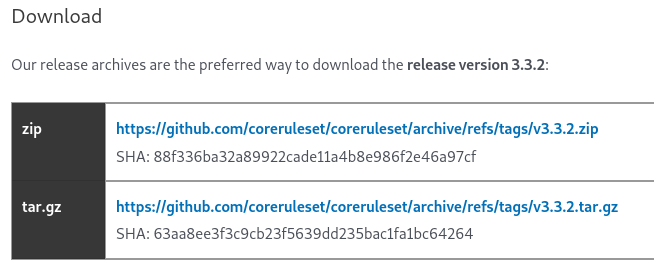
$ wget https://github.com/coreruleset/coreruleset/archive/refs/tags/v3.3.2.zip
$ sha1sum v3.3.2.zip && echo ProvidedChecksum
88f336ba32a89922cade11a4b8e986f2e46a97cf  v3.3.2.zip
ProvidedChecksum
$ unzip v3.3.2.zip
$ sudo mv coreruleset-3.3.2/crs-setup.conf.example /etc/modsecurity/crs/crs-setup.conf
$ sudo mv coreruleset-3.3.2/rules/ /etc/modsecurity/crs/
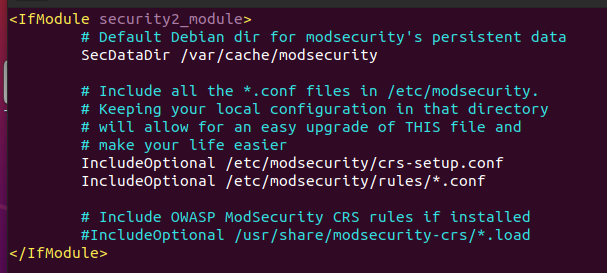
$ sudo vim /etc/apache2/mods-enabled/security2.conf
<IfModule security2_module>
        # Default Debian dir for modsecurity's persistent data
        SecDataDir /var/cache/modsecurity

        # Include all the *.conf files in /etc/modsecurity.
        # Keeping your local configuration in that directory
        # will allow for an easy upgrade of THIS file and
        # make your life easier
        IncludeOptional /etc/modsecurity/crs-setup.conf
        IncludeOptional /etc/modsecurity/rules/*.conf

        # Include OWASP ModSecurity CRS rules if installed
        #IncludeOptional /usr/share/modsecurity-crs/*.load
</IfModule>
$ sudo vim /etc/apache2/apache2.conf
Copy & Paste the following code and save it.
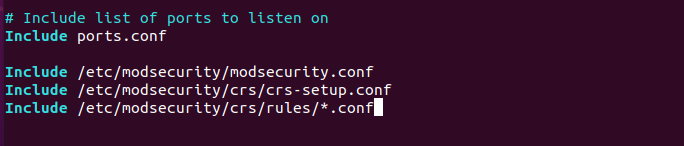
# Include list of ports to listen on
Include ports.conf

Include /etc/modsecurity/modsecurity.conf
Include /etc/modsecurity/crs/crs-setup.conf
Include /etc/modsecurity/crs/rules/*.conf