 alejandro609x/jefazo-cve-2025-55182-checker
Escáner pasivo de seguridad para CVE-2025-55182 que identifica indicadores públicos asociados a Next.js y React Server Components. Realiza validaciones seguras, analiza cabeceras y rutas, y proporciona una evaluación de exposición basada en evidencias sin explotación.


JEFAZO-CVE-2025-55182-Checker is a passive analysis tool designed to identify indicators related to CVE-2025-55182 in applications built with Next.js and React Server Components (RSC).
The tool performs safe and non-intrusive checks, without attempting to exploit the vulnerability or execute code on the target system.
This tool helps administrators, developers, and security analysts to identify potential exposure indicators related to CVE-2025-55182.
It provides a quick initial assessment before carrying out more in-depth audits or manual reviews of configuration and versions.
The scanner performs the following checks:
Retrieves the HTTP headers of the target site.
Searches for indicators such as:
Analyzes the HTML content for public Next.js artifacts.
Checks common routes used by the framework.
Calculates a score based on the indicators found.
Generates a confidence rating (Low, Medium, or High).
Clone the repository:
git clone https://github.com/Alejandro609x/JEFAZO-CVE-2025-55182-Checker.git
cd JEFAZO-CVE-2025-55182-Checker
Install dependencies:
pip install -r requirements.txt
Or manually:
pip install requests colorama urllib3
Run the program:
python3 can_cve_2025_55182.py
Enter the URL when prompted:
Introduce la URL objetivo: https://ejemplo.com
Not enough evidence was found to associate the target with relevant Next.js or React Server Components indicators.
Some indicators were detected suggesting the presence of potentially related technologies.
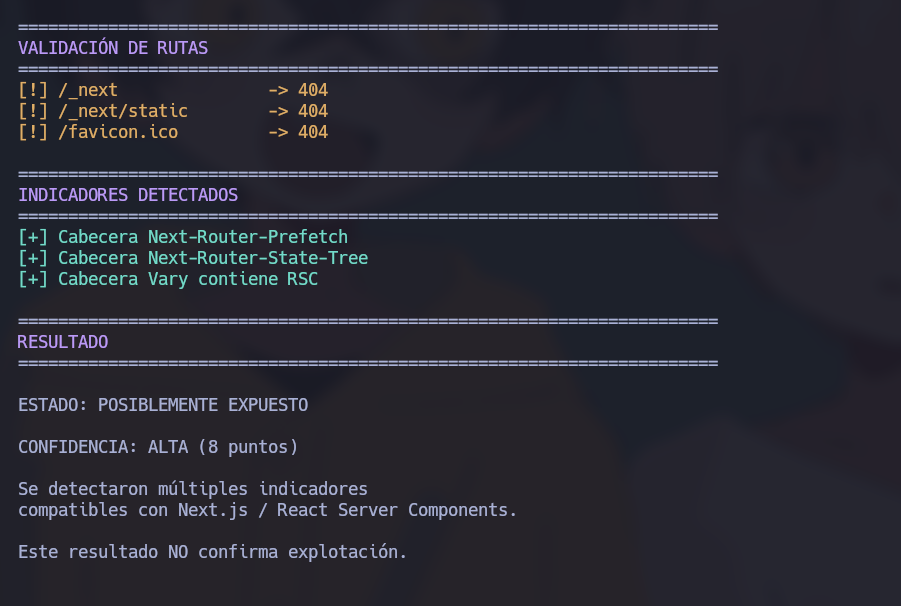
Multiple indicators compatible with Next.js and React Server Components were detected.
Important: This result does not confirm the existence of an exploitable vulnerability. It is recommended to verify versions, configurations, and apply the corresponding patches.
======================================================
RESULTADO
======================================================

ESTADO: POSIBLEMENTE EXPUESTO

CONFIDENCIA: ALTA (10 puntos)

Se detectaron múltiples indicadores compatibles
con Next.js y React Server Components.
