
Penetration testing report and exploit for CVE-2024-10924, a 2FA bypass in Really Simple SSL, including reconnaissance, exploitation, and remediation guidance.

Target: https://skior.co
Vulnerability: CVE-2024-10924 - 2FA Bypass in Really Simple SSL Plugin
Severity: Critical (CVSS Score: 9.8)
Status: Successfully Exploited
Discovery Date: 2025-06-25
Report Version: 2.1
This penetration test discovered a critical authentication bypass vulnerability that allows unauthenticated attackers to gain administrative access to the WordPress site by bypassing two-factor authentication (2FA) controls.
| Risk Level | Probability | Impact | Mitigation Priority |
|---|---|---|---|
| Critical | High | Complete System Compromise | Immediate |
| High | Medium | Data Breach | High |
| Medium | Low | Service Disruption | Medium |
| Field | Value |
|---|---|
| Domain | https://skior.co |
| IP Address | 123.456.789.200 |
| Server | nginx/1.26.0 (Ubuntu) |
| PHP Version | 8.2.28 |
| CMS | WordPress 6.8.1 |
| Vulnerable Plugin | Really Simple SSL |
| Geographic Location | United States |
| Hosting Provider | Professional hosting (likely VPS/Dedicated) |
This assessment followed a systematic black-box penetration testing methodology based on industry standards:
| Date/Time | Event | Details |
|---|---|---|
| 2025-06-25 14:02 | Initial Reconnaissance | Wappalyzer analysis completed |
| 2025-06-25 14:05 | Technology Stack Identified | WordPress 6.8.1, nginx, PHP 8.2.28 |
| 2025-06-25 14:10 | User Enumeration | Discovered user "pastor" (ID: 1) |
| 2025-06-25 14:15 | WPScan Analysis | No known vulnerabilities found |
| 2025-06-25 14:20 | REST API Enumeration | Discovered Really Simple SSL endpoints |
| 2025-06-25 14:25 | Vulnerability Research | Identified CVE-2024-10924 |
| 2025-06-25 14:30 | Manual Testing | Confirmed vulnerability existence |
| 2025-06-25 14:35 | Exploit Development | Created Python proof-of-concept |
| 2025-06-25 14:40 | Successful Exploitation | Obtained admin access |
| 2025-06-25 14:45 | Impact Assessment | Documented potential damage |
| 2025-06-25 15:00 | Report Generation | Comprehensive documentation |
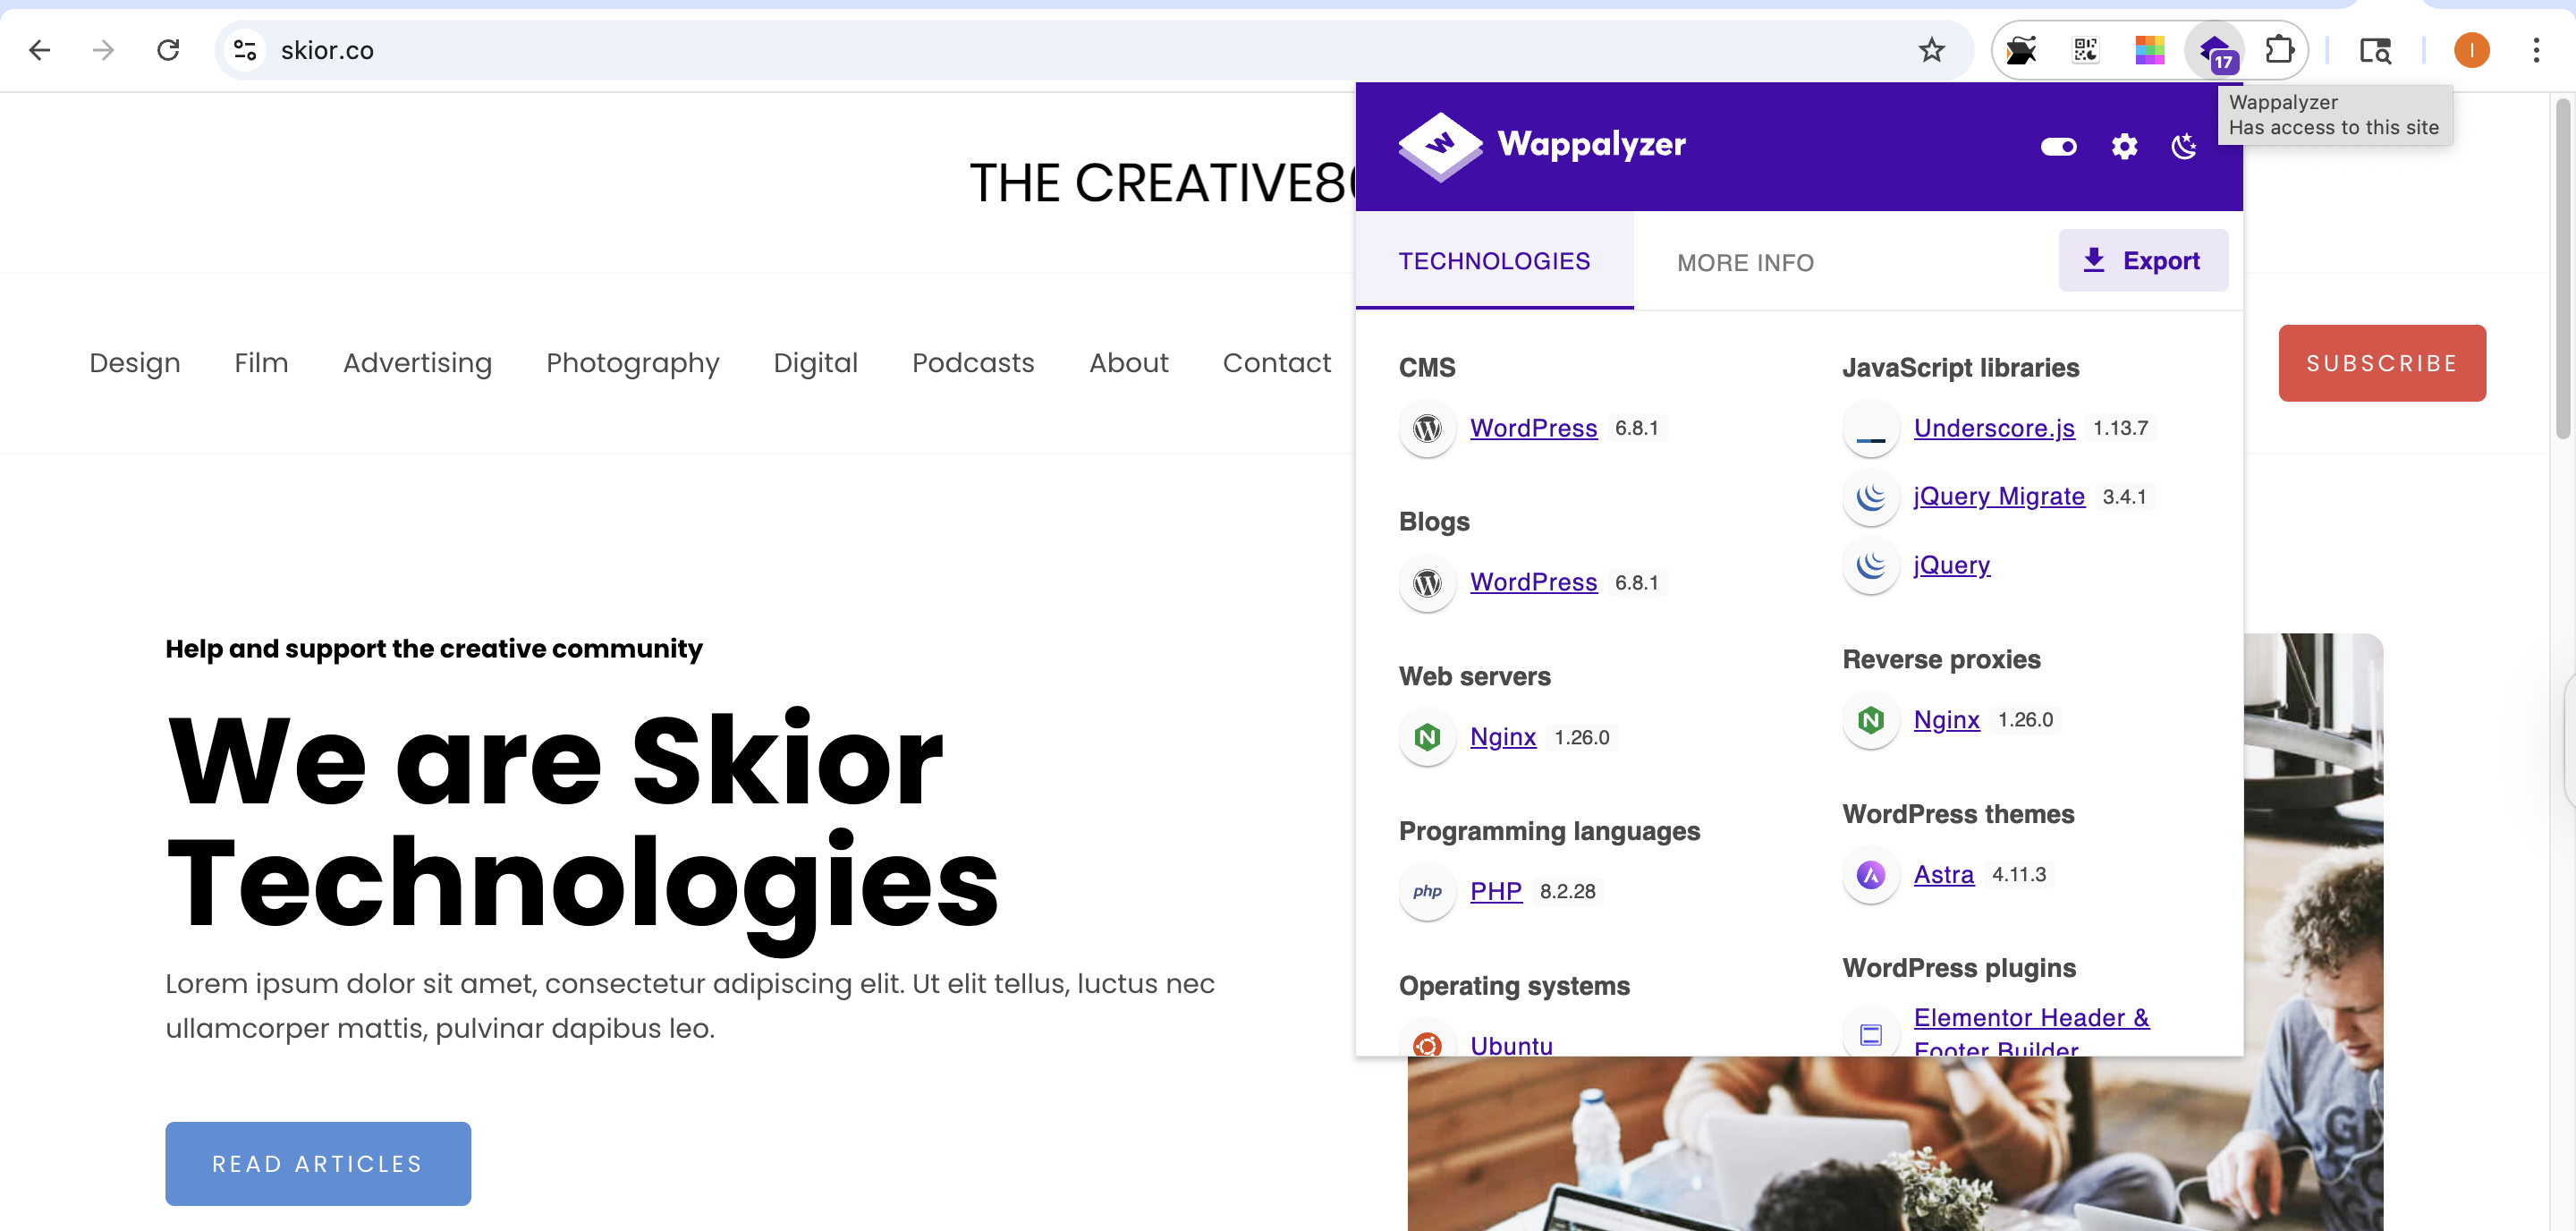
Identified Technologies:
└─$ whatweb https://skior.co
https://skior.co [200 OK] Country[UNITED STATES][US], HTML5, \
HTTPServer[Ubuntu Linux][nginx/1.26.0 (Ubuntu)], IP[123.456.789.200], \
JQuery[3.7.1],MetaGenerator[Elementor 3.29.2; \
features: additional_custom_breakpoints, e_local_google_fonts; \
settings: css_print_method-external, google_font-enabled, font_display-swap,\
WordPress 6.8.1], PHP[8.2.28], PoweredBy[Skior], \
Script[speculationrules,text/javascript], Title[Skior Technologies], \
UncommonHeaders[link], WordPress[6.8.1], X-Powered-By[PHP/8.2.28], nginx[1.26.0]
Key Findings:
└─$ curl -I https://skior.co/?author=1
HTTP/1.1 301 Moved Permanently
Server: nginx/1.26.0 (Ubuntu)
Date: Wed, 25 Jun 2025 18:12:15 GMT
Content-Type: text/html; charset=UTF-8
Connection: keep-alive
X-Powered-By: PHP/8.2.28
X-Redirect-By: WordPress
Location: https://skior.co/author/pastor/
Discovered User: pastor (User ID: 1)
# Check for multiple users
for i in {1..10}; do
    echo "Checking user ID: $i"
    curl -s -o /dev/null -w "%{http_code}" "https://skior.co/?author=$i"
    echo " - https://skior.co/?author=$i"
done
| User ID | Username | Status | Redirect URL |
|---|---|---|---|
| 1 | pastor | ✅ Found | /author/pastor/ |
| 2-10 | N/A | ❌ Not Found | 404 responses |
└─$ wpscan --url https://skior.co --api-token my-api-key
Scan Results Summary:
Note: WPScan did not detect the Really Simple SSL plugin, indicating it may be using obfuscation or custom naming.
└─$ curl -s https://skior.co/wp-json/ | jq '.routes | keys[]'
Discovered Custom Endpoints:
/reallysimplessl/v1/two_fa
/reallysimplessl/v1/two_fa/skip_onboarding
/reallysimplessl/v1/two_fa/do_not_ask_again
/reallysimplessl/v1/two_fa/resend_email_code
/reallysimplessl/v1/two_fa/save_default_method_email
/reallysimplessl/v1/two_fa/save_default_method_email_profile
/reallysimplessl/v1/two_fa/save_default_method_totp
/reallysimplessl/v1/two_fa/validate_email_setup
Critical Discovery: The /reallysimplessl/v1/two_fa/skip_onboarding endpoint appeared suspicious and warranted further investigation.
After discovering the custom REST API routes, external research revealed CVE-2024-10924, a critical vulnerability affecting the Really Simple SSL plugin.
CVE ID: CVE-2024-10924
CVSS Score: 9.8 (Critical)
Affected Plugin: Really Simple SSL
Vulnerability Type: Authentication Bypass
Attack Vector: REST API
Discovery Date: November 6, 2024
Public Disclosure: November 14, 2024
