


FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled Argon2id verifier, AES-GCM integrity.
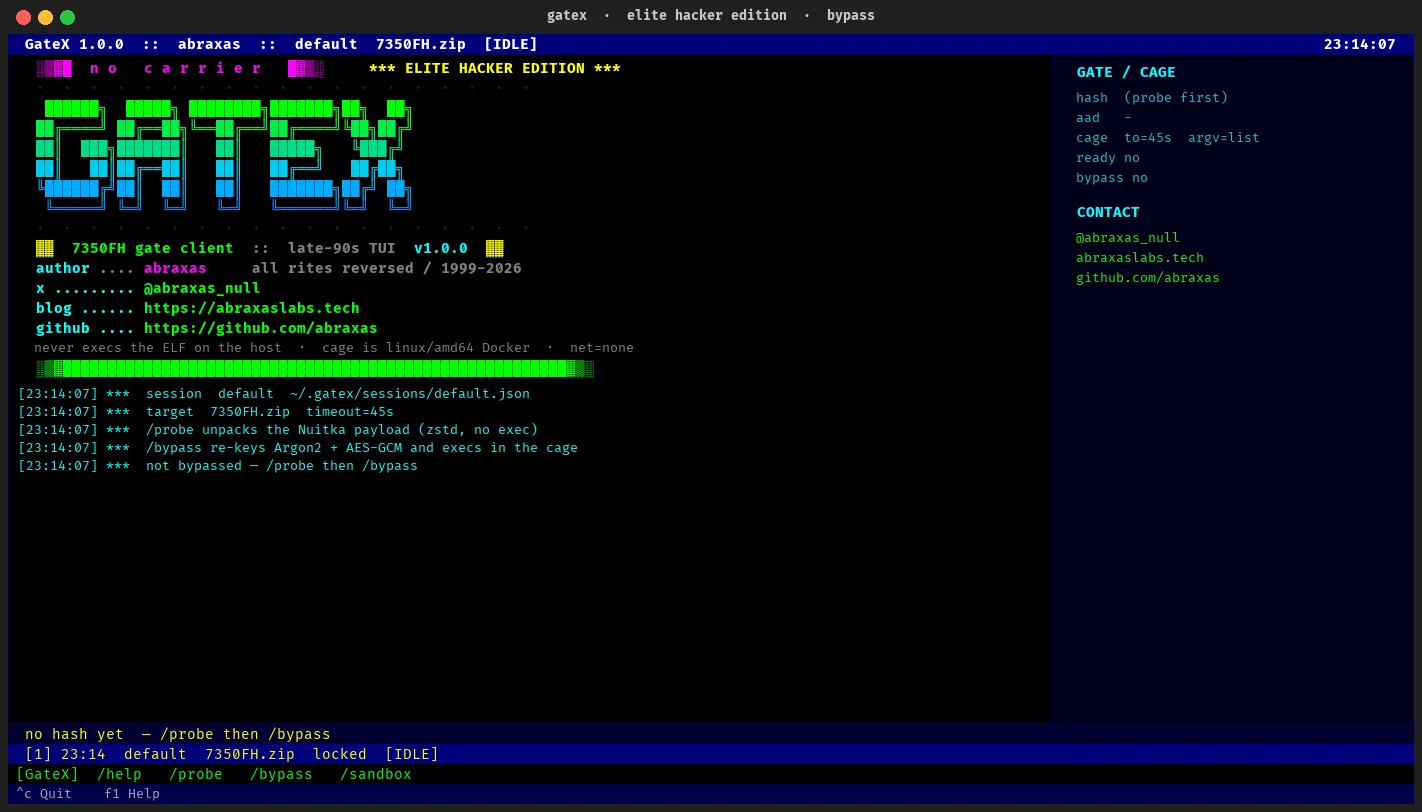
TUI that re-keys the "Fortinet Hunter 2026" Nuitka password gate. Part of a capture-the-flag challenge from @YoSoth0) Write-up: Hunting the Fortinet Hunter 0-day
The ELF never runs on the host. GateX statically unpacks the onefile payload, XOR-unmasks the scrambled Argon2id hash and AES-GCM banner, rewrites those blobs so FH_PASS=gatex satisfies both checks, then execs the inner binary inside a locked-down Docker cage.
This does not recover the author's original passphrase. Argon2id (m=65536,t=3,p=4) is doing its job. The plugins were already compiled into the inner ELF; the password only unwraps a banner.
abraxas
7350FH.zip (not shipped)The payload is untrusted CTF malware-shaped code. GateX only execs it under:
--platform linux/amd64--network none--read-only + tmpfs for unpack--cap-drop ALL --security-opt no-new-privileges:true65532, 2 GiB RAM, 1 CPU, 256 pidsgit clone [email protected]:abraxas/GateX.git
cd GateX
python3 -m venv .venv
.venv/bin/pip install -r requirements.txt
Place the challenge zip (or the inner ELF) where GateX can see it:
mkdir -p files
cp /path/to/7350FH.zip files/7350FH.zip
TUI:
.venv/bin/python -m gatex --target files/7350FH.zip
Inside the TUI:
/probe          # static zstd unpack + assemble the Argon2id hash (no exec)
/sandbox up     # start Docker, build gatex-cage:noble
/bypass         # re-key to FH_PASS=gatex and exec list in the cage
/cmd --help     # argv against the patched inner ELF
/cmd --version
/cmd score --ml
Headless:
# unpack + print the assembled argon2id hash (no TUI, no exec)
.venv/bin/python -m gatex --target files/7350FH.zip --probe

# re-key + exec list in the cage
.venv/bin/python -m gatex --target files/7350FH.zip --bypass
Optional --session name keeps state under ~/.gatex/sessions/ (mode 0600).
| Command | What it does |
|---|---|
/help | Command list |
/probe | Static unpack + assemble Argon2id hash (no exec) |
/bypass [password] | Re-key gate blobs (default gatex) and exec in the cage |
/cmd [args…] | argv passed to the patched ELF (list, --help, --version, …) |
/sandbox /sandbox up /sandbox down | Docker status / build / destroy |
/target <zip|elf> | Switch binary |
/session name | Switch reusable session |
/timeout <seconds> | Cage exec timeout |
/quit | Save and leave |
F1 = help.
KAY + zstd). Inner image is 7350FH.bin.BYTES constant c + fh-slim-hardened-v2.utf-8(xor(b64decode(ct), cycle(b64decode(key)))). Three fragments assemble the real PHC. A plaintext Argon2 string in the binary is the argon2-cffi doctest decoy — ignore it.fh-slim-v2-salt-2026 / fh-slim-v2-core) → AES-256-GCM of a 79-byte banner. Then cli.main(). The exploits are not in the ciphertext./bypass writes a new PHC of a password you know, encrypts a replacement banner under AAD b"fh-slim-hardened-v2" (the bytes value, not the on-disk cfh-… needle), and runs the patched inner as /opt/fh/7350FH.bin with LD_LIBRARY_PATH=$ORIGIN.Original inner + FH_PASS=gatex still prints [!] access denied. That is the experiment.
Live docker exec against the re-keyed inner, linux/amd64, net none, caps dropped, uid 65532. Captured 2026-08-26.
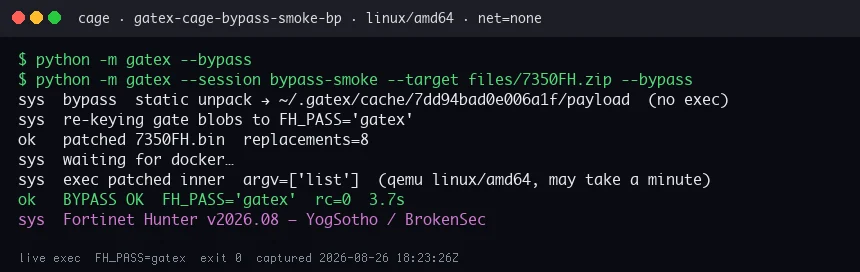
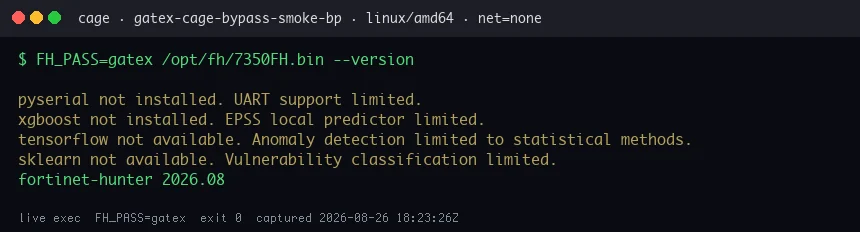
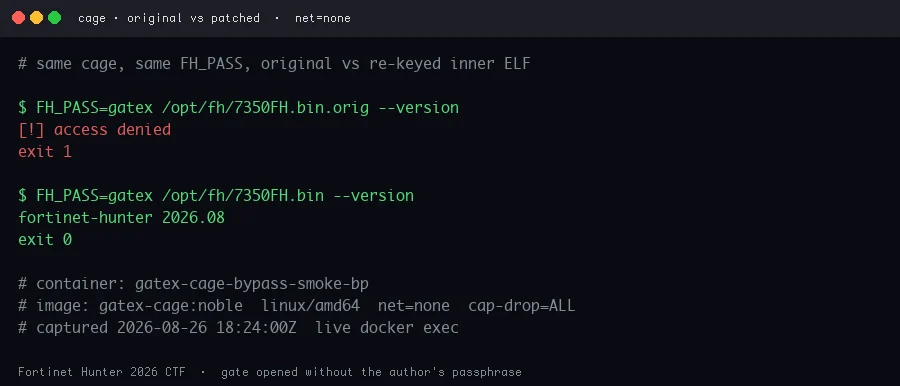
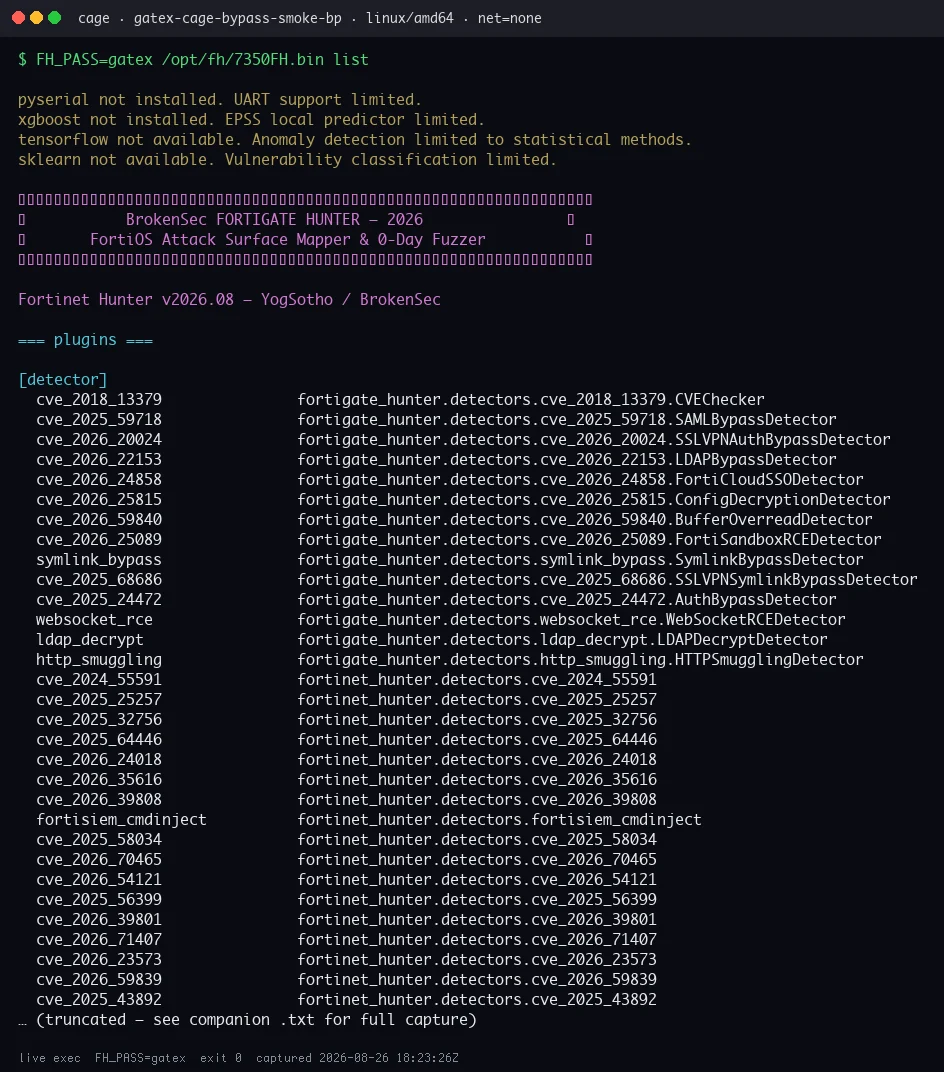
Full transcripts: files/evidence/*.txt and files/hunter-cli/.
.venv/bin/pip install pytest
.venv/bin/python -m pytest tests/test_offline.py -q
Patch/unpack tests that need files/7350FH.zip skip if the zip is absent.
Written for a CTF the author permitted. Do not point this at systems you do not own. GateX ships no exploits and no copy of 7350FH.
