
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-24919 — Exploit script for Check Point CVE-2024-24919 that reads arbitrary sensitive files via the vulnerable /clients/MyCRL endpoint, supporting single and batch targets with proxy and output options. | Kitploit
Tools/GitHubGitHub/0xkalawy/cve-2024-24919
ReconnaissanceVulnerability AnalysisExploitationWeb Application ExploitationInformation Gathering
GitHub0xkalawy/cve-2024-24919

CVE-2024-24919

Exploit script for Check Point CVE-2024-24919 that reads arbitrary sensitive files via the vulnerable /clients/MyCRL endpoint, supporting single and batch targets with proxy and output options.

View Repository
32 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Exploit for CVE-2024-24919

Description

This Python script is an exploit for CVE-2024-24919, a CVE that hitted Check Point Products: (CloudGuard Network, Quantum Maestro, Quantum Scalable Chassis, Quantum Security Gateways, Quantum Spark Appliances) Versions: (R77.20 (EOL), R77.30 (EOL), R80.10 (EOL), R80.20 (EOL), R80.20.x, R80.20SP (EOL), R80.30 (EOL), R80.30SP (EOL), R80.40 (EOL), R81, R81.10, R81.10.x, R81.20), allowing unauthorized access to sensitive files on a target system. It targets a vulnerability in the /clients/MyCRL endpoint
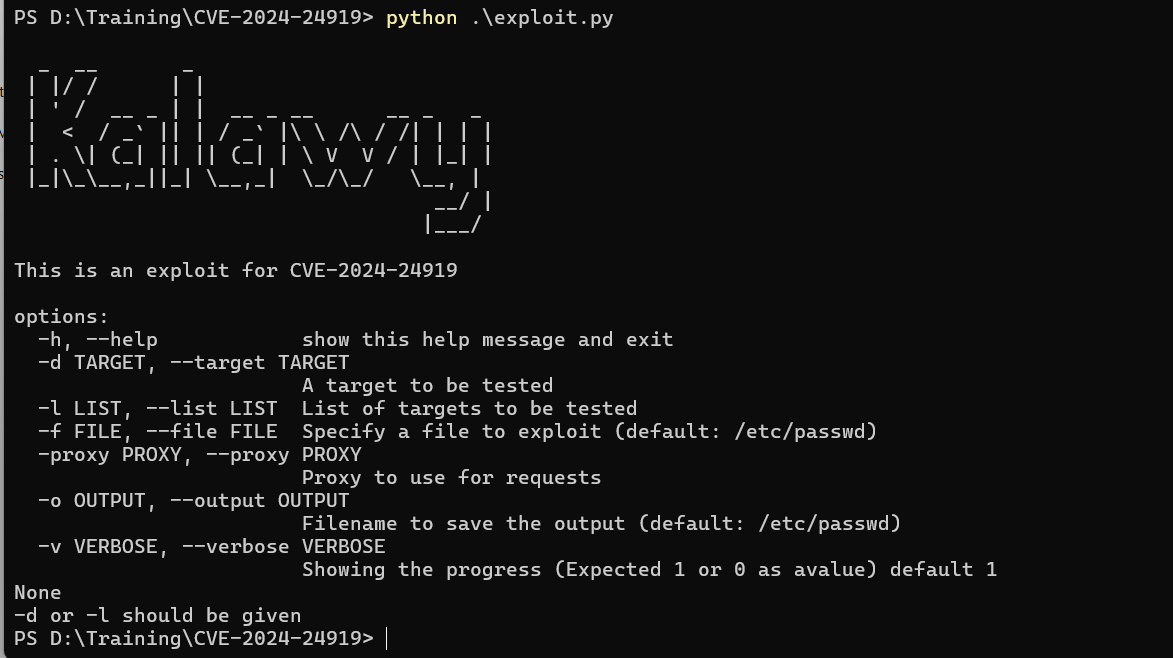
Running

Installation

git clone https://github.com/MohamedWagdy7/CVE-2024-24919

target.txt

is a file contains number of targets running vulnerable version, these targets enumerated from shodan using this dork "Server: Check Point SVN" "X-UA-Compatible: IE=EmulateIE7" 200 country:"IL"

Usage

python exploit.py -d <target> [-f <file>] [-proxy <proxy>] [-o <output>]
python exploit.py -l <list> [-f <file>] [-proxy <proxy>] [-o <output>]

Example

python exploit.py -l ./targets.txt -proxy 127.0.0.1:8080 -o CVE-2024-24919.txt

Arguments

  • -d, --target: Specifies a single target to be tested.
  • -l, --list: Specifies a list of targets to be tested.
  • -f, --file: Specifies a file to exploit (default: /etc/passwd).
  • -proxy, --proxy: Specifies a proxy to use for requests.
  • -o, --output: Specifies a filename to save the output (default: output.txt).

References

Watchtowr Labs - Wrong Check Point

Check Point Support

NVD - CVE-2024-24919

Download Tool