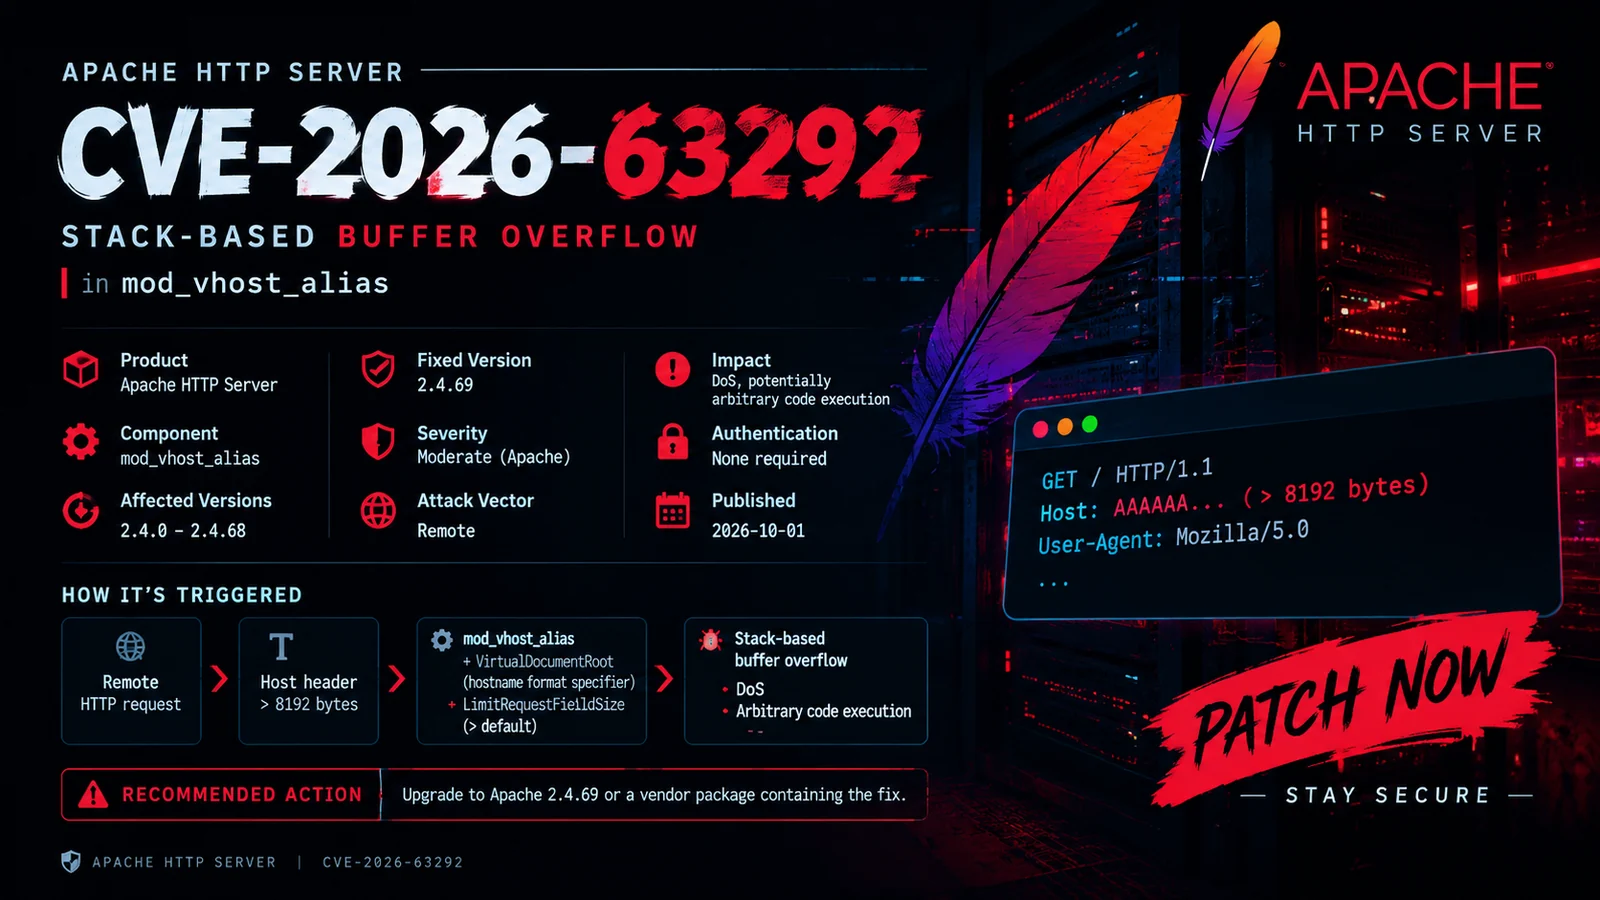
 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and patch guidance.

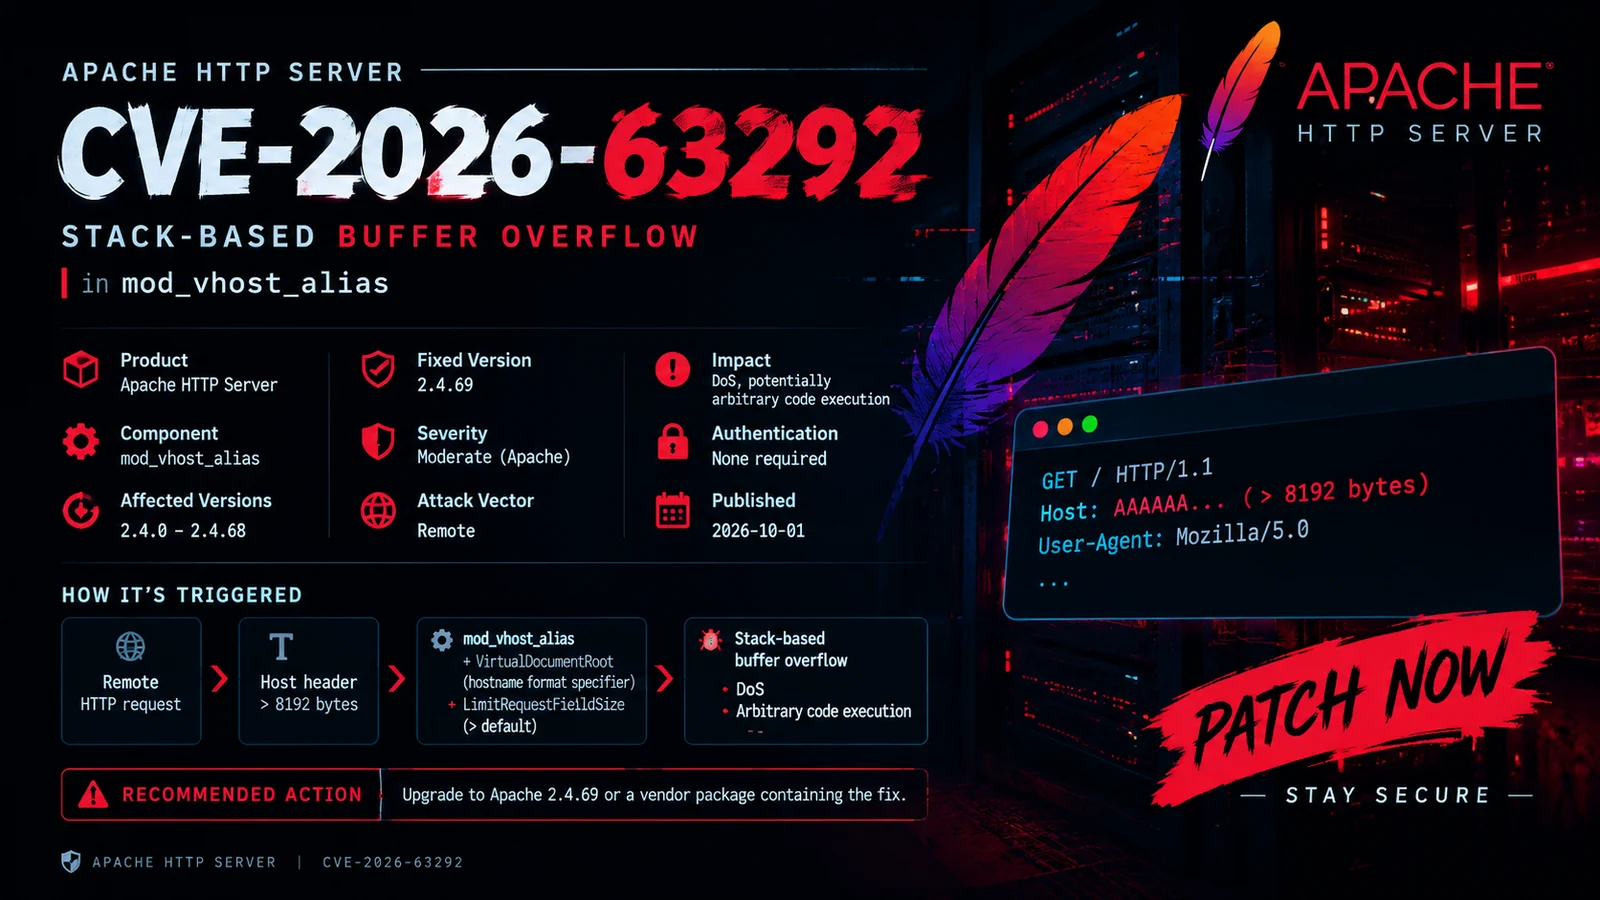
CVE-2026-63292 is a stack-based buffer overflow vulnerability affecting the Apache HTTP Server mod_vhost_alias module.
The issue can be triggered under specific server configurations involving oversized HTTP Host headers and VirtualDocumentRoot hostname format specifiers.
CVE-2026-63292
├── Component: mod_vhost_alias
├── Type: Stack-Based Buffer Overflow
├── CWE: CWE-121
├── Attack Vector: Network
├── Authentication: Not required
└── Impact: Denial of Service / Potential Code Execution
| Apache HTTP Server | Status |
|---|---|
2.4.0 – 2.4.68 | ⚠️ Affected |
2.4.69+ | ✅ Fixed |
Always verify the package version supplied by your operating-system vendor, as distributions may backport security fixes without changing the upstream version number.
Apache HTTP Server
        │
        ▼
   mod_vhost_alias
        │
        ▼
VirtualDocumentRoot
        │
        ▼
Hostname format processing
        │
        ▼
Oversized Host header
        │
        ▼
Stack-based buffer overflow
The vulnerability is associated with a specific configuration combination.
Relevant indicators include:
LoadModule vhost_alias_module modules/mod_vhost_alias.so

VirtualDocumentRoot /var/www/%0

LimitRequestFieldSize <value above default>
A vulnerable configuration should be evaluated only in an authorized test environment.
Check the Apache version:
apache2 -v
Debian / Ubuntu:
dpkg -l | grep apache2
RHEL / Fedora:
rpm -qa | grep httpd
Check whether mod_vhost_alias is loaded:
apachectl -M | grep vhost
or:
apache2ctl -M | grep vhost
Search the configuration:
grep -R "VirtualDocumentRoot" /etc/apache2/ 2>/dev/null
Check LimitRequestFieldSize:
grep -R "LimitRequestFieldSize" /etc/apache2/ 2>/dev/null
Upgrade Apache HTTP Server to a version containing the security fix.
Affected
2.4.0 ───────────────► 2.4.68
                         │
                         │ UPDATE
                         ▼
                     2.4.69+
                      FIXED
After updating, verify:
apache2 -v
Then validate the configuration:
apachectl configtest
Restart the service if appropriate for your environment:
sudo systemctl restart apache2
This repository intentionally focuses on safe vulnerability identification.
It does not provide:
The recommended approach is version and configuration verification.
     ┌──────────────────────┐
     │ Identify Apache      │
     │ version              │
     └──────────┬───────────┘
                │
                ▼
     ┌──────────────────────┐
     │ Check mod_vhost_alias │
     └──────────┬───────────┘
                │
                ▼
     ┌──────────────────────┐
     │ Review VirtualHost / │
     │ VirtualDocumentRoot  │
     └──────────┬───────────┘
                │
                ▼
     ┌──────────────────────┐
     │ Check request-header │
     │ configuration         │
     └──────────┬───────────┘
                │
                ▼
     ┌──────────────────────┐
     │ Patch / Verify       │
     │ fixed package        │
     └──────────────────────┘
| Property | Value |
|---|---|
| CVE | CVE-2026-63292 |
| Product | Apache HTTP Server |
| Module | mod_vhost_alias |
| Vulnerability | Stack-based buffer overflow |
| CWE | CWE-121 |
| Vector | Network |
| Authentication | Not required |
| Affected | 2.4.0 – 2.4.68 |
| Fixed | 2.4.69 |
| Primary Concern | Memory corruption |
| Safe Testing | Version + configuration checks |
CVE-2026-63292/
│
├── README.md
├── banner.png
├── CVE-2026-63292.py
├── requirements.txt
└── screenshots/
    └── lab-environment.png
This project is intended for authorized security research, defensive testing, vulnerability analysis, and educational purposes.
Only test systems that you own or have explicit permission to assess.
0xBlackash // Security Research
Understand • Verify • Patch • Secure
