 0xblackash/cve-2026-55450
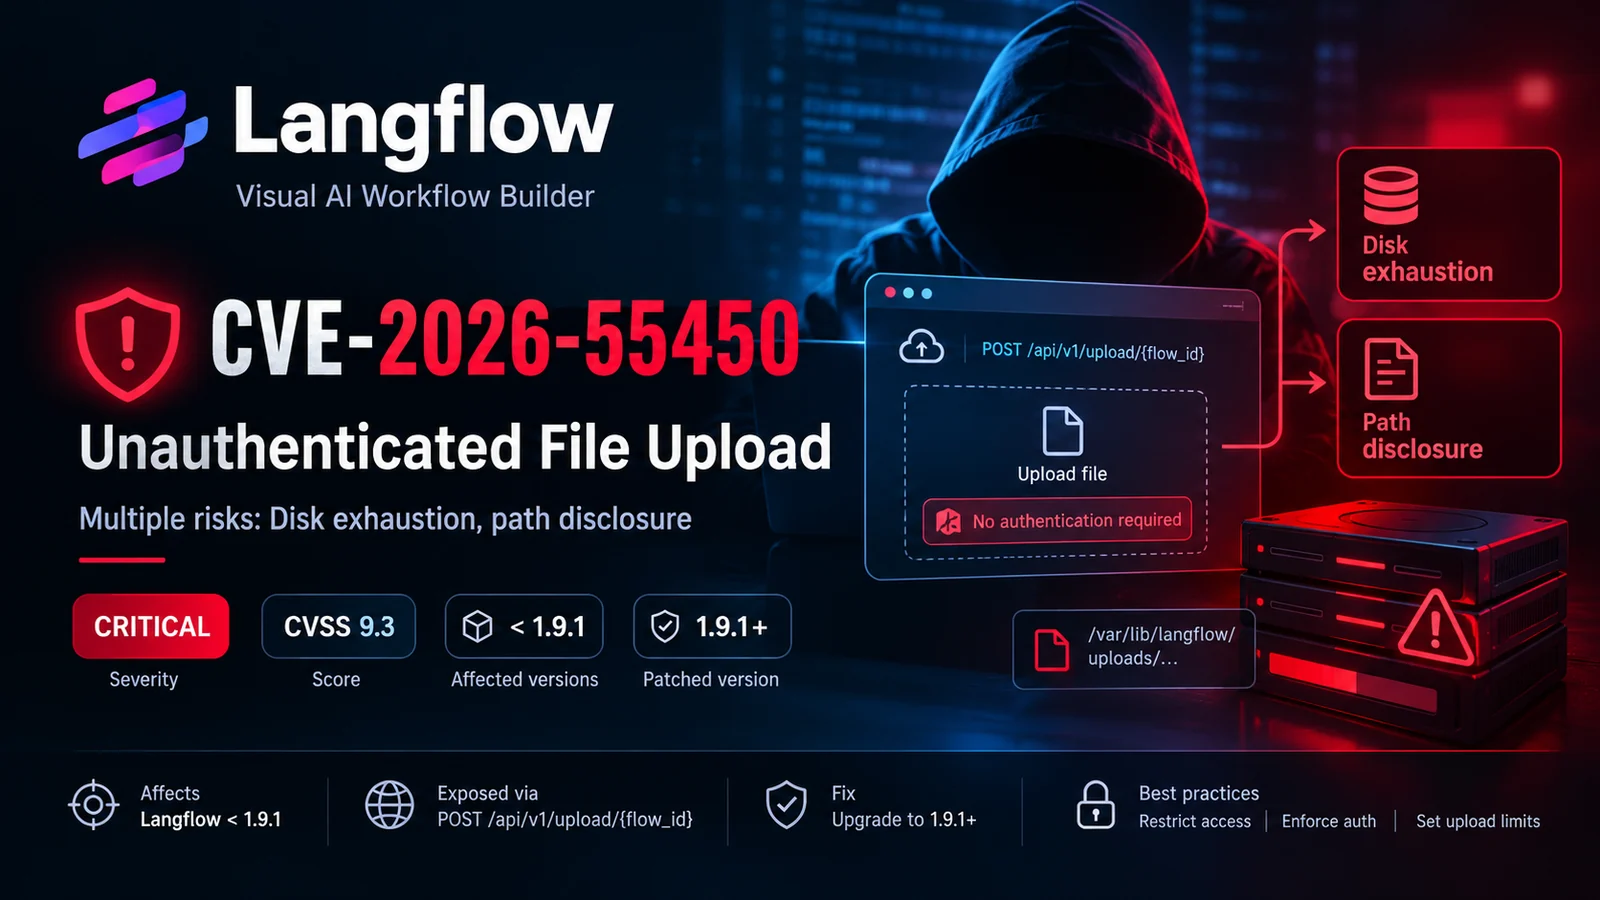
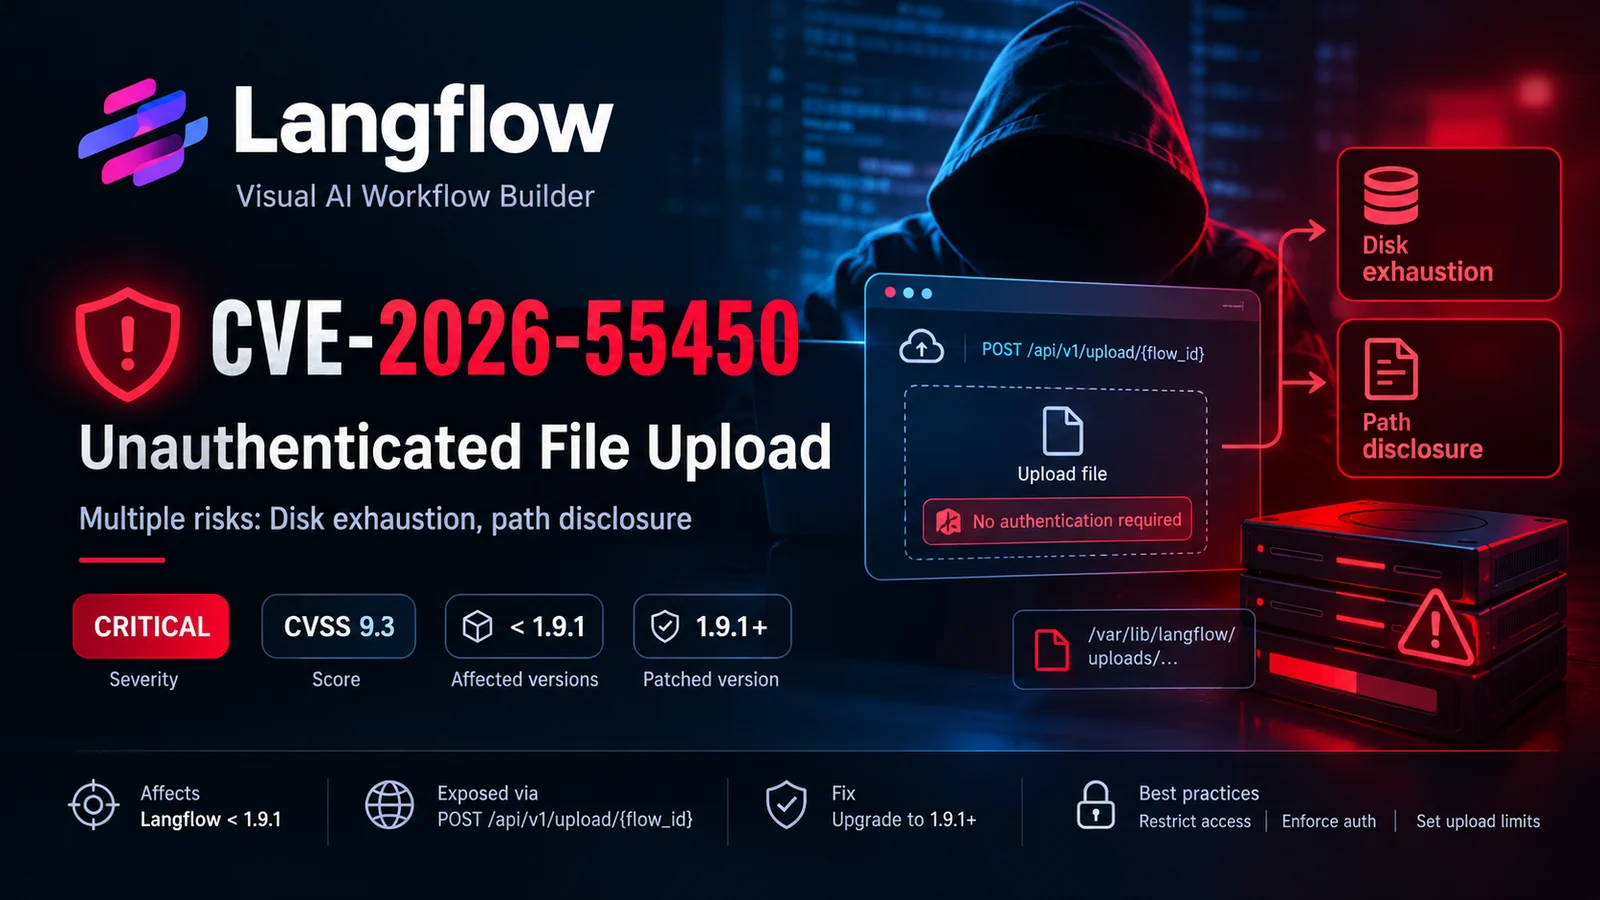
Advisory documenting CVE-2026-55450, an unauthenticated file upload flaw in Langflow, with impact analysis, detection references, and remediation guidance.

Unauthenticated File Upload Vulnerability
CVE-2026-55450 concerns a reported file-upload vulnerability affecting Langflow, an open-source platform for building AI-powered workflows.
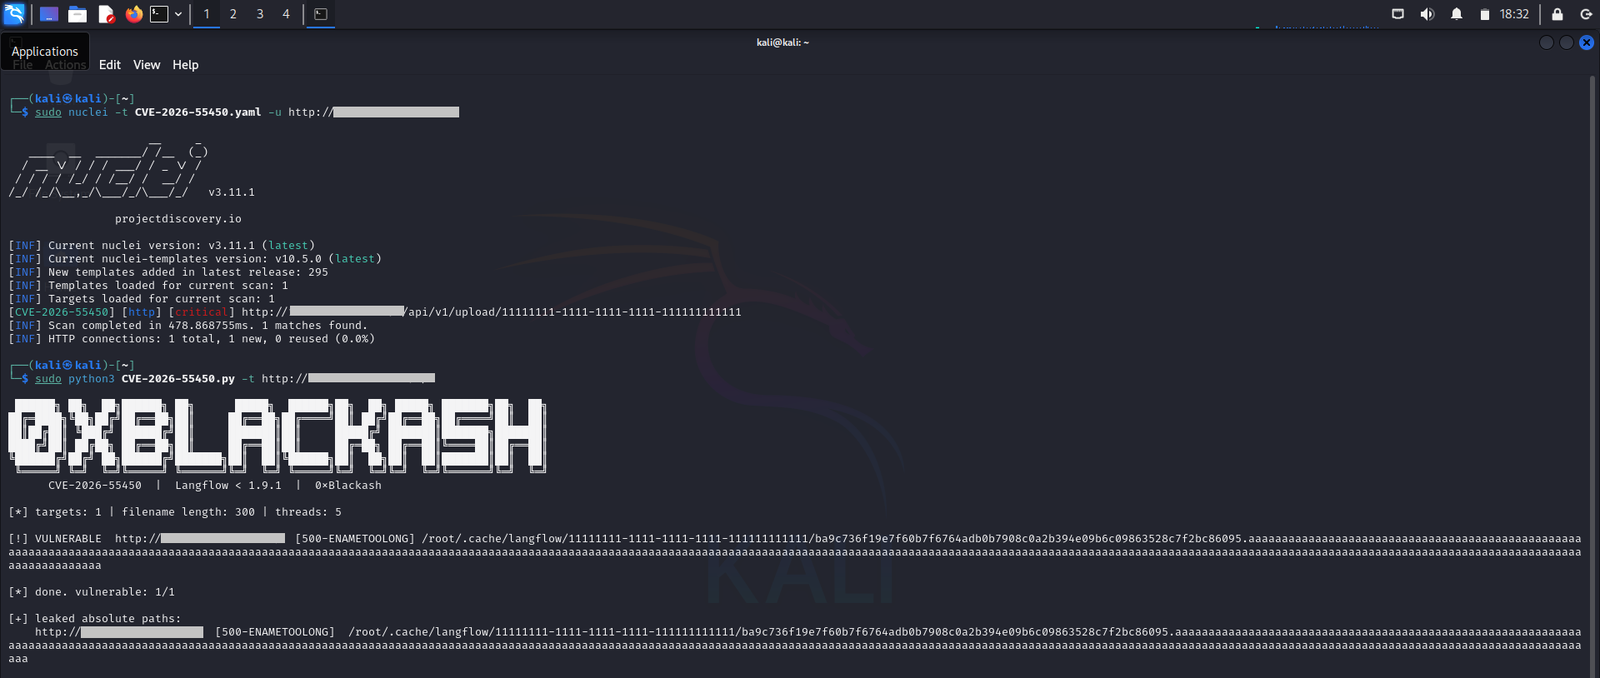
An exposed upload endpoint may permit unauthenticated file uploads, potentially resulting in excessive disk consumption and disclosure of internal filesystem paths.
This repository documents the vulnerability, its potential impact, detection references, and recommended mitigation measures.
| Attribute | Details |
|---|---|
| CVE ID | CVE-2026-55450 |
| Product | Langflow |
| Affected versions | Earlier than 1.9.1, according to the referenced advisory |
| Fixed version | 1.9.1 or later |
| Attack vector | Network |
| Authentication | Not required for the reported vulnerable endpoint |
| Potential impact | Denial of service and information disclosure |
| Related weaknesses | CWE-306, CWE-400, CWE-200 |
For authoritative information, consult the official GitHub Security Advisory.
The reported vulnerability involves the following API endpoint:
POST /api/v1/upload/{flow_id}
Insufficient authentication and upload restrictions may expose a deployment to unauthorized file uploads.
The potential consequences include:
The existence of this endpoint alone does not confirm that a deployment is vulnerable. Version, configuration, and patch status must be verified.
Excessive file uploads can consume available storage resources and affect application availability.
Responses that expose internal filesystem paths may reveal implementation details useful for further security assessment.
An upload endpoint that does not enforce the required authentication and authorization controls may allow unauthorized operations.
Security teams should validate their Langflow deployments using authorized, non-destructive methods.
Recommended checks:
Automated detection results should be treated as indicators rather than definitive proof of vulnerability. Active testing must be restricted to systems for which explicit authorization has been granted.
Recommended defensive measures:
Where supported, review the max_file_size_upload setting and verify its effective value against the documentation for the deployed release.
This repository is intended for defensive security research, vulnerability awareness, and authorized testing.
Do not test systems without permission. The author assumes no responsibility for damage or misuse resulting from unauthorized activity.
Security Research | Vulnerability Analysis | Defensive Validation
