📌 Overview
- CVE ID: CVE-2026-25049
- Affected Software: n8n
- Severity: Critical
- Category: Improper Access Control / Information Disclosure
This vulnerability allows unauthenticated access to internal configuration data via a REST API endpoint in certain n8n deployments.
🧭 Table of Contents
🔍 Technical Details
In vulnerable configurations, the following endpoint is accessible without authentication:
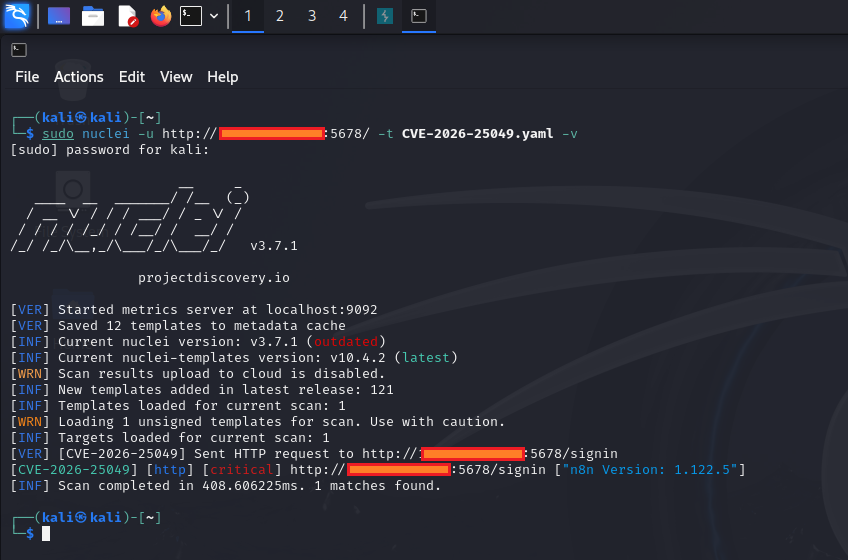
GET /rest/settings
📤 Exposed Data May Include
- 🔐 Authentication method (e.g., email login)
- 🌐 Instance mode (e.g.,
public)
- ⚙️ Feature flags and runtime settings
- 🧩 Application configuration metadata
This endpoint should normally be restricted to authenticated users, but misconfigurations or vulnerable versions may expose it publicly.
⚠️ Impact
While not directly leading to full system compromise, this vulnerability can:
- 📡 Leak sensitive configuration details
- 🧠 Enable target fingerprinting
- 🔗 Facilitate attack chaining with other vulnerabilities
- 🎯 Reduce complexity of further attacks
💡 Even limited information disclosure can significantly weaken overall security posture.
📦 Affected Versions
- Confirmed on:
n8n v1.123.5
- Other versions may be affected depending on configuration
⚠️ Always verify against official advisories and changelogs.
✅ Verification (High-Level)
To verify the vulnerability:
-
Send a request to:
/rest/settings
-
Observe the response behavior.
✔️ Expected Behavior (Secure)
401 Unauthorized- Authentication required
❌ Vulnerable Behavior
200 OK- JSON response containing configuration data
🛡️ Mitigation
To secure your instance of n8n:
- 🔄 Update to the latest patched version
- 🔒 Restrict access to port
5678 (VPN, firewall, IP allowlist)
- 🚫 Avoid exposing n8n directly to the public internet
- 🔑 Enforce proper authentication mechanisms
- 🧱 Place behind a reverse proxy with access controls
🧠 Security Notes
- Exposure often depends on deployment configuration
- Instances running in public mode are more likely affected
- Common in misconfigured self-hosted environments
- Should be treated as part of a larger attack surface
📊 Risk Summary
| Factor | Assessment |
|---|
| Attack Complexity | Low |
| Privileges Required | None |
| User Interaction | None |
| Impact Scope | Partial (Info Leak) |
| Exploitability | High (if exposed) |
📎 Disclaimer
⚠️ This project is intended for educational purposes and authorized security testing only.
Do not test or scan systems without explicit permission.
⭐ Contribution & Usage
If you find this useful:
- ⭐ Star the repository
- 🛠️ Use responsibly in labs or authorized engagements
- 📢 Share knowledge ethically
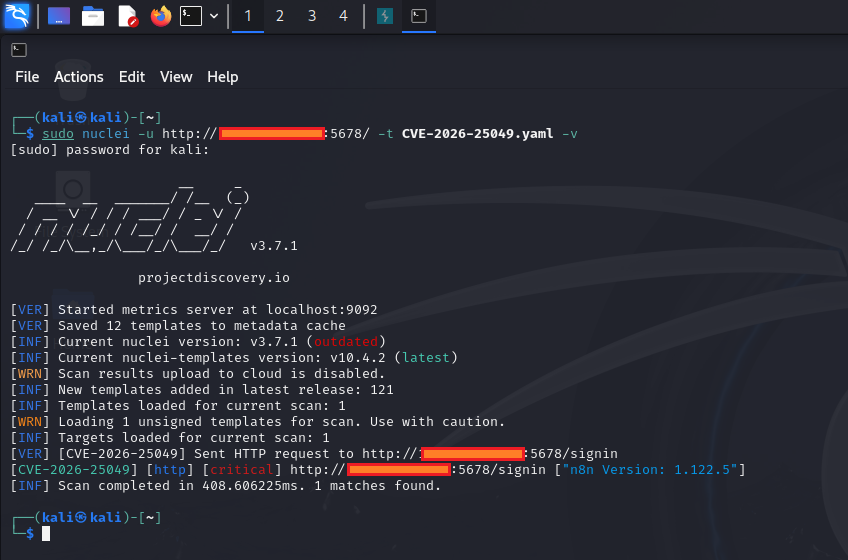
 0xblackash/cve-2026-25049