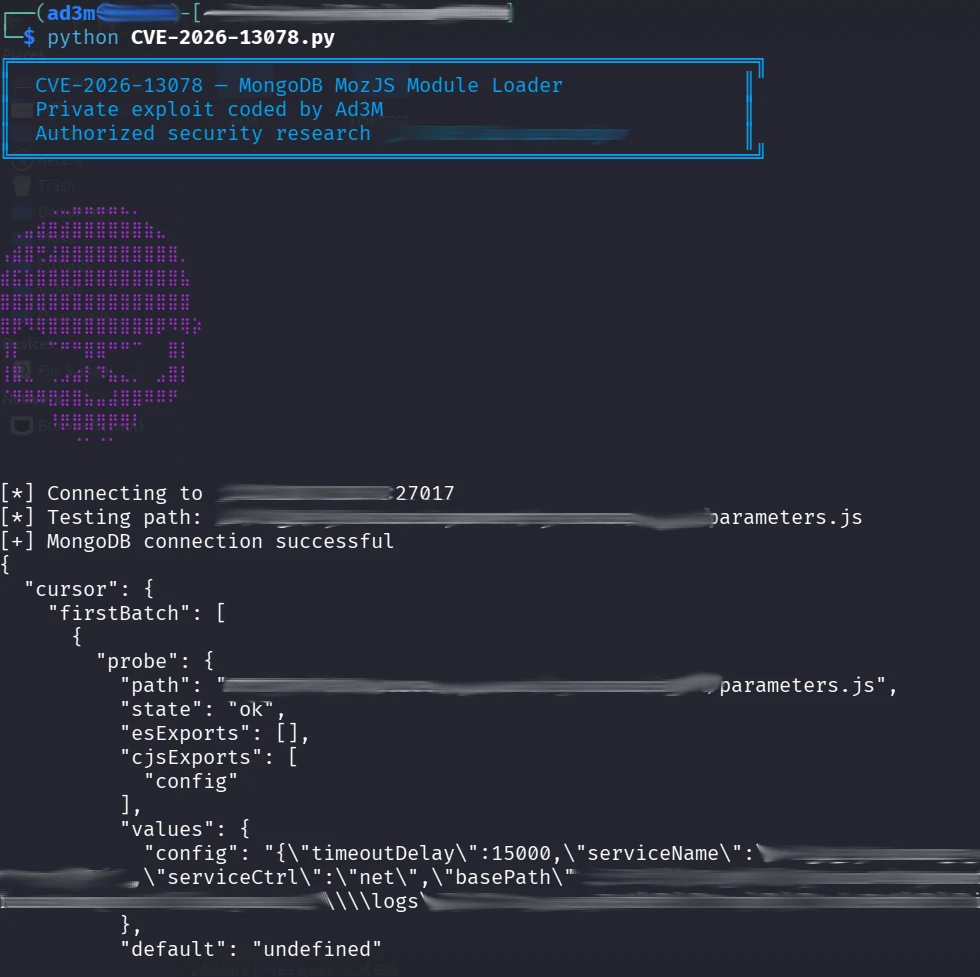
 0xad3m/cve-2026-13078-poc
Python proof-of-concept for CVE-2026-13078, a MongoDB MozJS module-loader authorization flaw (CWE-862) allowing authenticated users to disclose local files via server-side JavaScript.

Original PoC coded and developed by Ad3M.
Authorized security research only. Run this repository only against MongoDB instances you own or have explicit permission to test.
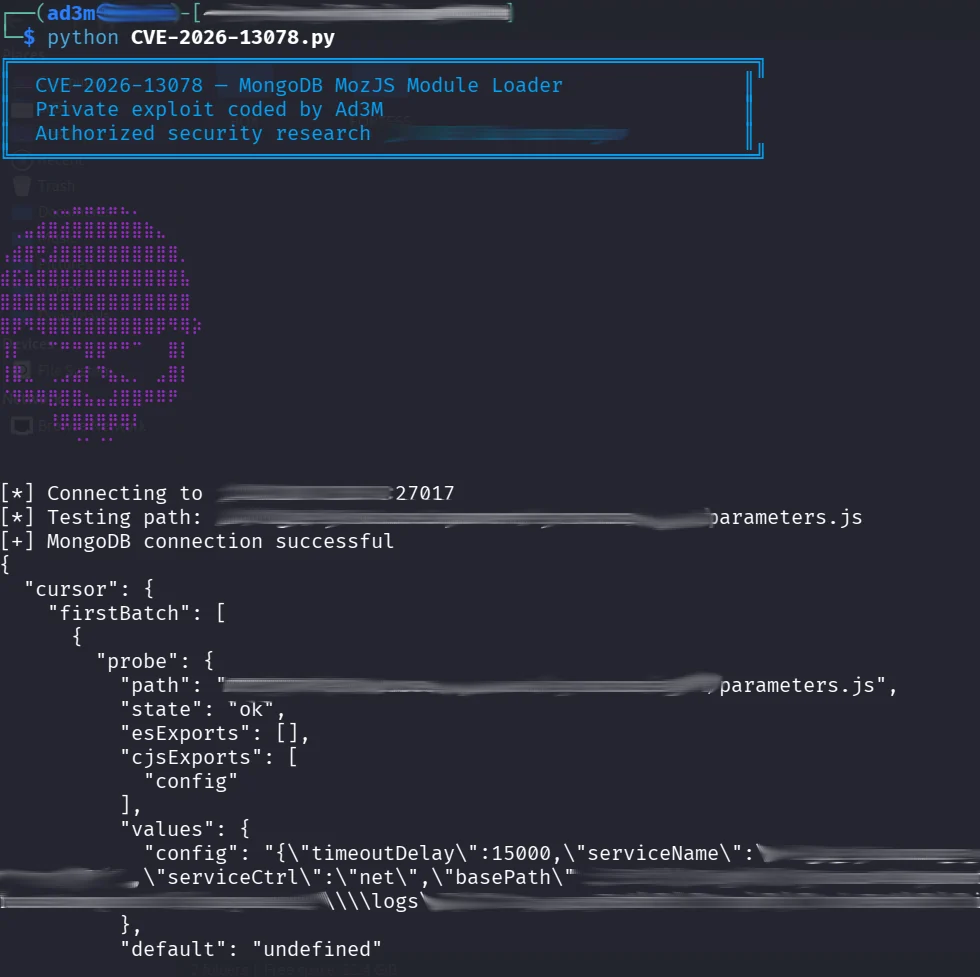
This repository contains a poc for CVE-2026-13078, a MongoDB Server MozJS module-loader authorization issue that may permit authenticated users to access files through server-side JavaScript.
During an authorized red team engagement, I identified a MongoDB instance in the organization's environment that was affected by CVE-2026-13078. After searching for a public proof of concept and finding none, I developed my own PoC to validate the vulnerability during the assessment.
The PoC successfully demonstrated disclosure of exported configuration data from a server-side JavaScript module. I'm now sharing my research publicly to help other security researchers and penetration testers reproduce and assess the issue in authorized environments.
| Field | Details |
|---|---|
| CVE | CVE-2026-13078 |
| Product | MongoDB Server |
| Vulnerability | Arbitrary local file disclosure |
| Component | MozJS scripting engine module loader |
| Weakness | CWE-862 — Missing Authorization |
| CVSS v3.1 | 7.7 (High) |
| CVSS v3.1 vector | CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:N/A:N |
| CVSS v4.0 | 6.3 (Medium) |
| Authentication | Required (low privileges), per the CVE record |
| Attack vector | Network |
| User interaction | None |
| Impact | File disclosure with the filesystem permissions of the mongod process |
| Public PoC | No existing public PoC found |
| Known exploitation | No confirmed in-the-wild reports found in the sources checked on October 12, 2026; CISA's July 23, 2026 assessment recorded exploitation as “none” |
Versions in each listed branch before its first fixed version are affected.
| Branch | First fixed version |
|---|---|
| MongoDB 7.0 | 7.0.39 |
| MongoDB 8.0 | 8.0.28 |
| MongoDB 8.2 | 8.2.12 |
| MongoDB 8.3 | 8.3.7 |
Sources: MongoDB-issued CVE record and CISA assessment, MongoDB advisory SERVER-128832
Initial research conclusion : The vulnerability was publicly documented, but I found no reproducible public exploit code during my initial search. This does not prove that no PoC existed. That gap motivated me to develop my own PoC.
pymongoInstall dependencies:
python -m pip install -r requirements.txt
Run the validation:
python poc.py --host 127.0.0.1 --port 27017
Apply the MongoDB vendor fix for your release line, restrict network access, use least-privilege database accounts, and disable server-side JavaScript where operationally possible.
Reference: https://jira.mongodb.org/browse/SERVER-128832
Do not include real secrets, host paths, credentials, or destructive payloads in issues, commits, screenshots, or logs. Report suspected vulnerabilities through the vendor’s coordinated disclosure process.
MIT. See LICENSE.






