
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
osint-suspicious-recruitment-case β€” OSINT investigation into a suspicious recruitment scheme involving miramedesdecasa | Kitploit
Tools/GitHubGitHub/0ggp4r1s/osint-suspicious-recruitment-case
OSINT (Open Source Intelligence)ReconnaissanceInformation GatheringSocial EngineeringPapers & ResearchLearning & EducationRepository Deleted
GitHub0ggp4r1s/osint-suspicious-recruitment-case

osint-suspicious-recruitment-case

OSINT investigation into a suspicious recruitment scheme involving miramedesdecasa

The upstream repository was not found during the latest Kitploit update check. This listing remains available for reference, but it has been removed from search results.
7136 months agoNot yet reviewed

Most Popular

View all β†’

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools β†’
Share

OSINT Investigation: Suspicious Recruitment Case

This repository documents an OSINT (Open Source Intelligence) investigation focused on a suspicious recruitment activity linked to multiple platforms, phone numbers, and online services.

The objective of this project is to analyze patterns, correlate data, and reconstruct the operational model using non-intrusive OSINT techniques.


Overview

The investigation started from a seemingly legitimate job offer that quickly revealed inconsistencies.

Through structured analysis, the case exposed:

  • A central communication node (phone number)
  • Presence across multiple platforms
  • Use of rotating phone numbers
  • Lack of persistent infrastructure
  • Repeated behavioral patterns

Key Findings

  • Phone numbers act as the core of the operation
  • No stable digital identity or infrastructure
  • Distributed presence across platforms
  • Evidence of evasive and adaptive behavior
  • Clear recruitment β†’ redirection β†’ escalation pattern

Full analysis:

  • analysis/findings.md

Methodology

The investigation follows a passive OSINT methodology based on:

  • Public data collection
  • Cross-platform correlation
  • Behavioral analysis
  • Tool-assisted enumeration

No intrusive or illegal techniques were used.

Full methodology:

  • analysis/methodology.md

Investigation Timeline

The investigation was conducted step by step, documenting how each discovery led to the next.

  • Initial job offer identification
  • Phone number pivoting
  • Platform correlation
  • Number rotation detection
  • Pattern consolidation

Full timeline:

  • analysis/timeline.md

Repository Structure

.
β”œβ”€β”€ analysis/
β”‚   β”œβ”€β”€ findings.md
β”‚   β”œβ”€β”€ methodology.md
β”‚   └── timeline.md
β”‚
β”œβ”€β”€ data/
β”‚   β”œβ”€β”€ domains.txt
β”‚   β”œβ”€β”€ email.txt
β”‚   └── phones.txt
β”‚
└── evidence/
    β”œβ”€β”€ ads/
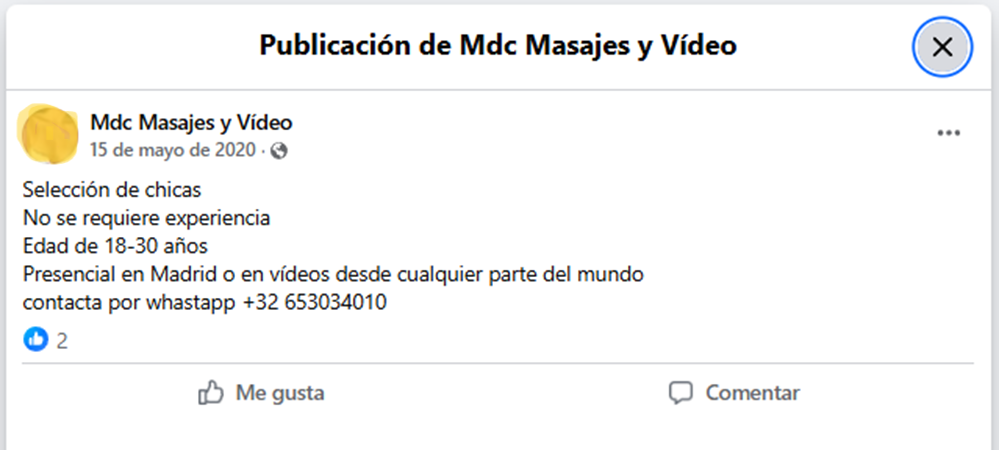
    β”‚   β”œβ”€β”€ facebook_post_recruitment.png
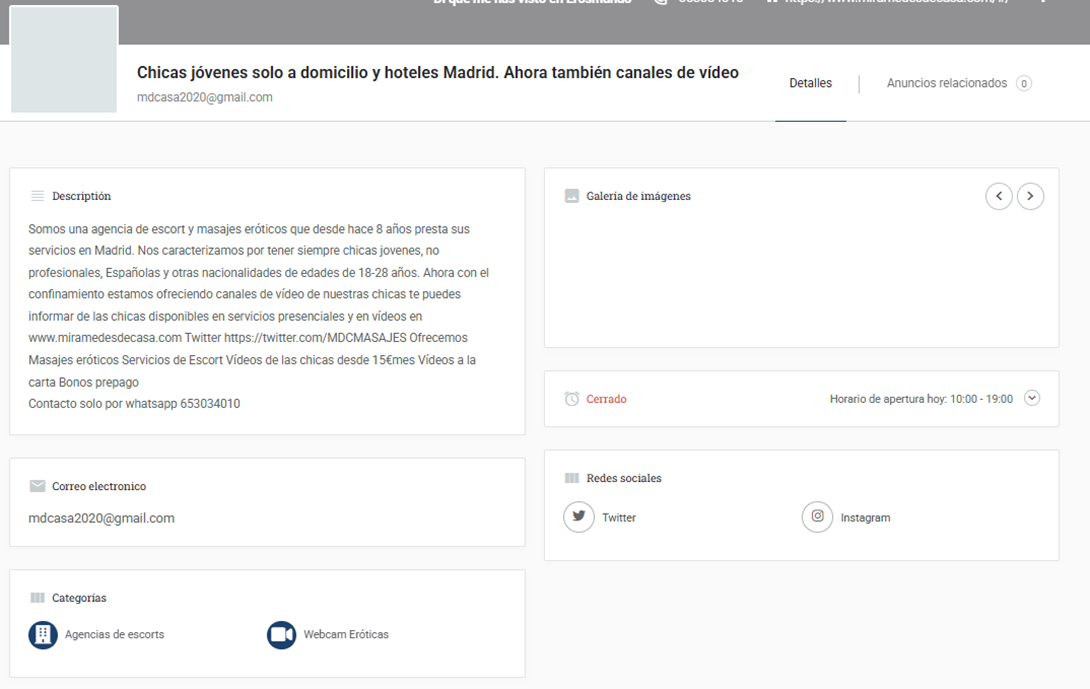
    β”‚   β”œβ”€β”€ web_listing_services.png
    β”‚   └── web_services_offers.png
    β”‚
    β”œβ”€β”€ chats/
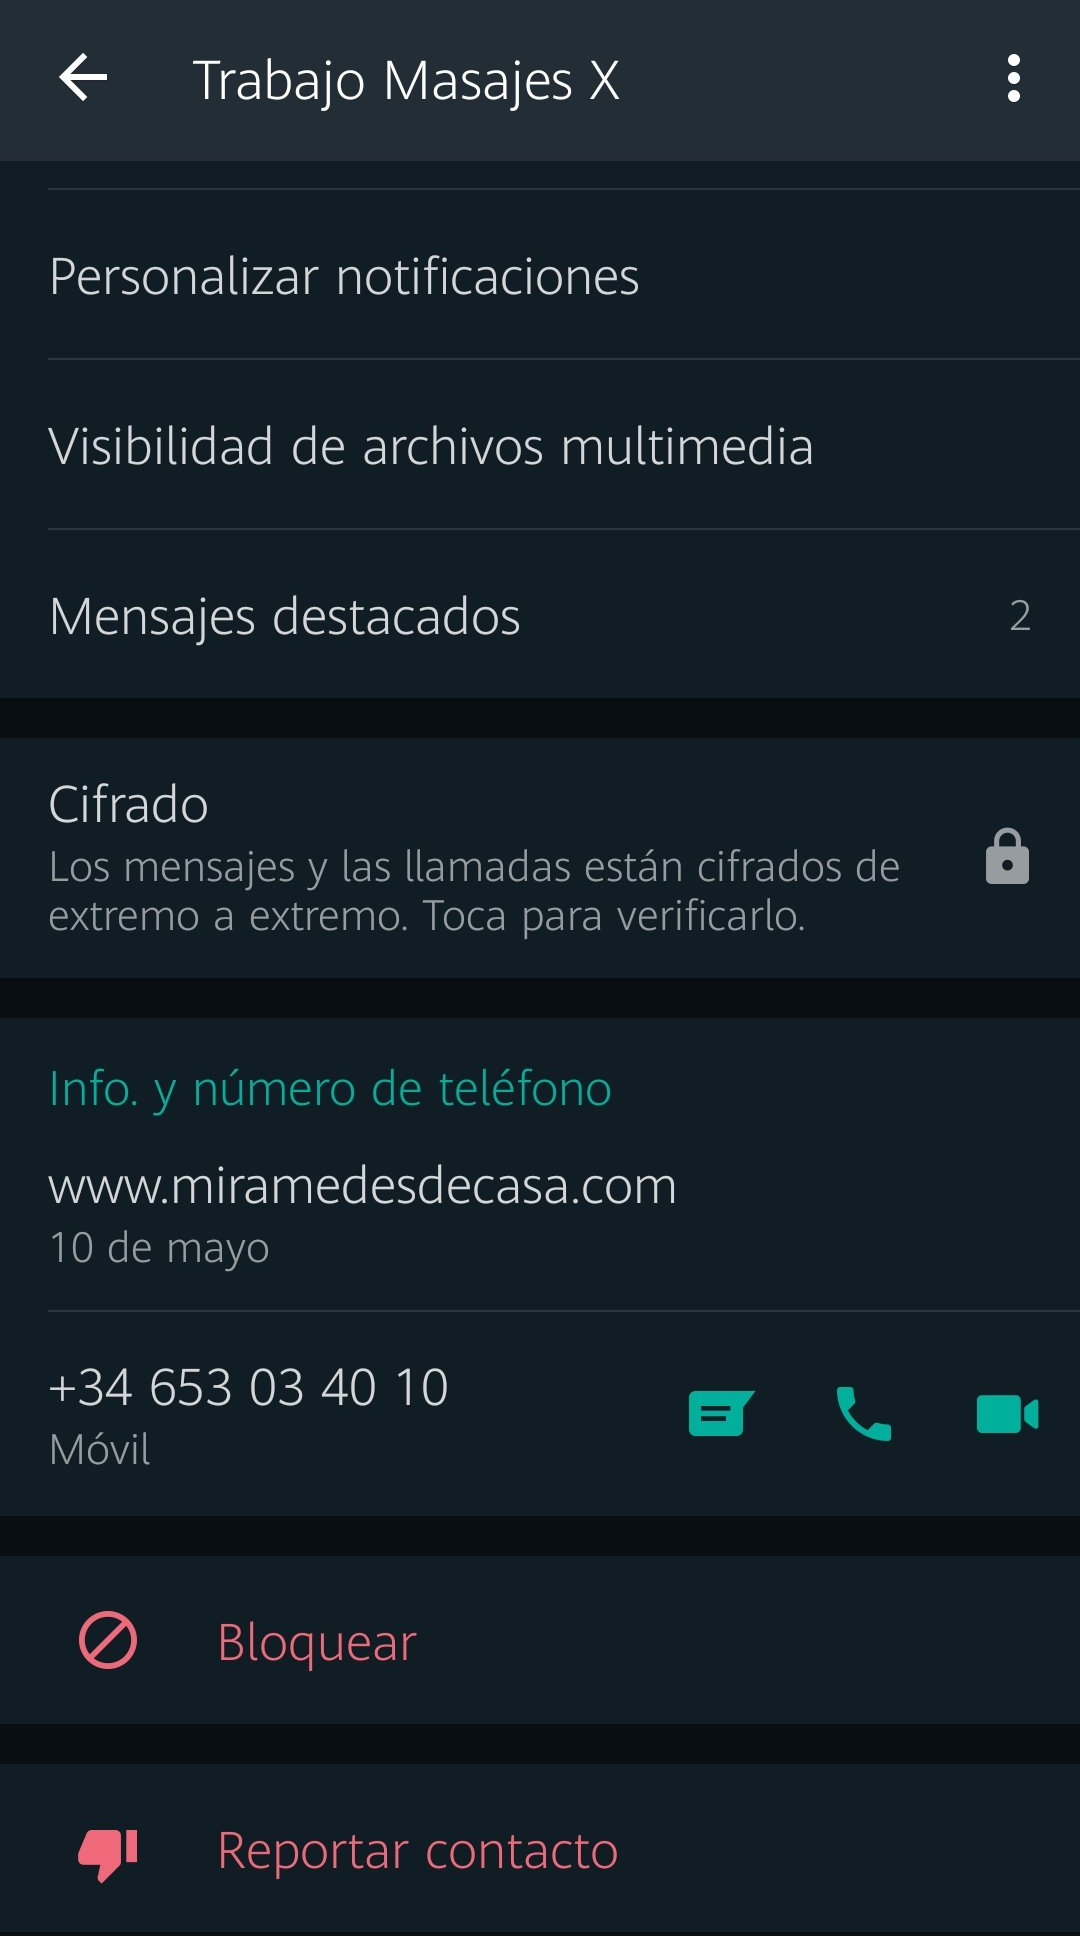
    β”‚   β”œβ”€β”€ whatsapp_contact_info.png
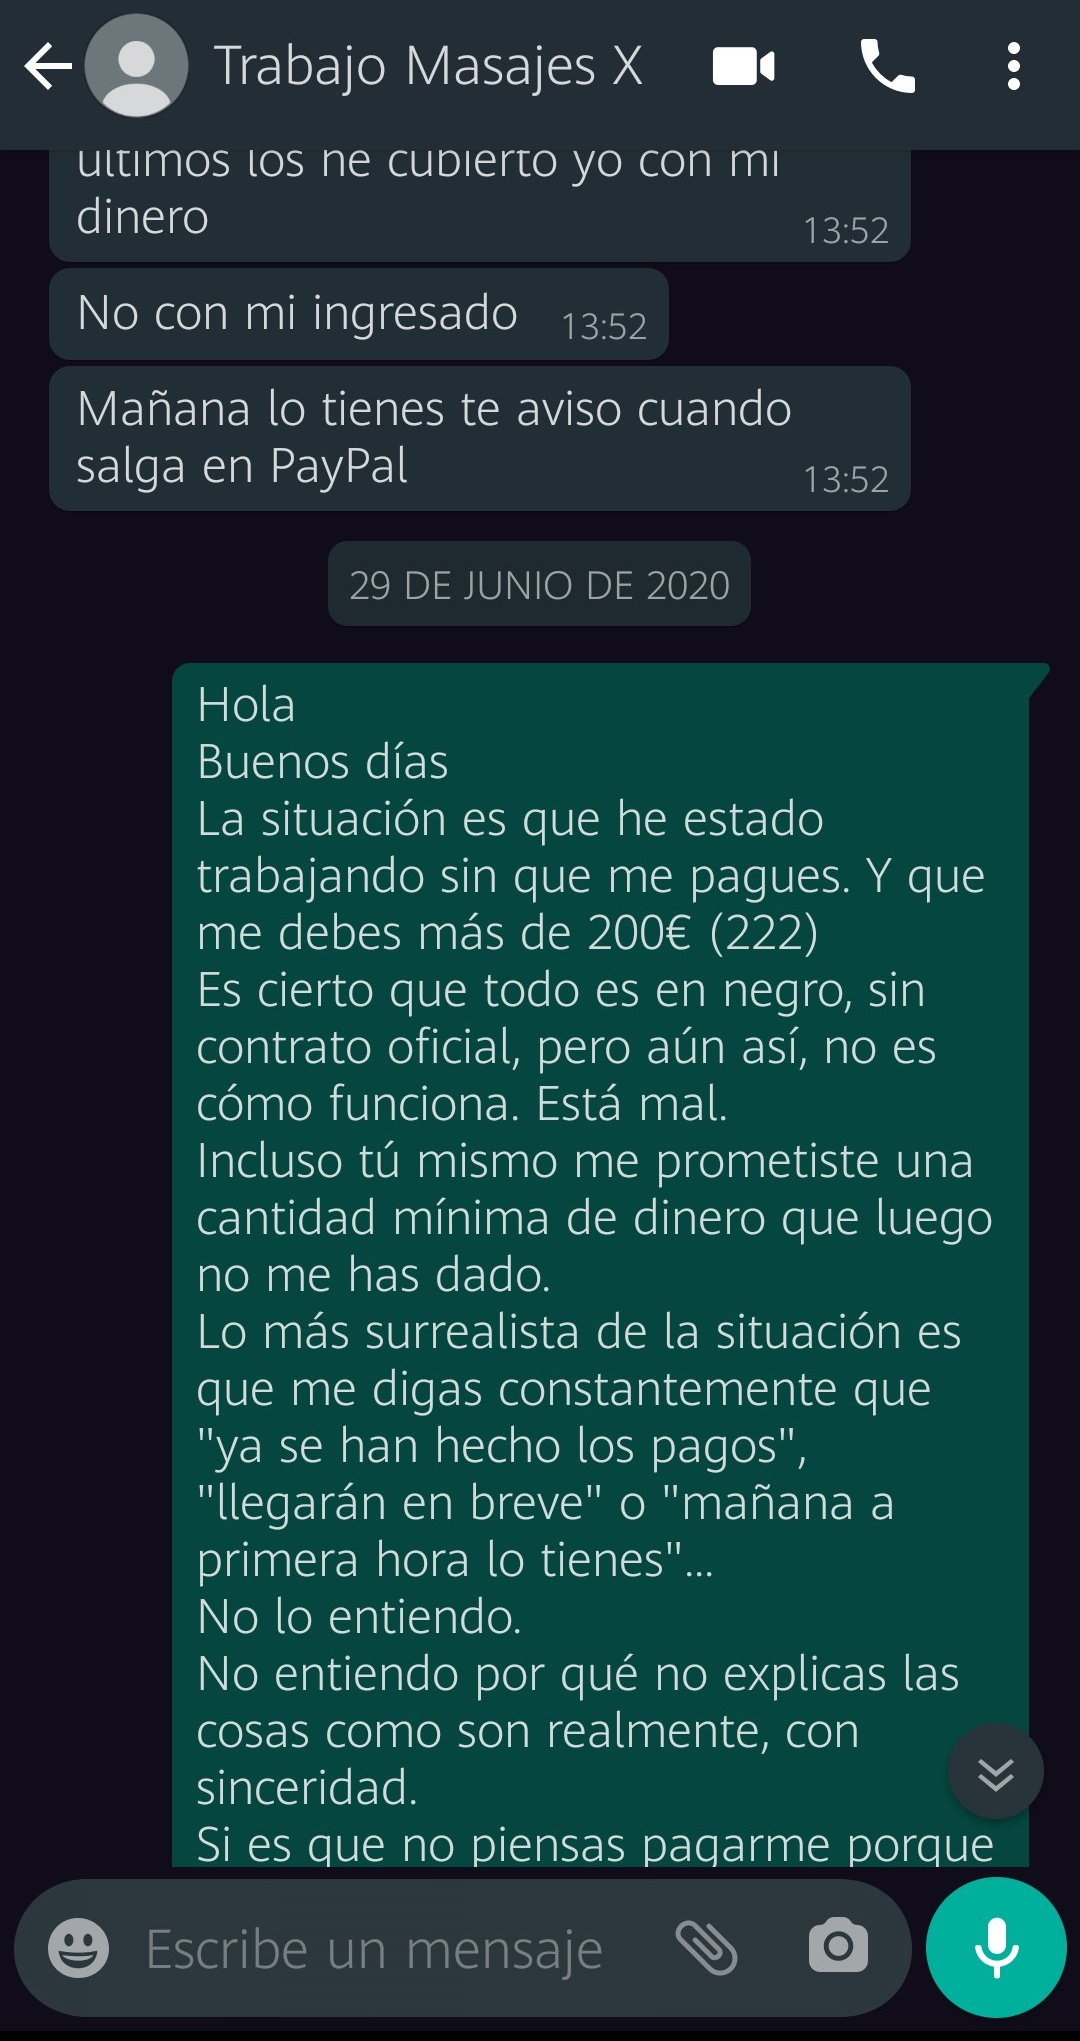
    β”‚   β”œβ”€β”€ whatsapp_debt_claim.png
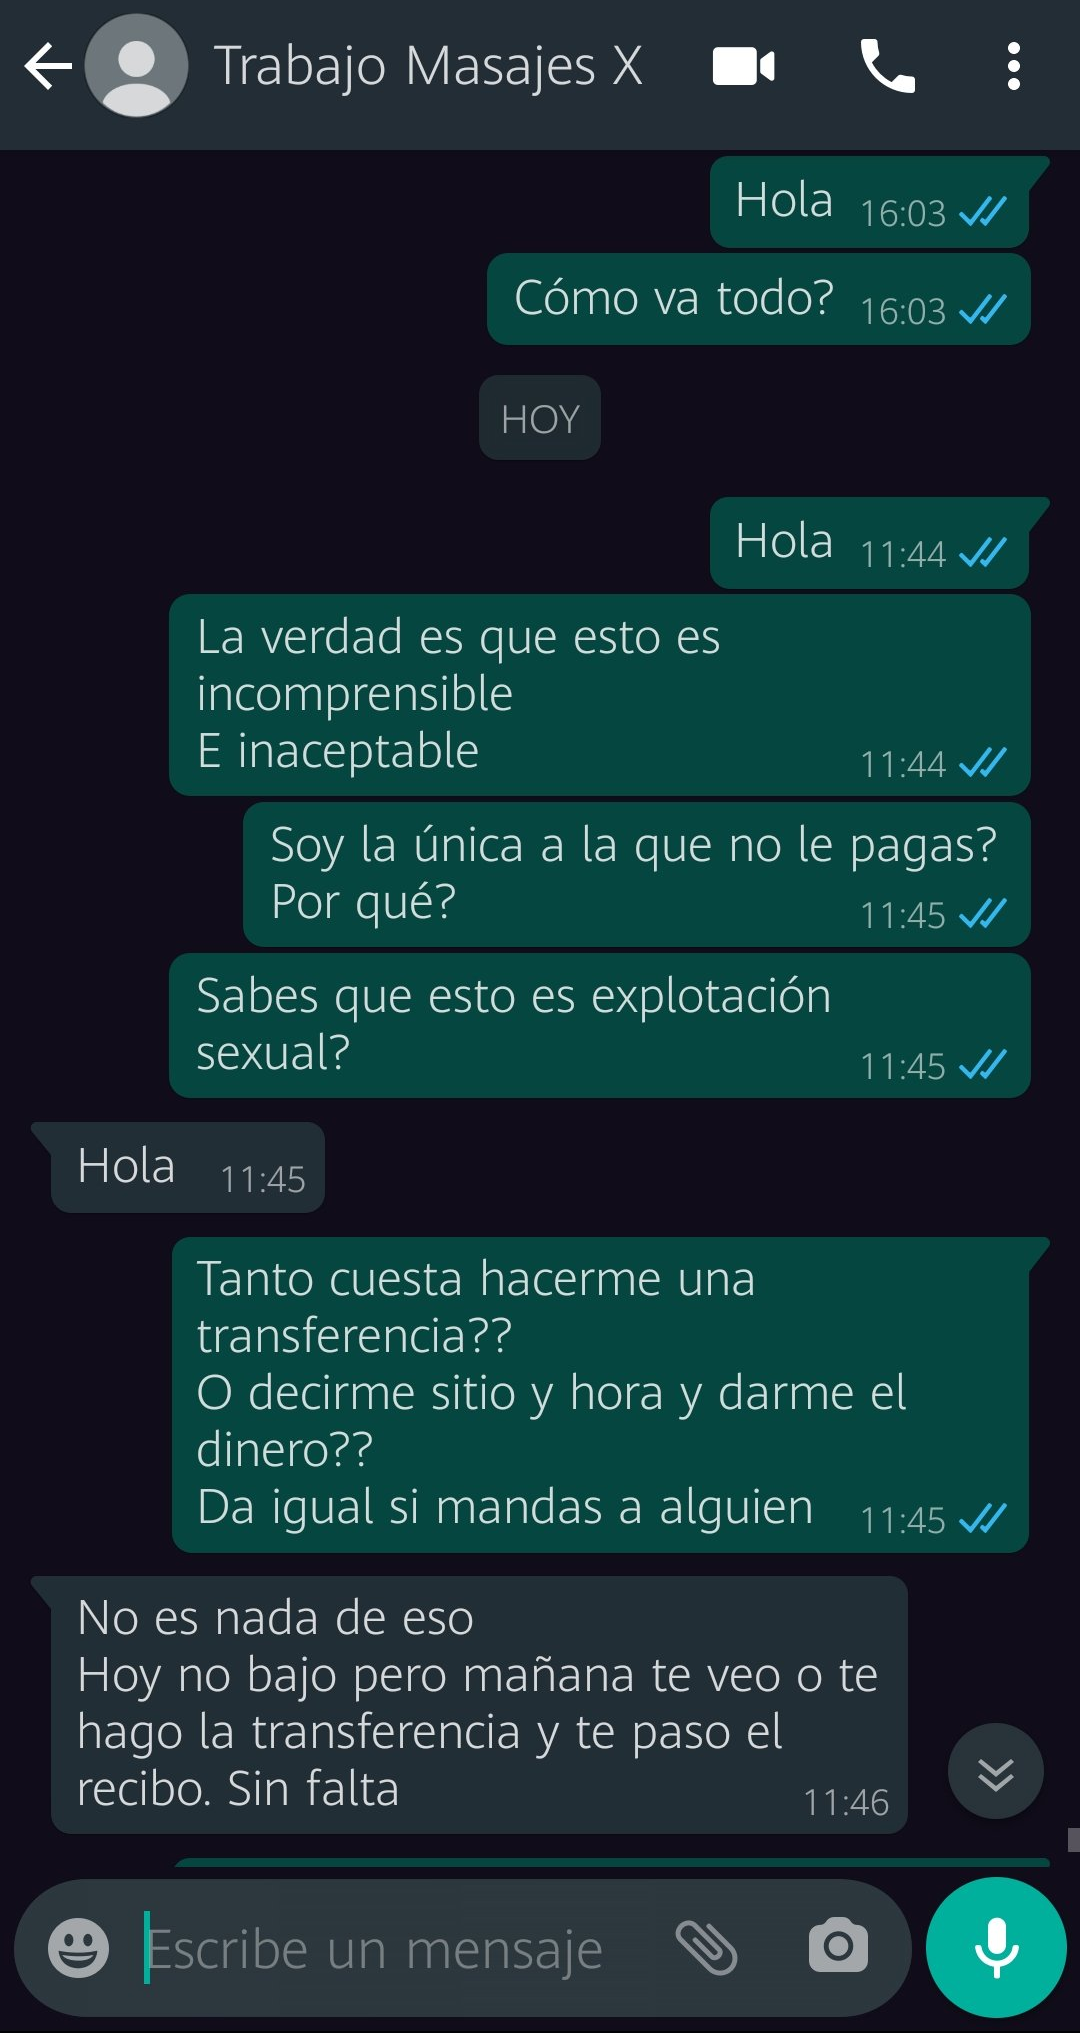
    β”‚   └── whatsapp_payment_excuses.png
    β”‚
    └── screenshots/
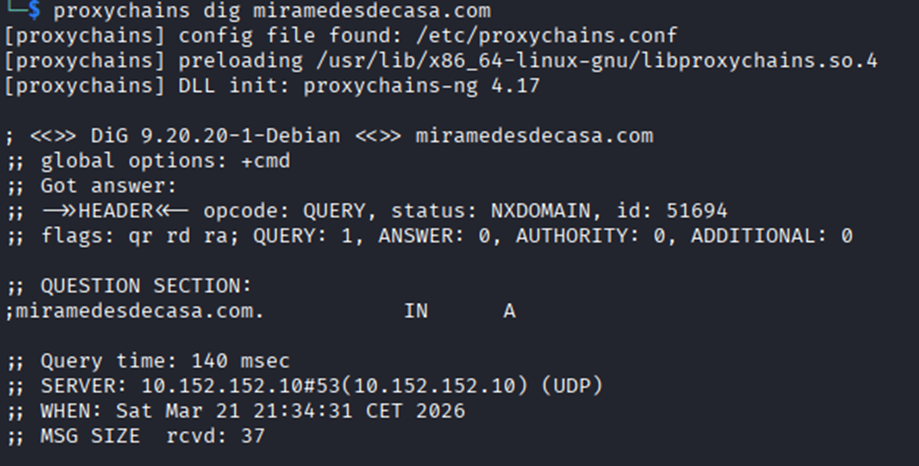
        β”œβ”€β”€ domain_nxdomain.png
        β”œβ”€β”€ external_victim_testimony_agata.png
        β”œβ”€β”€ facebook_contact_details.png
        β”œβ”€β”€ facebook_profile_mdc.png
        β”œβ”€β”€ facebook_profile_overview.png
        β”œβ”€β”€ forum_spalumi_complaint.png
        β”œβ”€β”€ google_search_3_phone.png
        β”œβ”€β”€ google_search_phone_main.png
        β”œβ”€β”€ google_search_secondary_phone.png
        β”œβ”€β”€ social_profile_inactive.png
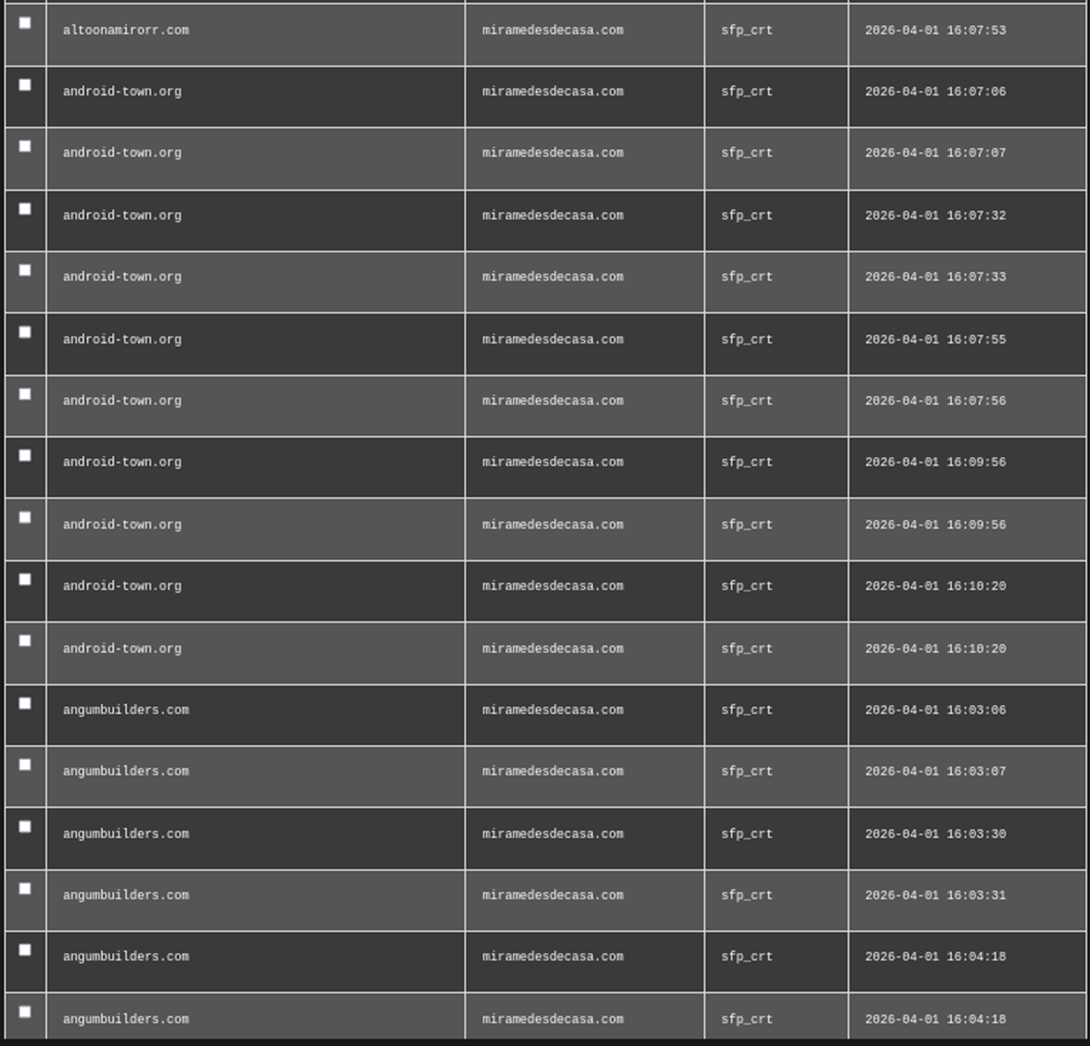
        β”œβ”€β”€ spiderfoot_cohosted_domains.png
        β”œβ”€β”€ spiderfoot_username_trabajochicasmadrid.png
        β”œβ”€β”€ technical_ip_result.png
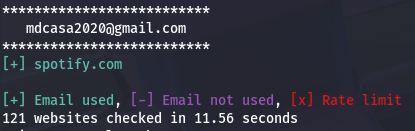
        β”œβ”€β”€ tool_holehe_email_analysis.png
        β”œβ”€β”€ tool_theharvester_no_results.png
        β”œβ”€β”€ twitter_complaint_agata.png
        β”œβ”€β”€ twitter_profile.png
        └── twitter_recruitment_post.png
Evidence Samples

Recruitment Content

Facebook Recruitment


WhatsApp Interaction

WhatsApp Contact
Debt Claim
Payment Excuses


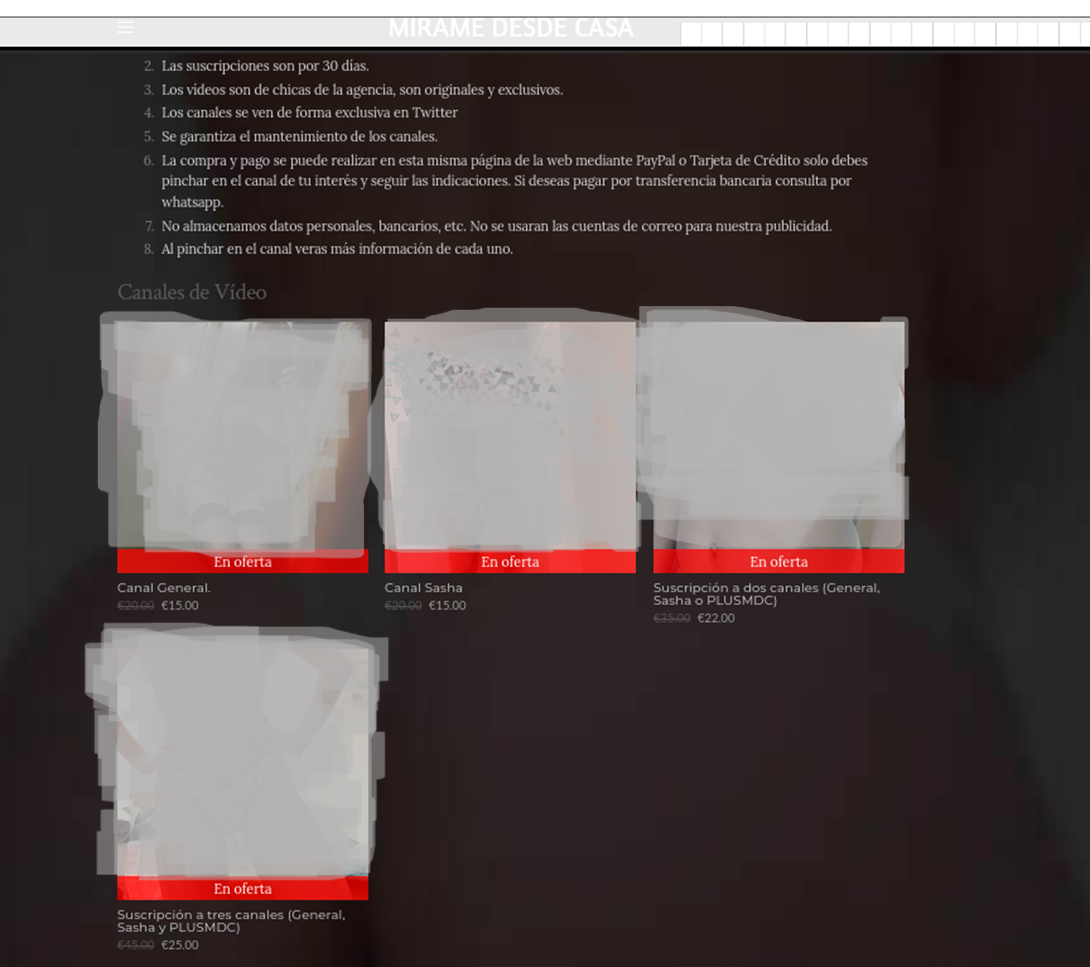
Web & Services

Web Listing
Service Offers


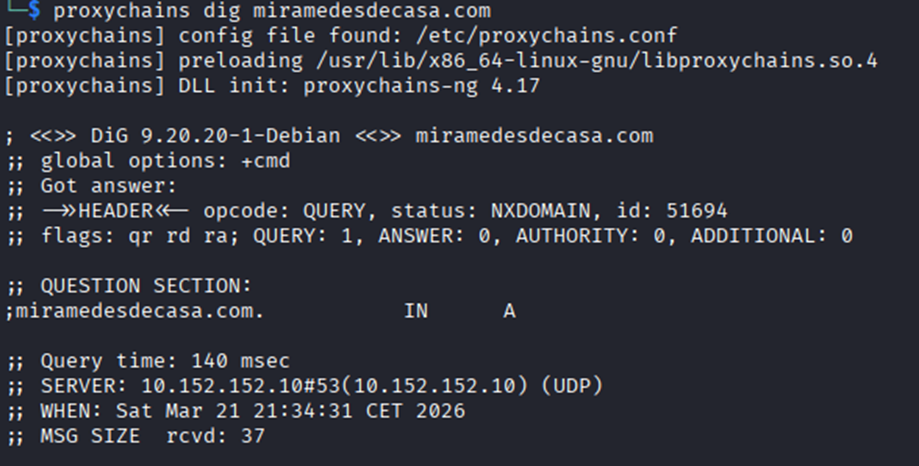
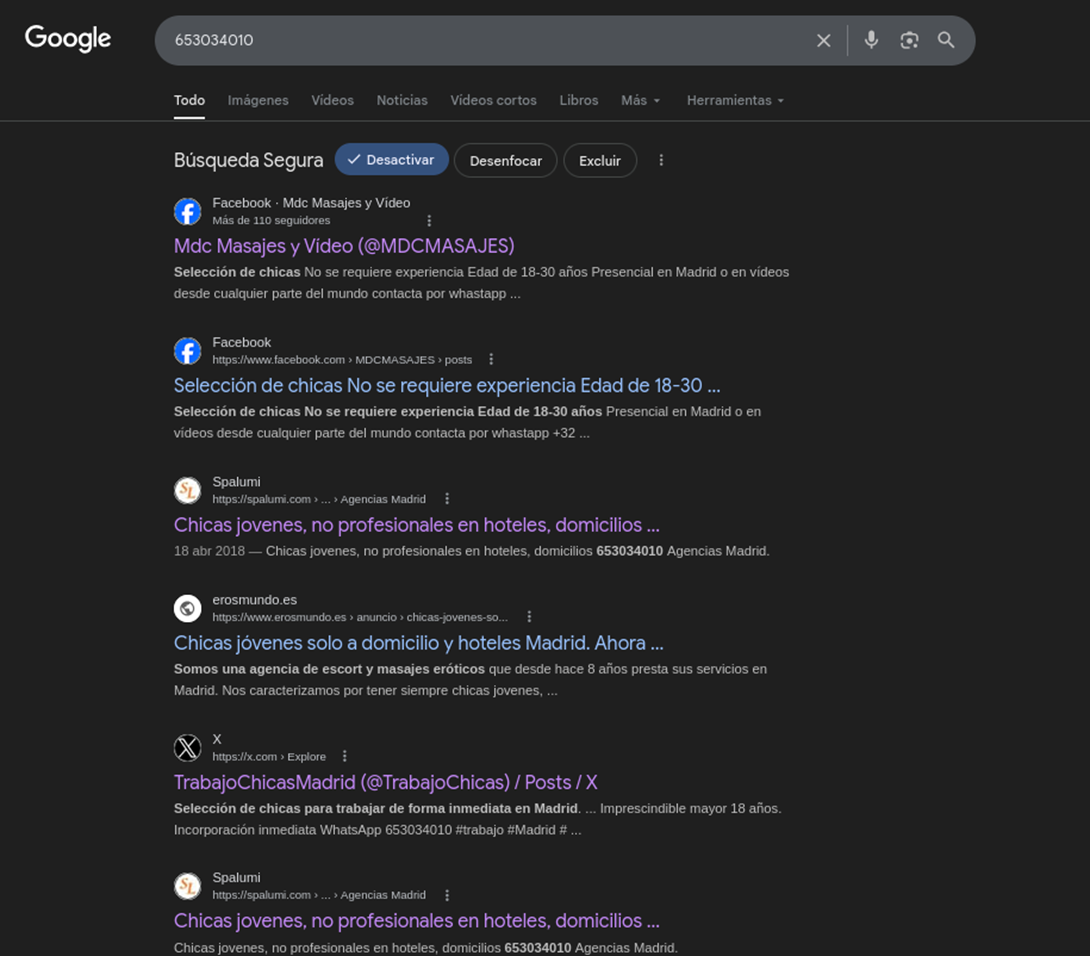
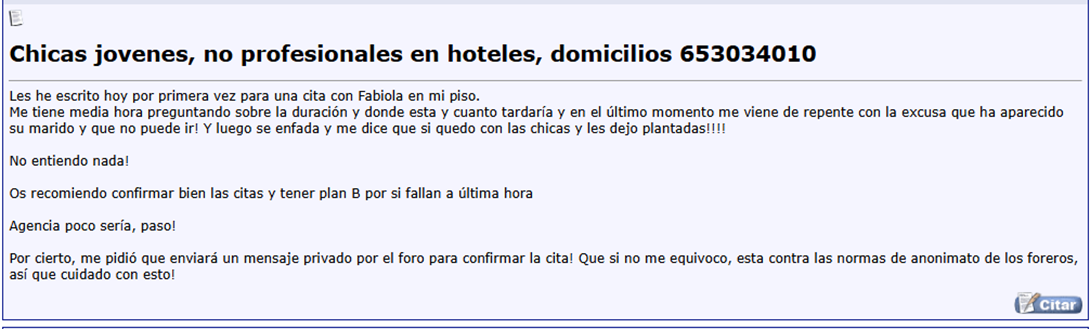
OSINT & Technical Analysis

NXDOMAIN
Google Search
Forum Evidence
SpiderFoot
Holehe


Key Indicators

The following elements were consistently linked across the investigation:

  • Phone numbers
  • Domain: miramedesdecasa.com
  • Email: [email protected]
  • Social media accounts

These elements only become meaningful when analyzed together, not individually.


⚠️ Disclaimer

This project is based entirely on:

  • Open Source Intelligence (OSINT)
  • Publicly available data
  • Provided materials

No claims of illegal activity are made.
All conclusions are analytical and non-conclusive.


Final Insight

The operation does not rely on infrastructure, but on communication.

By avoiding persistence and rotating identifiers, the activity achieves:

  • Low traceability
  • High adaptability
  • Operational continuity

About This Project

This project was developed as part of a learning process in:

  • Cybersecurity
  • OSINT investigations
  • Pattern analysis
  • Real-world case studies