

Apkx-Hunter v2.7.0
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning with ML-assisted secret classification.
APKX-Hunter v2.7.2 — Debian Package 

APKX-Hunter is an open-source Android Static Analysis Framework written entirely in C, purpose-built for Android security assessments, reverse engineering, malware analysis, OWASP MASVS compliance scanning, bug bounty hunting, and penetration testing.
The framework supports both single-application and large-scale Android application analysis by automatically extracting and analyzing supported Android package formats, including APK, APKS, APKM, XAPK, and ZIP archives. With Recursive Multi-APK Scanning and Silent Batch Mode, APKX-Hunter is designed to efficiently process large Android application collections while producing clean, organized, and actionable results.
APKX-Hunter combines multiple static analysis techniques—including decompilation, AndroidManifest analysis, permission analysis, exported component detection, endpoint discovery, hardcoded secret detection, cloud configuration discovery, native library detection, and OWASP MASVS security checks—to uncover security-relevant information inside Android applications.
APKX-Hunter also integrates a lightweight Machine Learning-based Secret Classification Engine, written entirely in C, which automatically classifies detected secrets by confidence and severity helping security researchers prioritize high-value findings, reduce false positives, and accelerate vulnerability triage.
At the end of every scan, APKX-Hunter generates detailed scan statistics, including the number of APKs scanned, files analyzed, secrets detected, patterns detected, and MASVS findings, providing researchers with a comprehensive overview of the entire security assessment.
- GitHub: https://github.com/SyscallX-18113/Apkx-Hunter
- Developed by: SyscallX-18113
- Version: v2.7.2
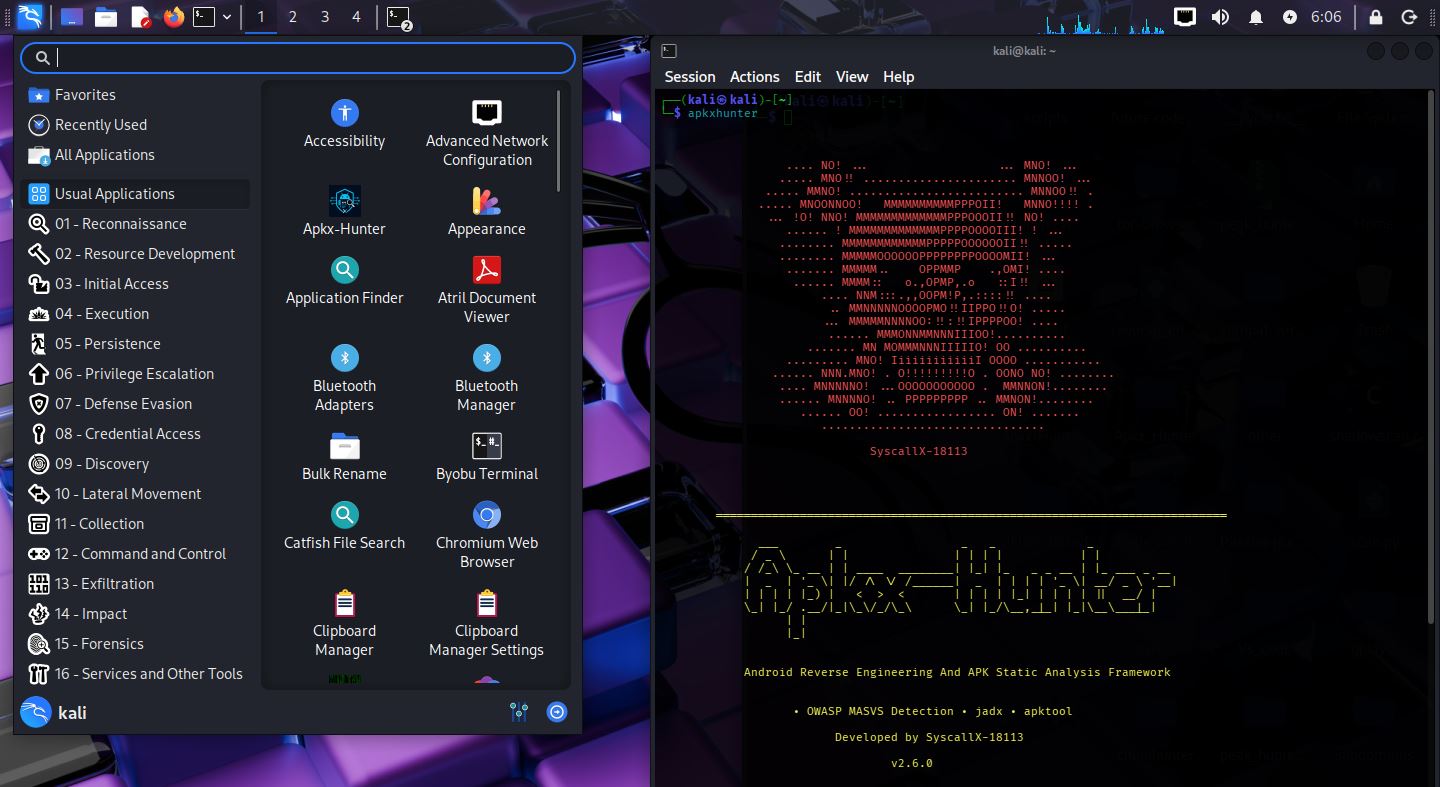
OWASP MASVS Scanning Support
Apkx-Hunter now includes OWASP MASVS security scanning with 15 categories and 166 detection patterns:
| # | Category | Patterns |
|---|---|---|
| 1 | Weak Cryptography | 28 |
| 2 | Certificate Pinning | 13 |
| 3 | Root Detection | 20 |
| 4 | Anti Debugging | 9 |
| 5 | Anti Tamper | 3 |
| 6 | SharedPreferences | 8 |
| 7 | SQLite | 9 |
| 8 | External Storage | 11 |
| 9 | Dynamic Code Loading | 10 |
| 10 | Reflection | 9 |
| 11 | Runtime Command Execution | 9 |
| 12 | WebView Security | 13 |
| 13 | Network Security | 10 |
| 14 | SSL Validation | 10 |
| 15 | Native Library Loading | 9 |
| TOTAL | 166 |
OWASP Validation
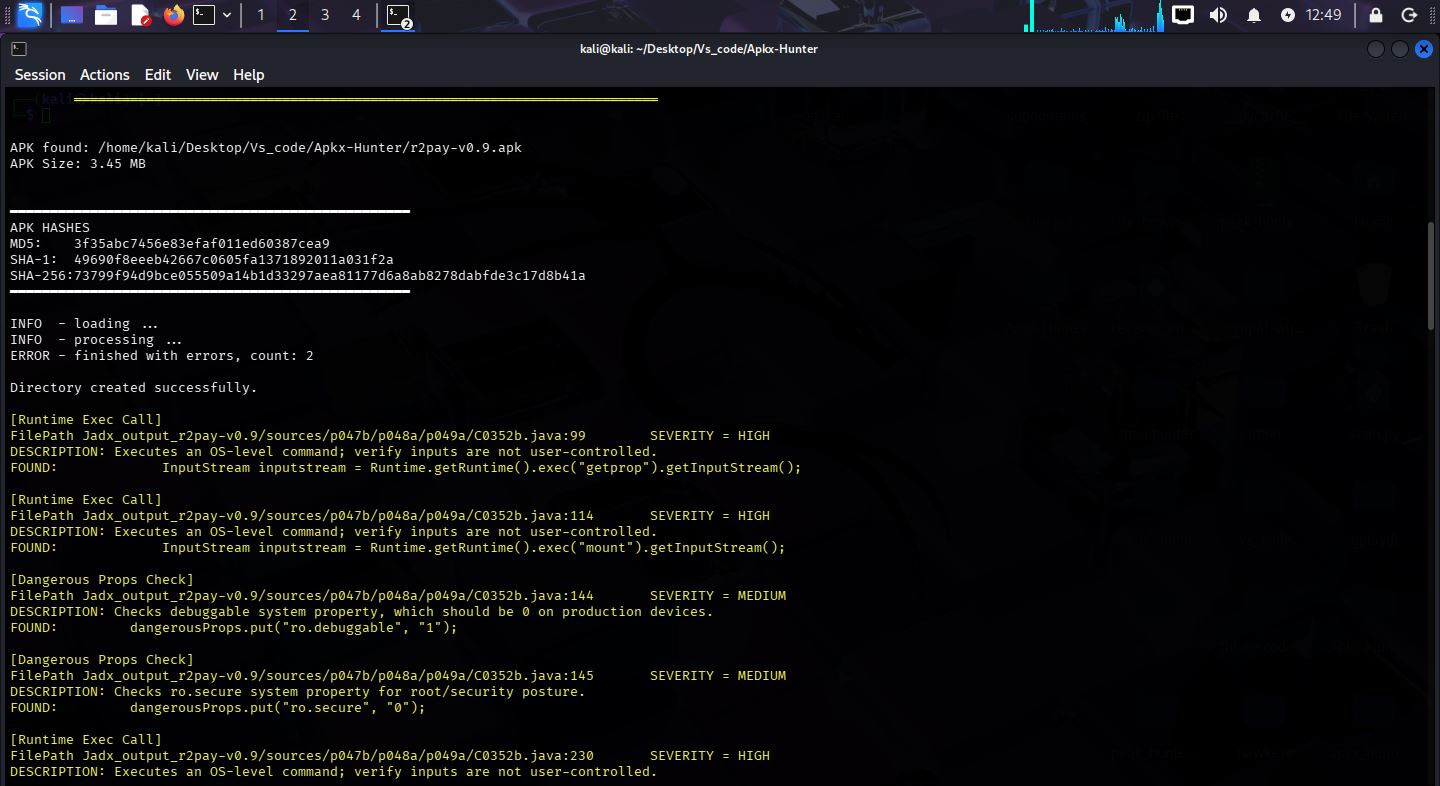
APKXHunter has been tested against the OWASP UnCrackable Level 4 application. The scan successfully identified multiple security findings, demonstrating the effectiveness of its OWASP MASVS scanning engine and Android static analysis capabilities.
Features
- Linux & Debian Integration — Native Debian package (.deb), System-wide installation, Desktop application launcher, Application menu integration, Custom application icon, Automatic framework asset installation, Built-in dependency manager (--install-dependencies)
- OWASP MASVS Support — Apkx-Hunter now includes comprehensive OWASP MASVS security scanning with 14+ categories and 160+ detection patterns:
- JADX Decompilation — Fast and deep decompilation modes
- APKTool Decompilation — Full APKTool-based decompilation and scanning
- Archive Extraction — Support for APK, APKM, APKS, XAPK, and ZIP formats
- Decompiled Folder Scanning — Scan any already-decompiled JADX source directory
- APKTool Folder Scanning — Scan any already-decompiled APKTool directory
- Secret Detection — Discover API keys, tokens, passwords, and embedded secrets
- Endpoint Discovery — Identify URLs, endpoints, and security-relevant patterns
- Android Permission Analysis — Analyze permissions and exported activities
- Native (.so) Library Detection — Detect native libraries bundled in the app
- File Inventory Generation — Generate a complete file inventory report
- Machine Learning-based Secret Classification (Highlighted Feature) — ML-assisted confidence scoring for detected secrets to accelerate triage and reducing false positive in secrets finding
- Recursive Multi-APK Scanning — Automatically scan multiple APKs recursively for large-scale Android application analysis
- Automatic Package Extraction — Automatically extract and analyze APKs from APKS, APKM, XAPK, and ZIP package formats
- Silent Batch Mode — Cleaner terminal output during large-scale scans while preserving analysis results
- End-of-Scan Statistics — Display detailed scan summary including APKs scanned, files analyzed, secrets detected, patterns detected, and MASVS findings
- Enhanced Command-Line Interface — Improved argument parsing, input validation, and user-friendly error reporting
- Improved Framework Stability — Enhanced error handling, memory management, and overall framework reliability
Machine Learning Model
APKXHunter uses an offline machine learning classifier. model.bin contains only trained numerical weights used to calculate the confidence score of detected secrets.
It is NOT executable.
It contains no code.
It is loaded as binary data only.
- Offline ML Inference — All model inference runs locally, with no cloud APIs or internet connection required
- Confidence Probability Scoring — Each detected secret receives a confidence probability from the trained model
Project Statistics
- Language: C
- Codebase: 5,800+ lines
- Architecture: Modular
- Platform: Linux
Platform Support
- Linux (Supported)
- Windows (Not Supported)
- macOS (Not Supported)
Performance
The following results are based on testing performed during development.
| Metric | Tested Value |
|---|---|
| Operating System | Kali Linux |
| RAM Used for Testing | 8 GB |
| CPU | Intel Core i3-2120 |
| Largest APK Successfully Decompiled or Scanned | 85 MB |
| Average Decompilation Time | ~50 - 60 seconds |
System Requirements
Minimum:
- Linux
- 4 GB RAM
- JADX
- APKTool
- unzip
Recommended:
- Linux
- 8 GB RAM or higher
- Quad-core CPU
- SSD storage
ML Secret Classification
APKXHunter integrates a lightweight Machine Learning-based Secret Classification Engine, written entirely in C, as part of its secret detection workflow. This is a statistical Machine Learning model — not a Large Language Model, ChatGPT, Generative AI, or Deep Learning system.
- Secrets detected by APKXHunter are analyzed by the integrated Machine Learning classification engine.
- The model estimates the probability that a detected secret is valid or security-sensitive.
- Findings are prioritized using confidence-based severity scoring.
- The ML engine assists researchers in triaging findings faster.
- The ML engine is designed to assist human analysis rather than replace manual verification.
How It Works
- Detect potential secret.
- Extract statistical features (entropy, character distribution, length, uppercase/lowercase ratios, digits, symbols, and other statistical token characteristics).
- Load trained model (
model.bin). - Perform ML inference.
- Produce a confidence probability.
- Present results to the user for manual verification.