
secretlint v13.0.3
Pluggable linting tool to prevent committing credential.
Secretlint 
Secretlint is a Pluggable linting tool to prevent committing credentials.
Features
- Scanner: Find credentials in a project and report these
- Project Friendly: Easy to set up your project and integrate CI services
- Pre-Commit Hook: Prevent committing credential files
- Pluggable: Allow creating custom rule and flexible configuration
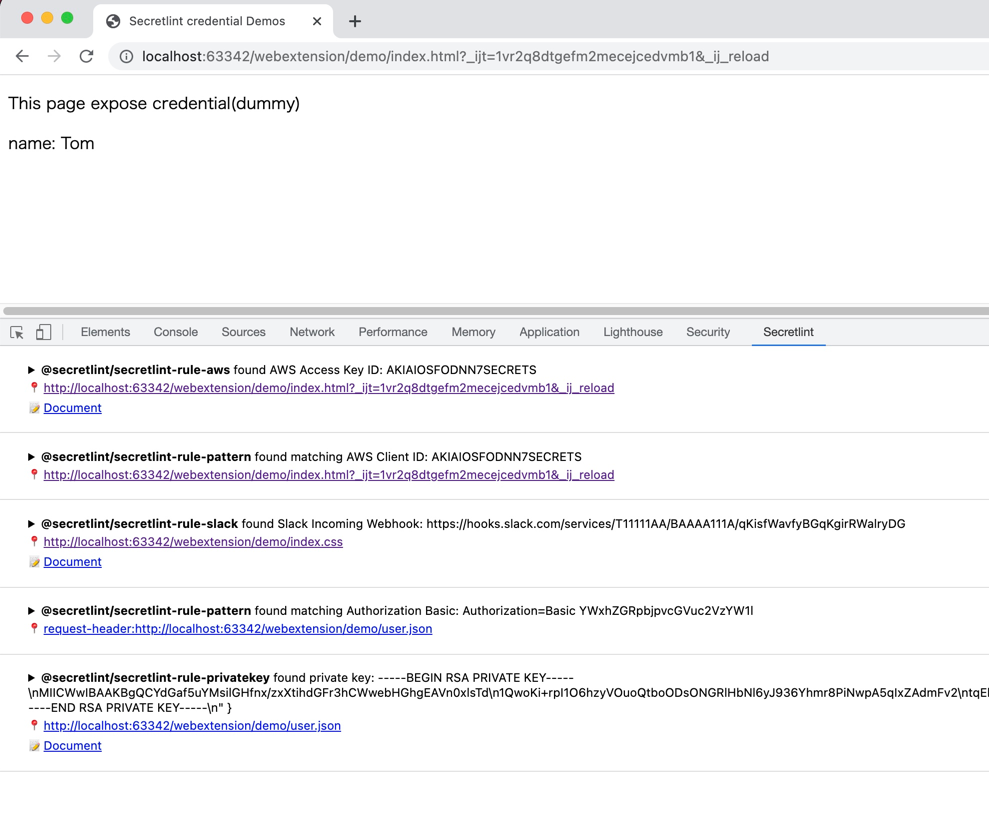
- Documentation: Describe the reason that rule detect it as secret
Quick Demo
You can view secretlint linting result on https://secretlint.github.io/.
Quick Start
You can try to use Secretlint on your project at one command.
If you already have installed Docker:
docker run -v `pwd`:`pwd` -w `pwd` --rm -it secretlint/secretlint secretlint "**/*"
If you already have installed Node.js:
npx @secretlint/quick-start "**/*"
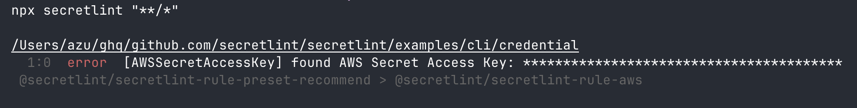
After running,
If you got empty result and exit status is 0, your project is secure.
Otherwise, you got some error report, your project includes credential as raw data.
You want to get continuous security, Please see following installation guide and setup pre-commit hook and CI.
Installation
Using Docker
Prerequisites: Require Docker
Use our Docker container to get an environment with Node.js and secretlint running as fast as you can download them.
You can check all files under the current directory with secretlint by following command:
docker run -v `pwd`:`pwd` -w `pwd` --rm -it secretlint/secretlint secretlint "**/*"
secretlint/secretlint docker container work without configuration by design.
This Docker Image has built-in packages:
- @secretlint/secretlint-rule-preset-recommend
- @secretlint/secretlint-rule-pattern
- @secretlint/secretlint-formatter-sarif
For more details, please see secretlint's Dockerfile.
Using Node.js
Prerequisites: Require Node.js 22+.
Secretlint is written by JavaScript. You can install Secretlint using npm:
npm install secretlint @secretlint/secretlint-rule-preset-recommend --save-dev
You should then set up a configuration file:
npx secretlint --init
Finally, you can run Secretlint on any file or directory like this:
npx secretlint "**/*"
📝 Secretlint supports glob pattern and glob pattern should be wrapped by a double quote.
It is also possible to install Secretlint globally using npm install --global. But, We do not recommend it, some rules may be broken globally.
Using Single-Executable Binary
Prerequisites: None
You can use secretlint command without Node.js by using a single-executable binary.
- Download the latest binary from Releases page
- Change the file permission to executable:
chmod +x ./secretlint - Run
./secretlint --initto create a configuration file - Run
./secretlint "**/*"to lint your project
For more details, please see publish/binary-compiler README.
Usage
secretlint --help shows Usage.
Secretlint CLI that scan secret/credential data.

Usage
$ secretlint [file|glob*]

Note
supported glob syntax is based on picomatch (the engine used by micromatch)
https://github.com/micromatch/picomatch#globbing-features
https://github.com/micromatch/micromatch#matching-features

Options
--init             setup config file. Create .secretlintrc.json file from your package.json
--format           [String] formatter name. Default: "stylish". Available Formatter: checkstyle, compact, github, jslint-xml, junit, pretty-error, stylish, tap, unix, json, mask-result, table
--output           [path:String] output file path that is written of reported result.
--secretlintrc     [path:String] path to .secretlintrc config file. Default: .secretlintrc.*
--secretlintignore [path:String] path to .secretlintignore file. Default: .secretlintignore
--stdinFileName    [String] filename to process STDIN content. Some rules depend on filename to check content.
--no-color         disable ANSI-color of output.
--no-terminalLink  disable terminalLink of output.
--no-maskSecrets   disable masking of secret values; secrets are masked by default.
--no-glob          disable glob pattern interpretation; treat all inputs as literal file paths.
--no-gitignore     disable .gitignore cascade respect; .gitignore files are
                   respected by default (since v13).

Options for Developer
--profile          Enable performance profile.
--secretlintrcJSON [String] a JSON string of .secretlintrc. use JSON string instead of rc file.

Experimental Options
--locale            [String] locale tag for translating message. Default: en

Examples
# Scan a single file
$ secretlint ./README.md

# Scan all files (wrap glob in double quotes to avoid shell expansion)
$ secretlint "**/*"
$ secretlint "source/**/*.ini"

# Treat inputs as literal paths (for SvelteKit (group) / Next.js [param] etc.)
$ secretlint --no-glob "src/(auth)/login.ts"

# Lint STDIN content (filename hint affects which rules apply)
$ echo "SECRET" | secretlint --stdinFileName=secret.txt

# Use a custom config file
$ secretlint "**/*" --secretlintrc=.secretlintrc.custom.json

# Scan files ignored by .gitignore (e.g. to verify build artifacts)
$ secretlint --no-gitignore "dist/**/*"

# Mask secrets in a file in-place
$ secretlint .zsh_history --format=mask-result --output=.zsh_history

# Output JSON for programmatic parsing
$ secretlint "**/*" --format=json --output=secretlint-report.json

# Output GitHub Actions annotations in CI
$ secretlint "**/*" --format=github

Exit Status
Secretlint exits with the following values:

    - 0:
      - Linting succeeded, no errors found.
      - Found lint error but --output is specified.
    - 1:
      - Linting failed, errors found.
    - 2:
      - Unexpected error occurred, fatal error.
Configuration
Secretlint has a configuration file .secretlintrc.{json,yml,js}.
- Document: Configuring Secretlint
After running secretlint --init, you'll have a .secretlintrc.json file in your directory.
In it, you'll see some rules configured like this:
{
  "rules": [
    {
      "id": "@secretlint/secretlint-rule-preset-recommend"
    }
  ]
}
The id property is the name of secretlint rule package.
Secretlint does not have built-in rule.
You want to add some rule and You should install the package and add the rule to .secretlintrc file.
Each rule has same configuration pattern: