
sbomlyze v0.3.6
git diff for your SBOM ,compare CycloneDX/SPDX/Syft bills of materials, detect tampering, and gate CI
sbomlyze
git diff for your SBOM. Compare two Software Bills of Materials and see what changed between builds, versions, and releases.
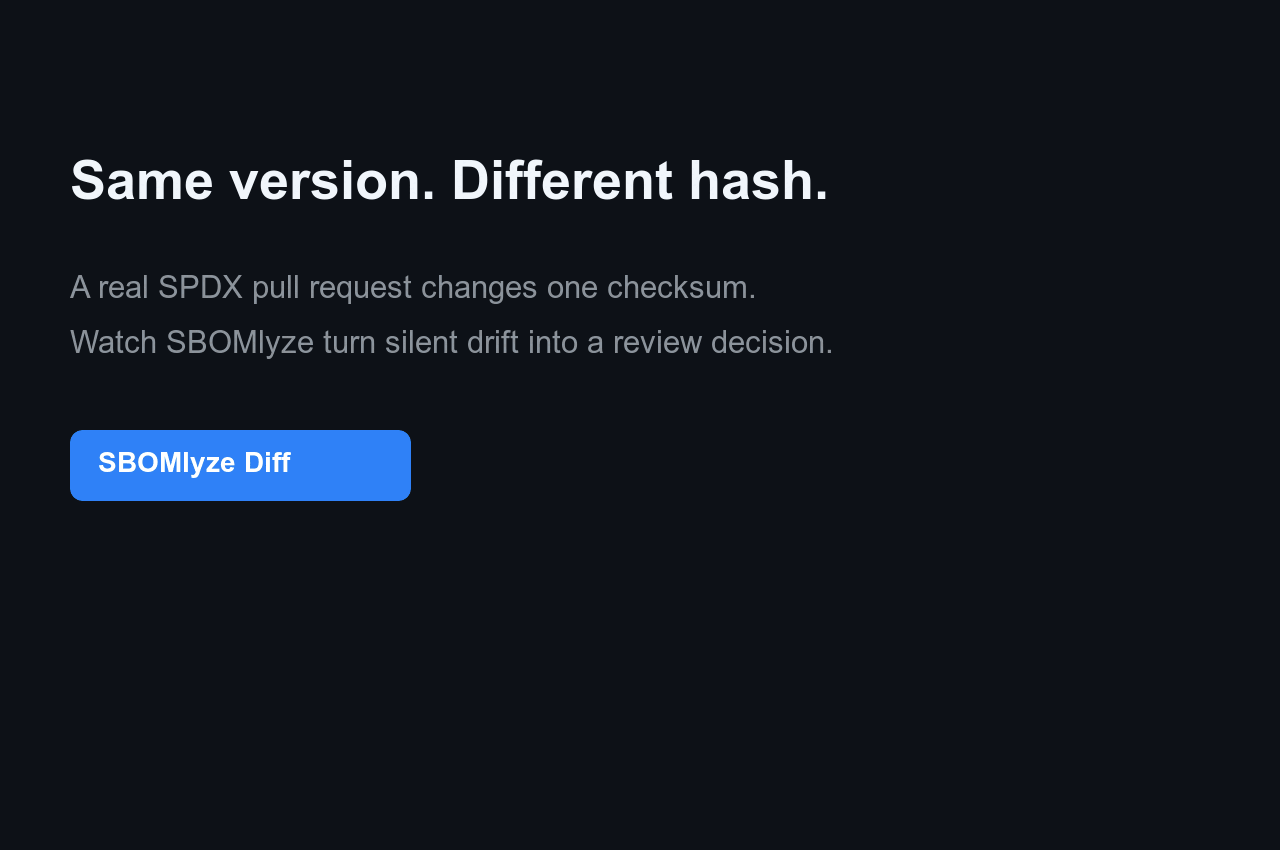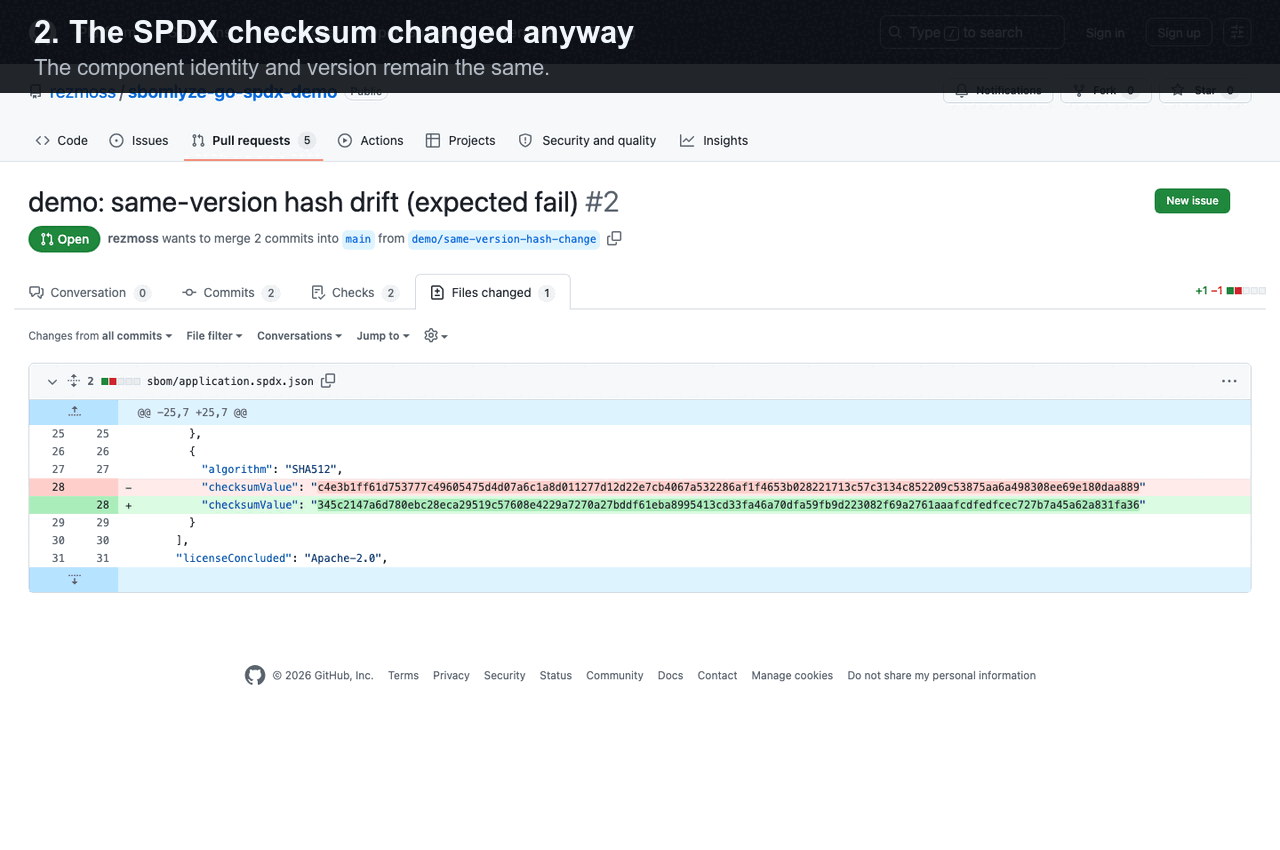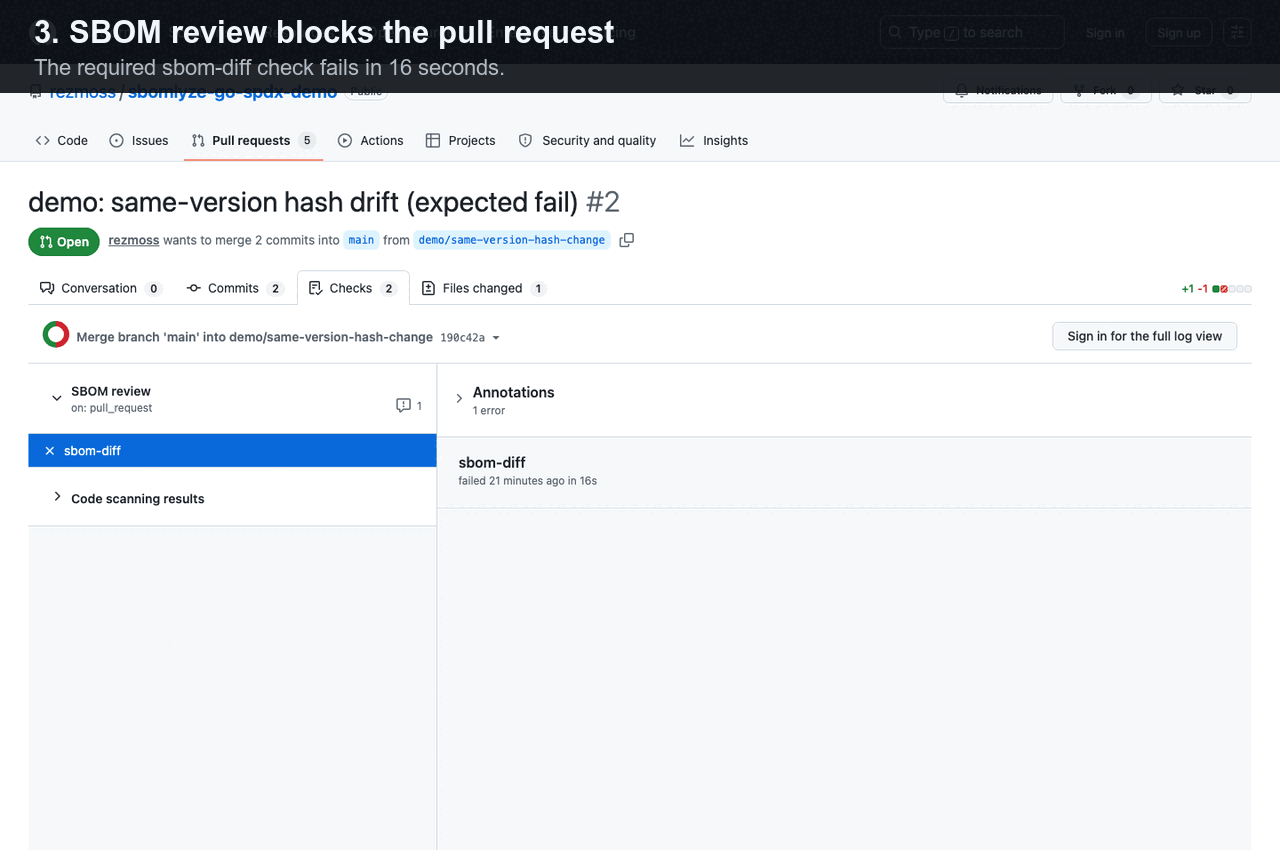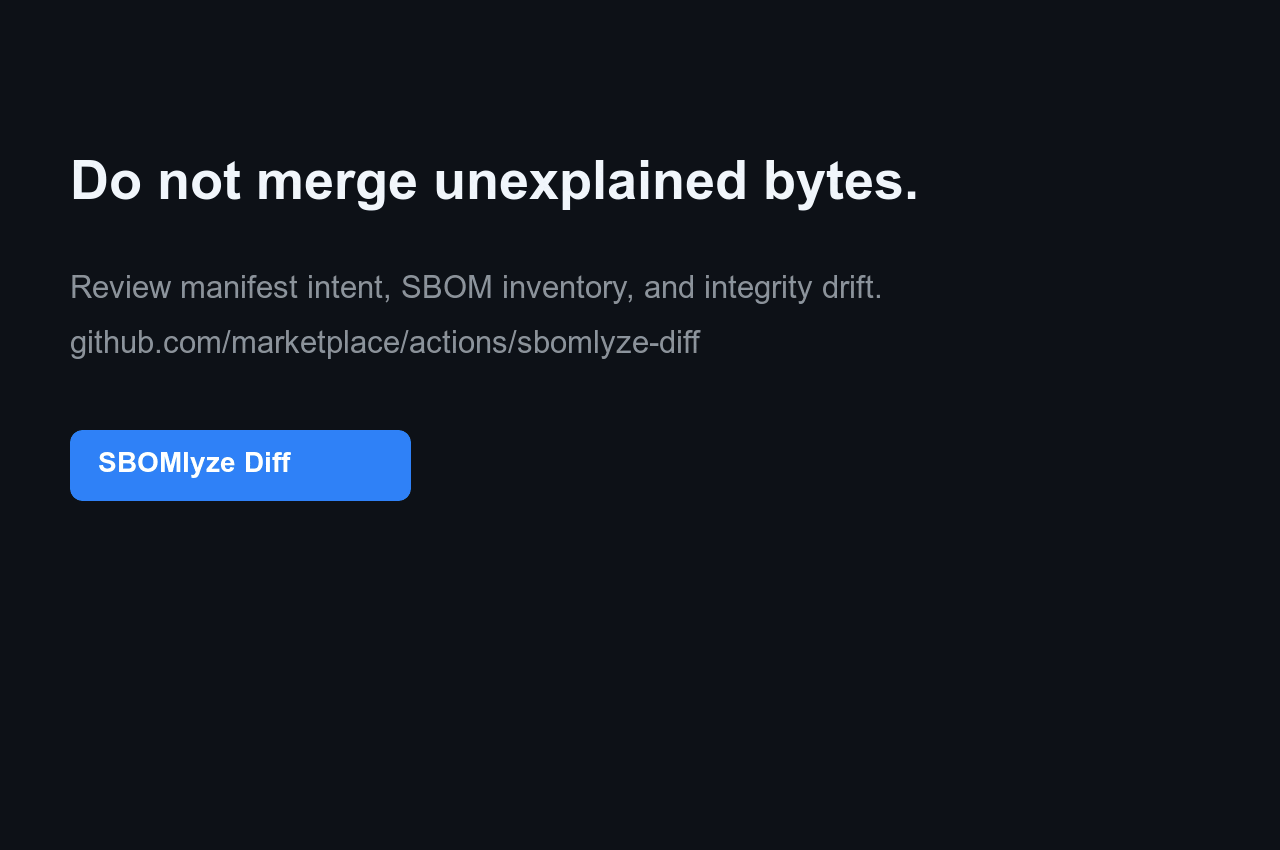
sbomlyze compares component hashes, not only version strings. When an attacker swaps a package without bumping its version, sbomlyze flags it. Generators and vulnerability scanners miss this.
[![CI][ci-img]][ci] [![GitHub Marketplace][marketplace-img]][marketplace] [![GitHub Release][release-img]][release] [![Go Report Card][go-report-img]][go-report] [![OpenSSF Scorecard][scorecard-img]][scorecard] [![License: Apache-2.0][license-img]][license] [![Downloads][download-img]][download]
See why this signal is different from a manifest or ordinary component diff in Manifest diff vs. SBOM diff vs. integrity drift.
Generators make SBOMs and scanners find CVEs. sbomlyze tells you what changed between two SBOMs and whether to trust it. Run it after your generator:
syft image:tag -o cyclonedx-json | sbomlyze - --complianceanalyzes and scores the generated SBOM without a temporary file. Compare it with a baseline to classify drift and gate your pipeline.
GitHub Action quickstart
Add [SBOMlyze Diff from GitHub Marketplace][marketplace] to compare a checked-in
or separately generated SBOM with its git baseline. The immutable SHA below is
the published v0.5.1 Action:
steps:
  - uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    with:
      fetch-depth: 0

  - uses: rezmoss/sbomlyze@31503690611fda8ebba4ed2bd186eda000442594 # v0.5.1
    with:
      sbom-path: build/sbom.cdx.json
The Action writes a Job Summary by default and can enforce policy, report integrity drift, upload SARIF, or maintain a single pull-request comment. See the complete Action reference for inputs, outputs, permissions, and security guidance. See the live demonstration repository for a passing dependency update and a blocked same-version hash change, with public workflow runs and SARIF evidence.
For format-specific dogfood, use the public Go + SPDX, Node + CycloneDX, or container example. Each contains five reproducible review scenarios. The 10-minute beta guide collects four focused activation and signal quality questions.
Generated SBOMs do not need to be committed: baseline: workflow-artifact
retrieves the most recent matching artifact from a successful default-branch
run. A pinned Syft companion workflow
shows generation and baseline publication while SBOMlyze remains responsible
for review and policy.
Why sbomlyze?
Many tools generate SBOMs. Few compare them, and fewer tell you whether a change is routine or a supply-chain red flag. sbomlyze fills that gap.
| Capability | sbomlyze | cyclonedx-cli | sbomqs | syft / trivy |
|---|---|---|---|---|
| SBOM-to-SBOM diff | ✅ | basic | ❌ | ❌ |
| Integrity / tamper drift (hash changed without version) | ✅ | ❌ | ❌ | ❌ |
| Dependency-graph diff + transitive depth risk | ✅ | ❌ | ❌ | ❌ |
| NTIA / CISA / BSI compliance scoring | ✅ | ❌ | ✅ | ❌ |
| Format conversion (Syft / CycloneDX / SPDX) | ✅ | ✅ | ❌ | partial |
| TUI + Web UI explorers | ✅ | ❌ | ❌ | ❌ |
| Policy gate + SARIF / JUnit / Markdown / HTML / Patch | ✅ | partial | partial | partial |
Features
- SBOM diffing: Compare two SBOMs and see added, removed, and changed components at a glance
- Drift classification: Distinguish version drift from integrity drift (a hash changed without a version change, signaling tampering) and metadata drift
- Compliance scoring: Score any SBOM against NTIA, CISA 2025, and BSI TR-03183 minimum elements
- Dependency graph diff: Track transitive dependencies and supply-chain depth
- Multi-format support: Syft, CycloneDX, SPDX (JSON)
- Format conversion: Convert between CycloneDX, SPDX, and Syft formats
- Strong identity matching: PURL → CPE → BOM-ref → namespace/name precedence
- Statistics mode: Analyze single SBOMs for license, dependency, and integrity metrics
- Interactive TUI mode: Explore SBOMs with keyboard navigation and search
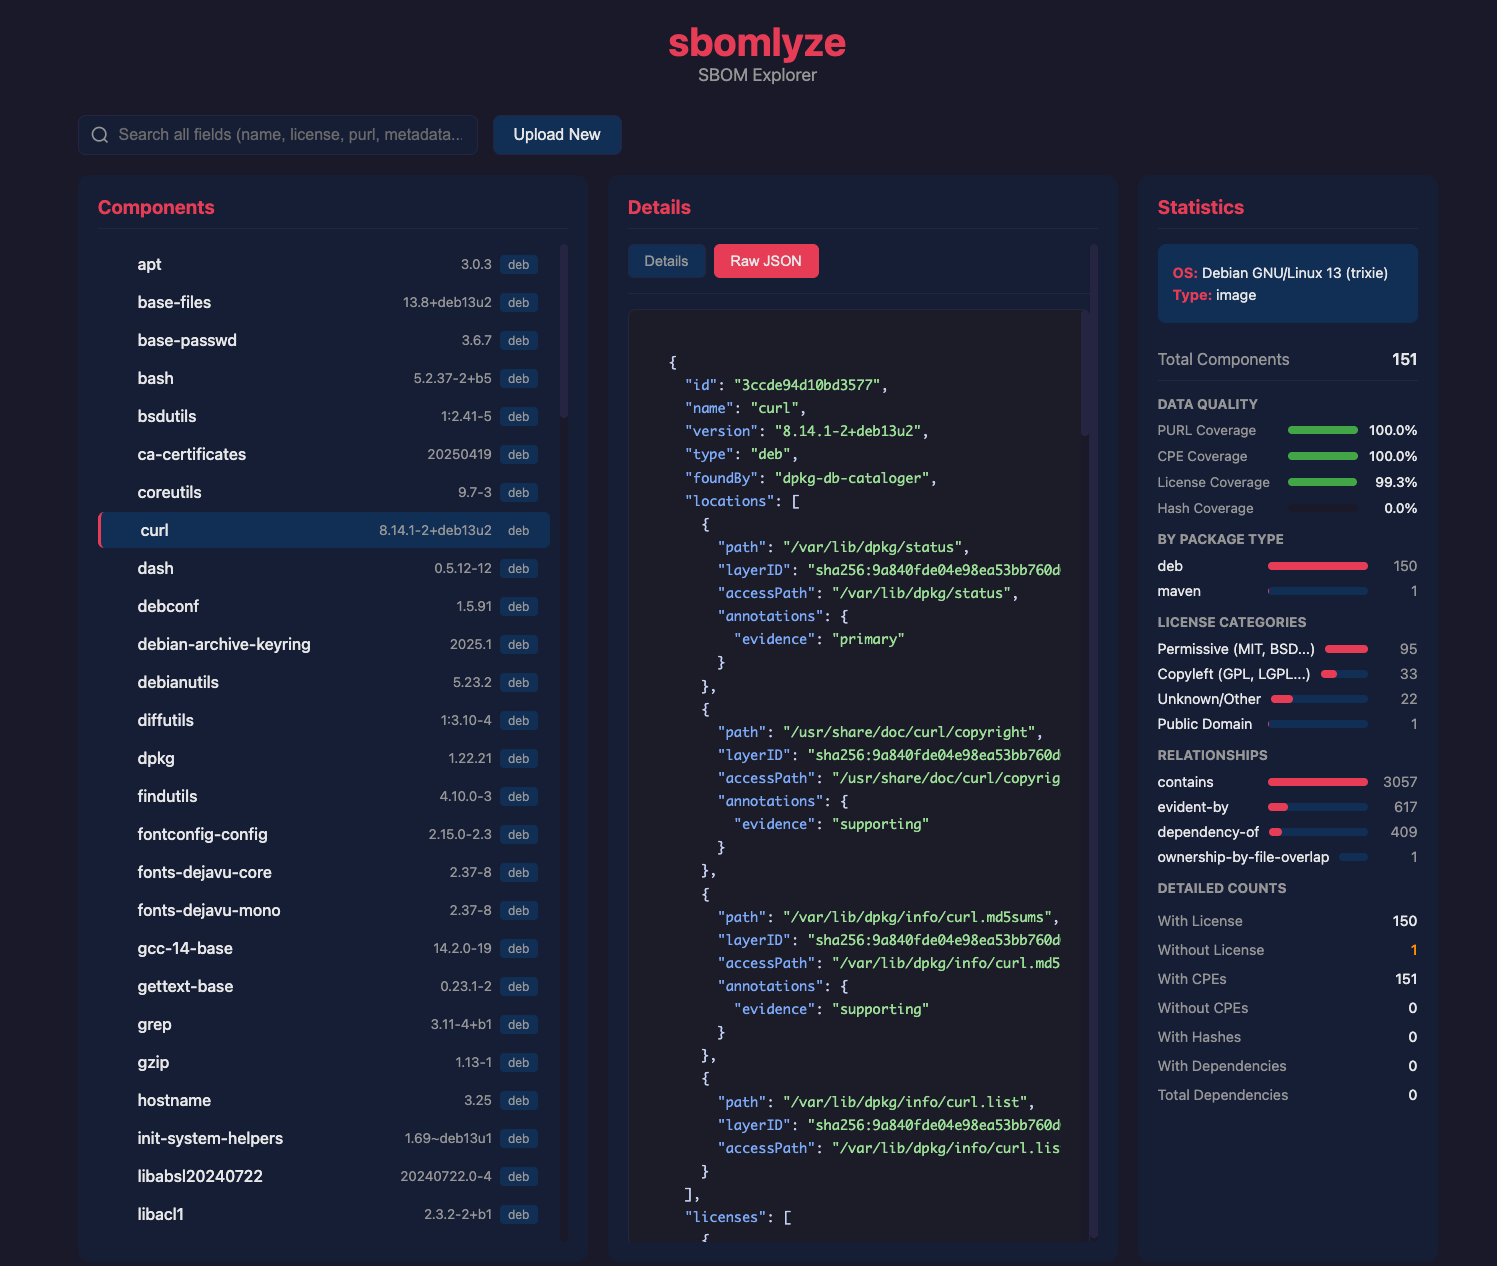
- Web UI mode: Browser-based SBOM explorer with drag-and-drop upload
- Policy engine: Enforce drift, license, and compliance-score rules in CI pipelines
- GitHub Marketplace Action: Gate pull requests on SBOM drift with Job Summary, SARIF, and optional comment output
- Duplicate & collision detection: Find multiple versions of the same package and ambiguous identity matches
- Multiple output formats: Text, JSON, SARIF, JUnit XML, Markdown, HTML, JSON Patch
- Tolerant parsing: Continue on errors with structured warnings
Installation
Homebrew (macOS/Linux)
brew install rezmoss/sbomlyze/sbomlyze
Installer Script
The installer script downloads the correct binary for your OS/architecture:
# Install to ./bin
curl -sSfL https://raw.githubusercontent.com/rezmoss/sbomlyze/main/install.sh | sh

# Install to /usr/local/bin (requires sudo)
curl -sSfL https://raw.githubusercontent.com/rezmoss/sbomlyze/main/install.sh | sudo sh -s -- -b /usr/local/bin

# Install specific version
curl -sSfL https://raw.githubusercontent.com/rezmoss/sbomlyze/main/install.sh | sh -s -- -v 0.4.0
Installer options:
| Option | Description |
|---|---|
-b <dir> | Installation directory (default: ./bin) |
-d | Enable debug output |
-v <ver> | Install specific version (default: latest) |
The installer always verifies the release checksum. When a compatible GitHub CLI is installed, it also verifies the release's build provenance and fails closed if that verification does not succeed.
Go Install
go install github.com/rezmoss/sbomlyze/cmd/sbomlyze@latest
From Binary Release
Download the latest binary from GitHub Releases.
Starting with v0.3.7, release archives are published with GitHub artifact attestations. Verify a download independently with:
gh attestation verify ./sbomlyze_0.4.0_Linux_x86_64.tar.gz \
  --repo rezmoss/sbomlyze \
  --signer-workflow rezmoss/sbomlyze/.github/workflows/release.yml
Unsigned apt, rpm, and apk repository instructions have been removed until the repositories support package-manager-native signature verification.
macOS users: Remove the quarantine flag after downloading:
xattr -d com.apple.quarantine ./sbomlyze
chmod +x ./sbomlyze
Build from Source
git clone https://github.com/rezmoss/sbomlyze.git
cd sbomlyze
go build -o sbomlyze ./cmd/sbomlyze
Quick Start
# Compare two SBOMs (the headline use case)
sbomlyze before.json after.json

# Analyze a single SBOM
sbomlyze image.json

# Read an SBOM from standard input
syft image:tag -o cyclonedx-json | sbomlyze -

# Use standard input on either side of a diff
syft image:tag -o cyclonedx-json | sbomlyze baseline.json -

# Score an SBOM against NTIA / CISA / BSI minimum elements
sbomlyze image.json --compliance

# Interactive TUI explorer
sbomlyze image.json -i

# Web UI (opens browser)
sbomlyze -web

# Convert between SBOM formats
sbomlyze convert syft.json --to spdx
sbomlyze convert cdx.json --to syft -o output.json