

CyberStrikeAI v1.7.18
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.
CyberStrikeAI
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.
CyberStrikeAI connects planning, execution, human oversight, evidence, and replay in one auditable workspace. Built in Go, it combines Eino-powered agents, MCP-native tools, RAG knowledge, visual workflows, and attack-chain modeling and analysis for authorized security operations.
Start here: Quick start · Documentation · Security hardening
[!IMPORTANT] Use CyberStrikeAI only on systems you own or are explicitly authorized to test. For shared or production environments, review the security model and hardening guide before enabling high-risk tools, WebShell, or C2 capabilities.
Interface & Integration Preview
System Dashboard Overview
Light Mode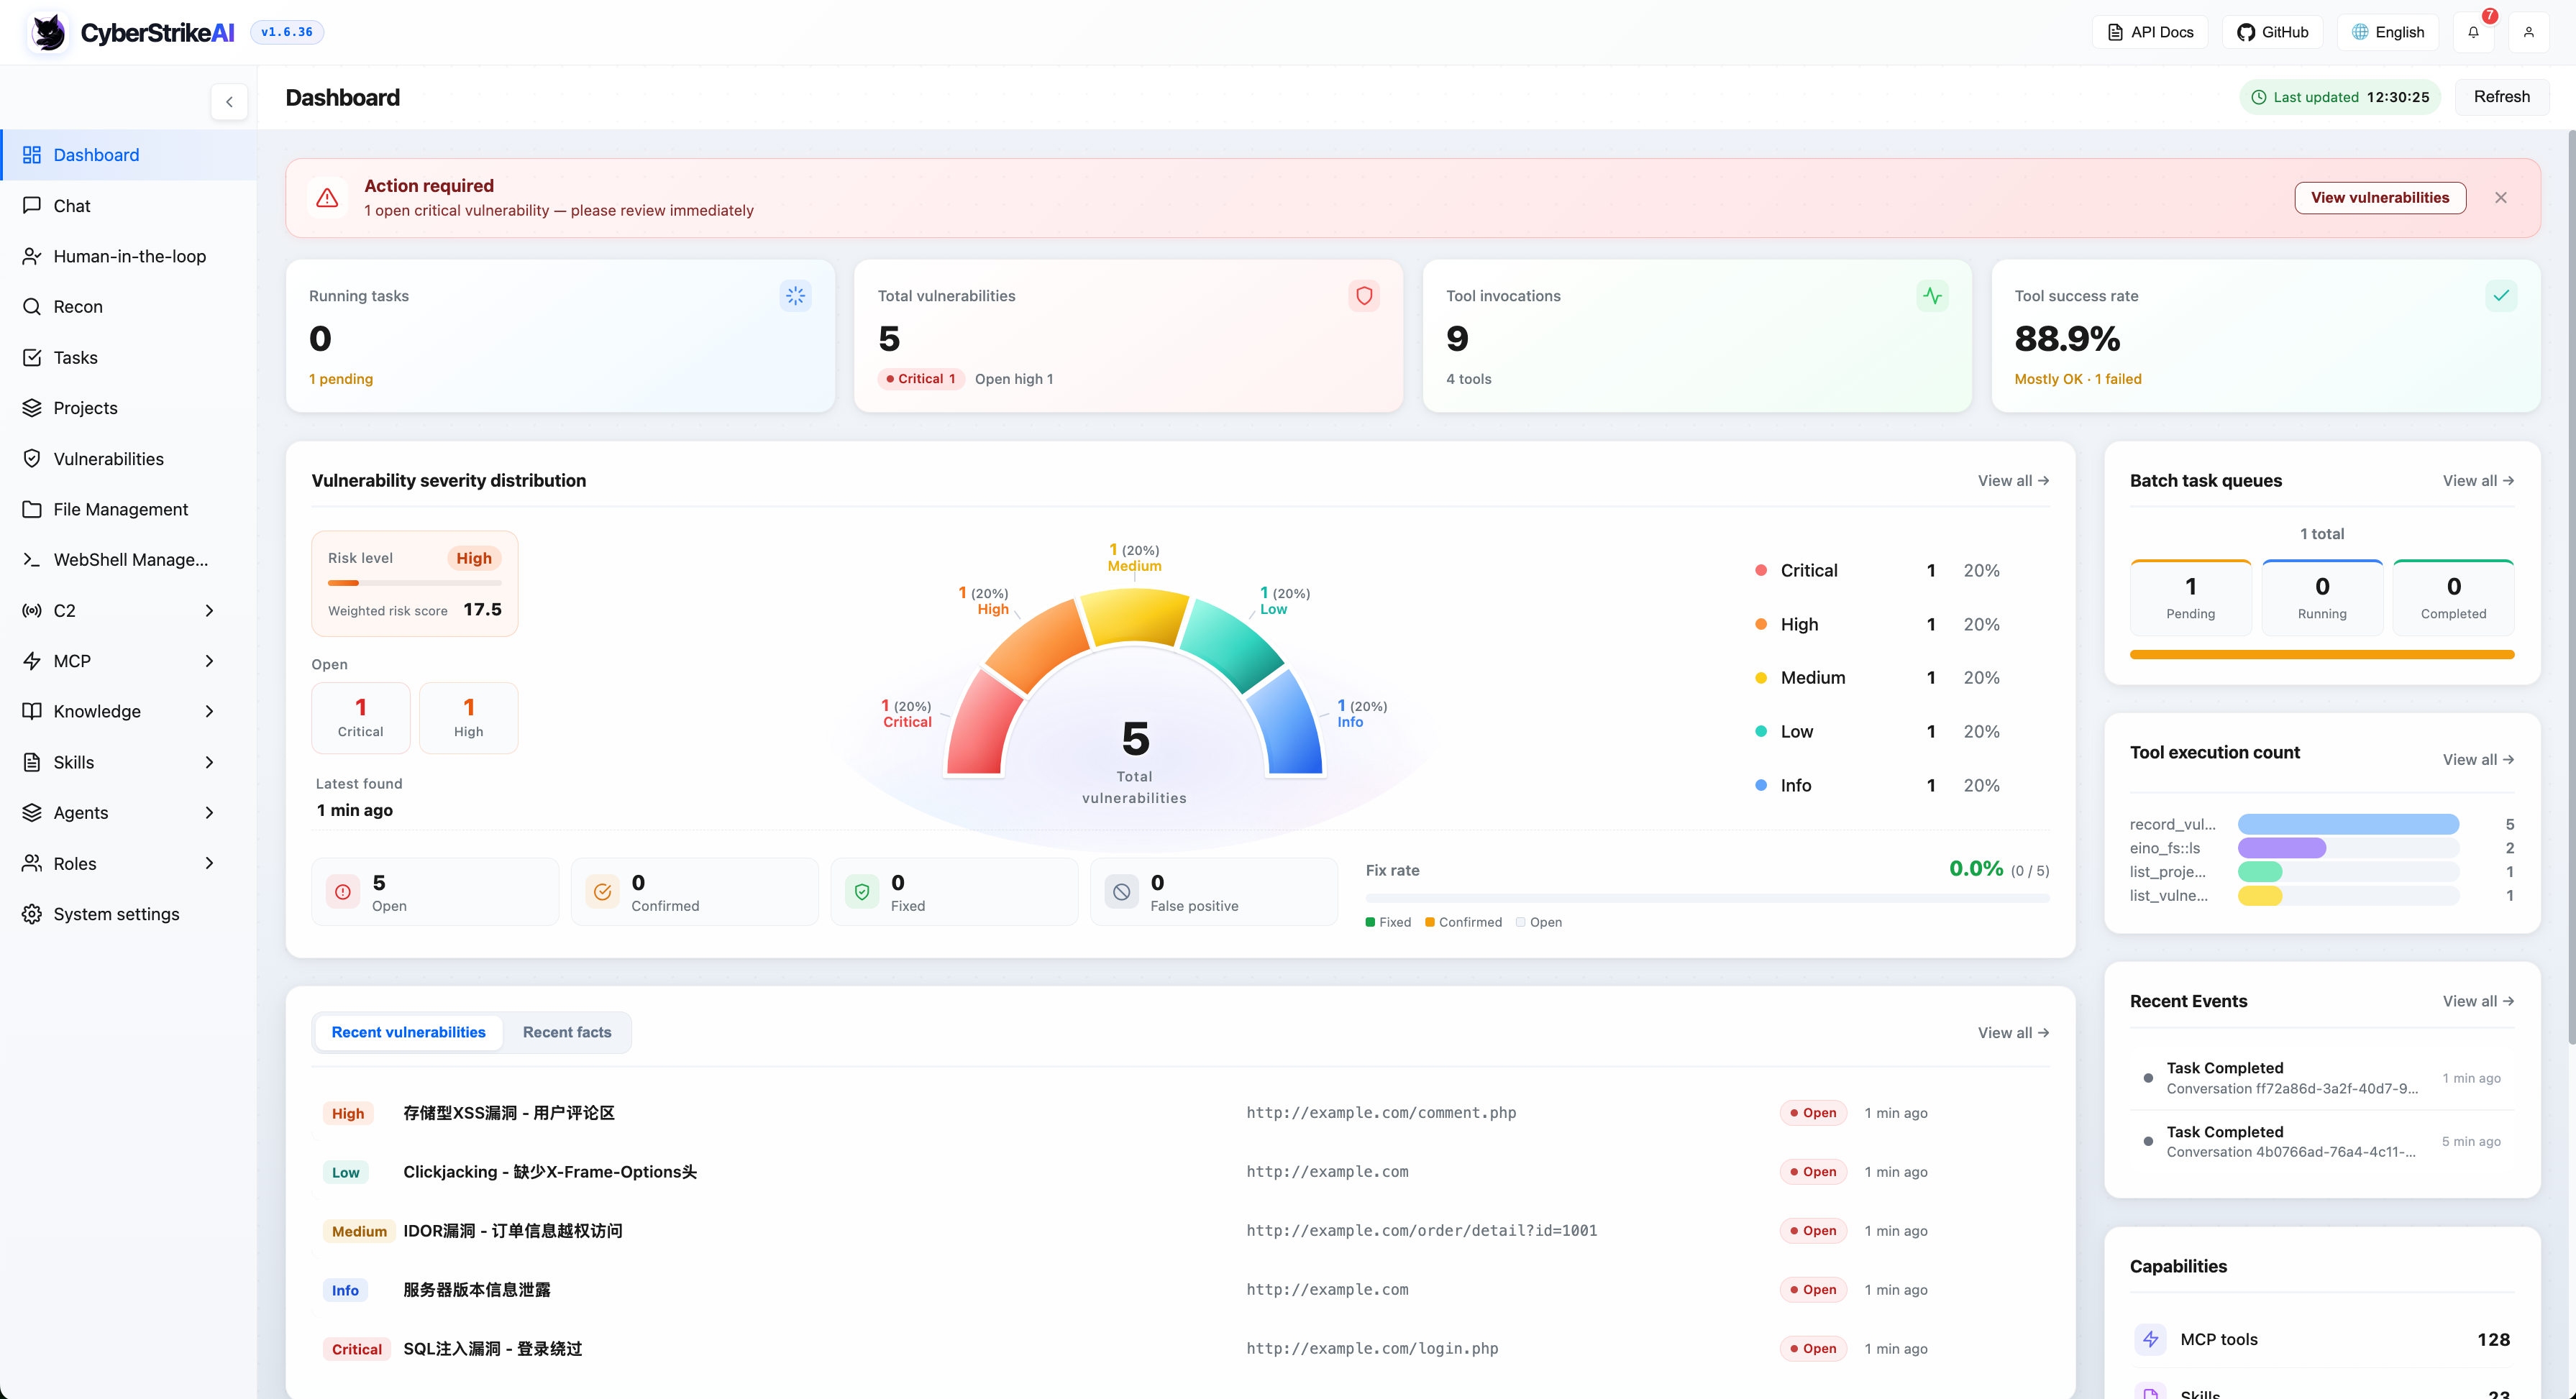
|
Dark Mode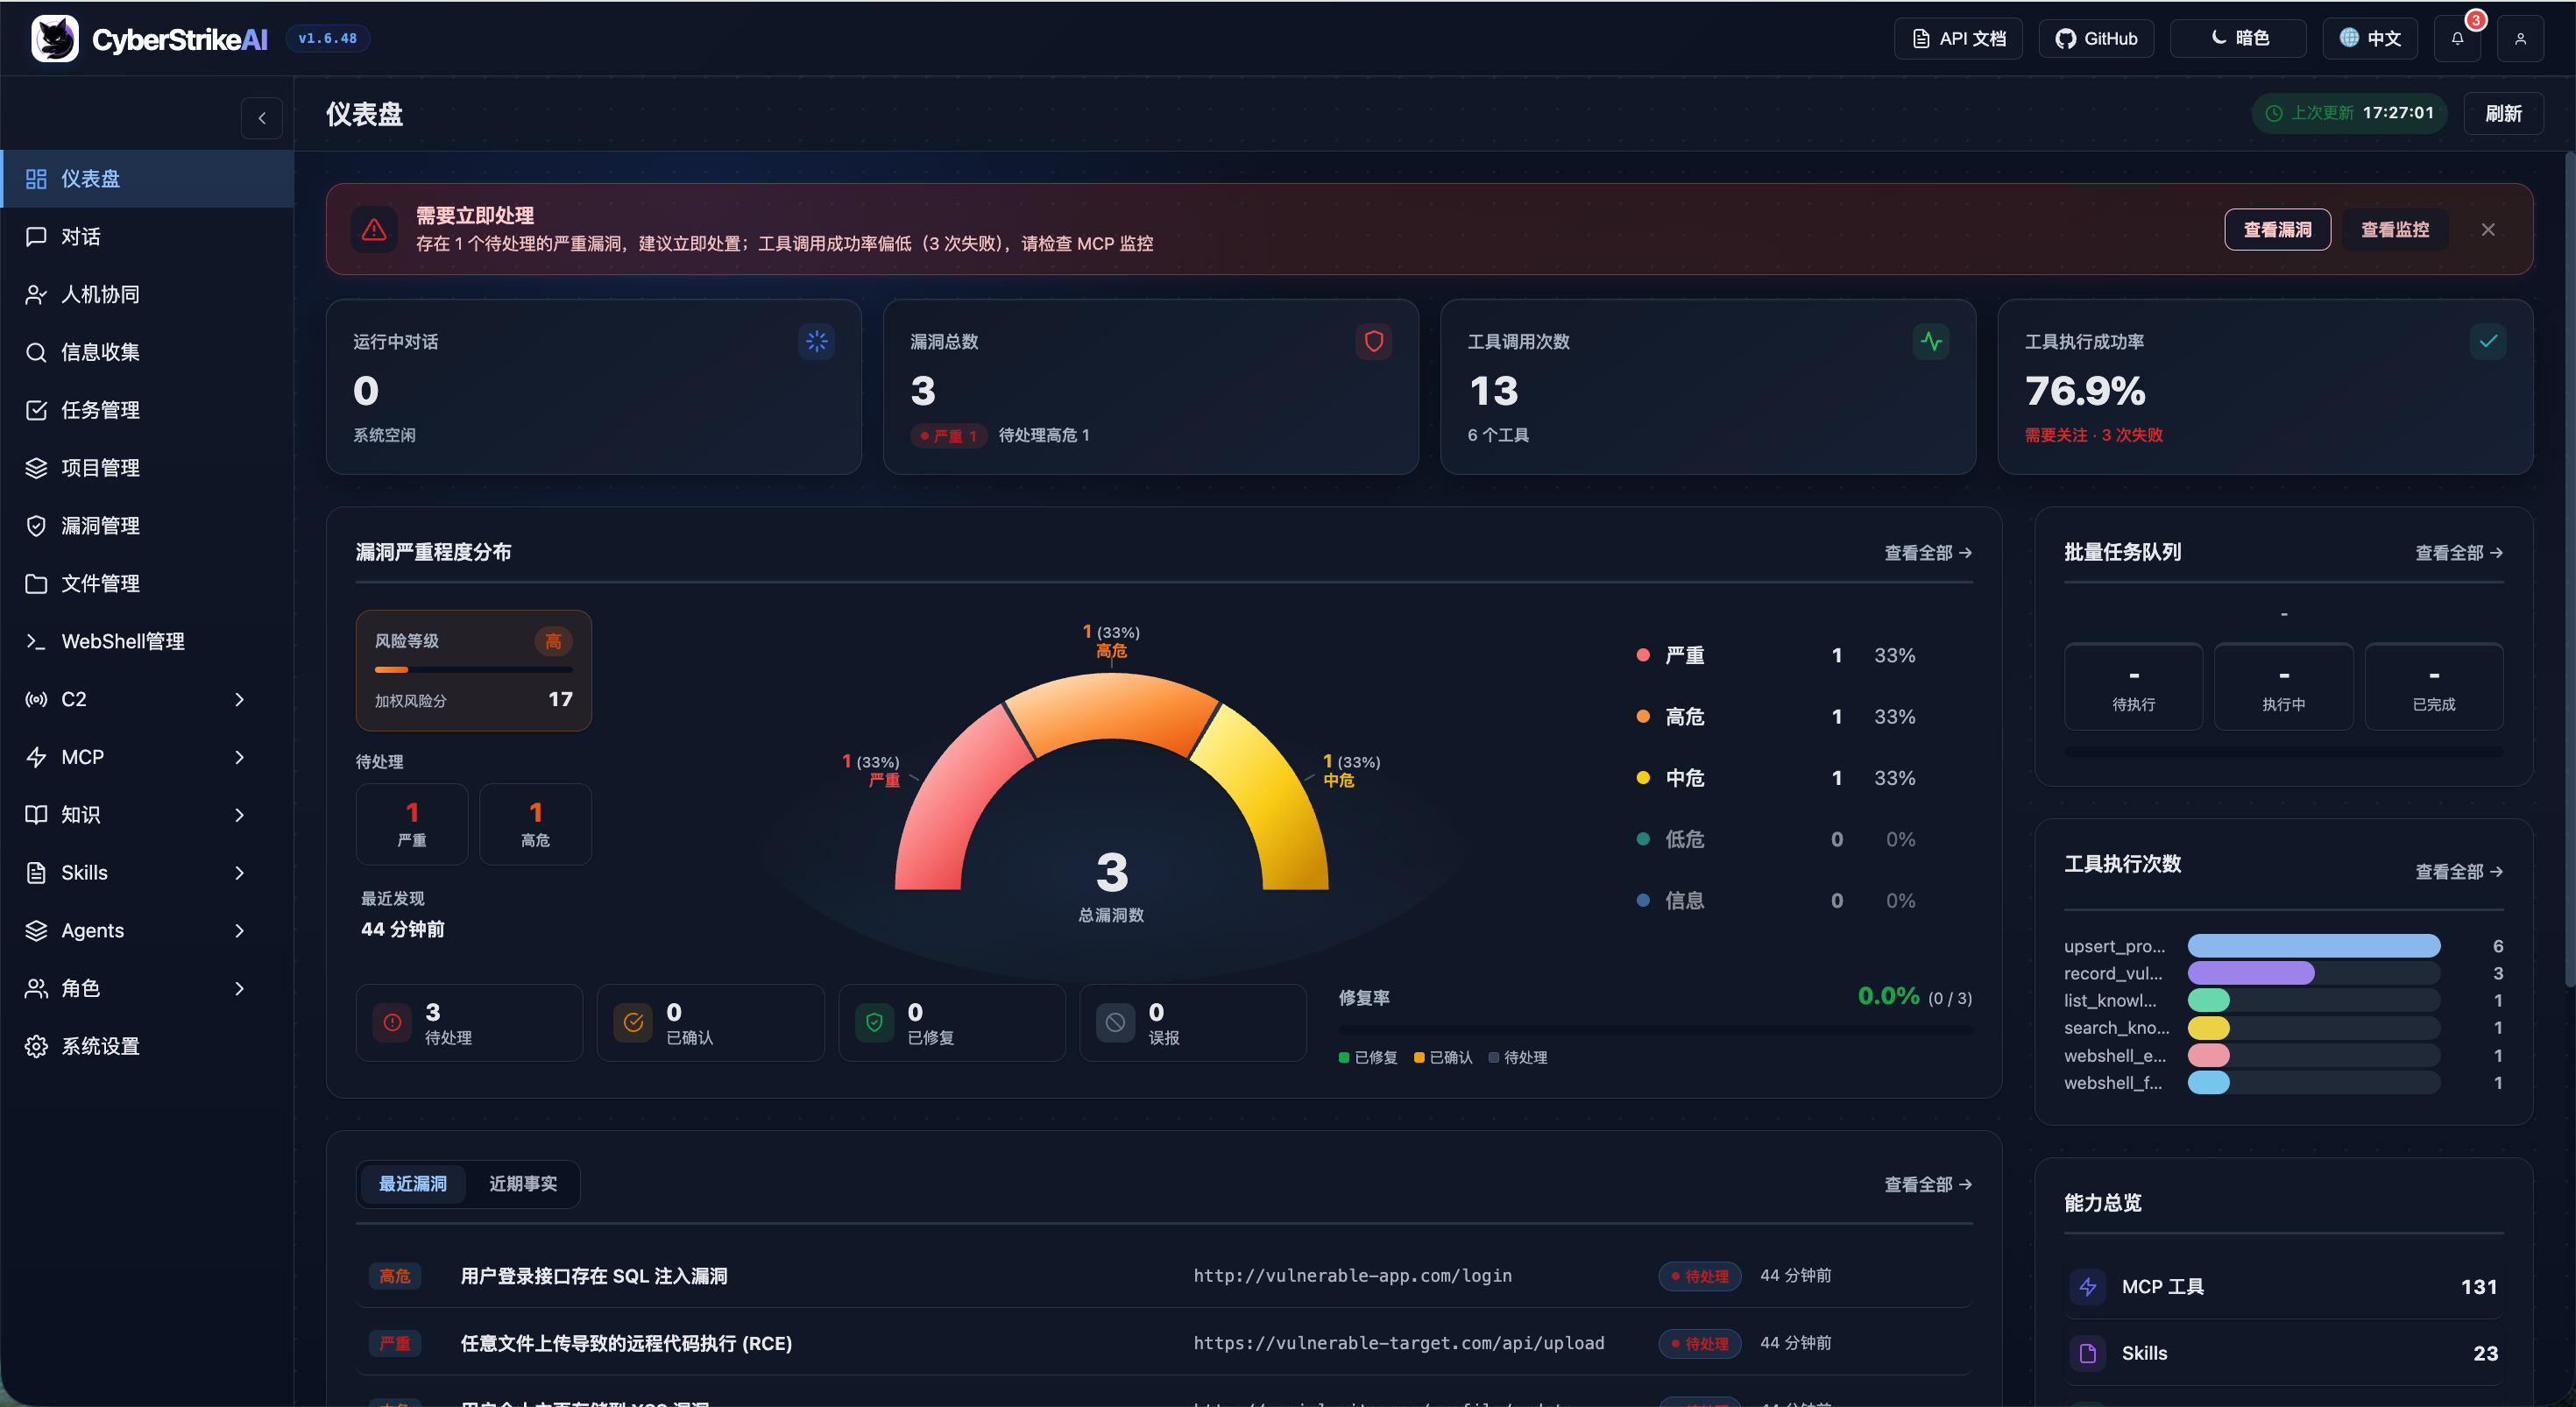
|
The dashboard provides a comprehensive overview of system runtime status, security vulnerabilities, tool usage, and knowledge base, helping users quickly understand the platform's core features and current state.
More interface screenshots
Core Features Overview
Web Console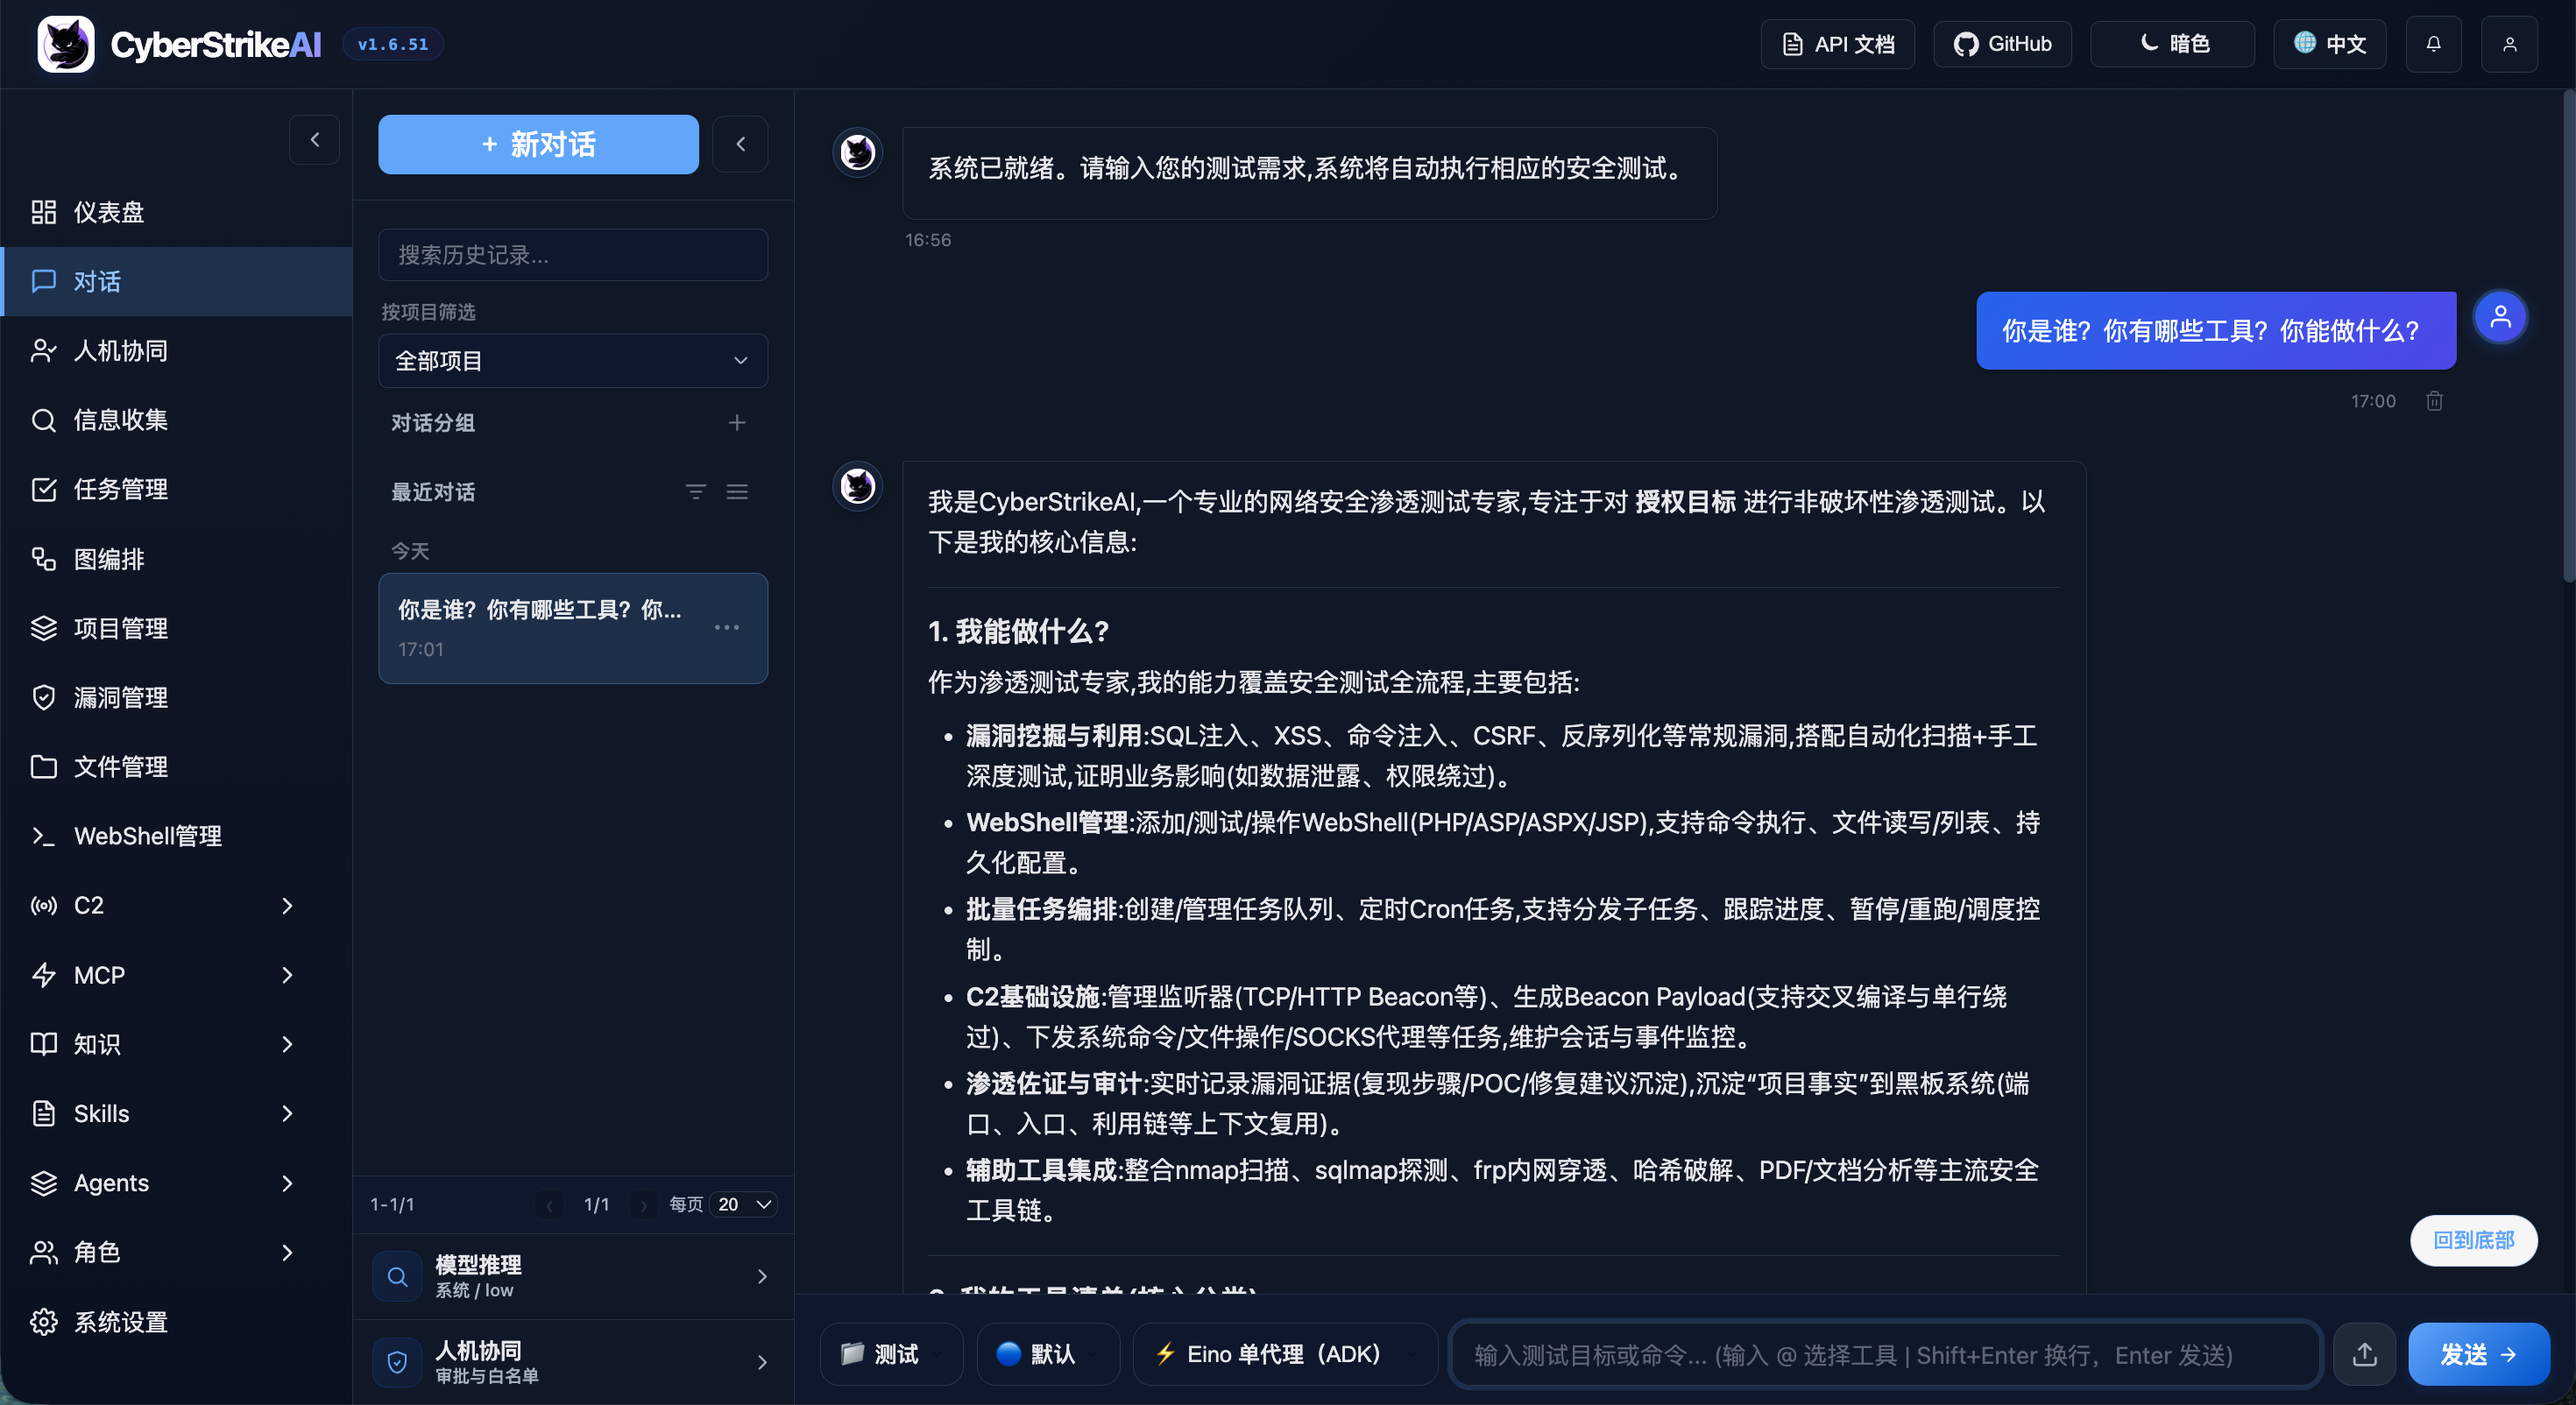
|
Task Management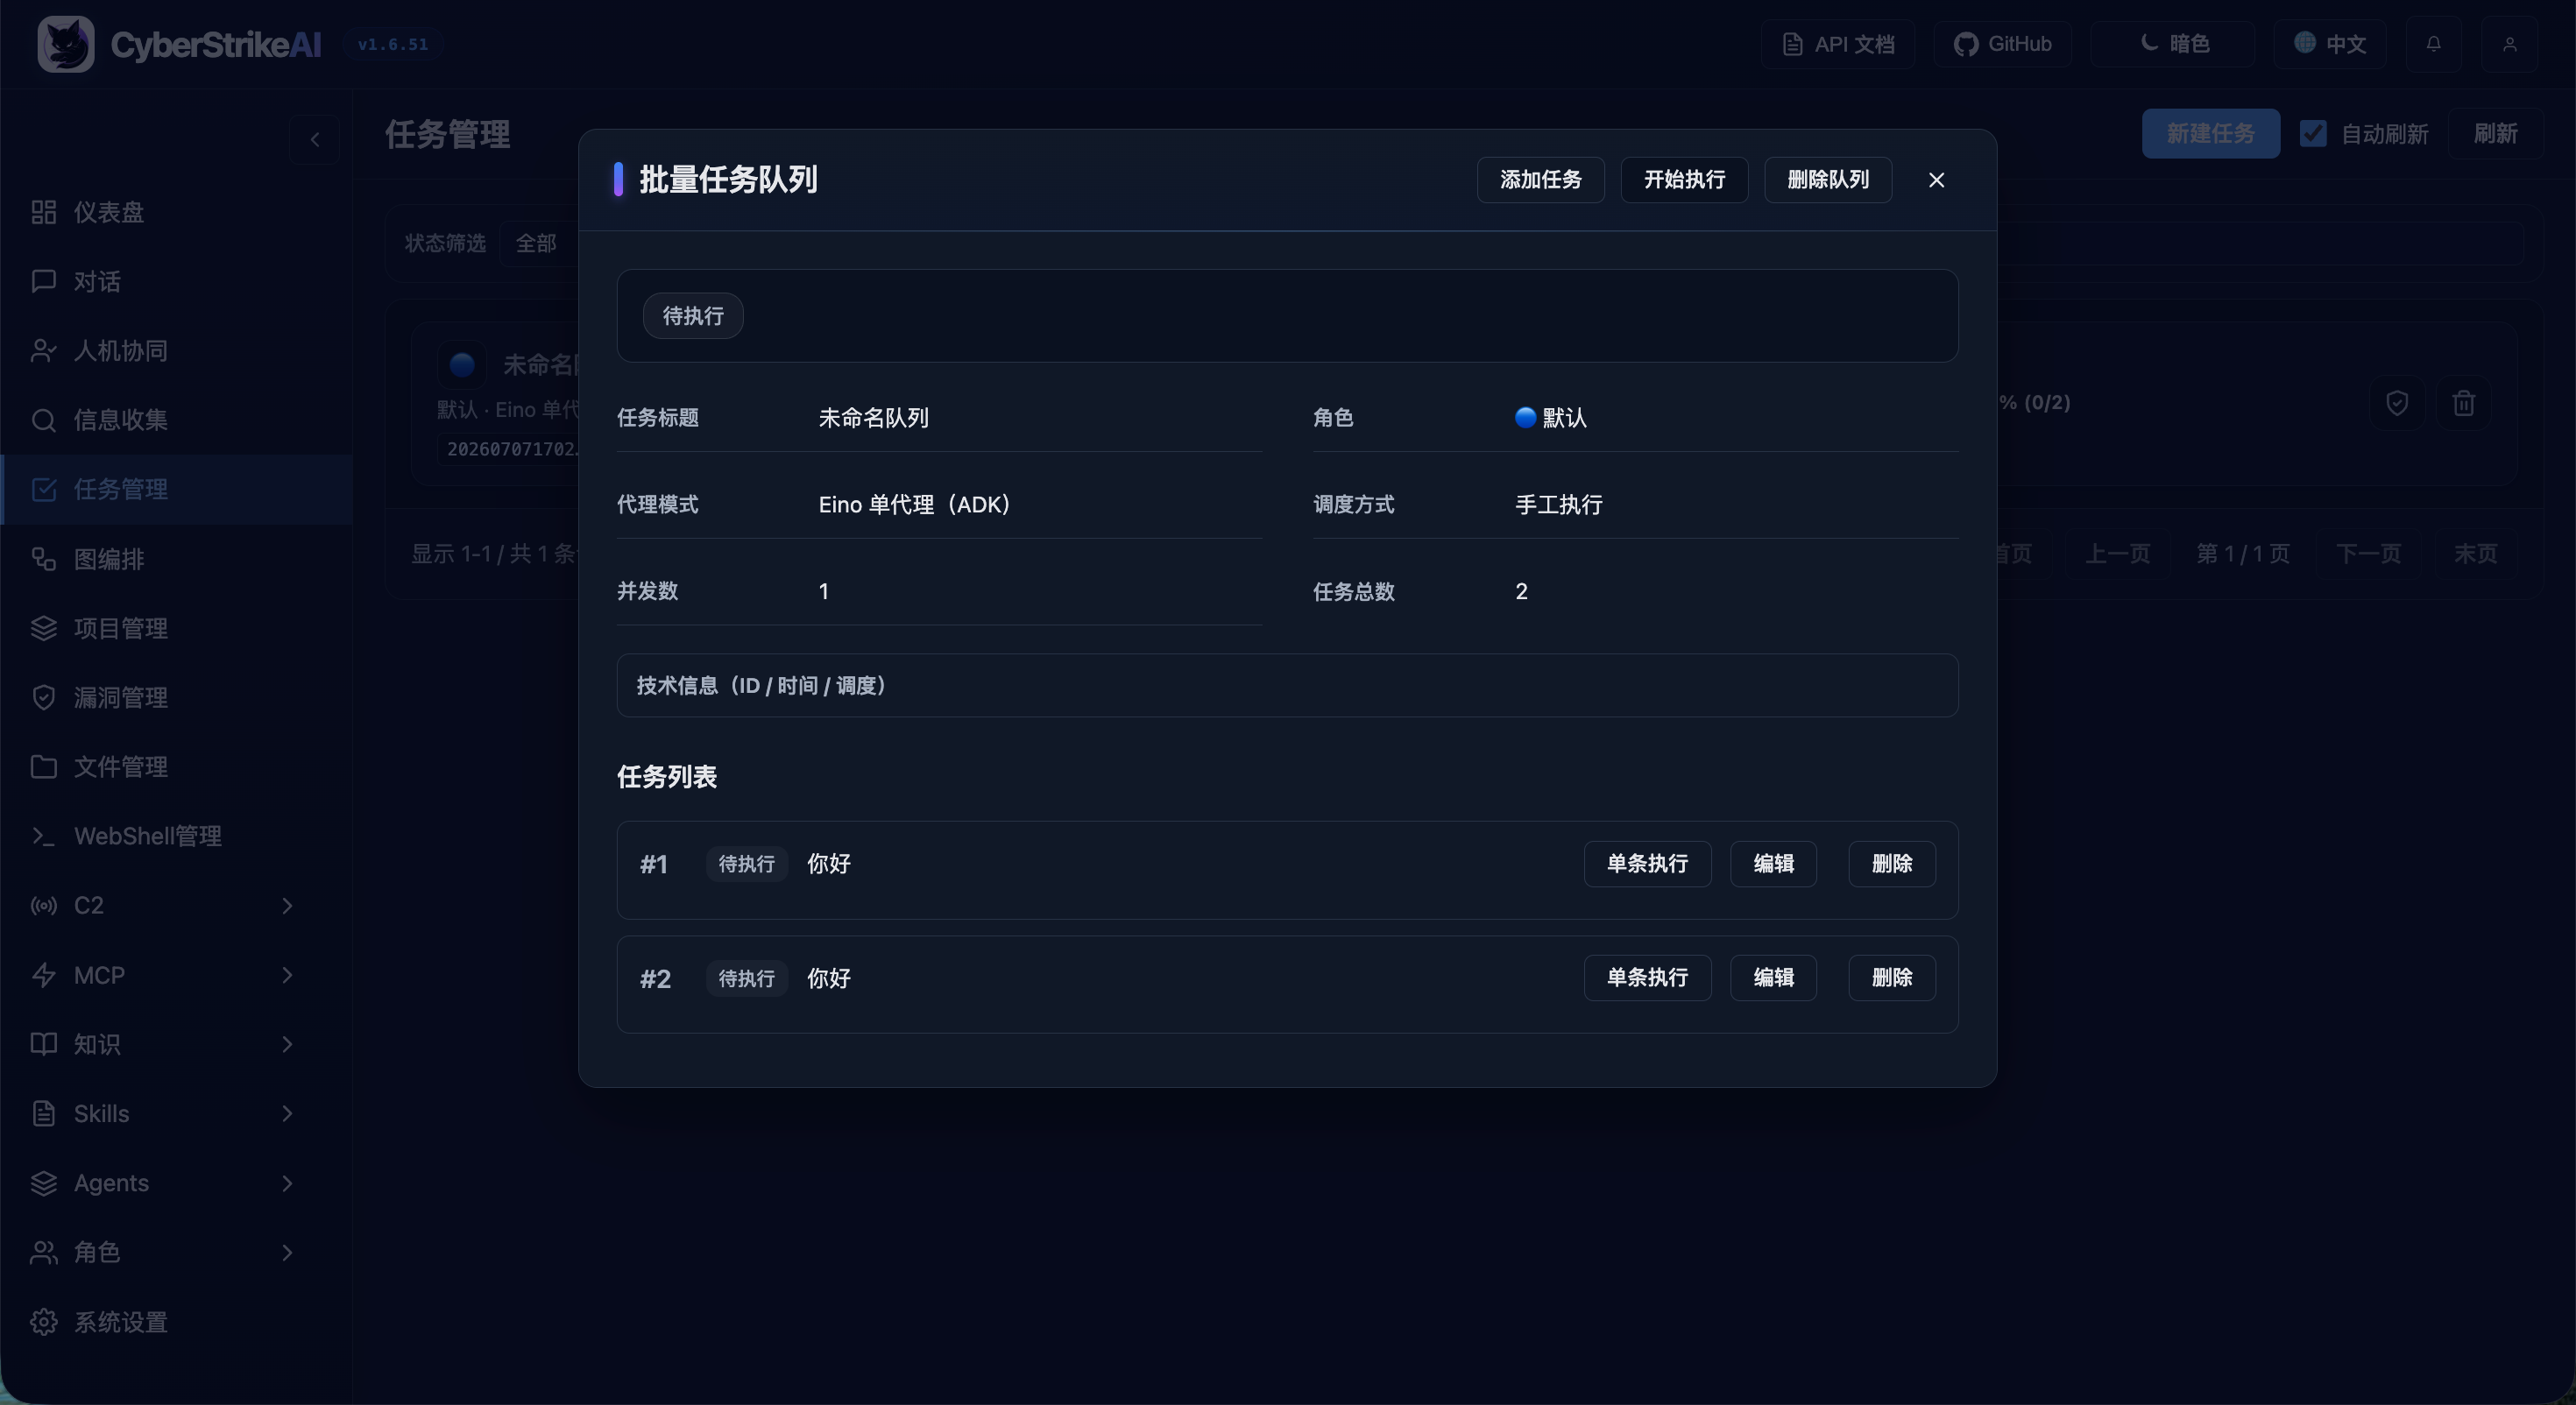
|
Vulnerability Management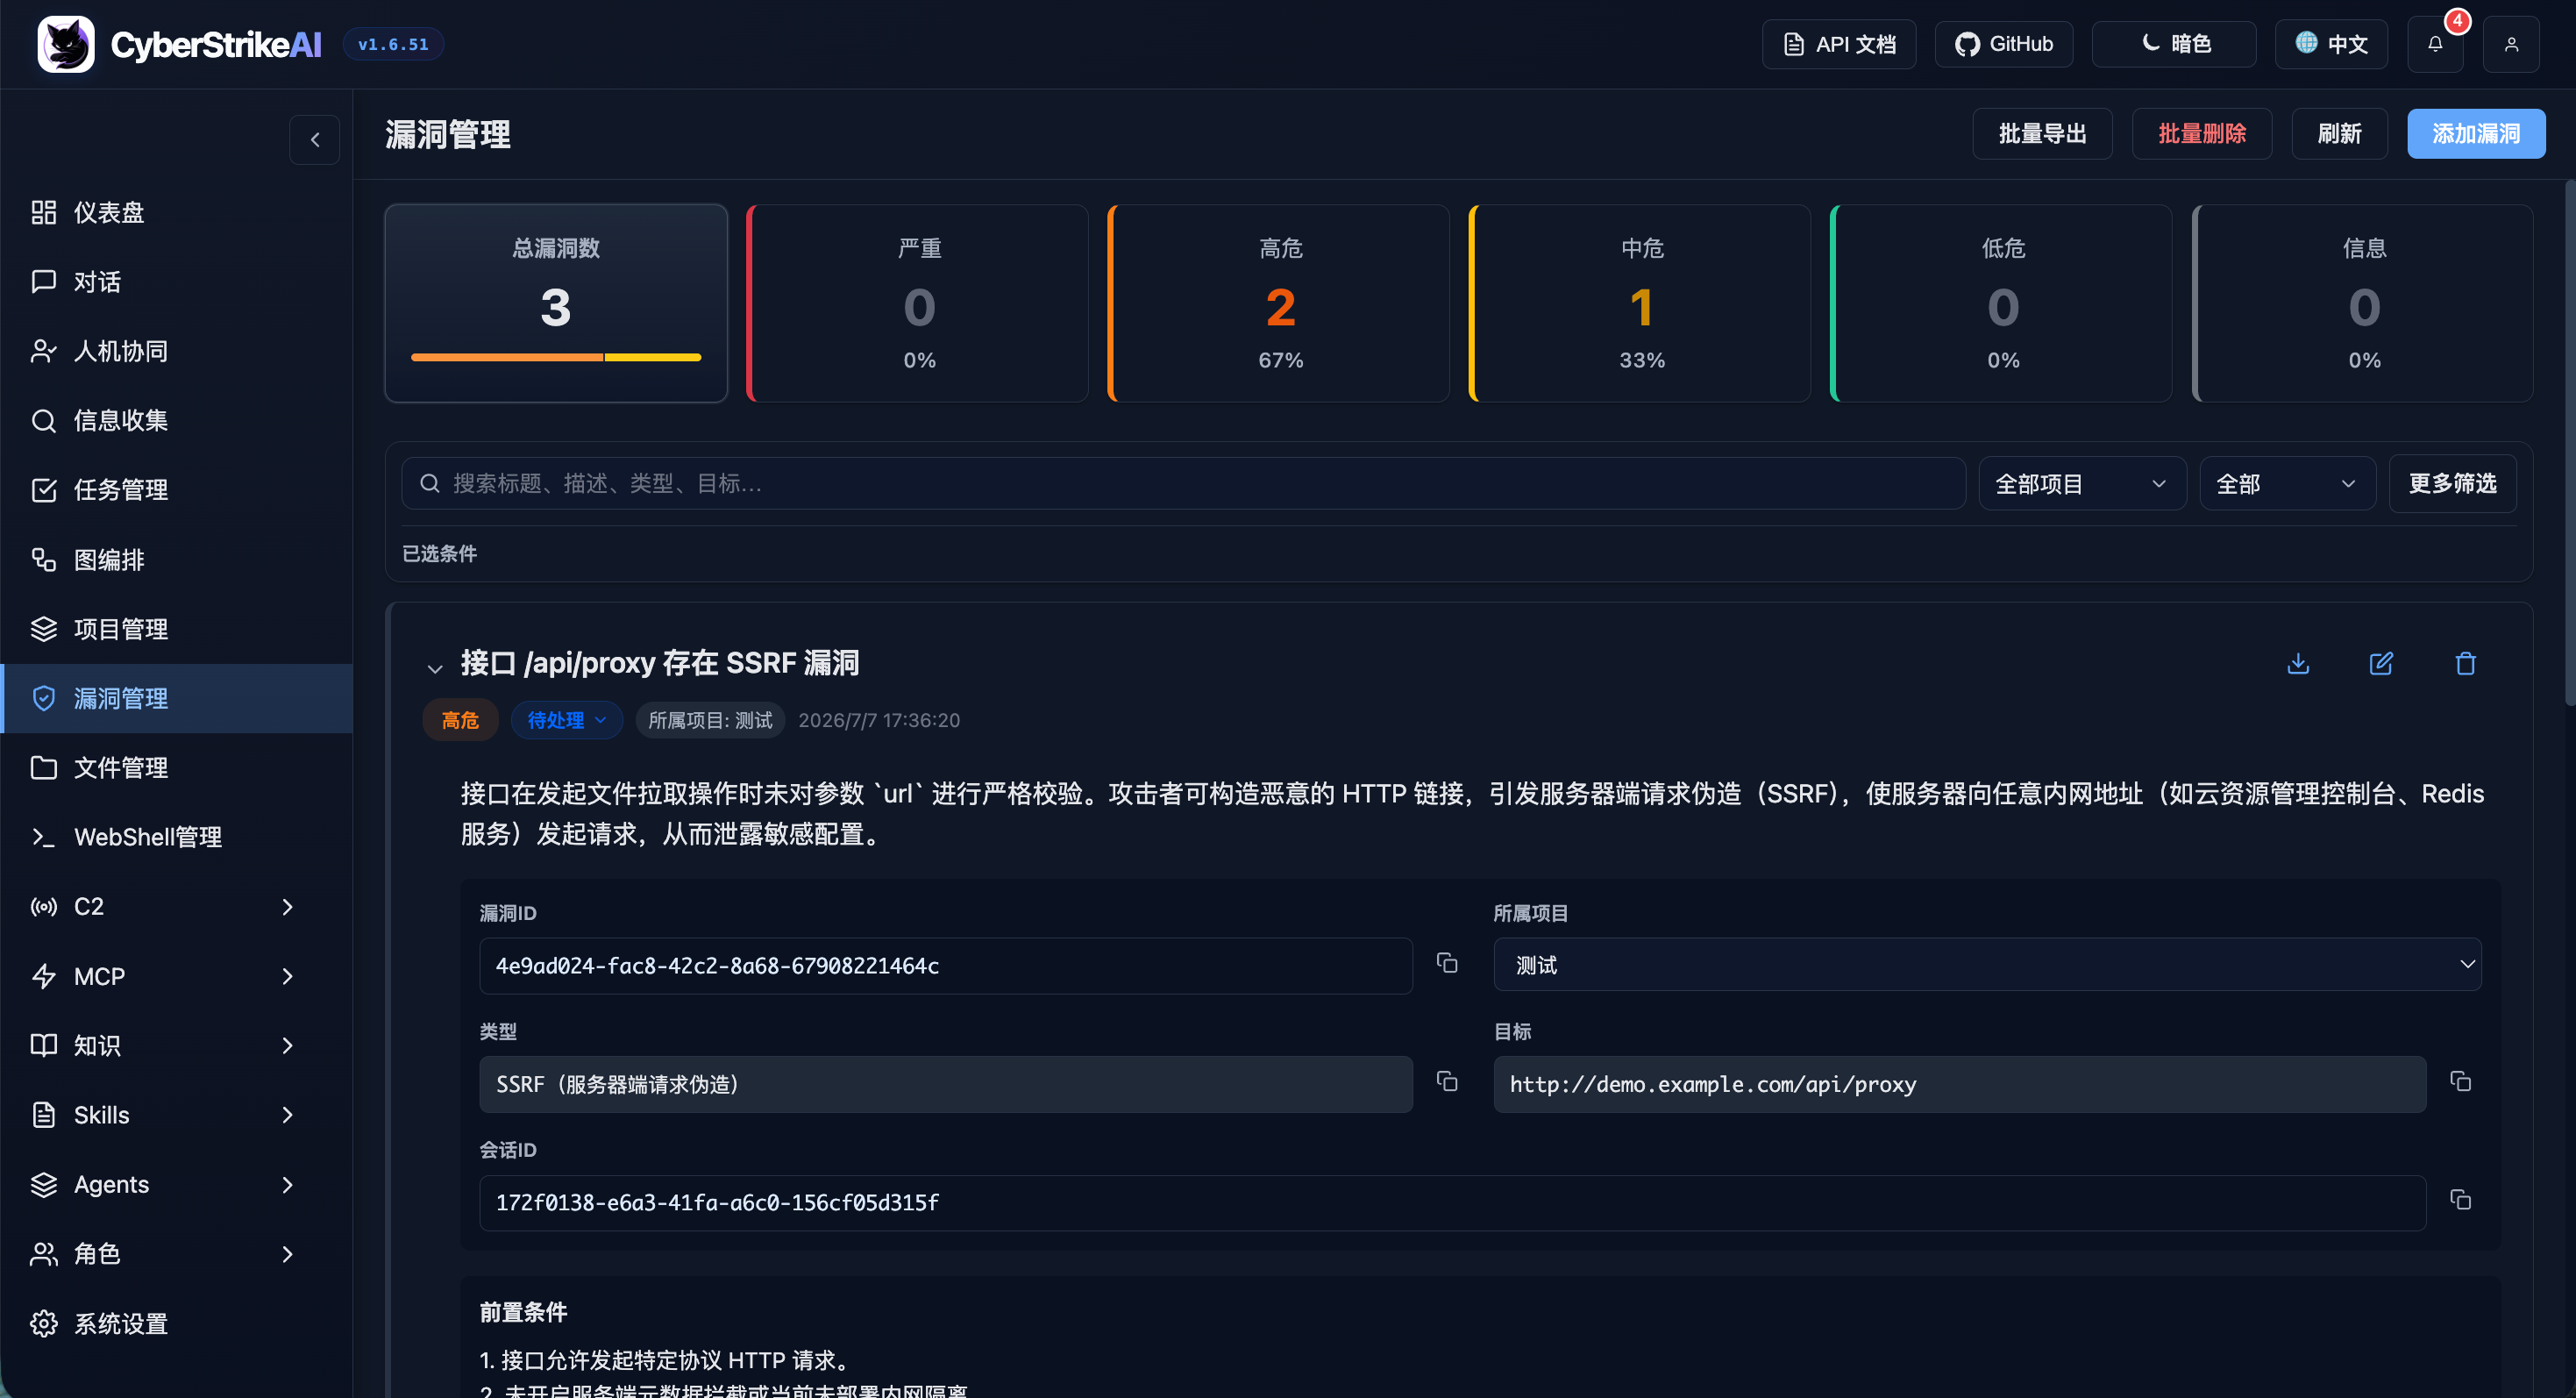
|
WebShell Management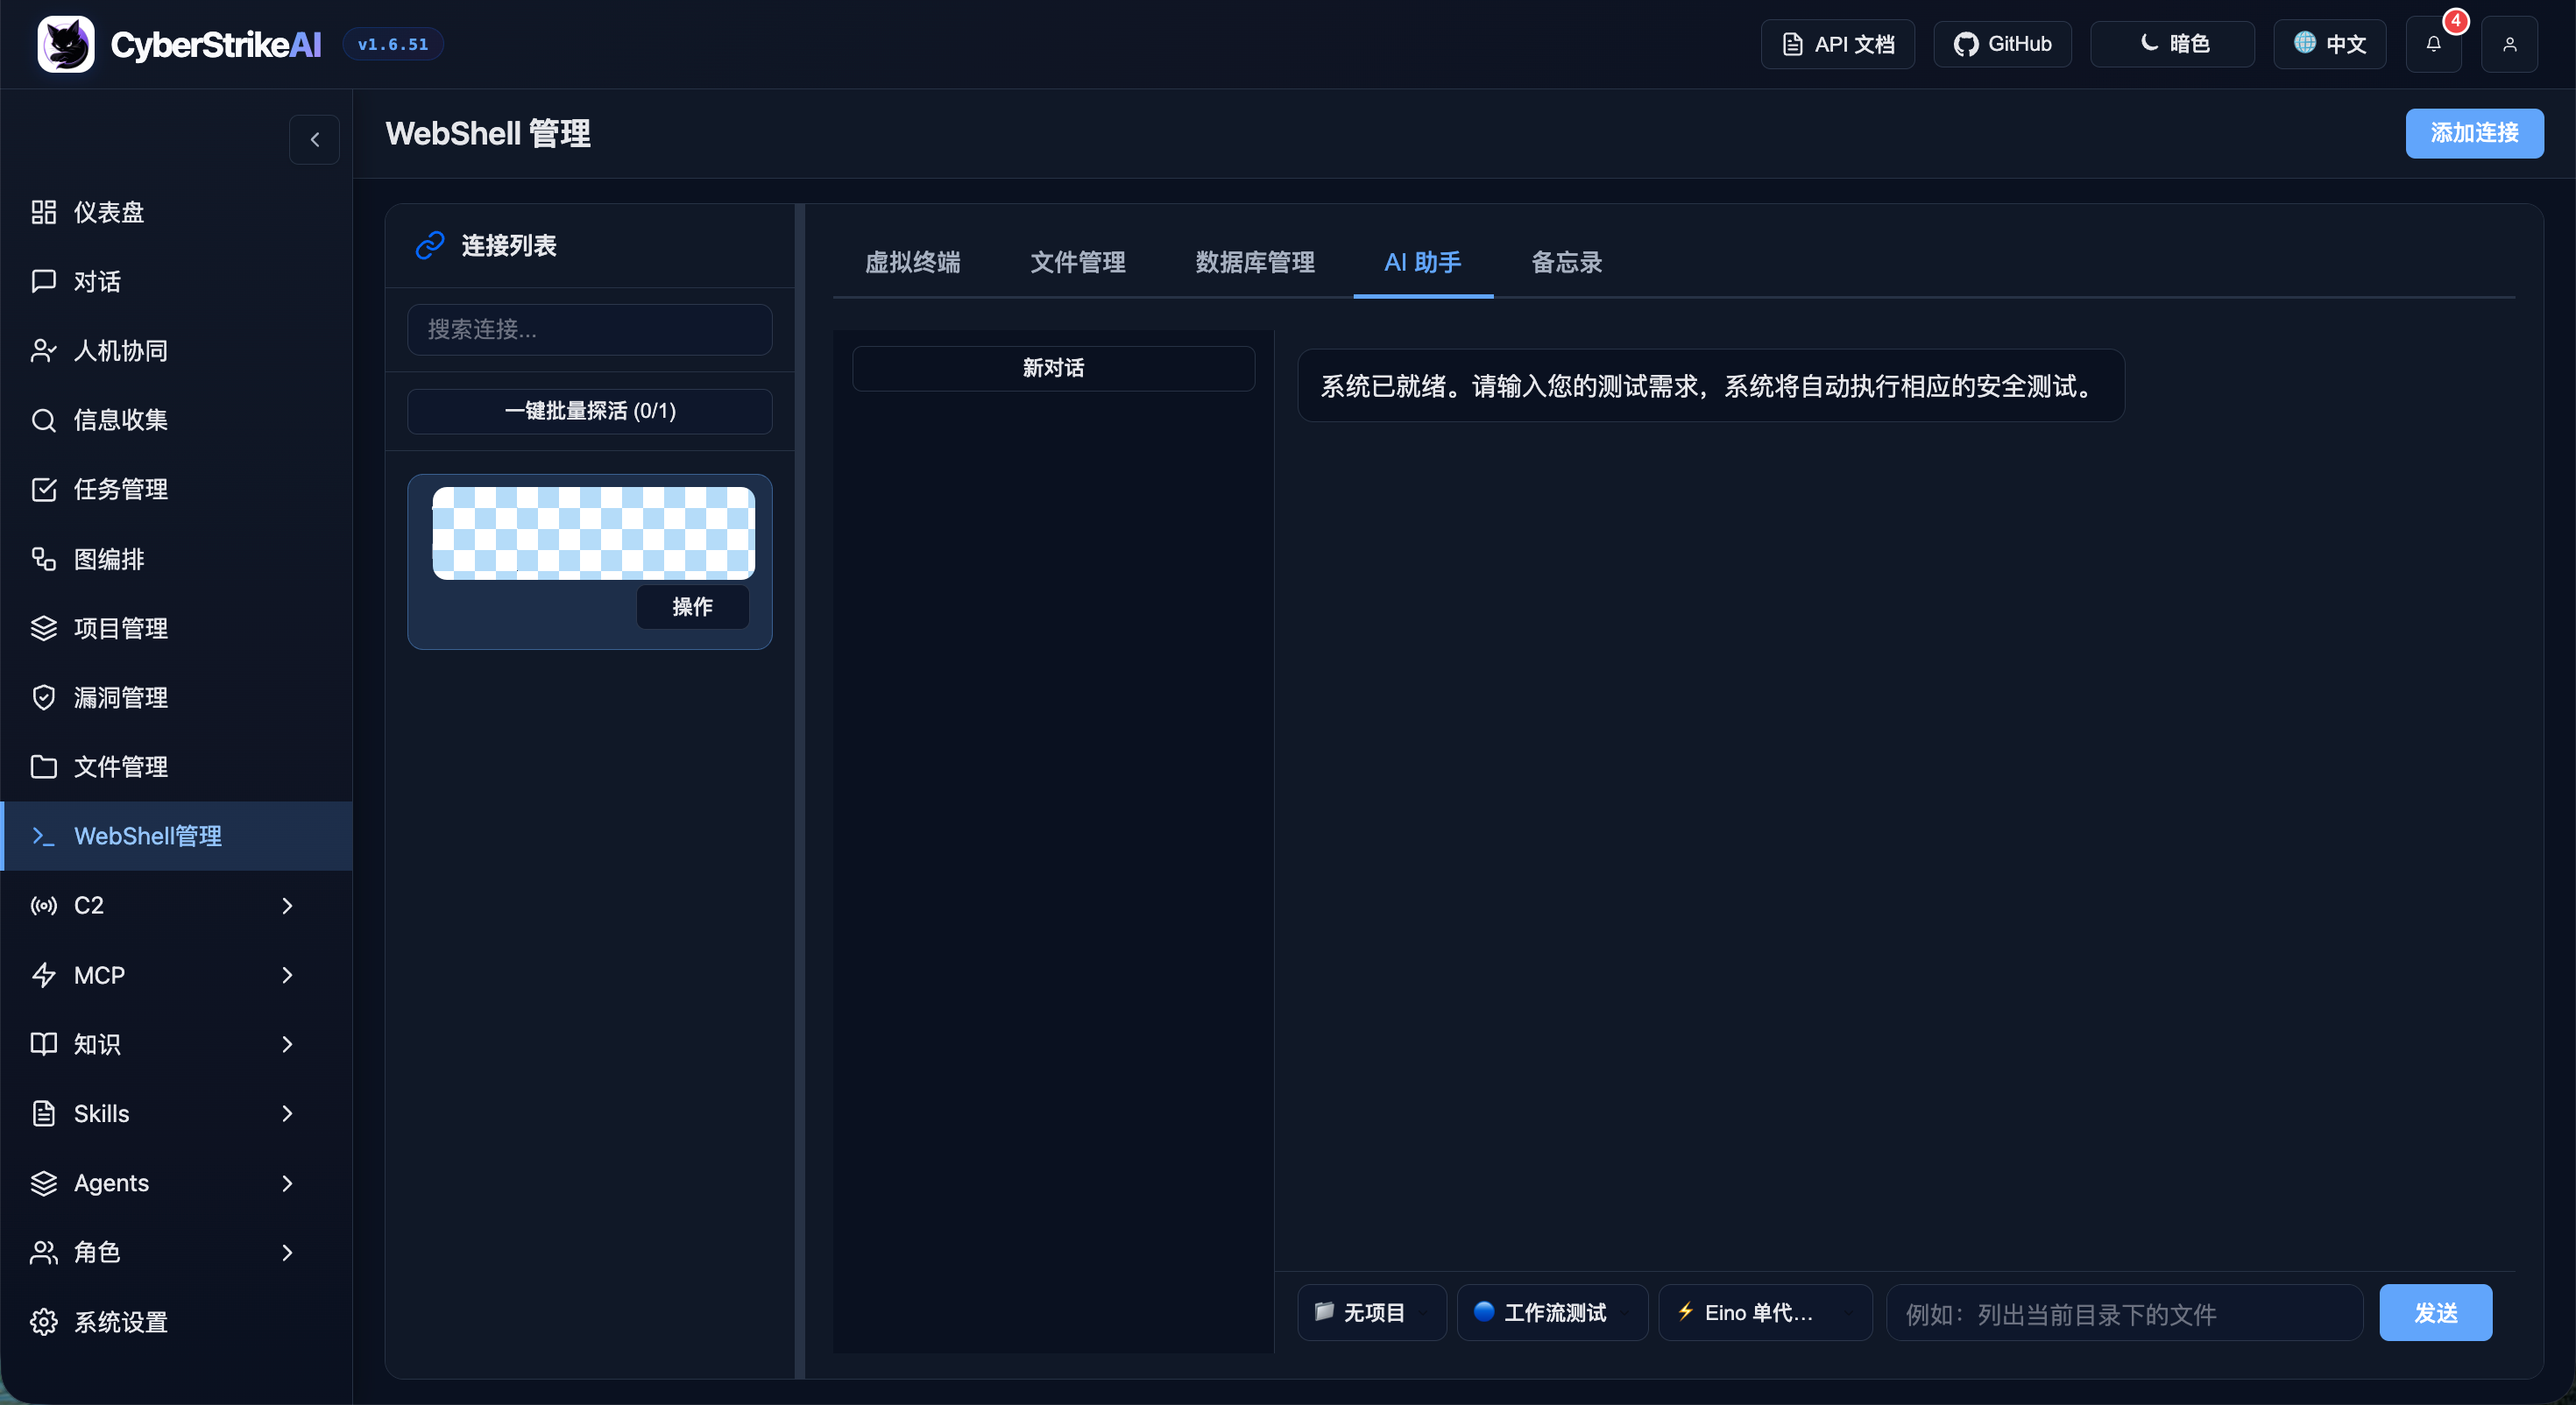
|
MCP Management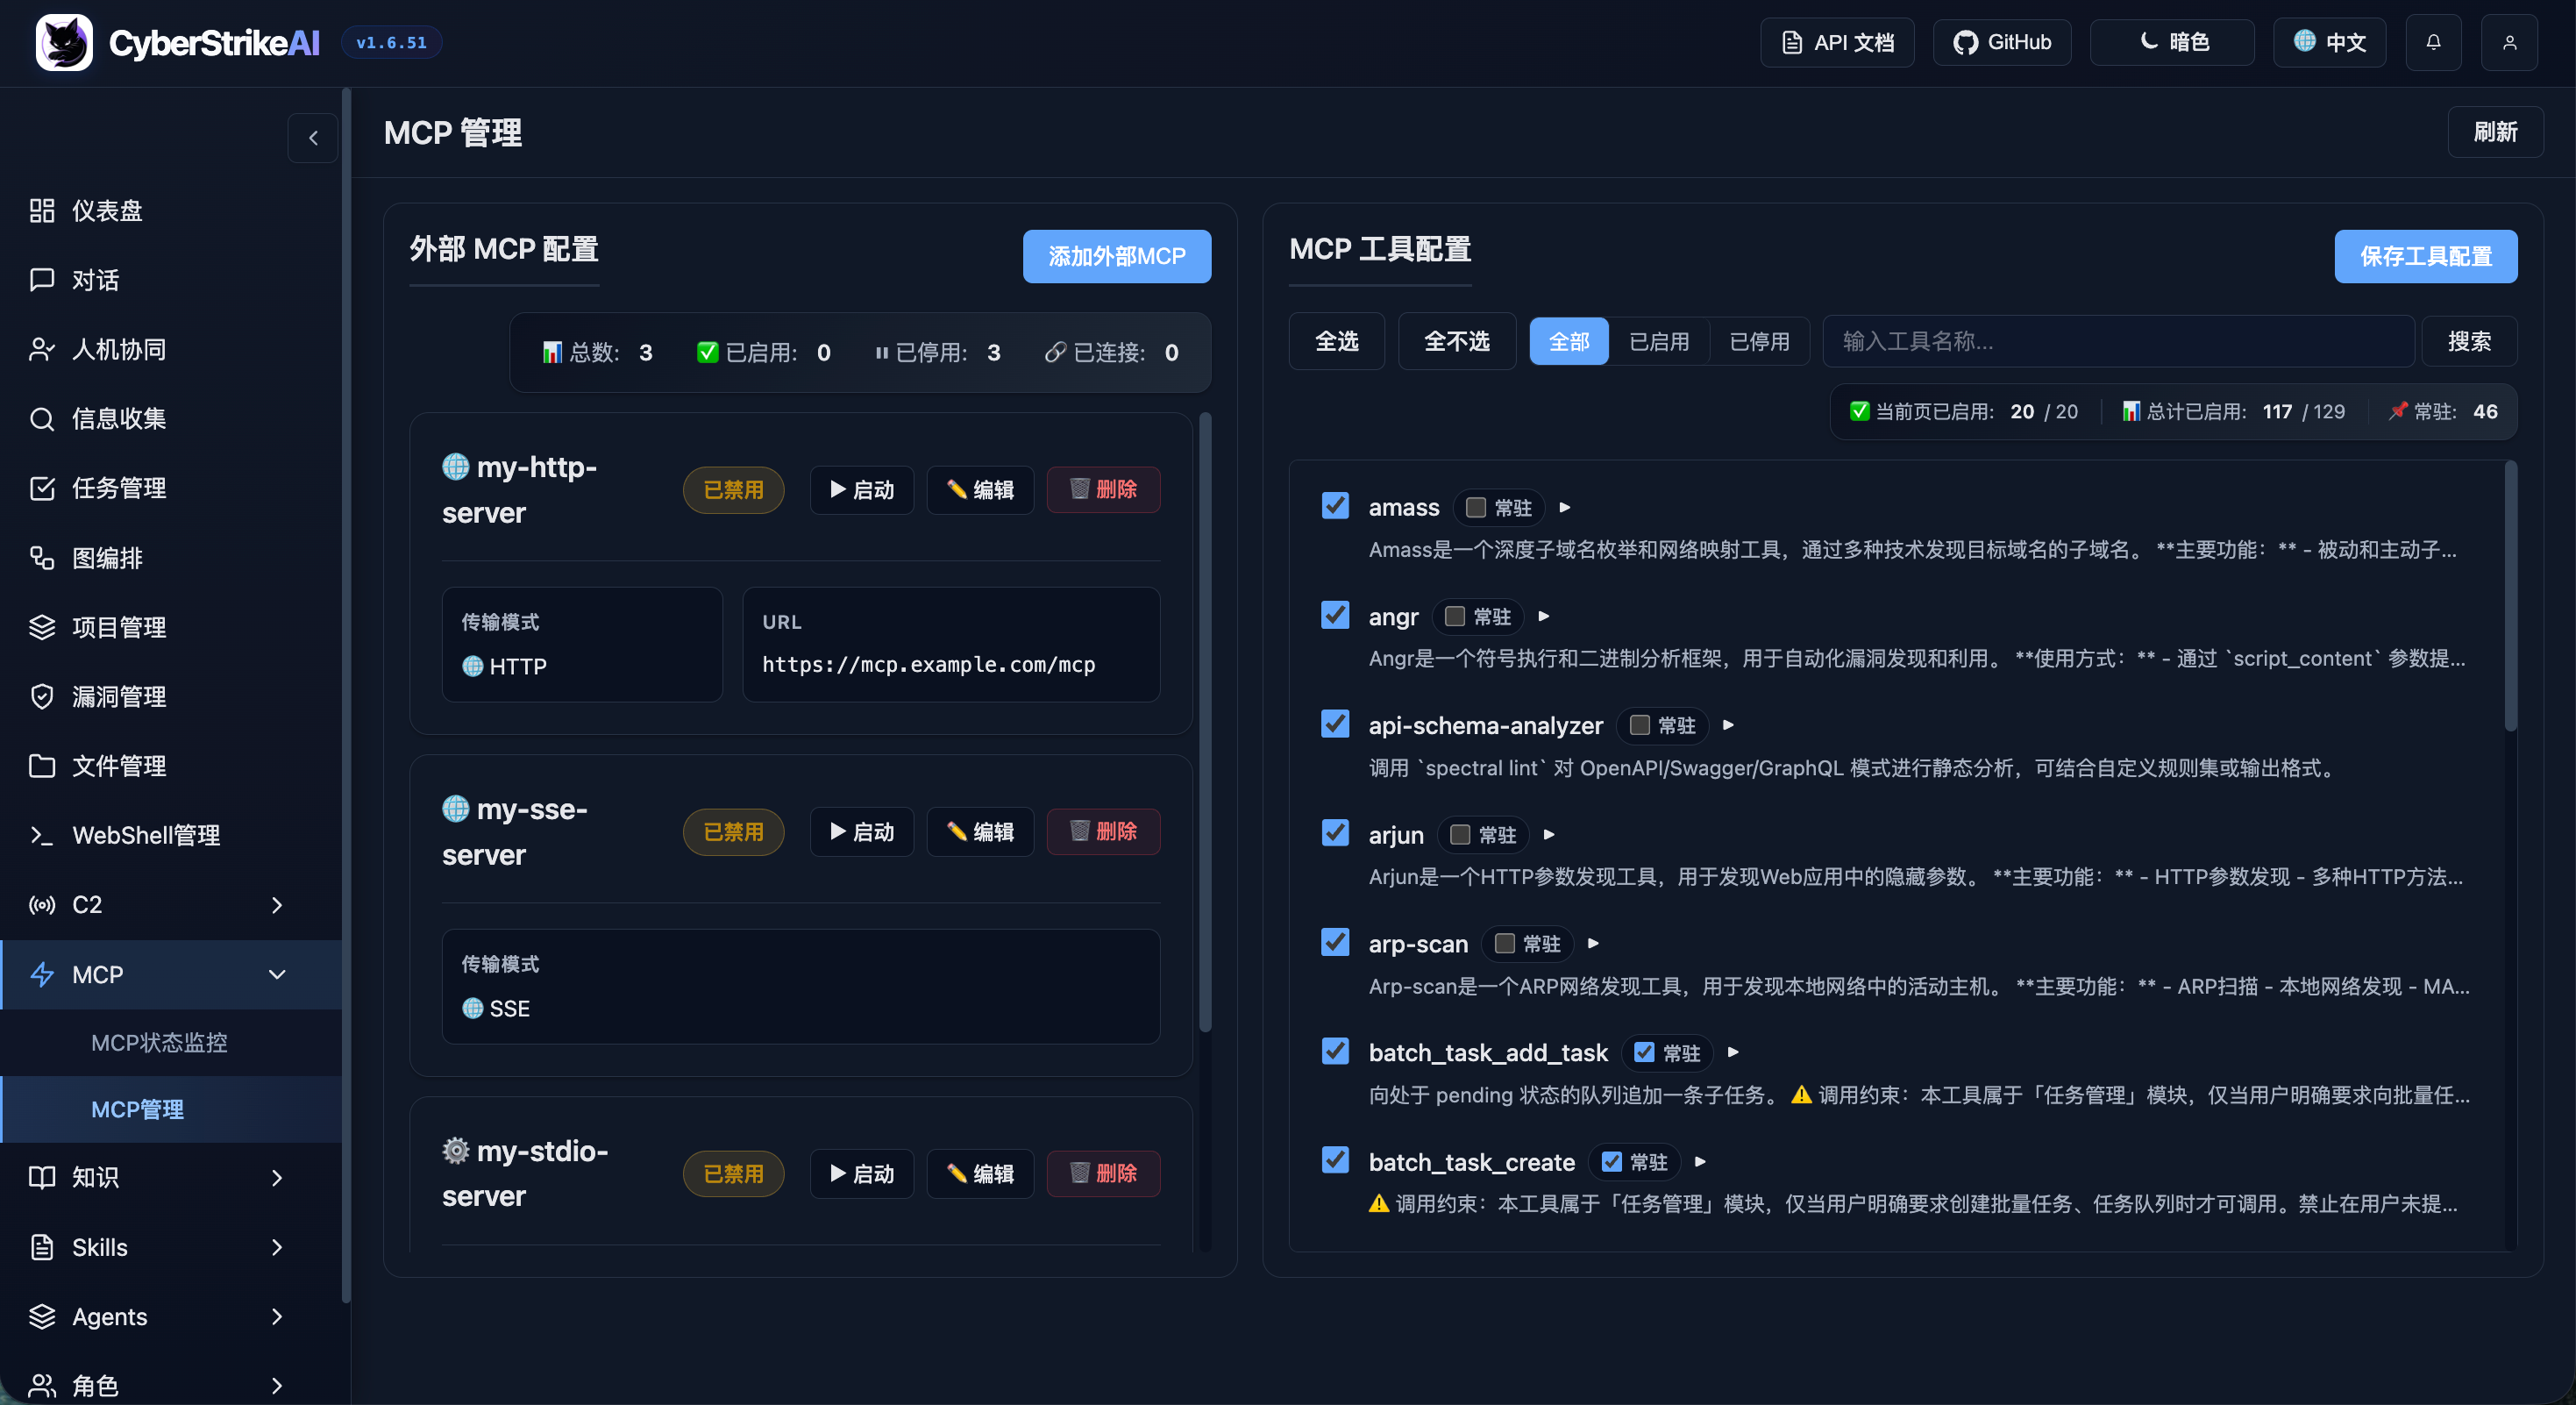
|
Knowledge Base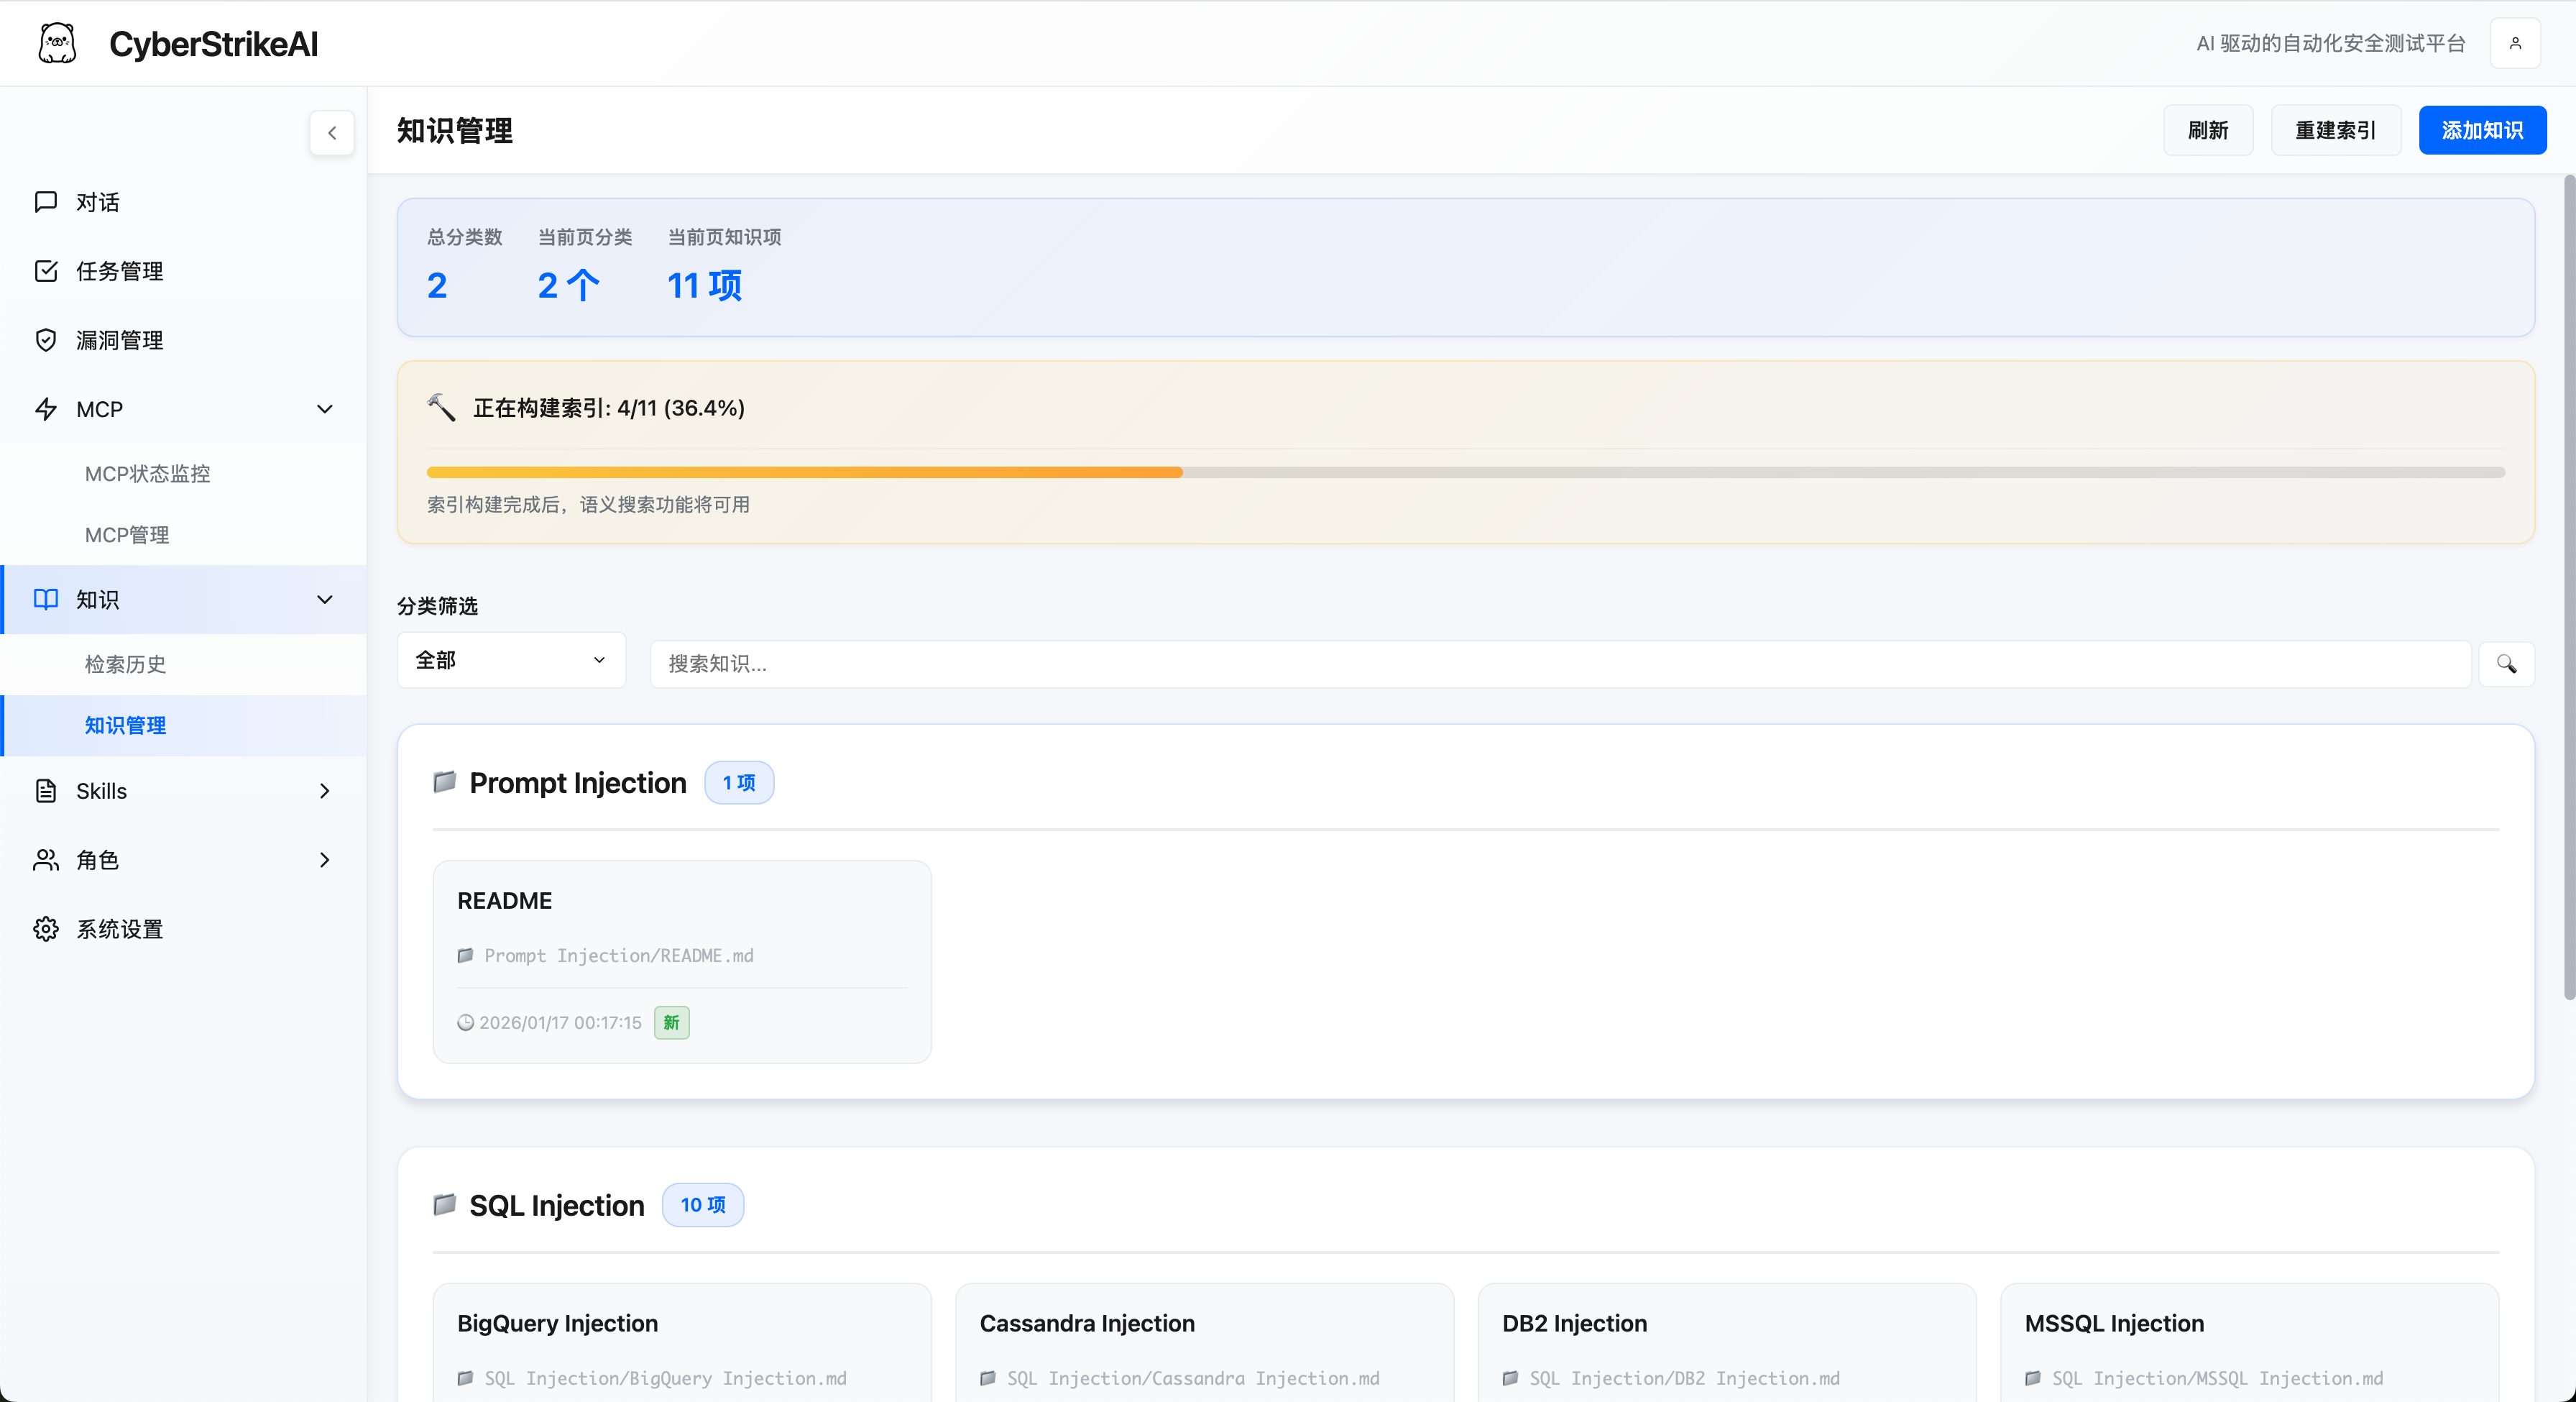
|
Skills Management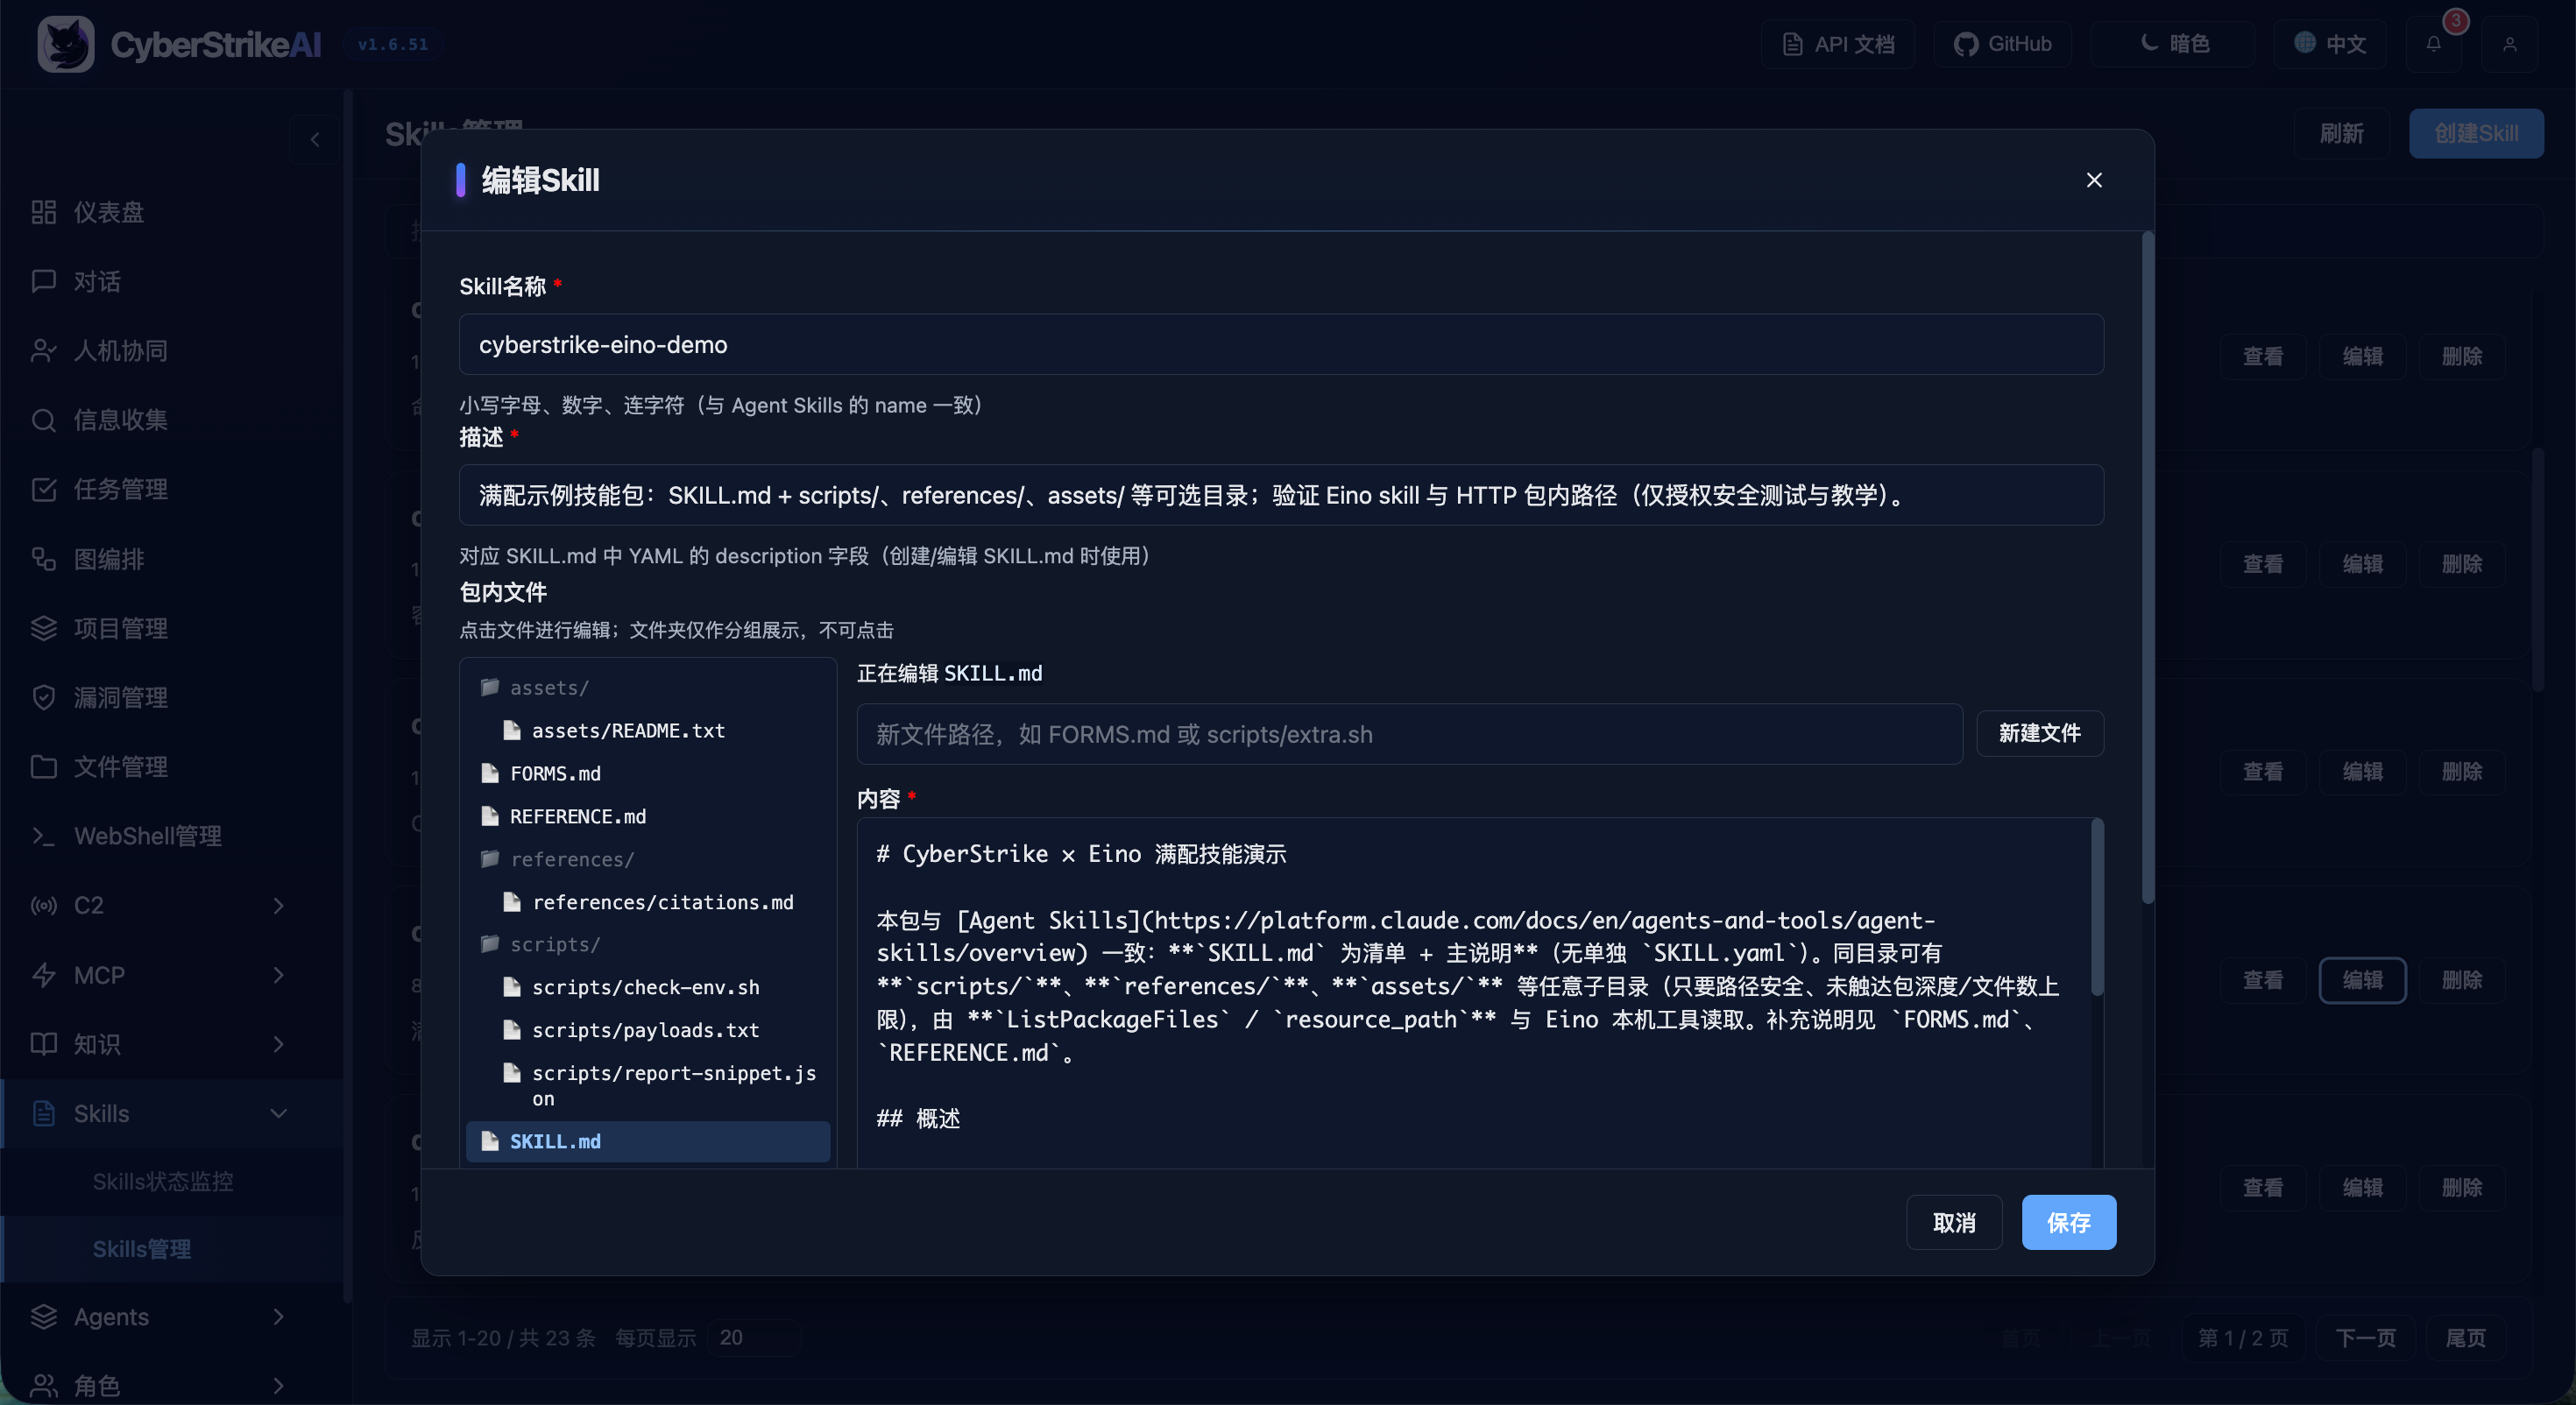
|
Agent Management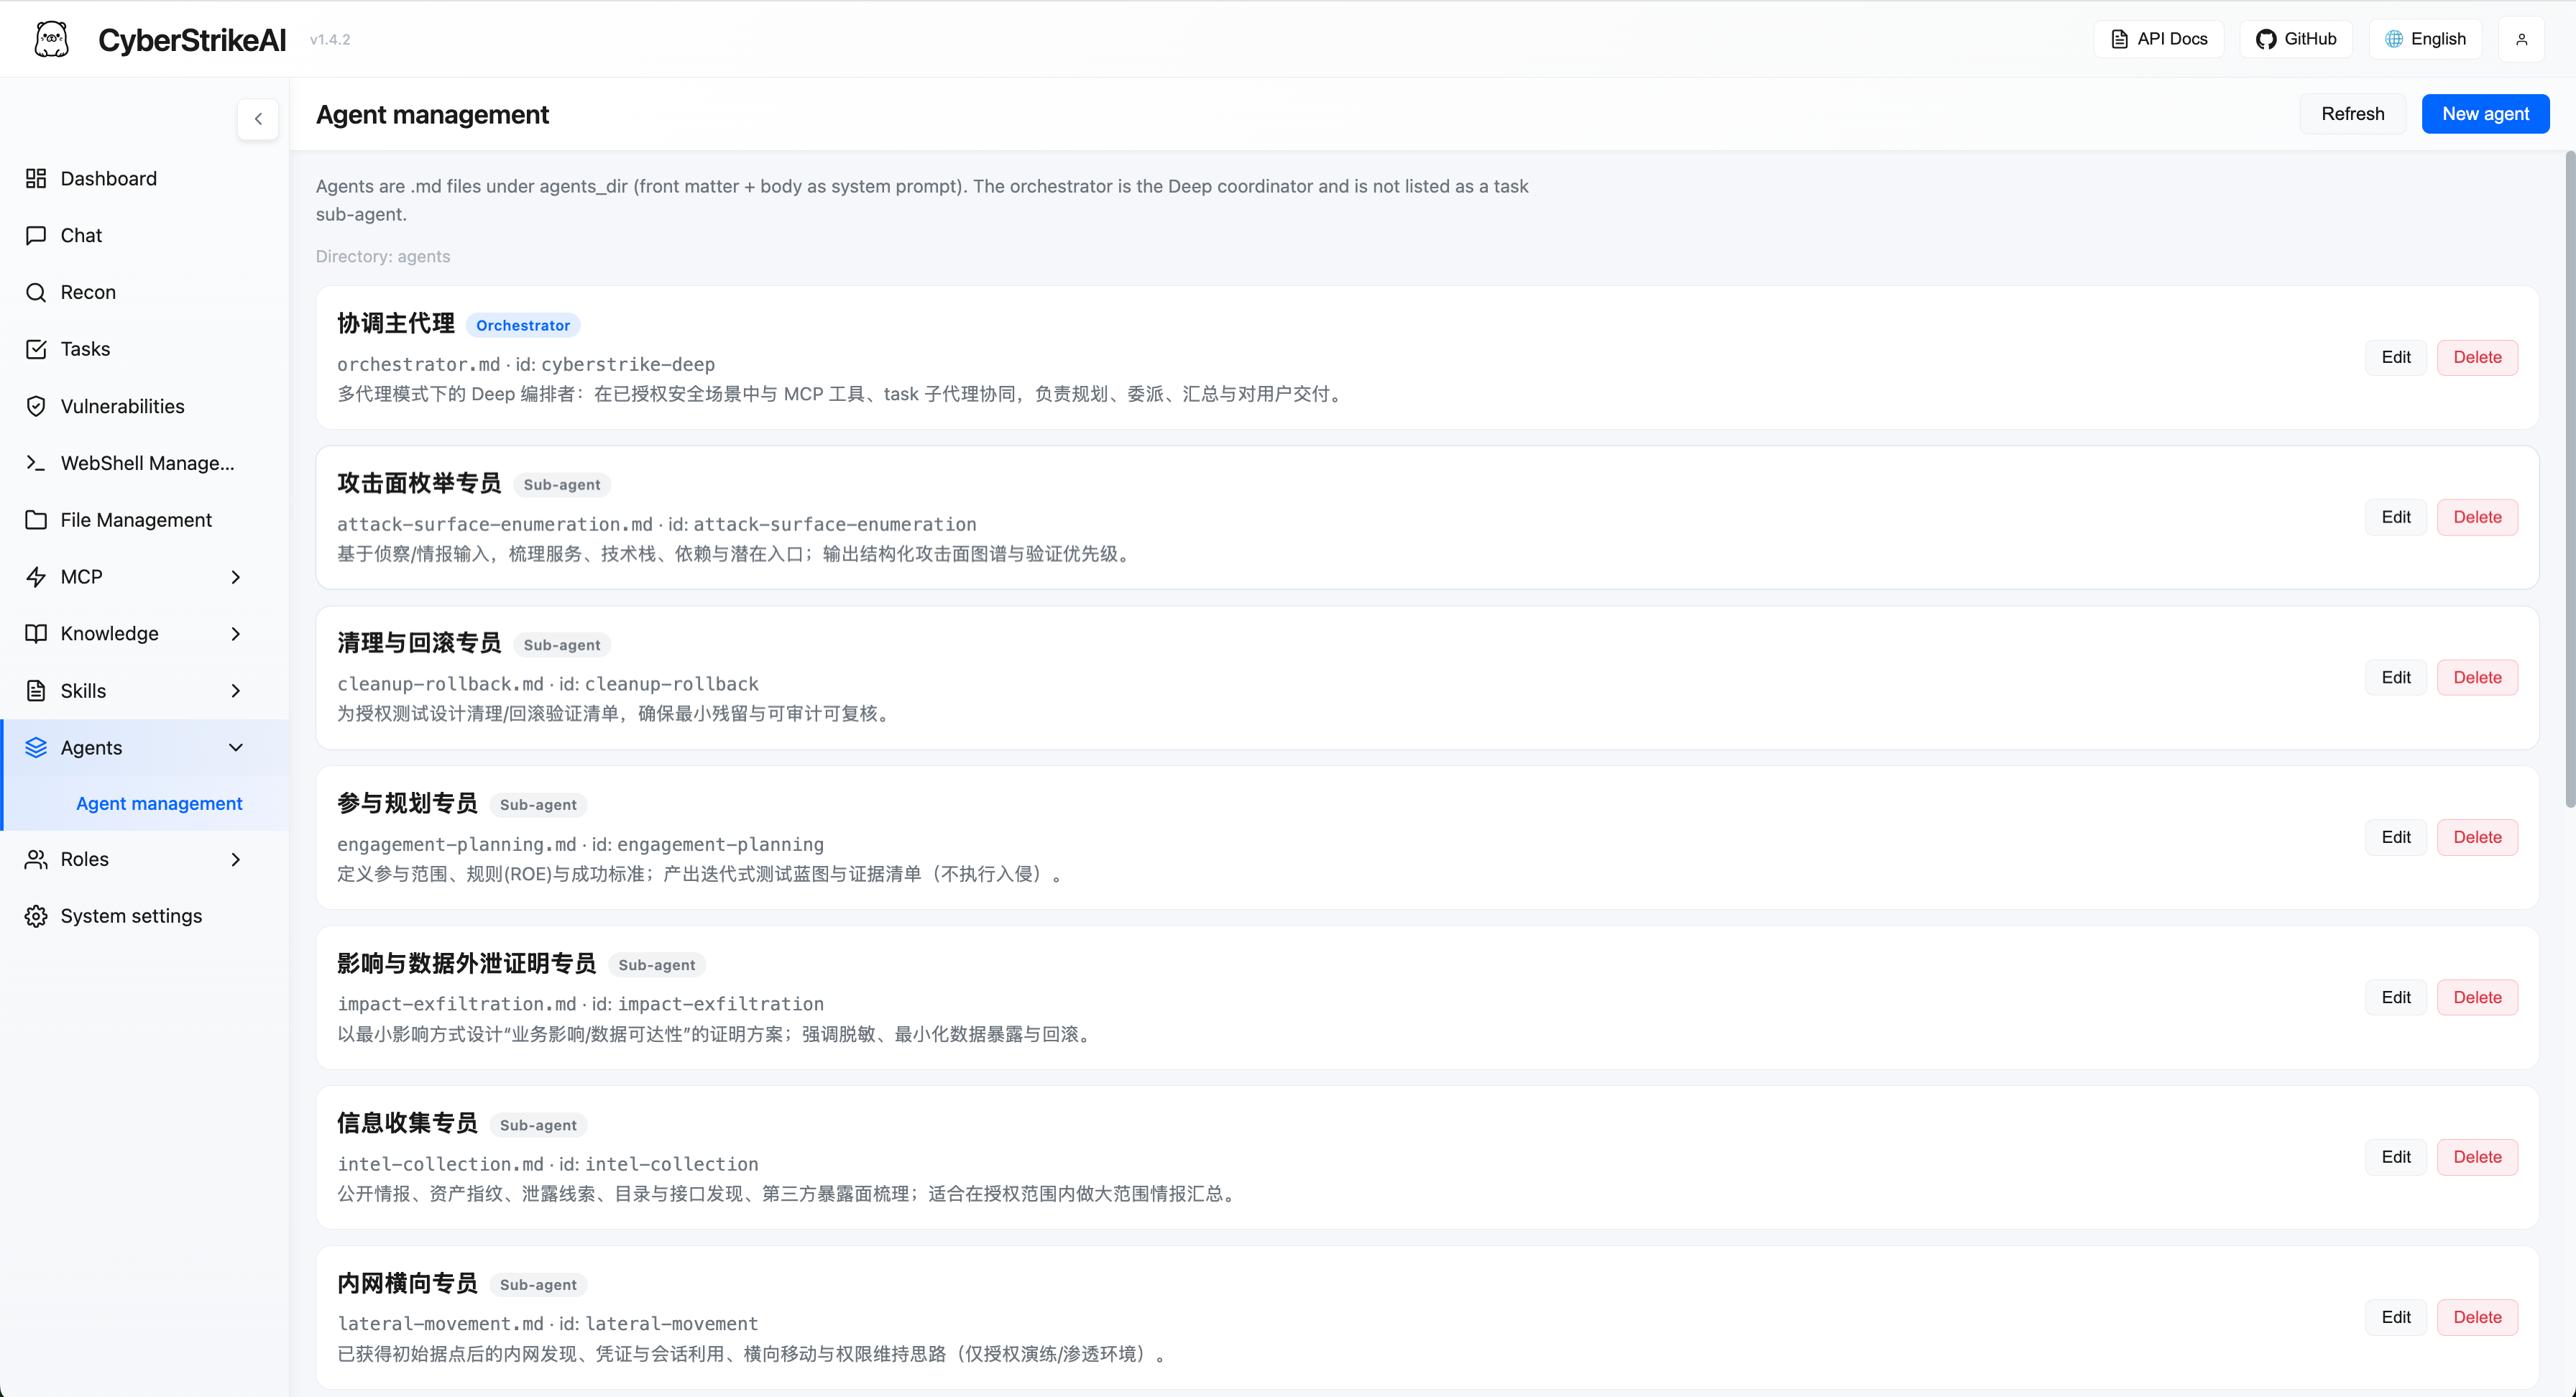
|
Role Management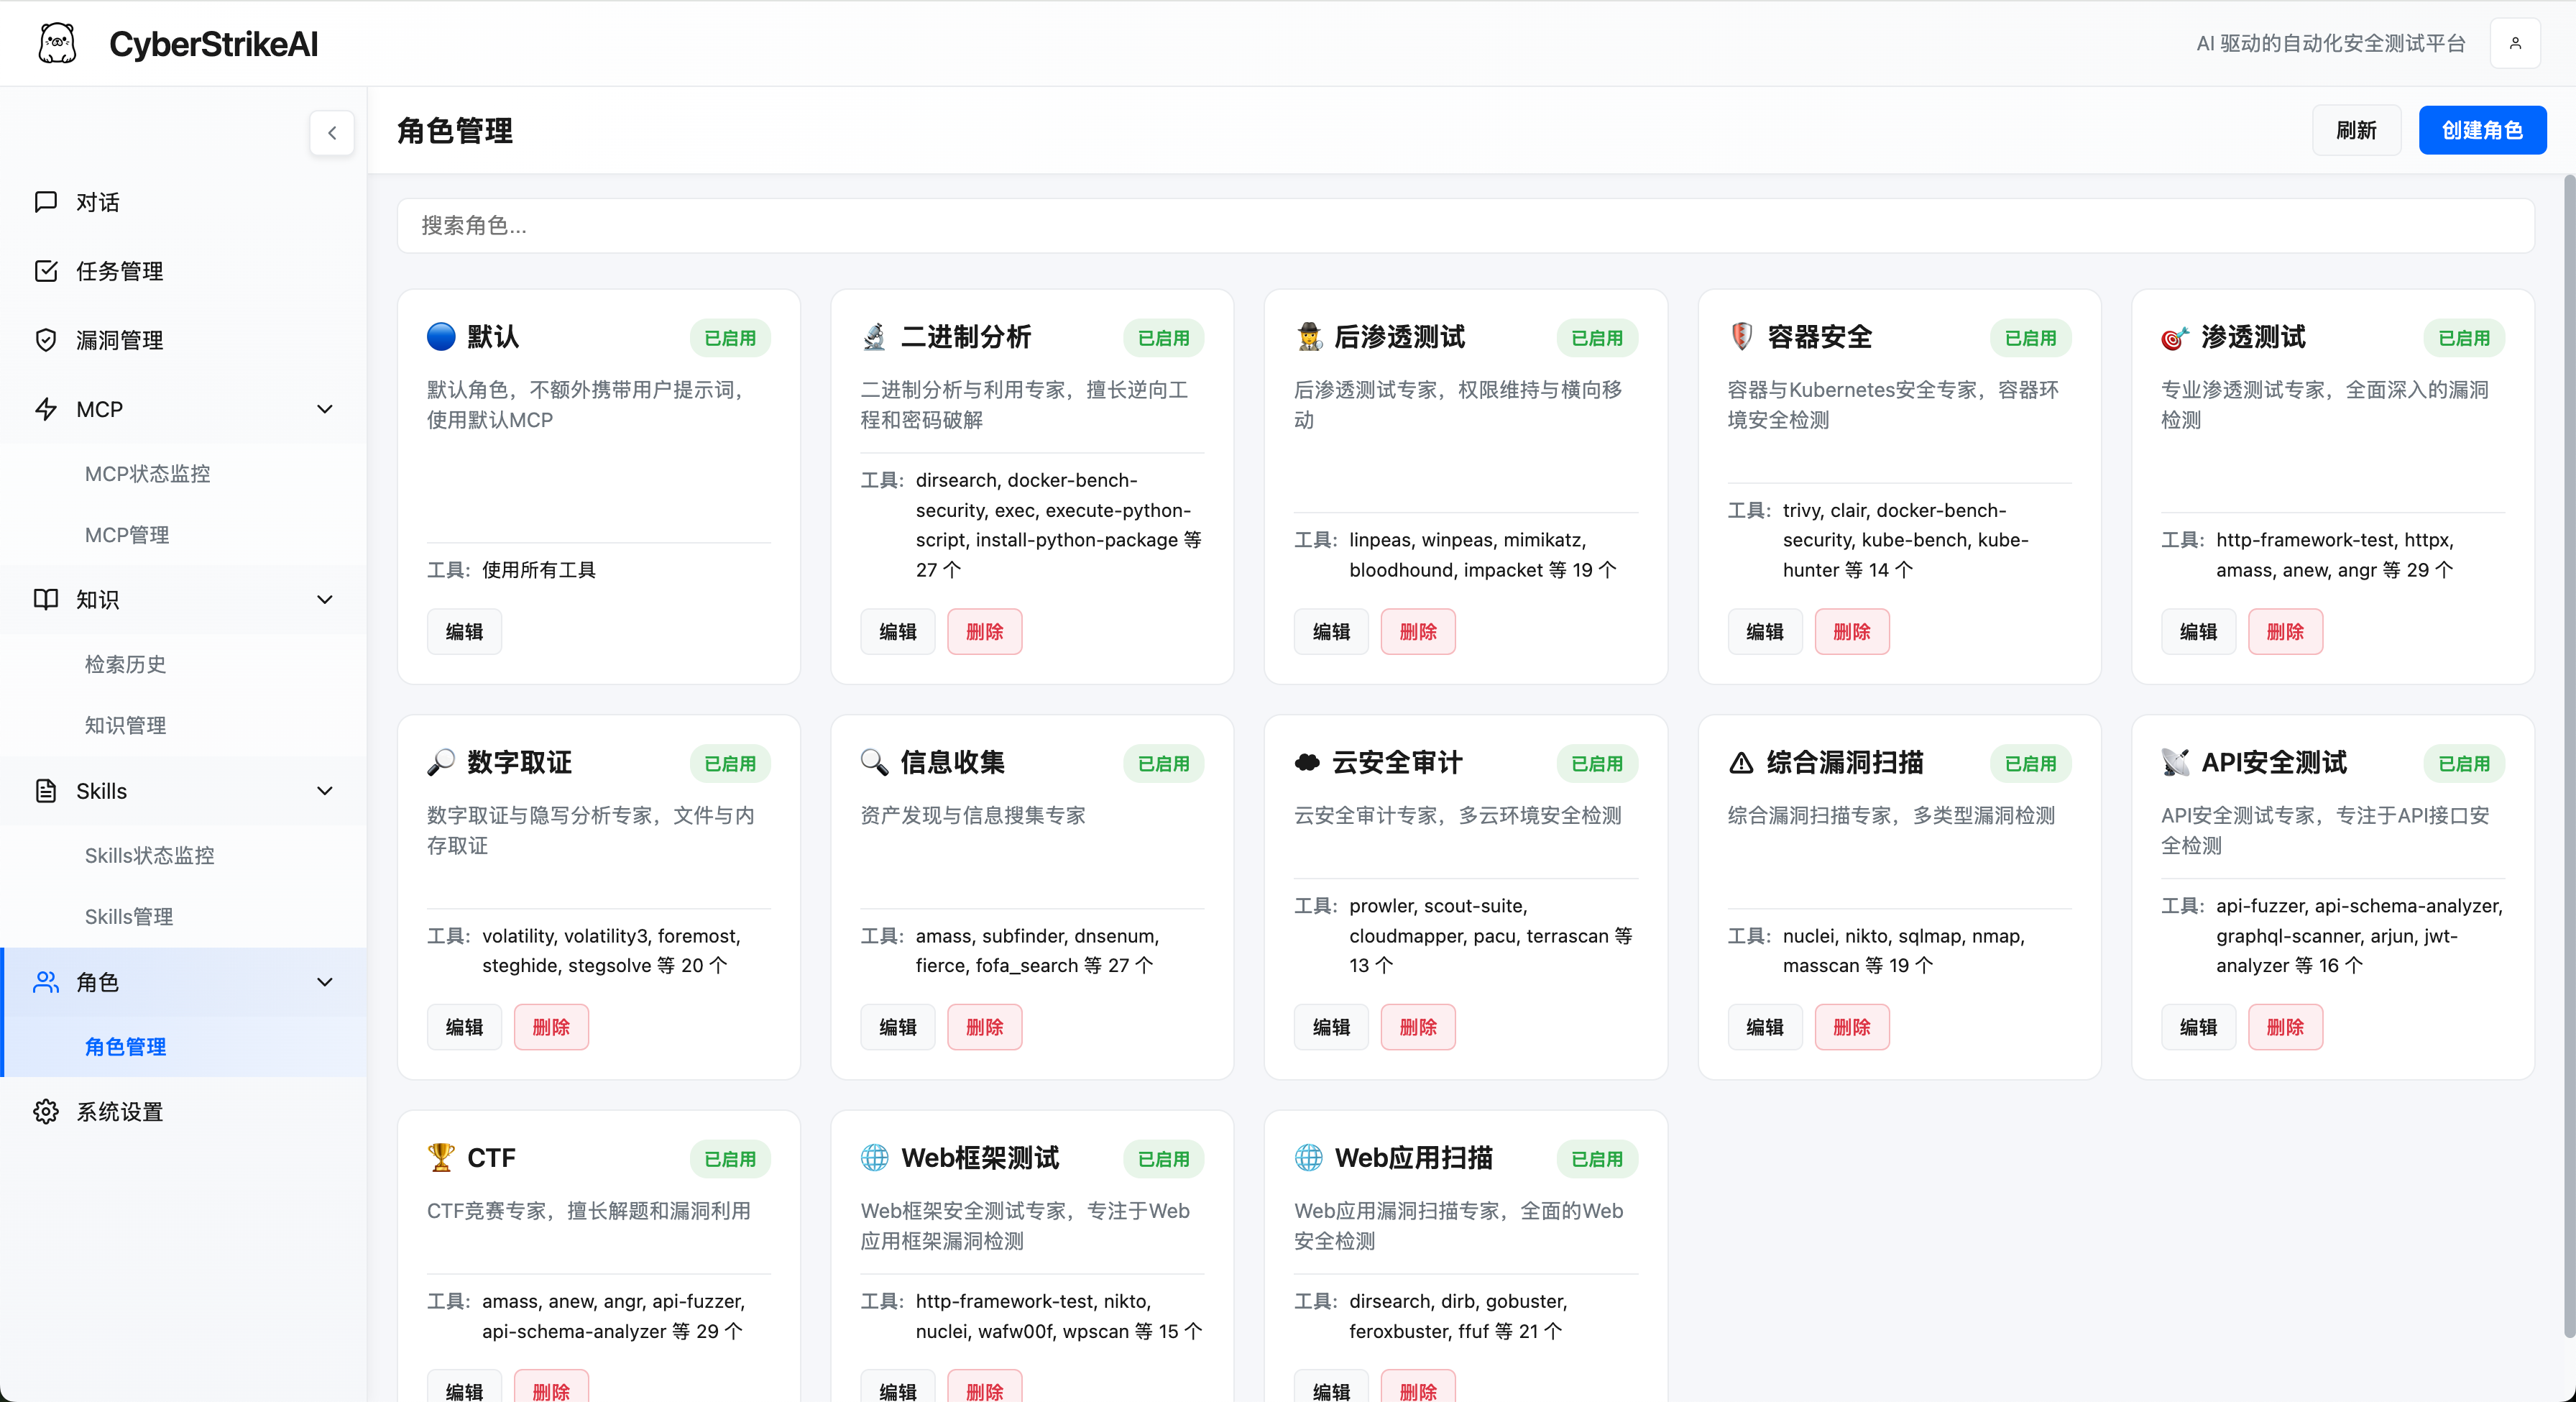
|
System Settings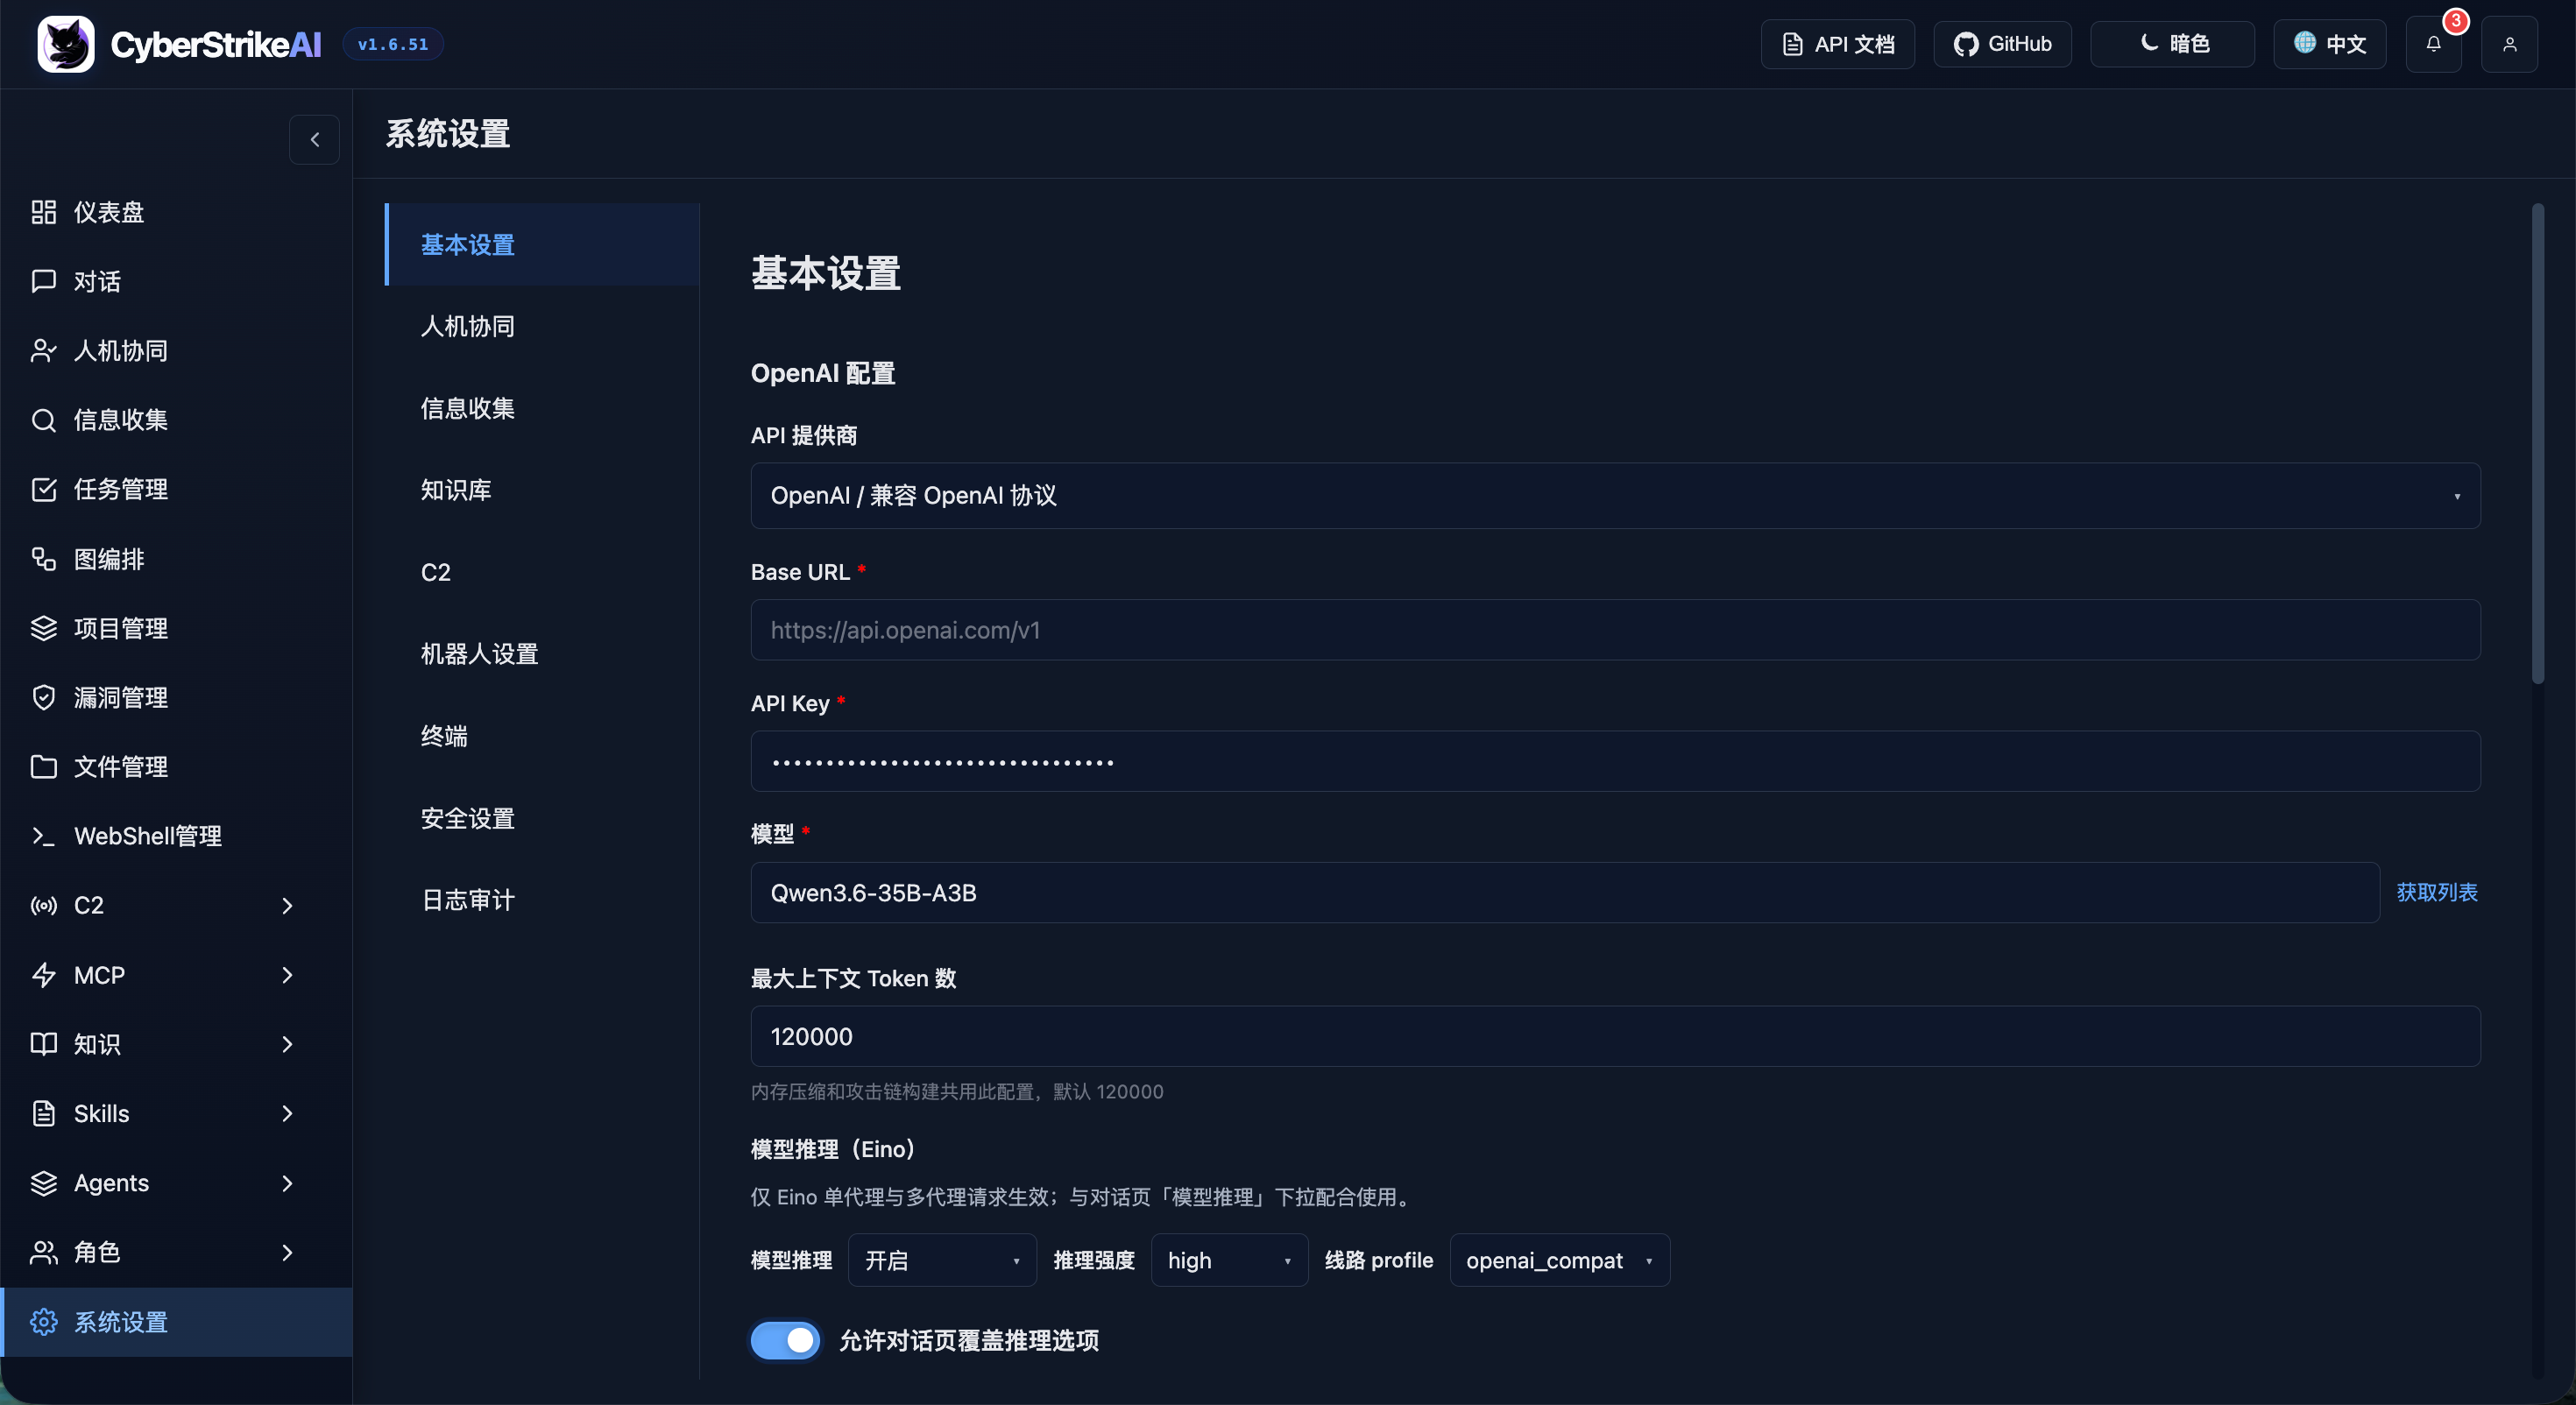
|
MCP stdio Mode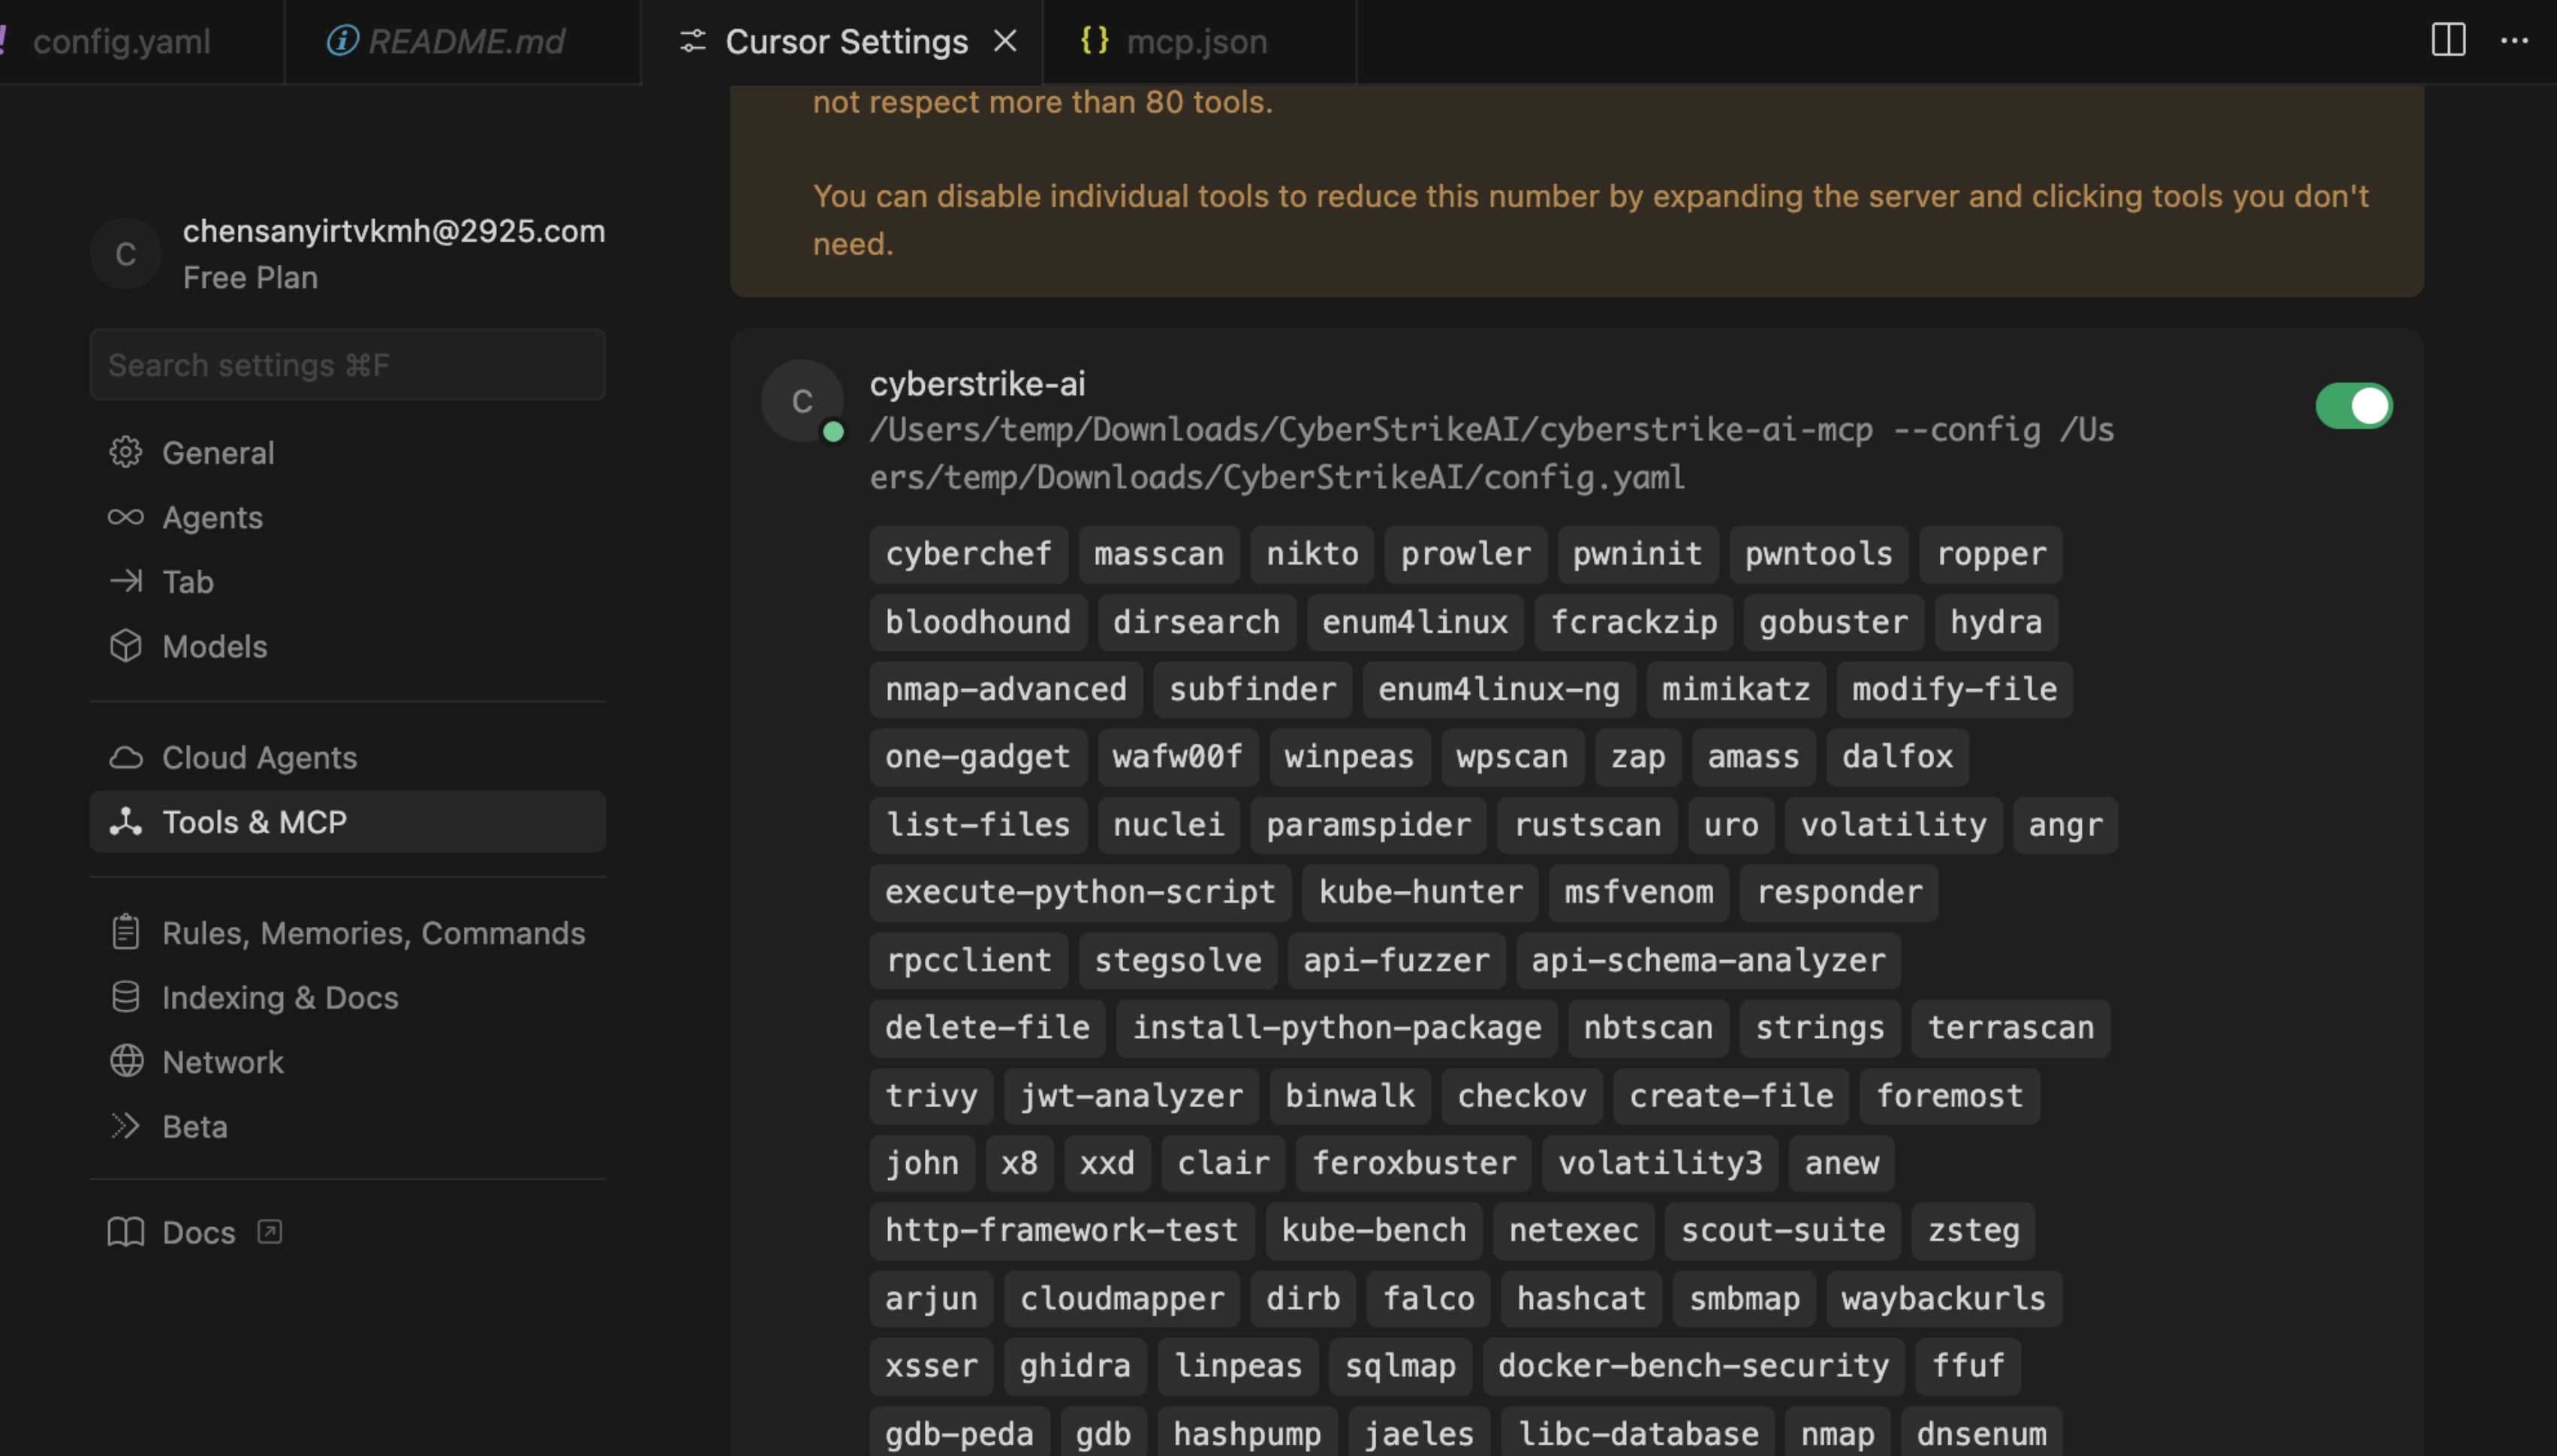
|
Burp Suite Plugin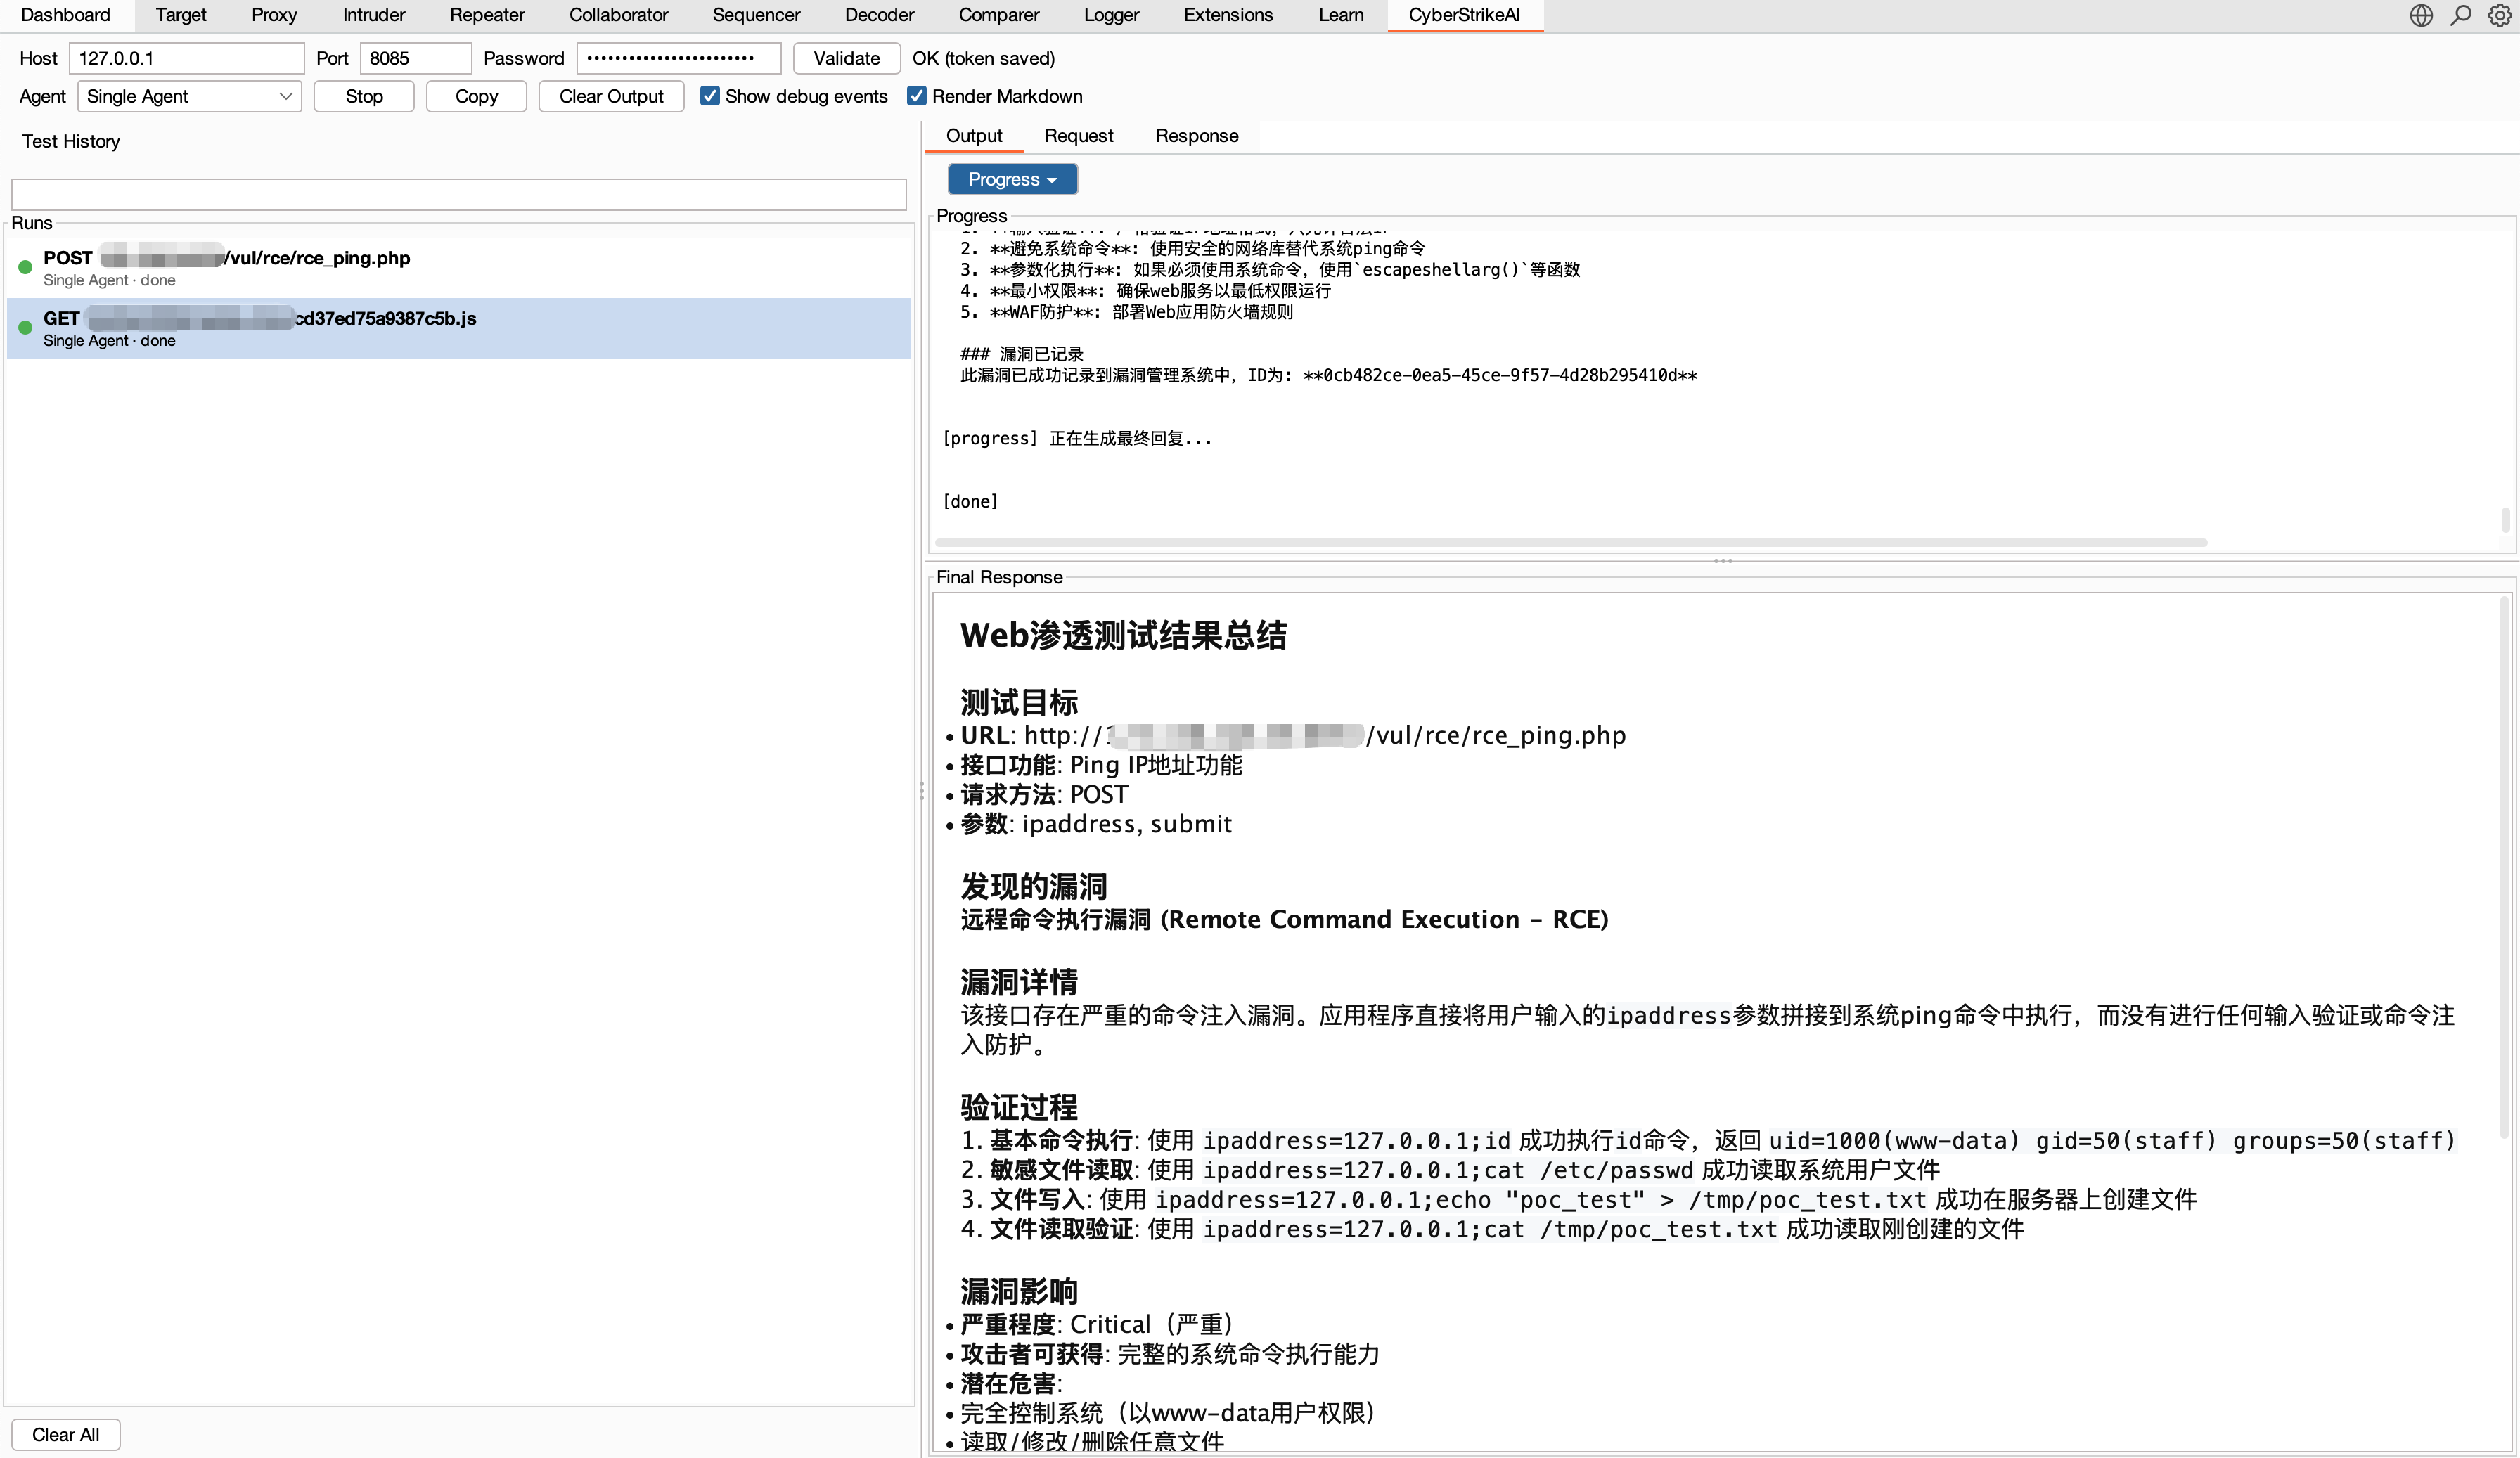
|
Highlights
Agents and orchestration
- 🤖 Agentic execution translates natural-language intent into governed, auditable security actions.
- 🧩 Eino orchestration supports single-agent execution plus Deep, Plan-Execute, and Supervisor multi-agent modes.
- 🔀 Graph workflows combine Agents, tools, conditions, approvals, and outputs into reusable flows.
- 🎭 Role-based testing provides focused prompts and tool policies for common security scenarios.
Tools and knowledge
- 🧰 Security tools include 100+ curated YAML recipes with custom extensions and role-scoped access.
- 🔌 MCP integration supports HTTP, stdio, SSE, external federation, and dynamic tool discovery.
- ⏱️ Resilient tool execution runs blocking MCP/tool calls in workers with bounded agent waits, resumable
execution_idpolling, cancellation, per-server circuit breakers, concurrency limits, and unified output caps. - 🎯 Agent Skills follow the standard Skill layout and support progressive, on-demand loading.
- 📚 Knowledge base combines query rewriting, vector retrieval, reranking, and result post-processing.
- 🖼️ Vision analysis uses a separate vision model for screenshots, captchas, and UI while retaining text summaries only.
Governance and audit
- 🧑⚖️ Human in the loop provides approval modes, tool allowlists, audit-agent review, and traceable decisions.
- 🛡️ Call blocking under Security adds configurable regex checks before MCP execution, reminder templates, and dry runs, with government-domain protection enabled by default. See Tool call blocking.
- 🔐 Platform RBAC supports multiple users, system and custom roles, scoped permissions, ownership, and explicit assignments.
- 🔒 Security and audit provide authenticated access, audit logs, SQLite persistence, and operational evidence retention.
- 📄 Result governance stores the same capped tool result seen by the agent, protects resume paths from oversized historical output, and adds UI safeguards for large detail views. See Tool Execution Governance.