#1
Tools for intercepting, analyzing, and modifying web traffic for security testing.
Kitploit recommended
 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors
 ianxtianxt/proxysqlmap
From Proxy to SqlMapApi
 ssh-mitm/ssh-mitm
Mirror moved — see GitHub and Codeberg
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…
 benrich127n/react2shell_analyzer
a dart package to analyze CVE-2025-55182 react2shell
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
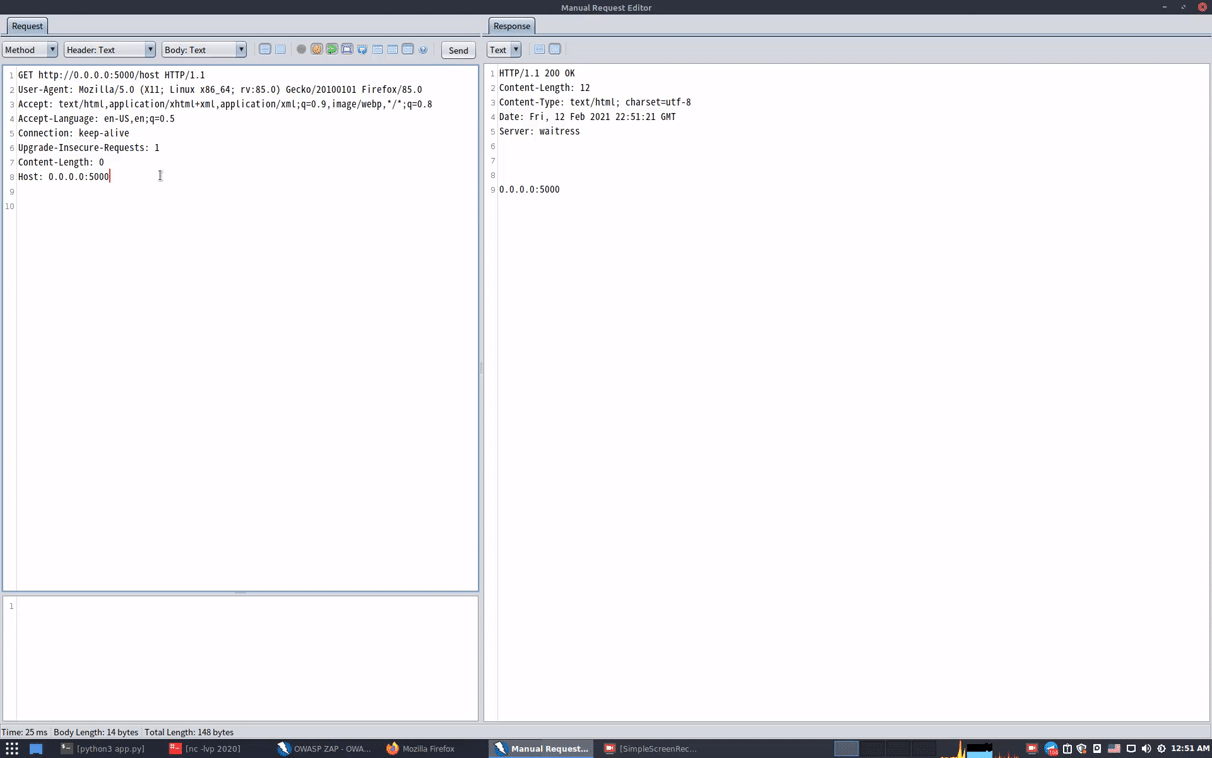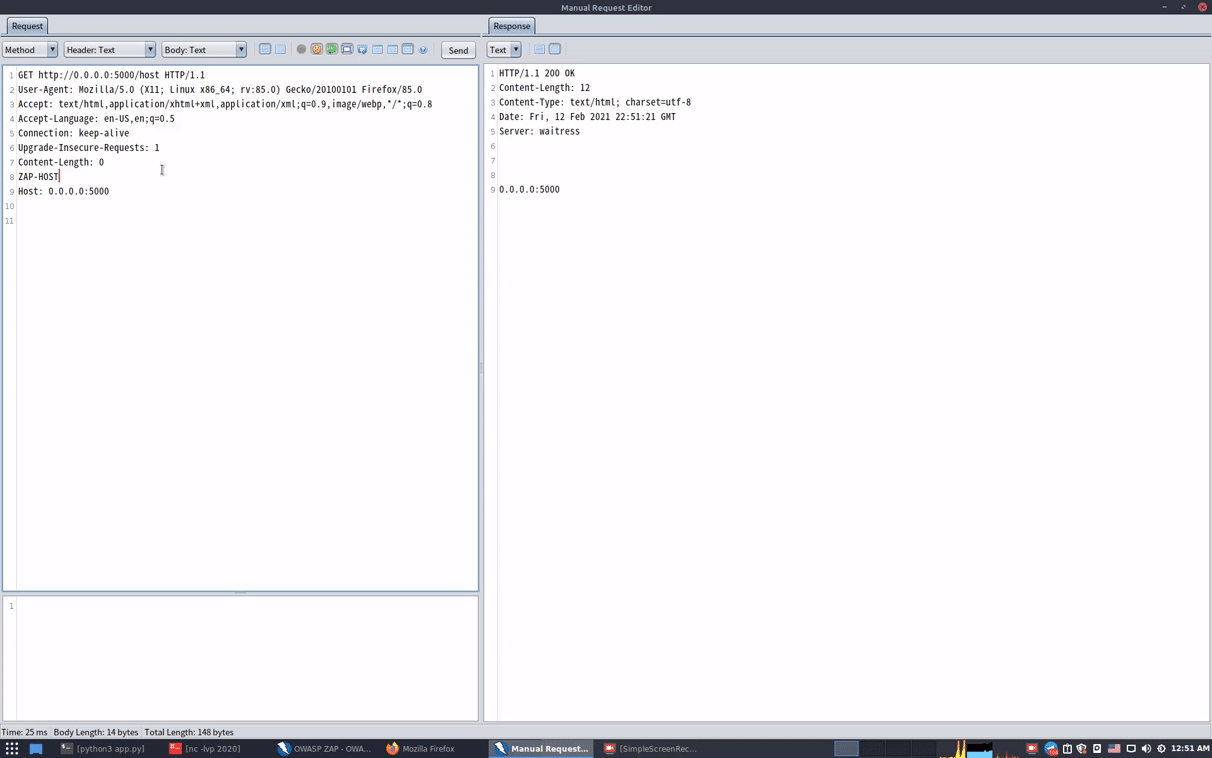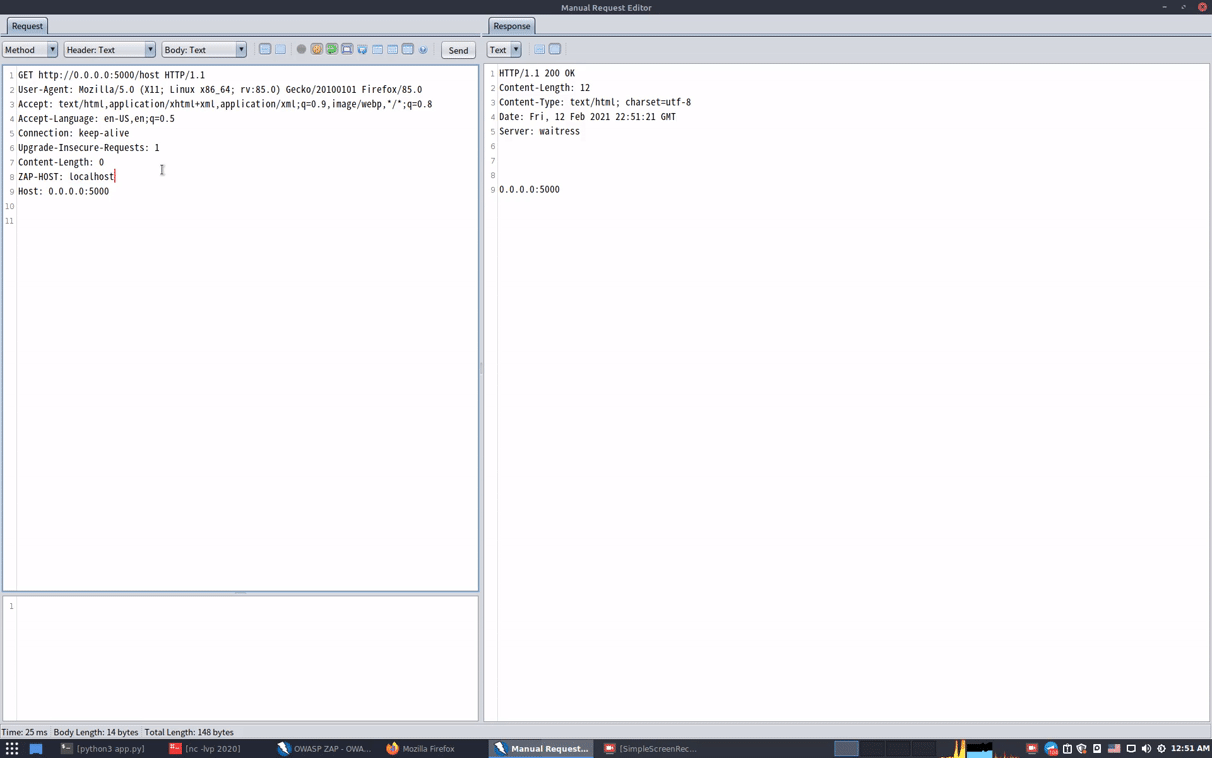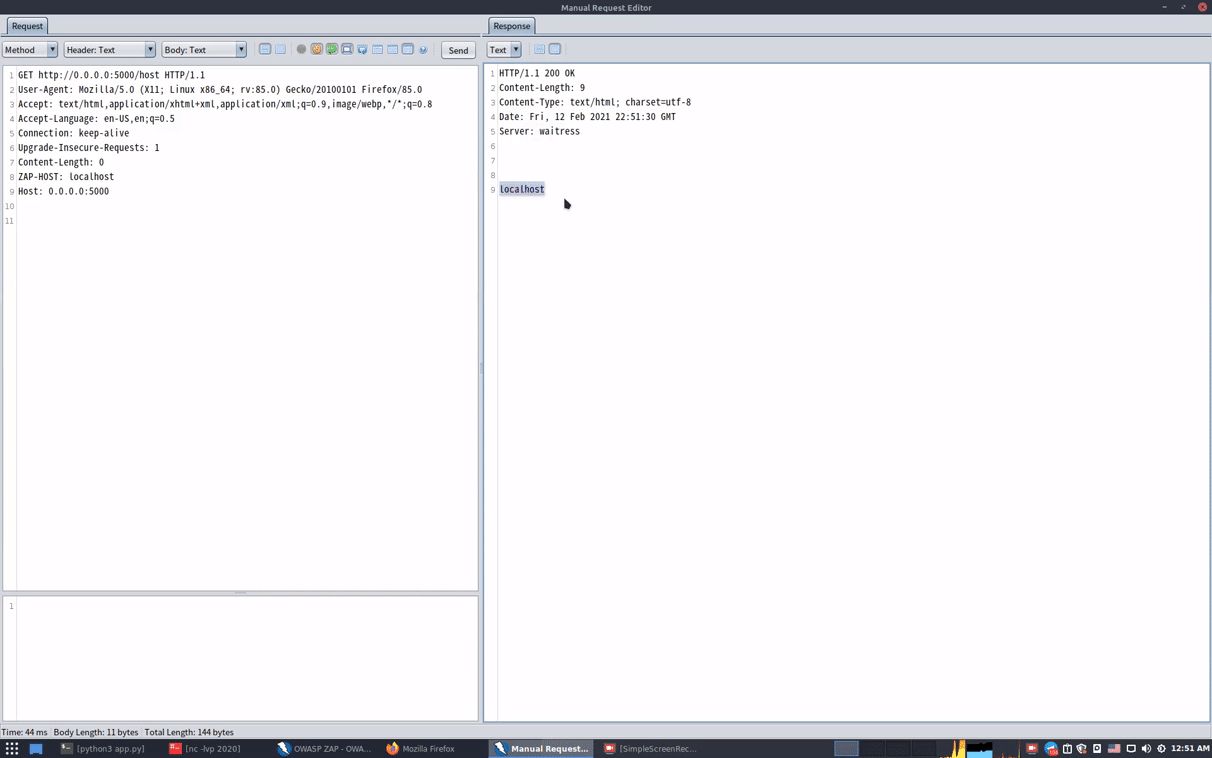 mindpatch/zaphoster
Fix host header error in zaproxy
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 hackwarts12/burp-recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
 jclarkcom/ble_proxy
BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 simplerhacking/evilginx3-phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
 abraxas/ats-authproxy-prefix
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - authproxy prefix
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.