
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 horizon3ai/cve-2024-29824
Ivanti EPM SQL Injection Remote Code Execution Vulnerability
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 b1anda0/cve-2020-8209
该脚本为Citrix XenMobile 目录遍历漏洞(CVE-2020-8209)批量检测脚本。
 shuai06/cve-2022-30525
Zyxel 防火墙远程命令注入漏洞(CVE-2022-30525)批量检测脚本
 verctor/nexus_rce_cve-2019-7238
Some debug notes and exploit(not blind)
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 p3nt3st3r-star/cve-2026-0300-poc
Proof-of-concept for CVE-2026-0300, a critical buffer overflow in PAN-OS User-ID Portal enabling unauthenticated remote code execution with root…
 wildkindcc/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Authenticated Command Injection (Reverse Shell)
 liangyueliangyue/spring-core-rce
Python-based exploit for CVE-2022-22965 (Spring4Shell) with vulnerability detection and webshell injection (Behinder/Godzilla) into Spring web…
 mr-xn/cve-2022-40127
Apache Airflow < 2.4.0 DAG example_bash_operator RCE POC
 ilmila/springcss-cve-2014-3625
spring mvc cve-2014-3625
 h4x0r-dz/cve-2024-3656
Keycloak admin API allows low privilege users to use administrative functions
 boogipop/metabasercetools
CVE-2023-38646 Metabase RCE
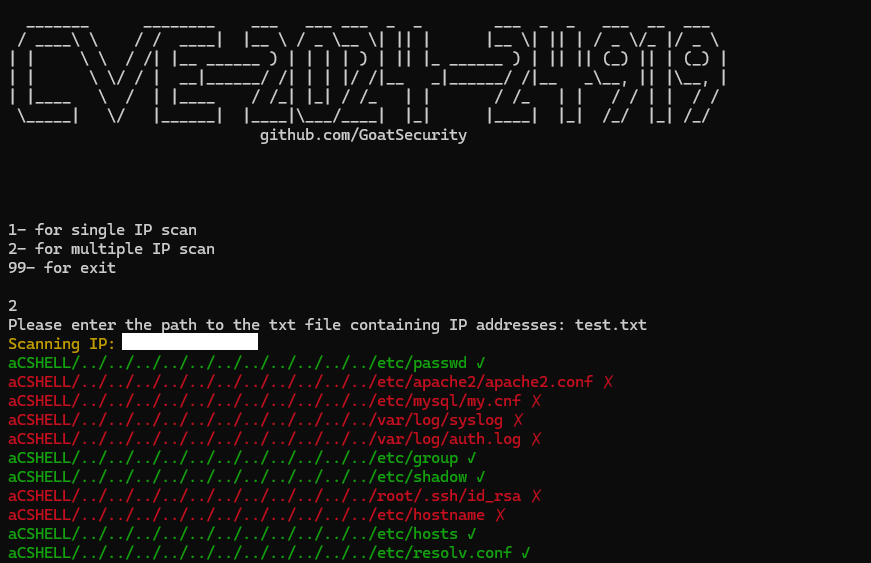 goatsecurity/cve-2024-24919
CVE-2024-24919 exploit
 purplewaveio/cve-2022-25765-pdfkit-exploit-reverse-shell
pdfkit <0.8.6 command injection shell. The package pdfkit from 0.0.0 are vulnerable to Command Injection where the URL is not properly sanitized.…
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 emerinohdz/facebrute
Facebook brute forcer script
 jaiguptanick/cve-2019-0232
Vulnerability analysis and PoC for the Apache Tomcat - CGIServlet enableCmdLineArguments Remote Code Execution (RCE)








