
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 justakazh/mass_cve-2021-41773
MASS CVE-2021-41773
 mr-xn/cve-2022-24112
CVE-2022-24112:Apache APISIX apisix/batch-requests RCE
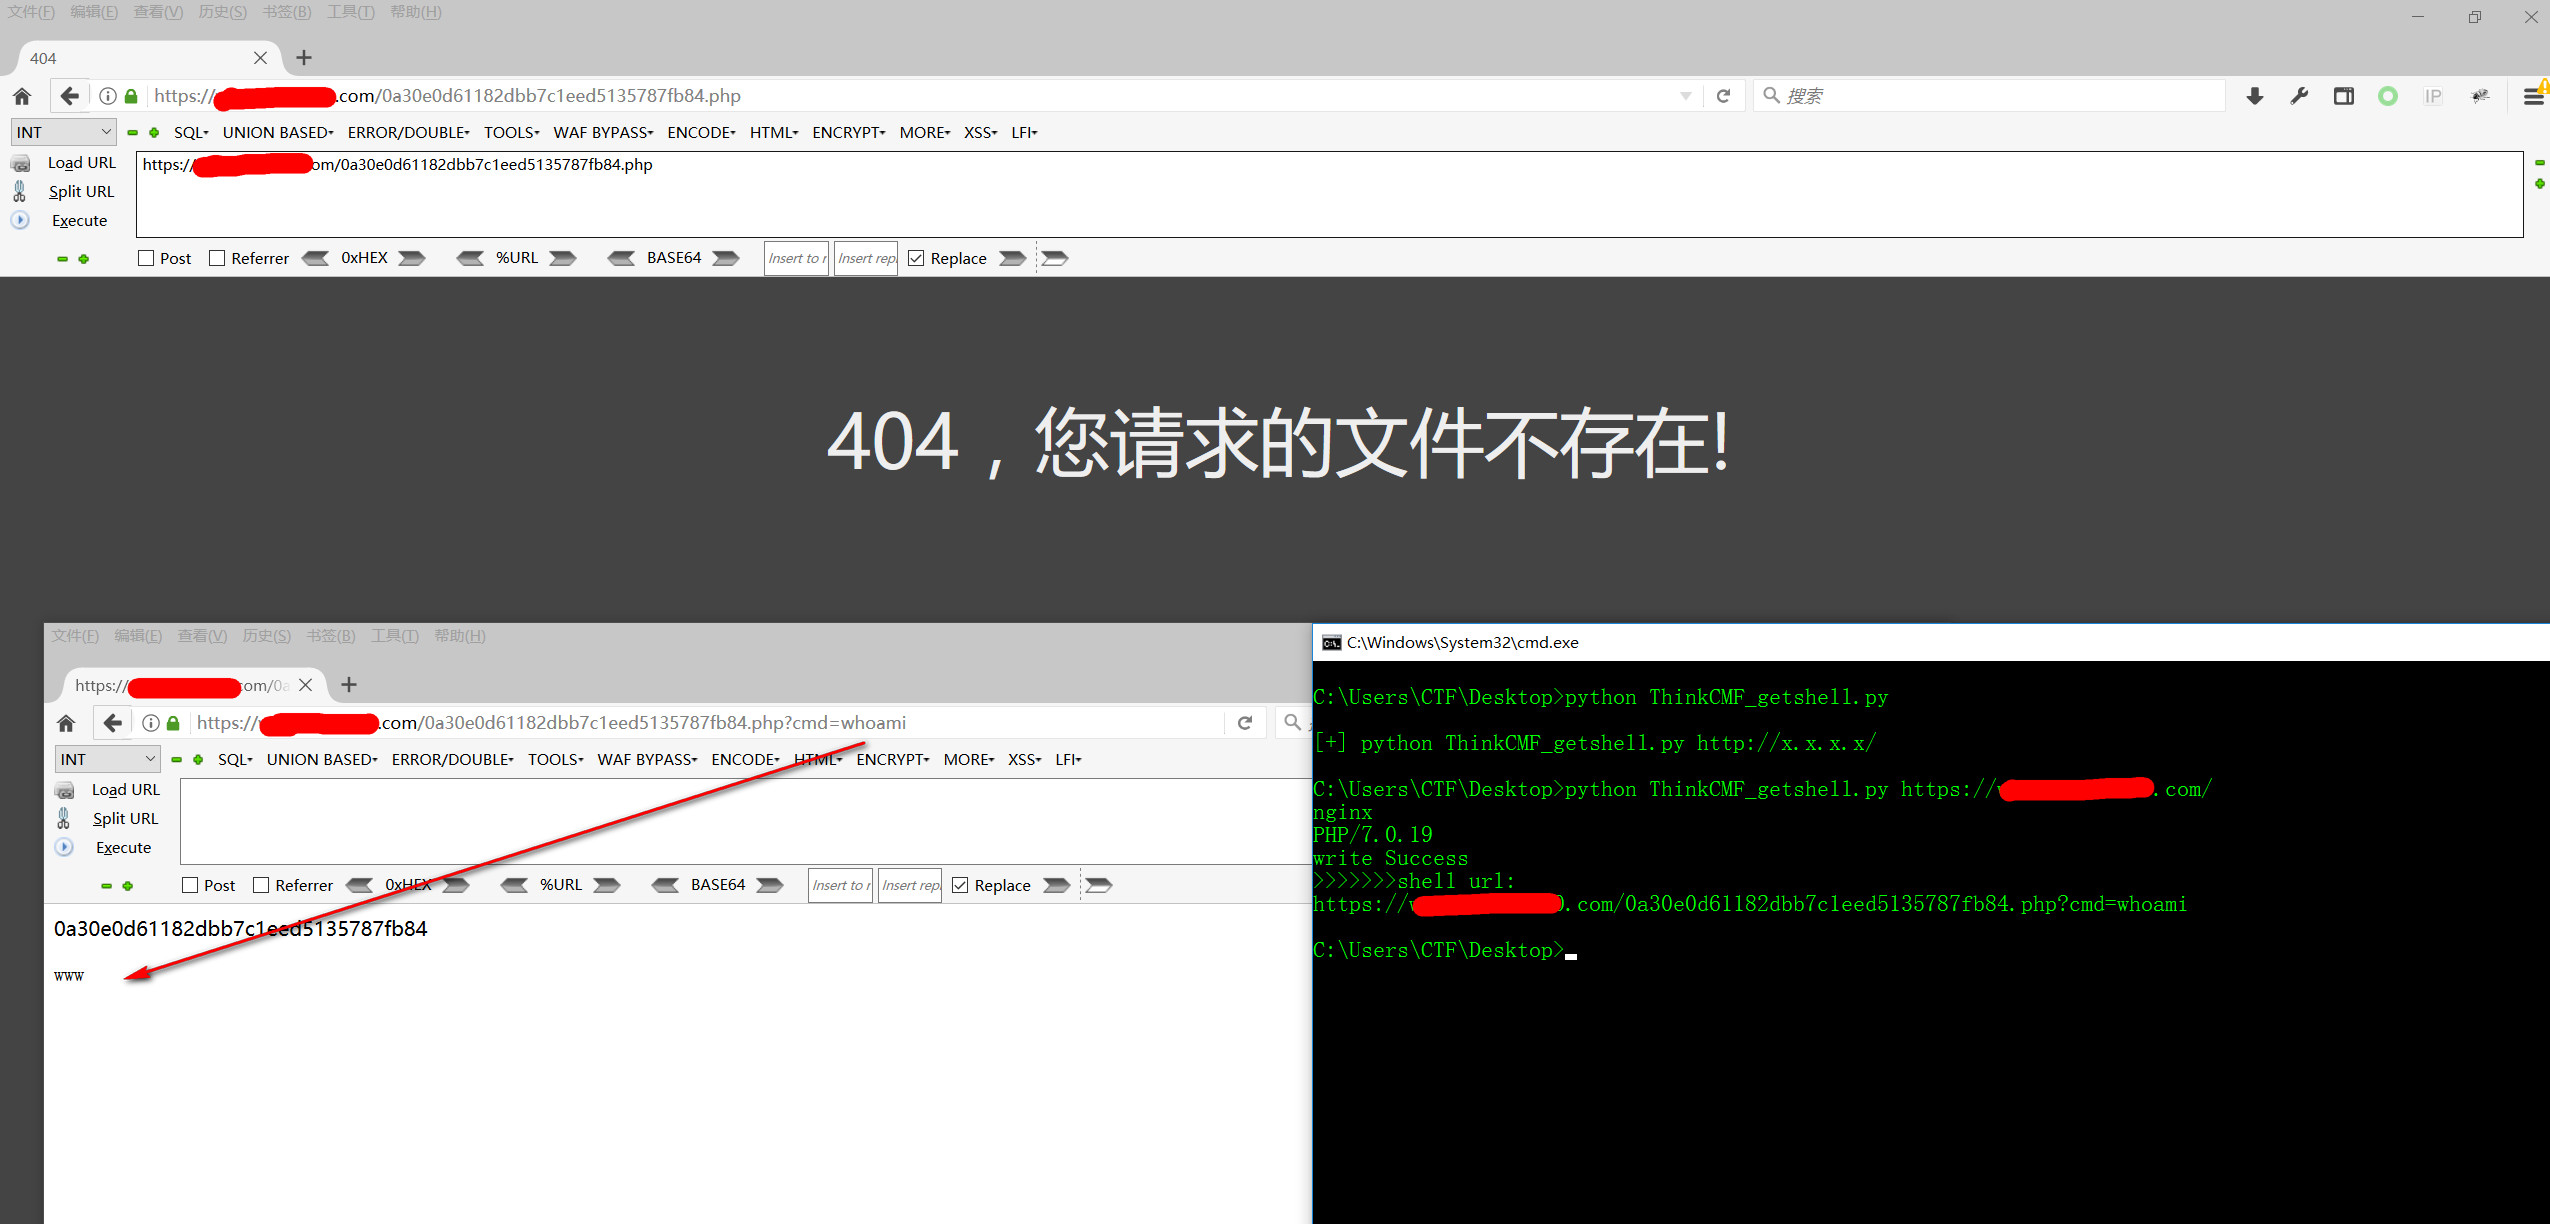 jas502n/thinkcmf_getshell
ThinkCMF 框架上的任意内容包含漏洞
 holygu/cve-2023-42442
Go-based exploit for JumpServer unauthorized access vulnerability (CVE-2023-42442) with a single-command execution interface for penetration testing.
 lz2y/cve-2021-2394
Proof-of-concept exploit for CVE-2021-2394, a remote code execution vulnerability in Oracle WebLogic Server. Uses LDAP or RMI deserialization to…
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 knqyf263/cve-2019-6340
Environment for CVE-2019-6340 (Drupal)
 d0n601/pentest-cheat-sheet
There are many cheat sheets out there, but this is mine.
 kiddo-pwn/cve-2024-50629_50631
N-day Exploit for Synology BeeStation RCE by DEVCORE (Pwn2Own 2024)
 jofpin/compaxss
Bypass XSS Reflected Cross-site scripting
 pwnedshell/larascript
Laravel RCE exploit. CVE-2018-15133
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container
 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
 mr-xn/cve-2021-42342
Proof-of-concept exploit for CVE-2021-42342, a remote code execution vulnerability in GoAhead web server, demonstrating LD_PRELOAD injection via CGI…
 eviladan0s/cve-2019-16097
Proof-of-concept exploit for CVE-2019-16097 in Harbor, enabling attacker admin account creation and malicious image upload. For authorized security…
 win3zz/cve-2026-1731
CVE-2026-1731 - Critical command injection vulnerability in BeyondTrust Remote Support and Privileged Remote Access due to unsafe Bash arithmetic…
 silentsignal/websphere-wsif-gadget
CVE-2020-4464 / CVE-2020-4450
 horizon3ai/cve-2024-9465
Proof of Concept Exploit for CVE-2024-9465








