
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 shirouqwq/cve-2022-2333
SXF VPN RCE
 agienka/blindy
Simple script to automate brutforcing blind sql injection vulnerabilities
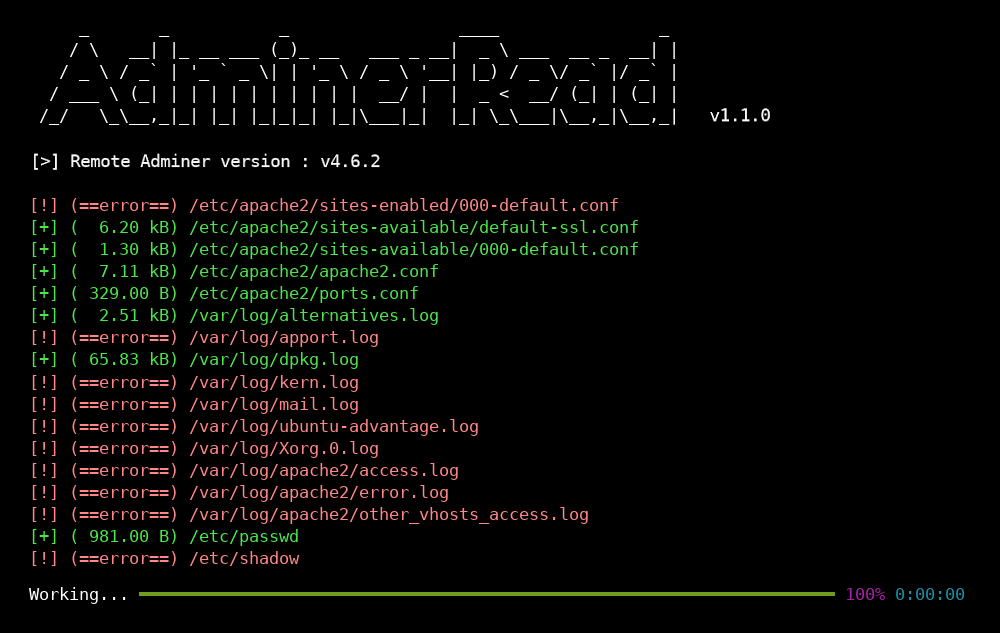 p0dalirius/cve-2021-43008-adminerread
Exploit tool for CVE-2021-43008 Adminer 1.0 up to 4.6.2 Arbitrary File Read vulnerability
 abdoghazy2015/ofbiz-cve-2023-49070-rce-poc
Pre-auth RCE proof-of-concept for Apache OFBiz CVE-2023-49070, exploiting XML-RPC Java deserialization to achieve remote code execution on vulnerable…
 zephrfish/cve-2024-4577-php-rce
PHP RCE PoC for CVE-2024-4577 written in bash, go, python and a nuclei template
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…
 nettitude/cve-2024-20356
This is a proof of concept for CVE-2024-20356, a Command Injection vulnerability in Cisco's CIMC.
 mpgn/cve-2019-7609
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer
 watchtowrlabs/fortios-auth-bypass-check-cve-2024-55591
Python script to detect FortiOS authentication bypass (CVE-2024-55591) by probing WebSocket connections to the management interface, identifying…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 xuechiyaobai/cve-2019-9810-poc
Array.prototype.slice wrong alias information.
 ambionics/owncloud-exploits
ownCloud exploits for CVE-2023-49105
 csenox/gitlab-exiftool-rce
Python exploit achieving remote code execution on GitLab versions before 13.10.3 by abusing ExifTool DjVu parsing through GitLab Workhorse image…
 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
 flyteas/struts2-045-exp
Struts2 S2-045(CVE-2017-5638)Exp with GUI
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 idealdreamlast/cve-2020-9484
用Kali 2.0复现Apache Tomcat Session反序列化代码执行漏洞
 dragoneeg/struts2-048
Python-based proof-of-concept exploit for CVE-2017-9791 (Apache Struts2 S2-048) with check and command execution modes for penetration testing.








