
 #1
Automated tools for detecting known vulnerabilities in systems and applications.
Kitploit recommended
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
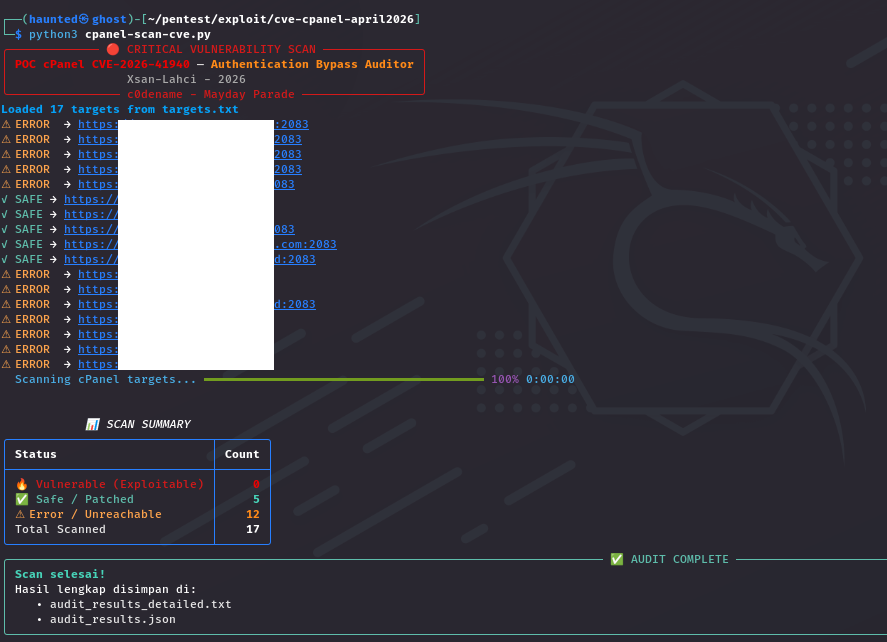 xsanflip/poc-cpanel-cve-2026-41940
Multi-threaded security auditing tool that detects CVE-2026-41940, an authentication bypass in cPanel/WHM, using CRLF injection and dynamic port…
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
 sdogancesur/log4j_github_repository
This work includes testing and improvement tools for CVE-2021-44228(log4j).
 samael0x4/cve-2026-21962
Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
 keraattin/cve-2026-39987
Detection and exploitation toolkit for CVE-2026-39987, a pre-auth RCE in Marimo notebooks. Includes Python scanner and Nmap NSE script to identify…
 kagantua/cpanelwhm-authbypass
Go-based scanner and exploit tool for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports batch scanning, token leakage, and…
 anon-cyber-team/cve-2026-27966--rce-in-langflow
All-in-one exploit tool for CVE-2026-27966, a critical RCE in Langflow. Features mass scanning, auto-detection, payload execution, interactive shell,…
 nabla-c0d3/sslyze
Fast and powerful SSL/TLS scanning library.
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 mozilla/cipherscan
A very simple way to find out which SSL ciphersuites are supported by a target.
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.








