
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 stamparm/dsxs
Damn Small XSS Scanner
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
 github/securitylab
Resources related to GitHub Security Lab
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 adeyosemanputra/pygoat
intentionally vuln web Application Security in django
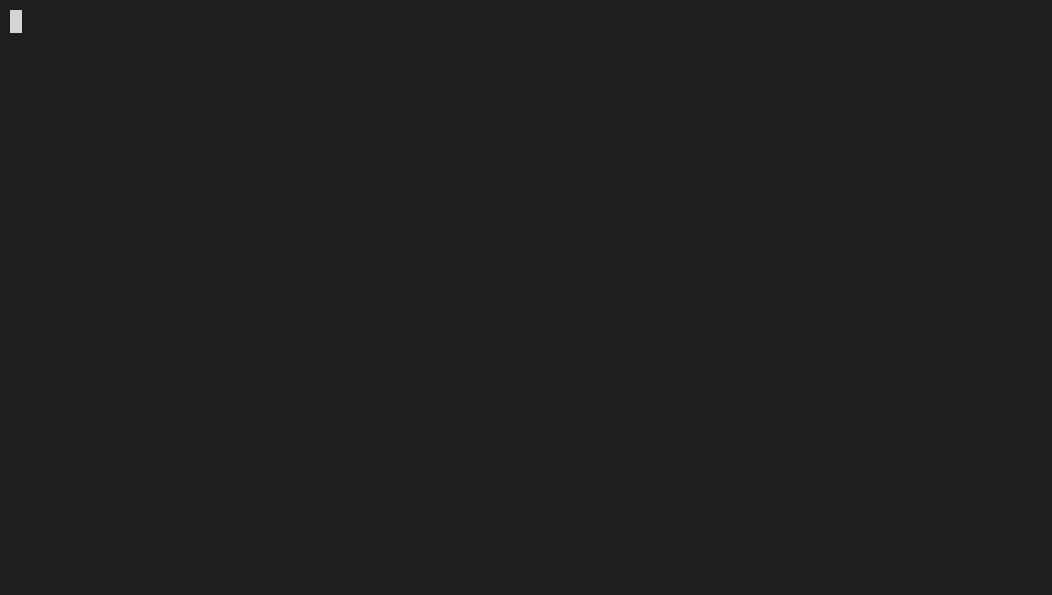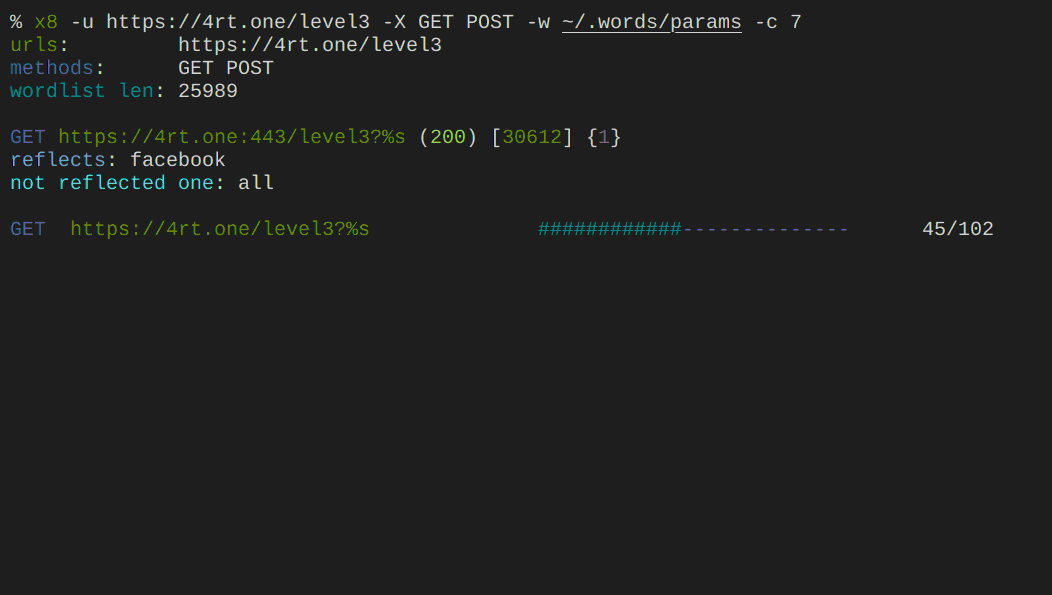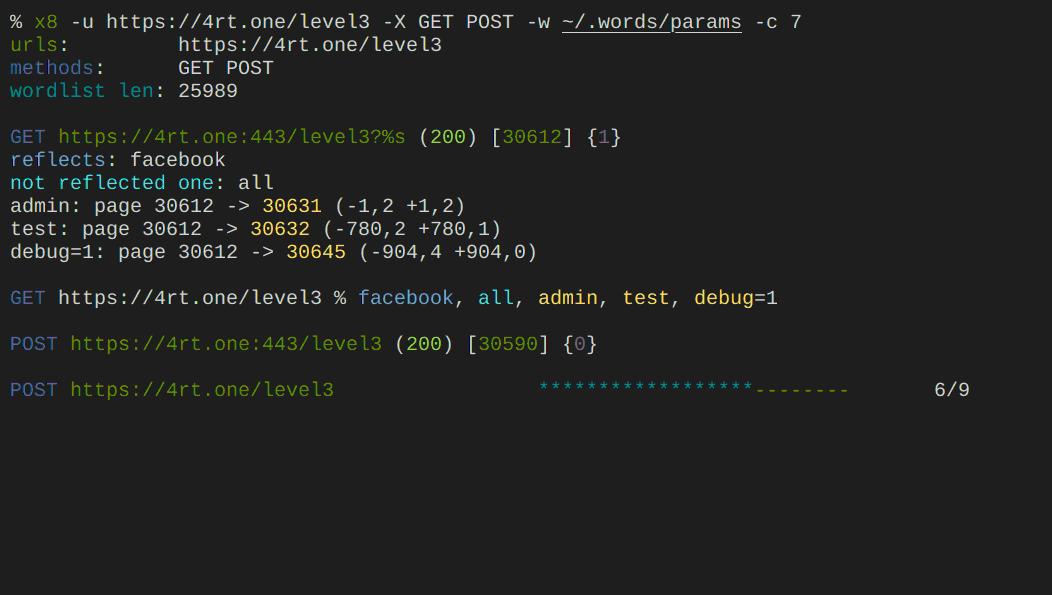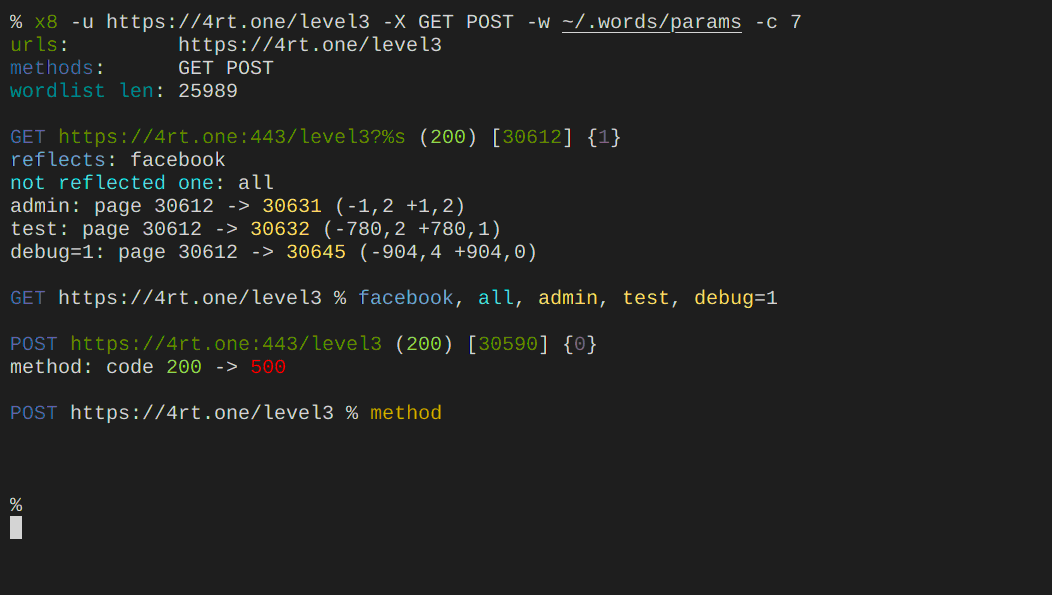 sh1yo/x8
Hidden parameters discovery suite
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 ayoubfathi/leaky-paths
A collection of special paths linked to common sensitive APIs, devops internals, frameworks conf, known misconfigurations, juicy APIs ..etc. It could…
 aquasecurity/starboard
Superseded by https://github.com/aquasecurity/trivy-operator
 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
 stamparm/identywaf
Blind WAF identification tool
 portswigger/bambdas
Bambdas collection for Burp Suite Professional and Community.








